

sobelow
 nccgroup/sobelow
Security-focused static analysis for the Phoenix Framework
code-analysisstatic-analysisvulnerability-analysis+2
1.8k
nccgroup/sobelowSecurity-focused static analysis for the Phoenix Framework
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 tillson/git-hound
Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.
 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro

 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 sektioneins/pcc
Automated PHP configuration auditor that scans php.ini for security misconfigurations, supports CLI and web modes, and outputs results in text, HTML,…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 google/kafel
A language and library for specifying syscall filtering policies.
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
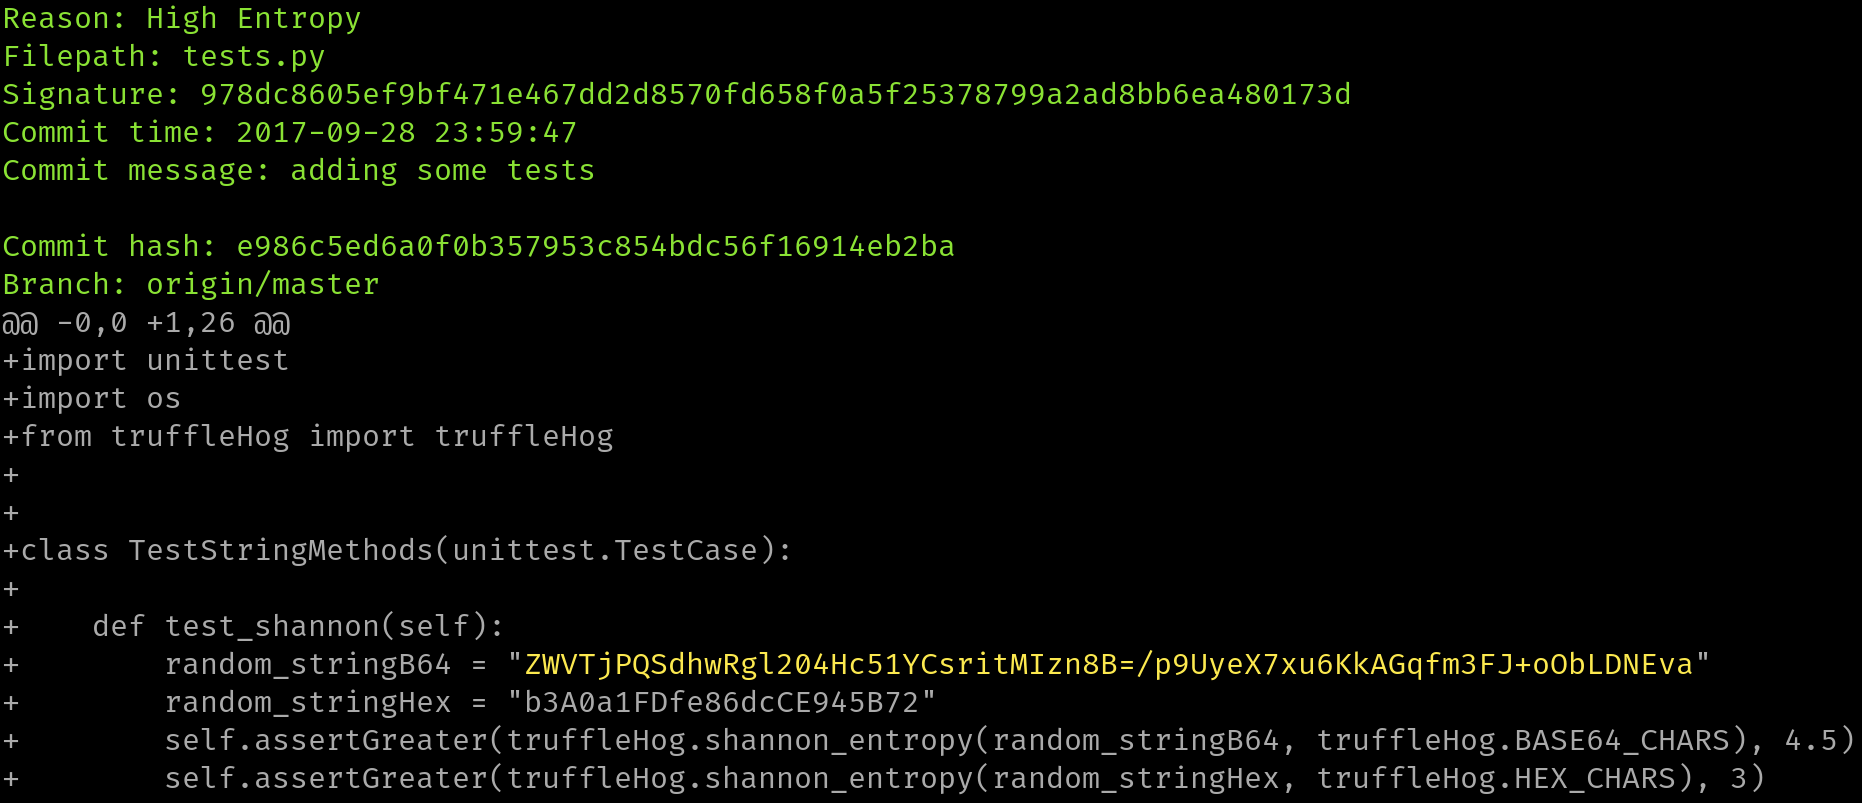 godaddy/tartufo
Searches through git repositories for high entropy strings and secrets, digging deep into commit history
 snowsnowsnows/eaglevm
Native code virtualizer for x64 binaries
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 adshao/flounder
Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.