
CVE-2021-42694
 k271266/cve-2021-42694
Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
code-analysiseducationstatic-analysis+2
k271266/cve-2021-42694Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 nccgroup/cq
Fast code security scanner designed for manual security code review by experts. Outputs line-referenced findings to text files for easy filtering and…
 jfrog/jfrog-cve-2022-21449
Scans compiled Java archives (JAR/WAR) for ECDSA algorithm usage to detect CVE-2022-21449 vulnerability. Recursively examines .class files with…
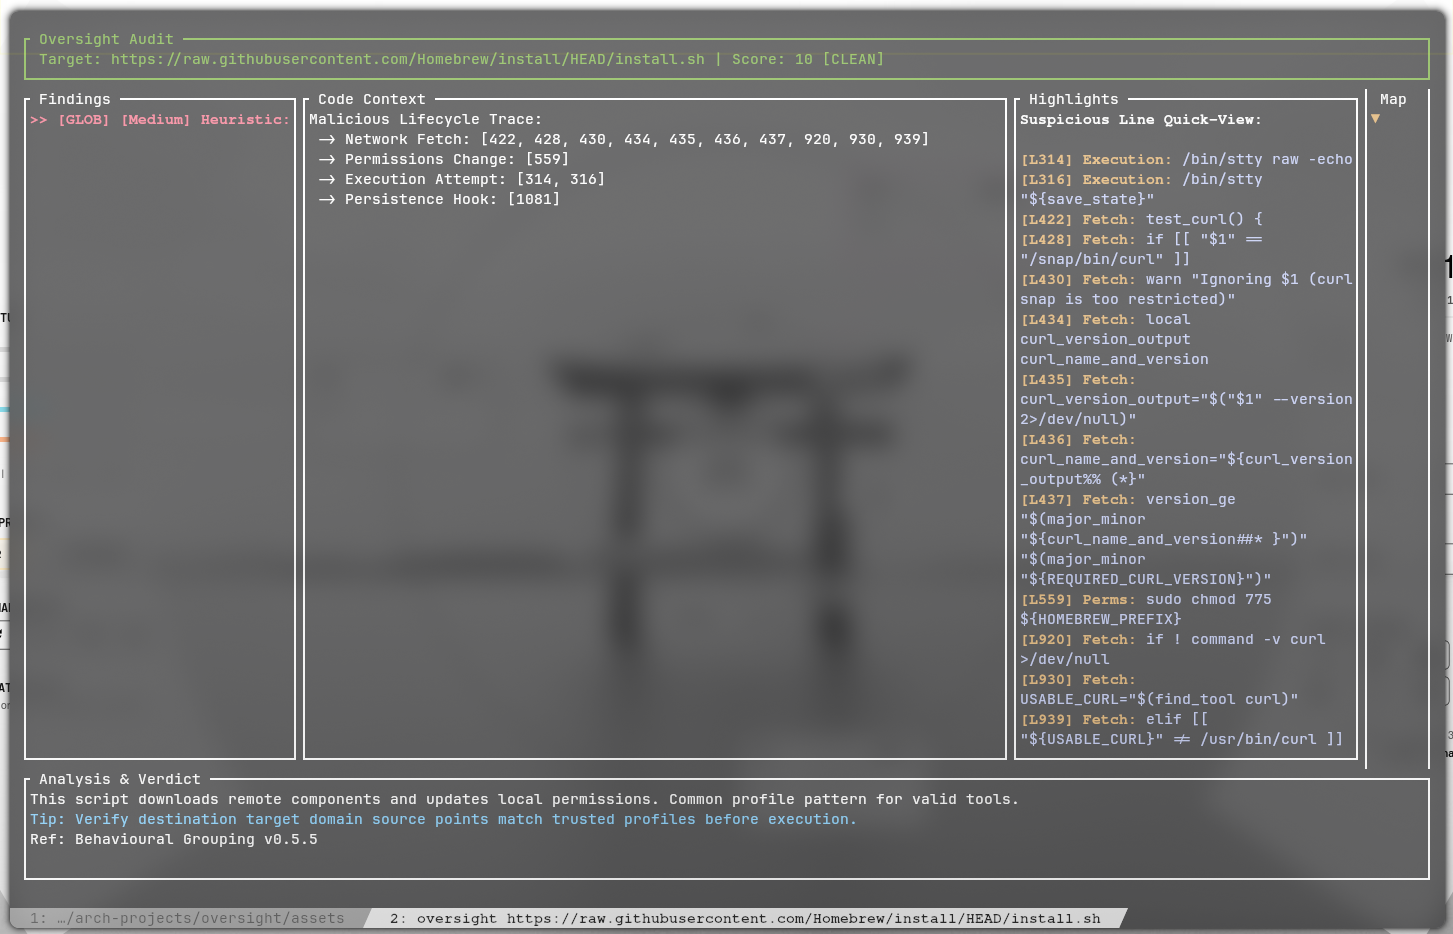 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 s1ko/cve-2026-52617
Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…
 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
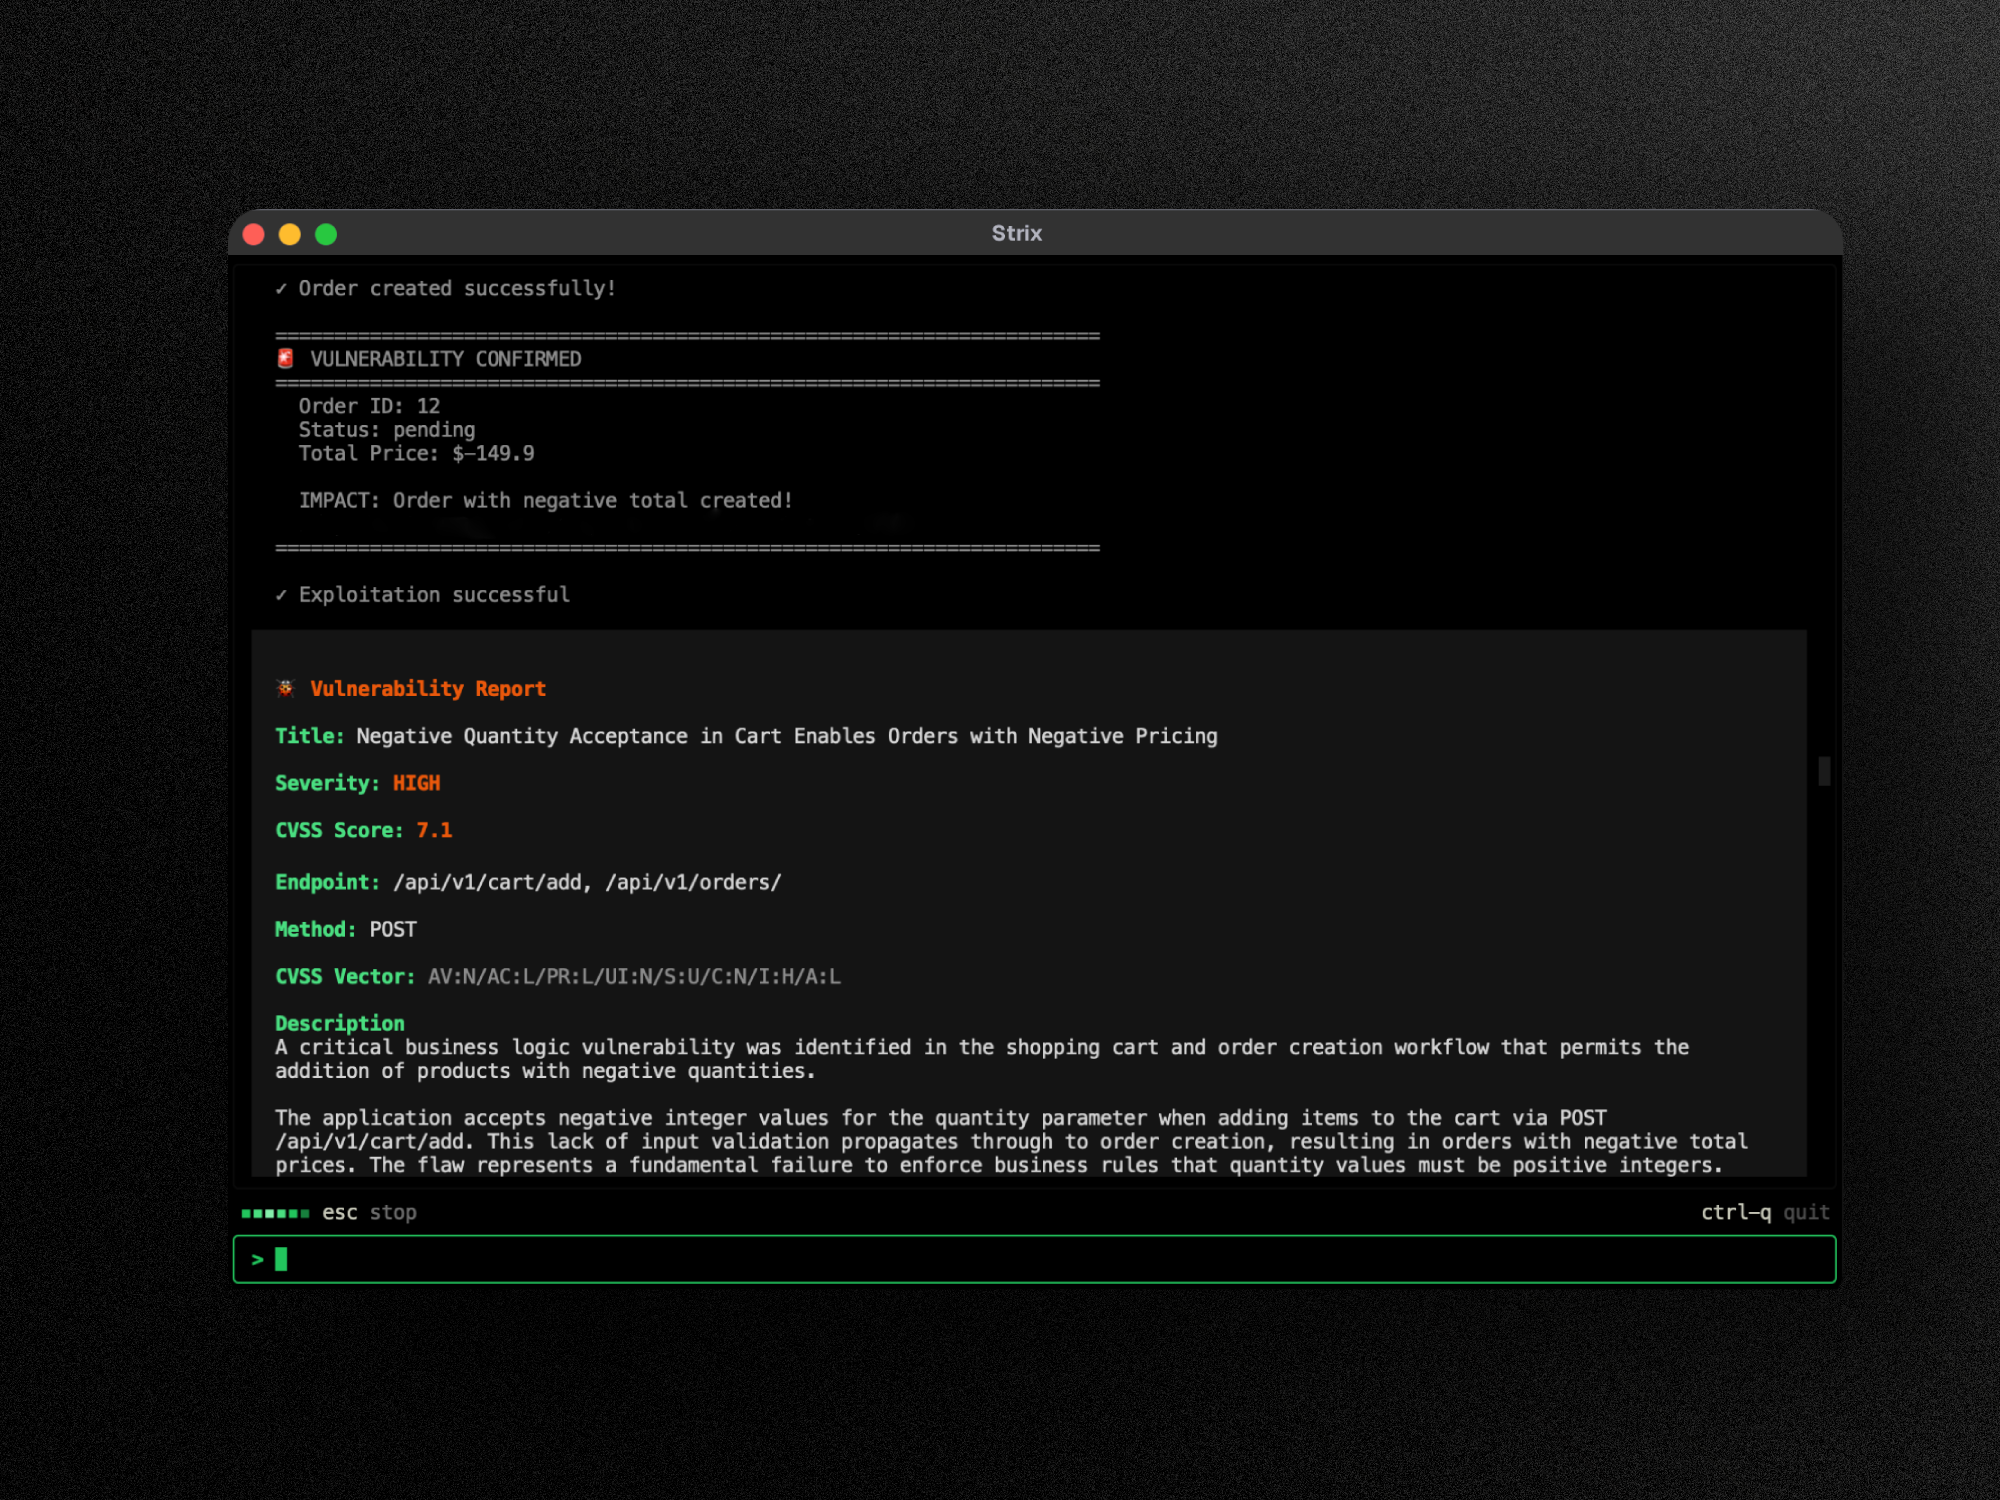 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.