
CVE-2024-9593
 randomrobbiebf/cve-2024-9593
Time Clock <= 1.2.2 & Time Clock Pro <= 1.1.4 - Unauthenticated (Limited) Remote Code Execution
code-analysisexploitationpenetration-testing+3
8
randomrobbiebf/cve-2024-9593Time Clock <= 1.2.2 & Time Clock Pro <= 1.1.4 - Unauthenticated (Limited) Remote Code Execution
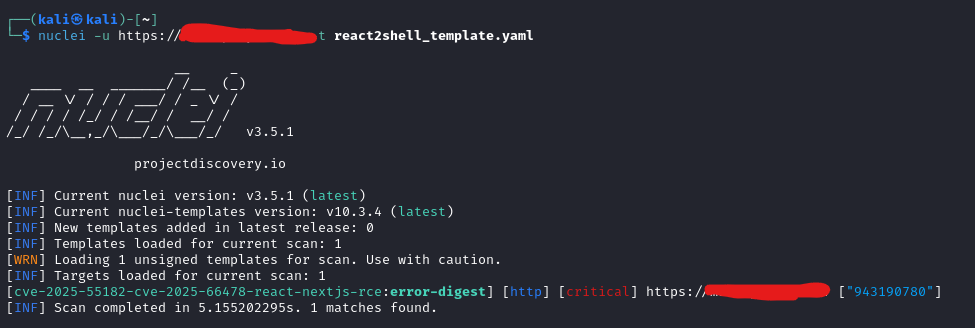 shamo0/react2shell-poc
Nuclei template for detecting react2shell (CVE-2025-55182 & CVE-2025-66478)
 mogwailabs/cve-2017-1000486
Proof of Concept Exploit for PrimeFaces 5.x EL Injection (CVE-2017-1000486)
 0xeval/cve-2015-3224
Ruby on Rails Web Console (v2) Whitelist Bypass Code Execution implementation in Python
 zhzyker/cve-2018-7600-drupal-poc-exp
CVE-2018-7600 Drupal Drupalgeddon 2 远程代码执行漏洞利用脚本
 kimtruth/cve-2025-55183-poc
PoC for CVE-2025-55183
 0xl0k1/cve-2012-1823
PHP CGI Argument Injection.
 hideki233/cve-2025-3248-langflow-rce
Proof-of-concept exploit for CVE-2025-3248, an unauthenticated remote code execution vulnerability in Langflow, demonstrating code injection via the…
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 jas502n/cve-2019-14439
Proof-of-concept exploit for Jackson-databind remote code execution vulnerability (CVE-2019-14439) targeting insecure deserialization in Java…
 ok0mo/cve-2022-24086-rce-poc
Verifed Proof of Concept on CVE-2022-24086
 brianwrf/cve-2019-6690
It is a simple PoC of Improper Input Validation in python-gnupg 0.4.3 (CVE-2019-6690).
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 0z09e/cve-2022-22909
Hotel Druid 3.0.3 Code Injection to Remote Code Execution
 fser/ghost-checker
Test wether you're exposed to ghost (CVE-2015-0235). All kudos go to Qualys Security
 trachinus/cve-2026-4813
Proof-of-concept exploit for authenticated remote code execution via XSLT injection in Lutece Core, demonstrating command execution through crafted…
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…