 ok0mo/cve-2022-24086-rce-poc
Verifed Proof of Concept on CVE-2022-24086

CVE-2022-24086 which Adobe saw being “exploited in the wild in very limited attacks” received a severity score of 9.8 out of 10, and adversaries exploiting it can achieve remote code execution on affected systems without the need to authenticate. Issue that is now tracked as CVE-2022-24087, which has the same severity score and can lead to the same result when leveraged in attacks. Both are Improper Input Validation vulnerabilities and the company released patches for Adobe Commerce and Magento Open Source to address the two security issues.
We will focus only on 2022-24086, because if CMS is patched, usually it already has both patches, so there is no point of digging into 2022-24087 one.
Magento Open Source / Adobe Commerce - 2.3.3-p1 - 2.3.7-p2
Magento Open Source / Adobe Commerce - 2.4.0 - 2.4.3-p1
This PoC checked on 2.3.4, 2.4.0 2.4.2-p2 2.4.3 and on 2.4.3-p1 versions with default email templates module and default sample data.
Let's dig into official patches, MDVA-43443, MDVA-43395. All composer patches for all versions share common parts, most important are:
+    private function sanitizeValue($value)
+    {
+        return is_bool($value) ? $value : str_replace(['{', '}'], '', (string) $value);
+    }
+        $pattern = '/{{.*?}}/';
+        do {
+            $result = preg_replace($pattern, '', (string)$result);
+        } while (preg_match($pattern, $result));
As we see, they try to get rid of {{ and }}. Those curly double brackets are used in built-in email templates.
Now it is the time to dig into email templates!
Official manual on email templates edited on 15-th of March, what changed and why? web.archive.org will show us an old version of that page and we can see that they removed mentions about system variables. Information about getTemplateFilter and addAfterFilterCallback methods were erased from manual.
    public function getTemplateFilter()
    {
        if (empty($this->templateFilter)) {
            $this->templateFilter = $this->getFilterFactory()->create();
            $this->templateFilter->setUseAbsoluteLinks($this->getUseAbsoluteLinks())
                ->setStoreId($this->getDesignConfig()->getStore())
                ->setUrlModel($this->urlModel);
        }
        return $this->templateFilter;
    }
    public function addAfterFilterCallback(callable $afterFilterCallback)
    {
        // Only add callback if it doesn't already exist
        if (in_array($afterFilterCallback, $this->afterFilterCallbacks)) {
            return $this;
        }

        $this->afterFilterCallbacks[] = $afterFilterCallback;
        return $this;
    }
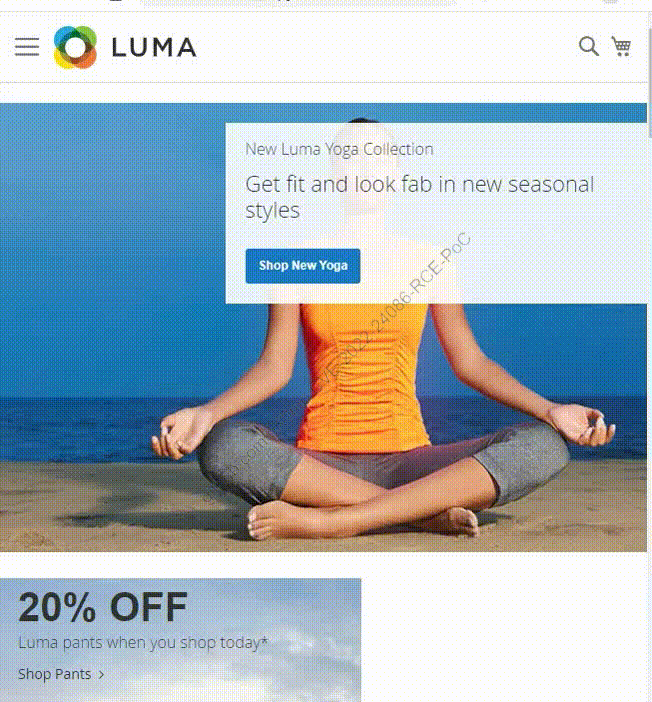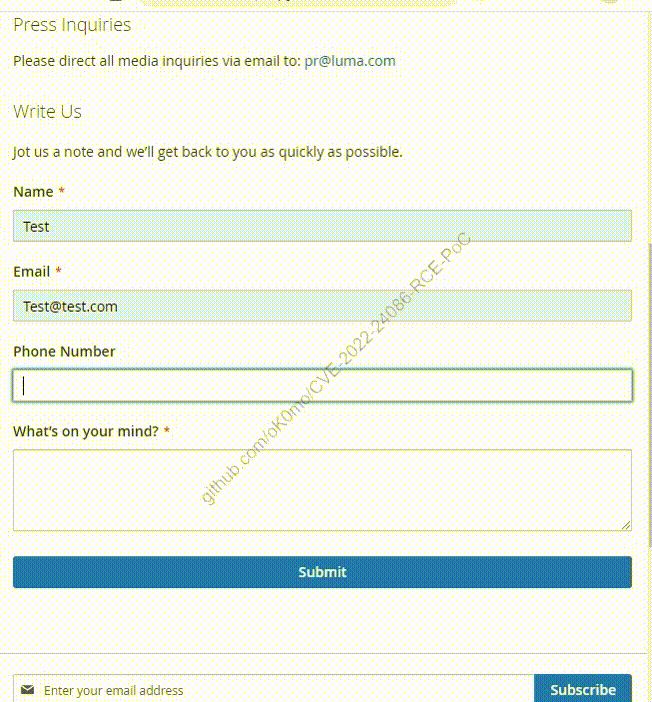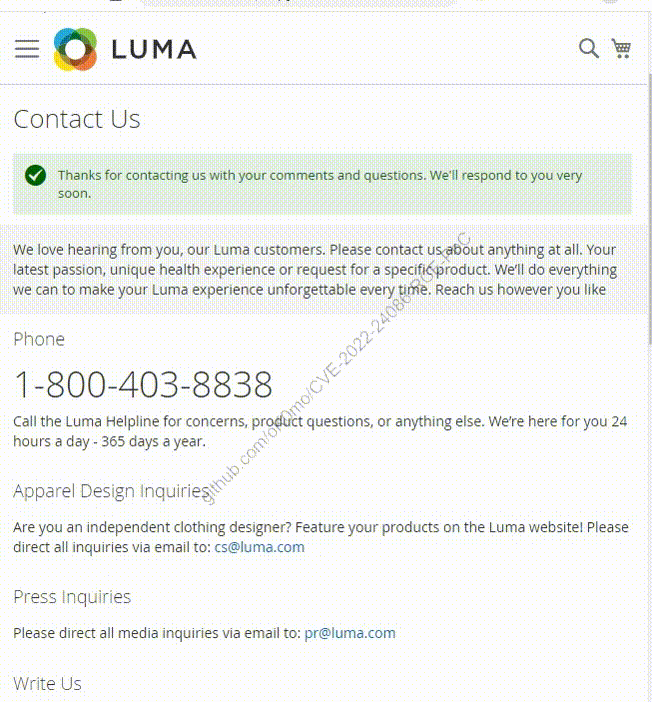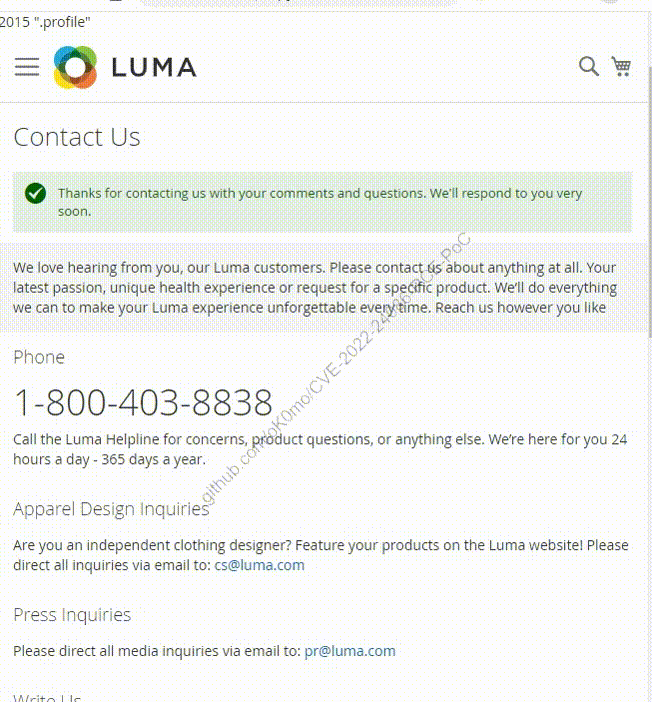
Most of the major Magento users have already patched and that tool is no longer as dangerous as it was a couple months ago. But due to potential damage that this tool can inflict this PoC should not be in limited access.
Current price - 0.5 BTC. It includes full instruction on penetration, sample payloads and support.
Our XMPP contact for consultation and ordering is [email protected].
This PoC is explicitly not in a state to cause any damage. It is a solid starting point for building something bigger.
The authors of this project is not responsible for any possible harm caused by the materials.
CC0






