external_expat_AOSP10_r33_CVE-2022-23852

C library for parsing XML, patched for CVE-2022-23852, providing stream-oriented XML parsing with handlers for efficient document processing.

C library for parsing XML, patched for CVE-2022-23852, providing stream-oriented XML parsing with handlers for efficient document processing.

Android KeyChain package with patch for CVE-2021-0963, addressing a security vulnerability in AOSP 10.

Post Saint <= 1.3.1 plugin for WordPress Arbitrary File Upload

Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…

Technical Details and Exploit for CVE-2024-11392

Docker-based lab environment for CVE-2015-1427 ElasticSearch Groovy sandbox bypass and remote code execution, demonstrating two POC methods with Java…

Proof-of-concept exploit for CVE-2024-32004, a Git remote code execution vulnerability, demonstrating exploitation via a malicious upload-pack filter.


Log4j2 Vulnerability (CVE-2021-44228)

CVE-2024-4367

Demonstrating Remote Code Execution Vulnerability via Pickle Serialization in ClearML

https://nvd.nist.gov/vuln/detail/CVE-2022-34169

PoC and fix for CVE-2024-38828: Spring Framework DoS via Content-Length manipulation in ByteArrayHttpMessageConverter. Includes load testing,…

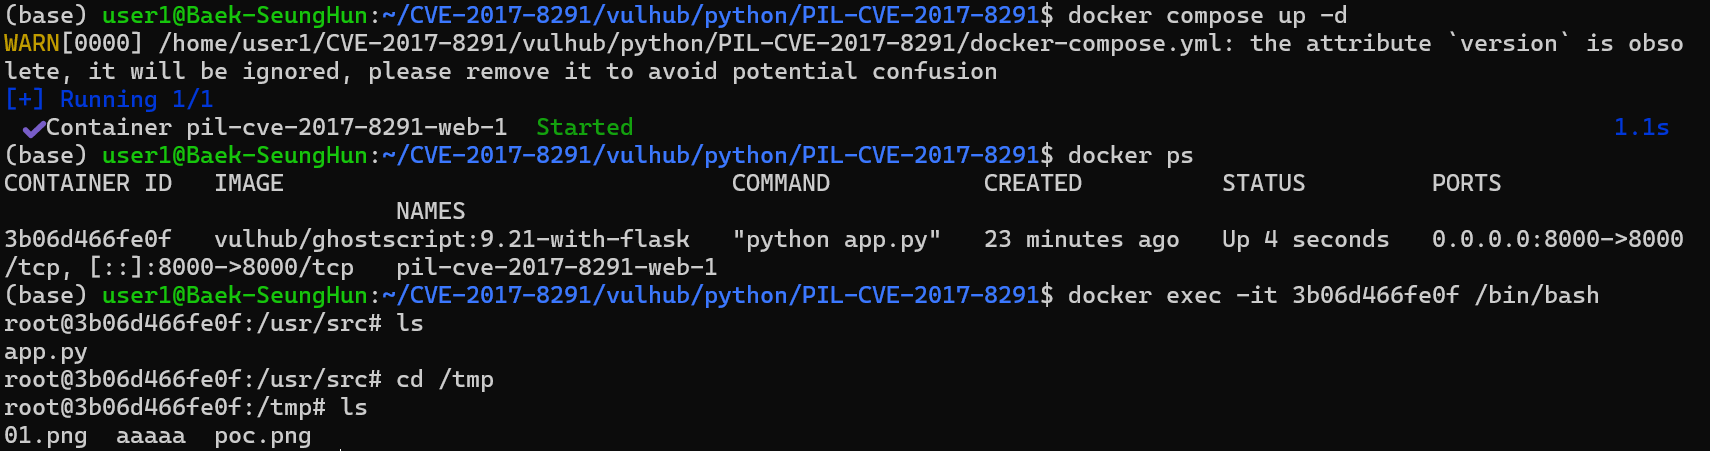
Educational lab demonstrating CVE-2017-8291 (PIL/GhostScript RCE) via crafted EPS file upload with PNG extension, including Docker setup and PoC…

jee web project with sanitised log4shell (CVE-2021-44228) vulnerability

Implementações de servidores HTML em GO para análise da vulnerabilidade CVE-2023-29406.