
fickling
 trailofbits/fickling
A Python pickling decompiler and static analyzer
ai-securitybinary-analysiscode-analysis+5
667
trailofbits/ficklingA Python pickling decompiler and static analyzer
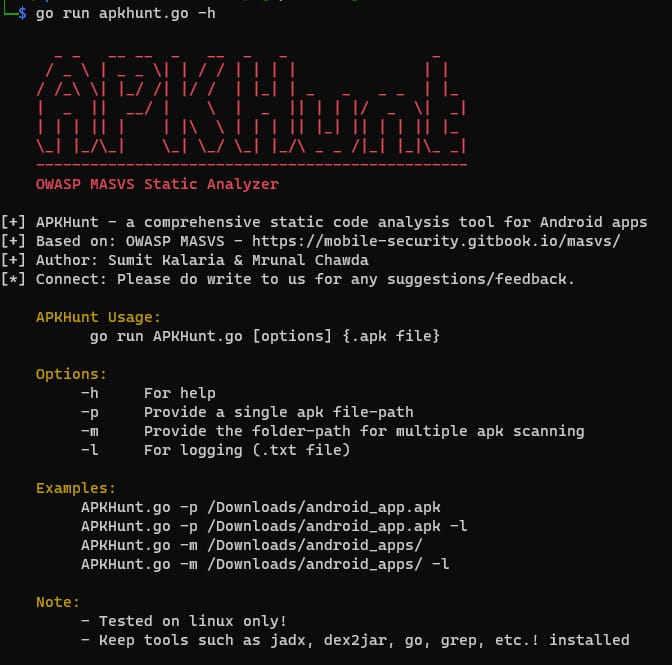 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
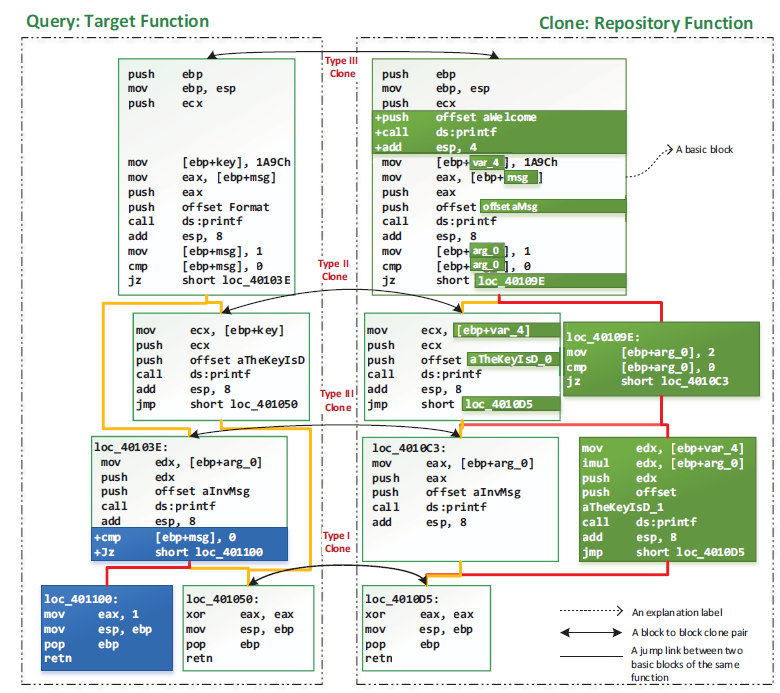 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
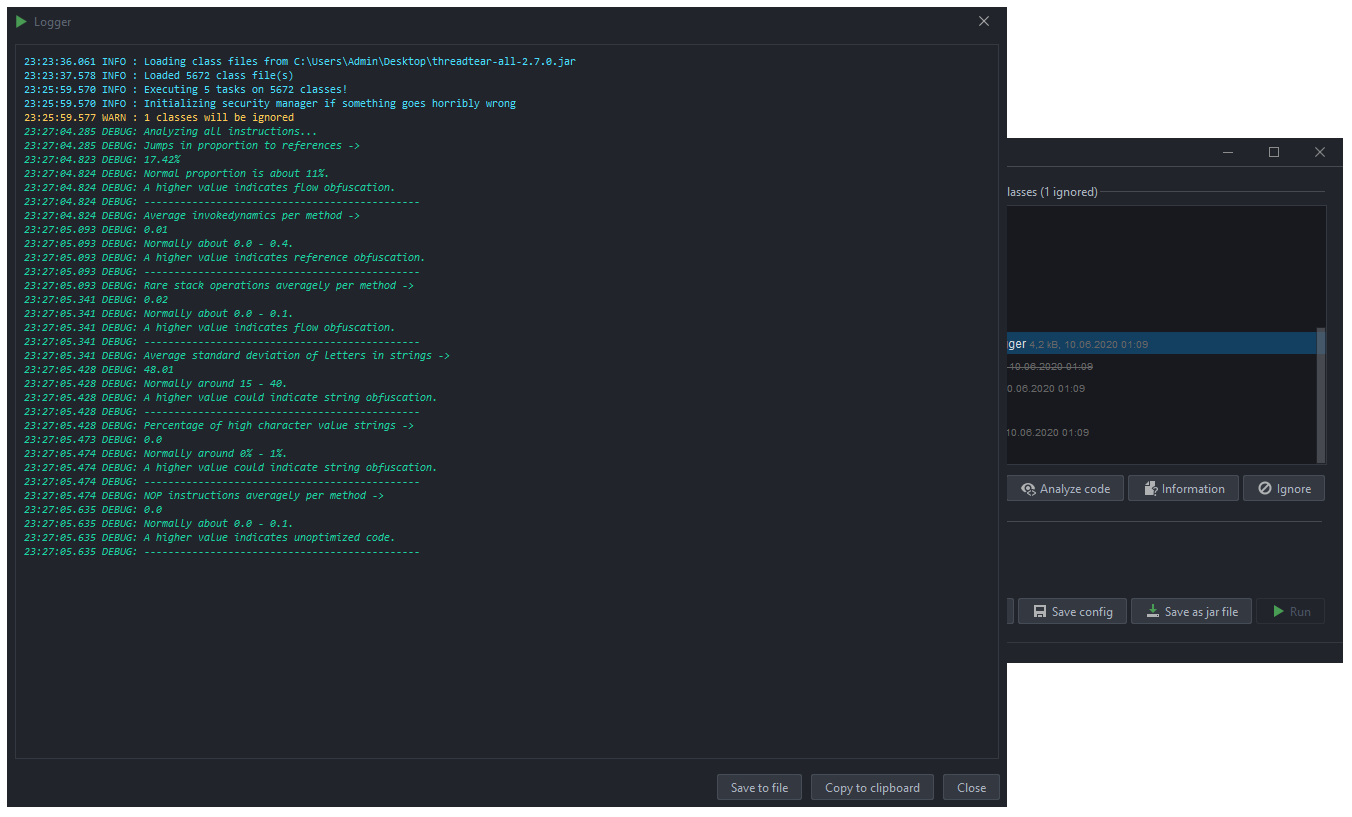 loerting/threadtear
Multifunctional java deobfuscation tool suite
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 nodesecure/js-x-ray
JavaScript & Node.js open-source SAST scanner. A static analyser for detecting most common malicious patterns 🔬.
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
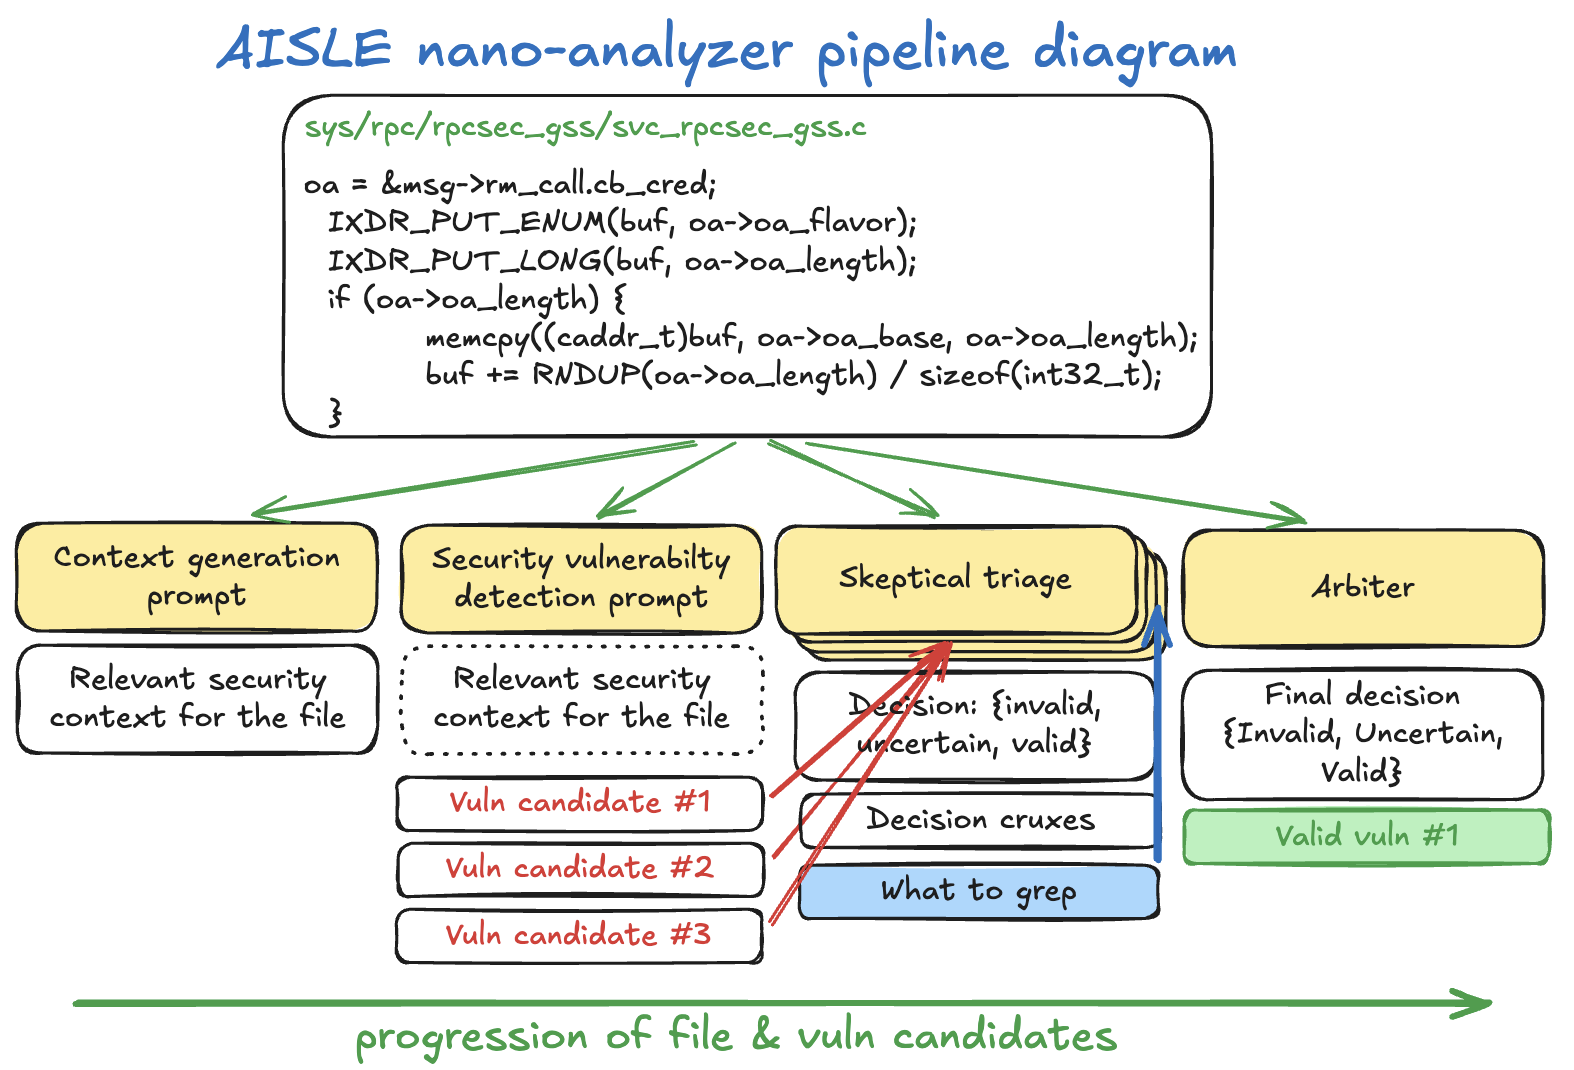 weareaisle/nano-analyzer
A minimal LLM-powered zero-day vulnerability scanner by AISLE.
 colton1skees/dna
LLVM based static binary analysis framework
 trailofbits/trailmark
Build and query a graph database representation of source code
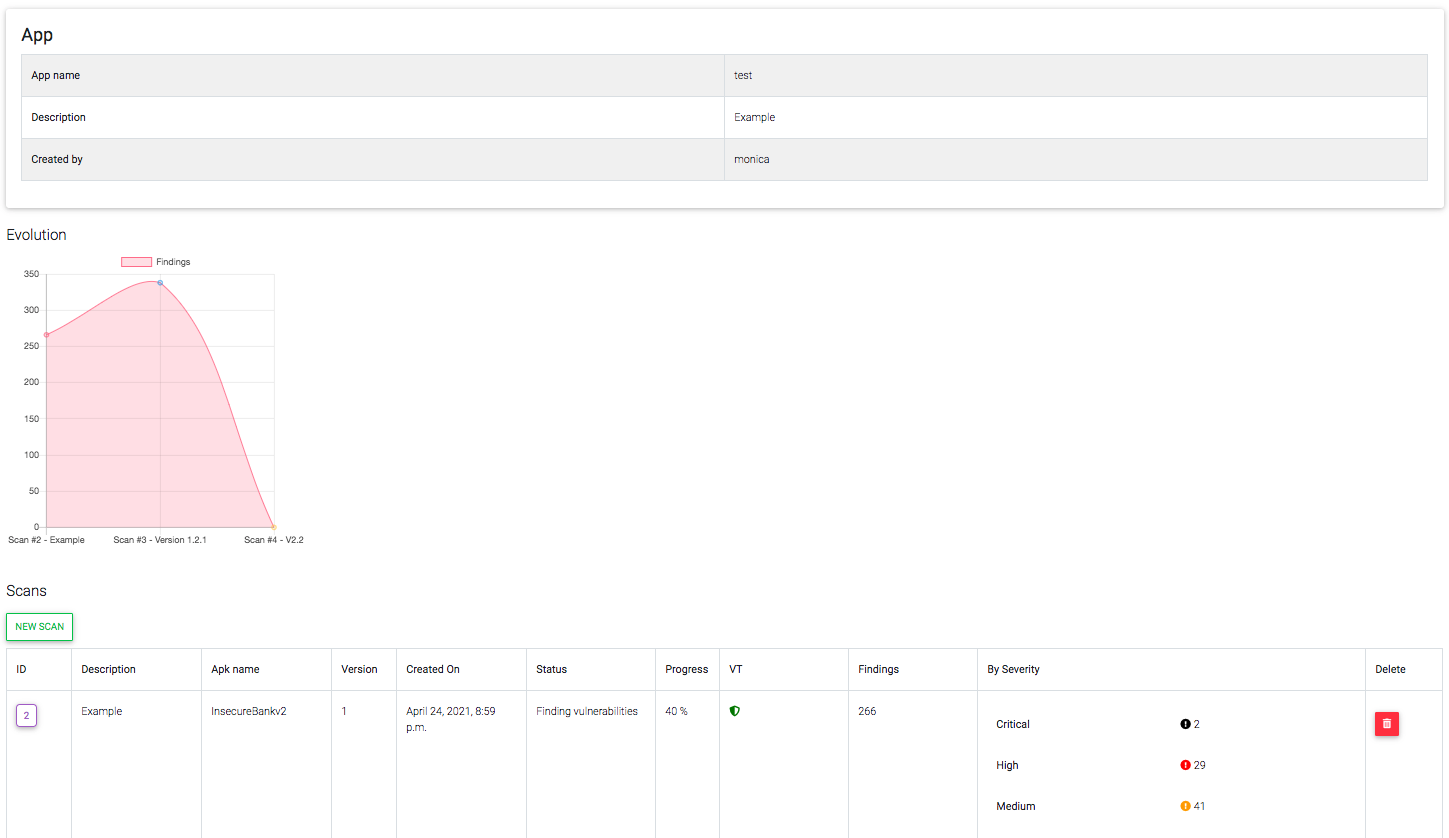 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
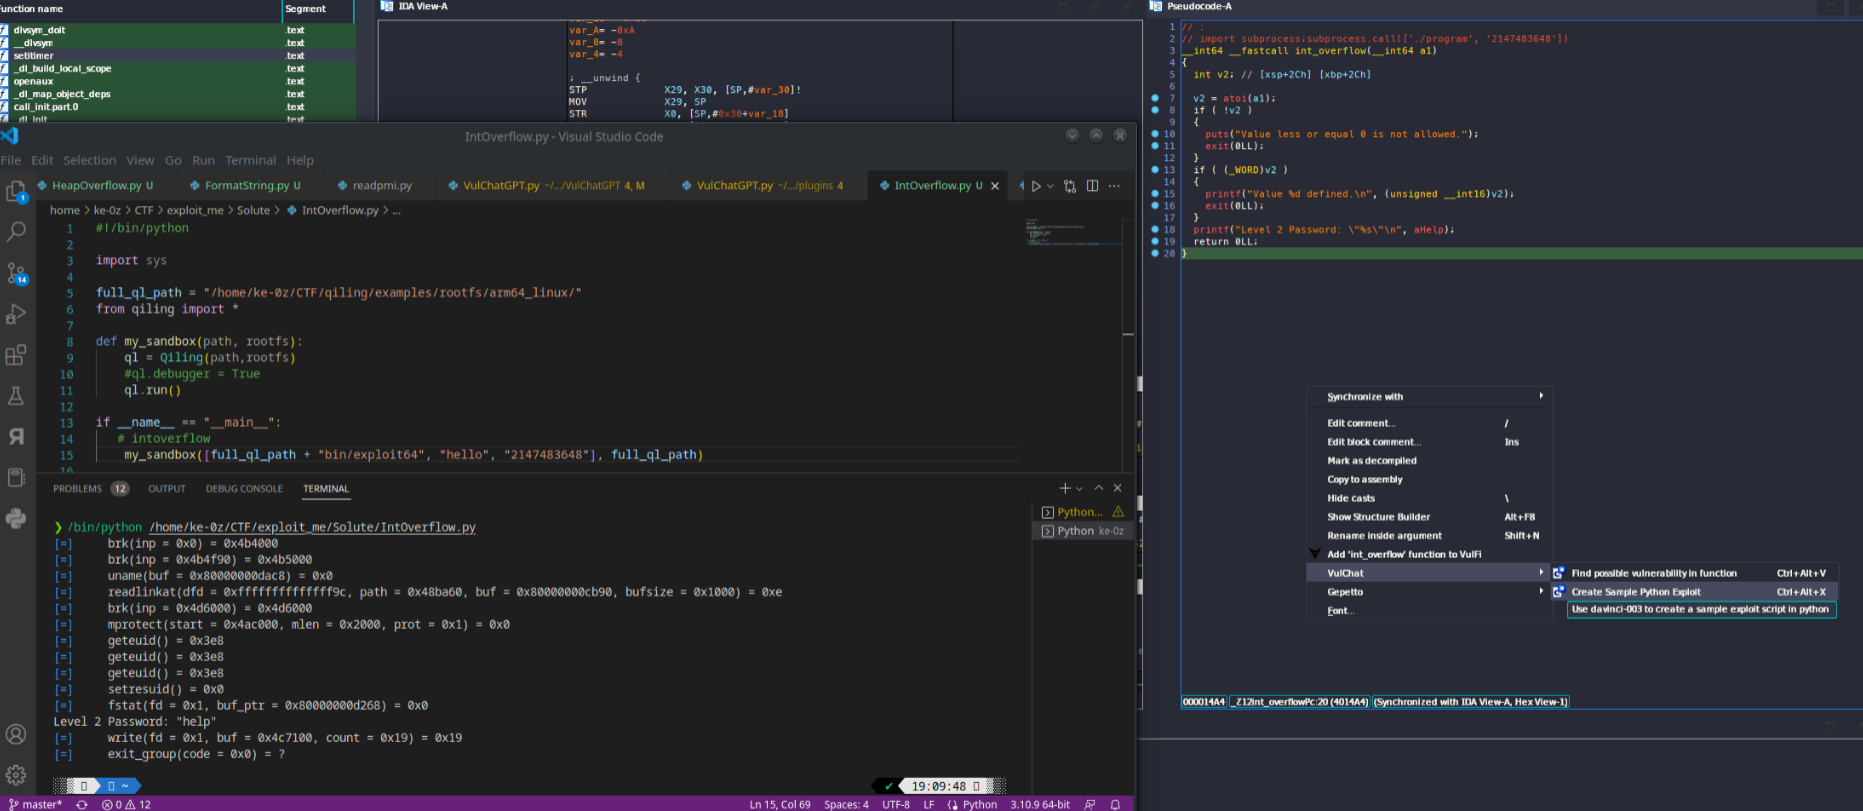 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.