
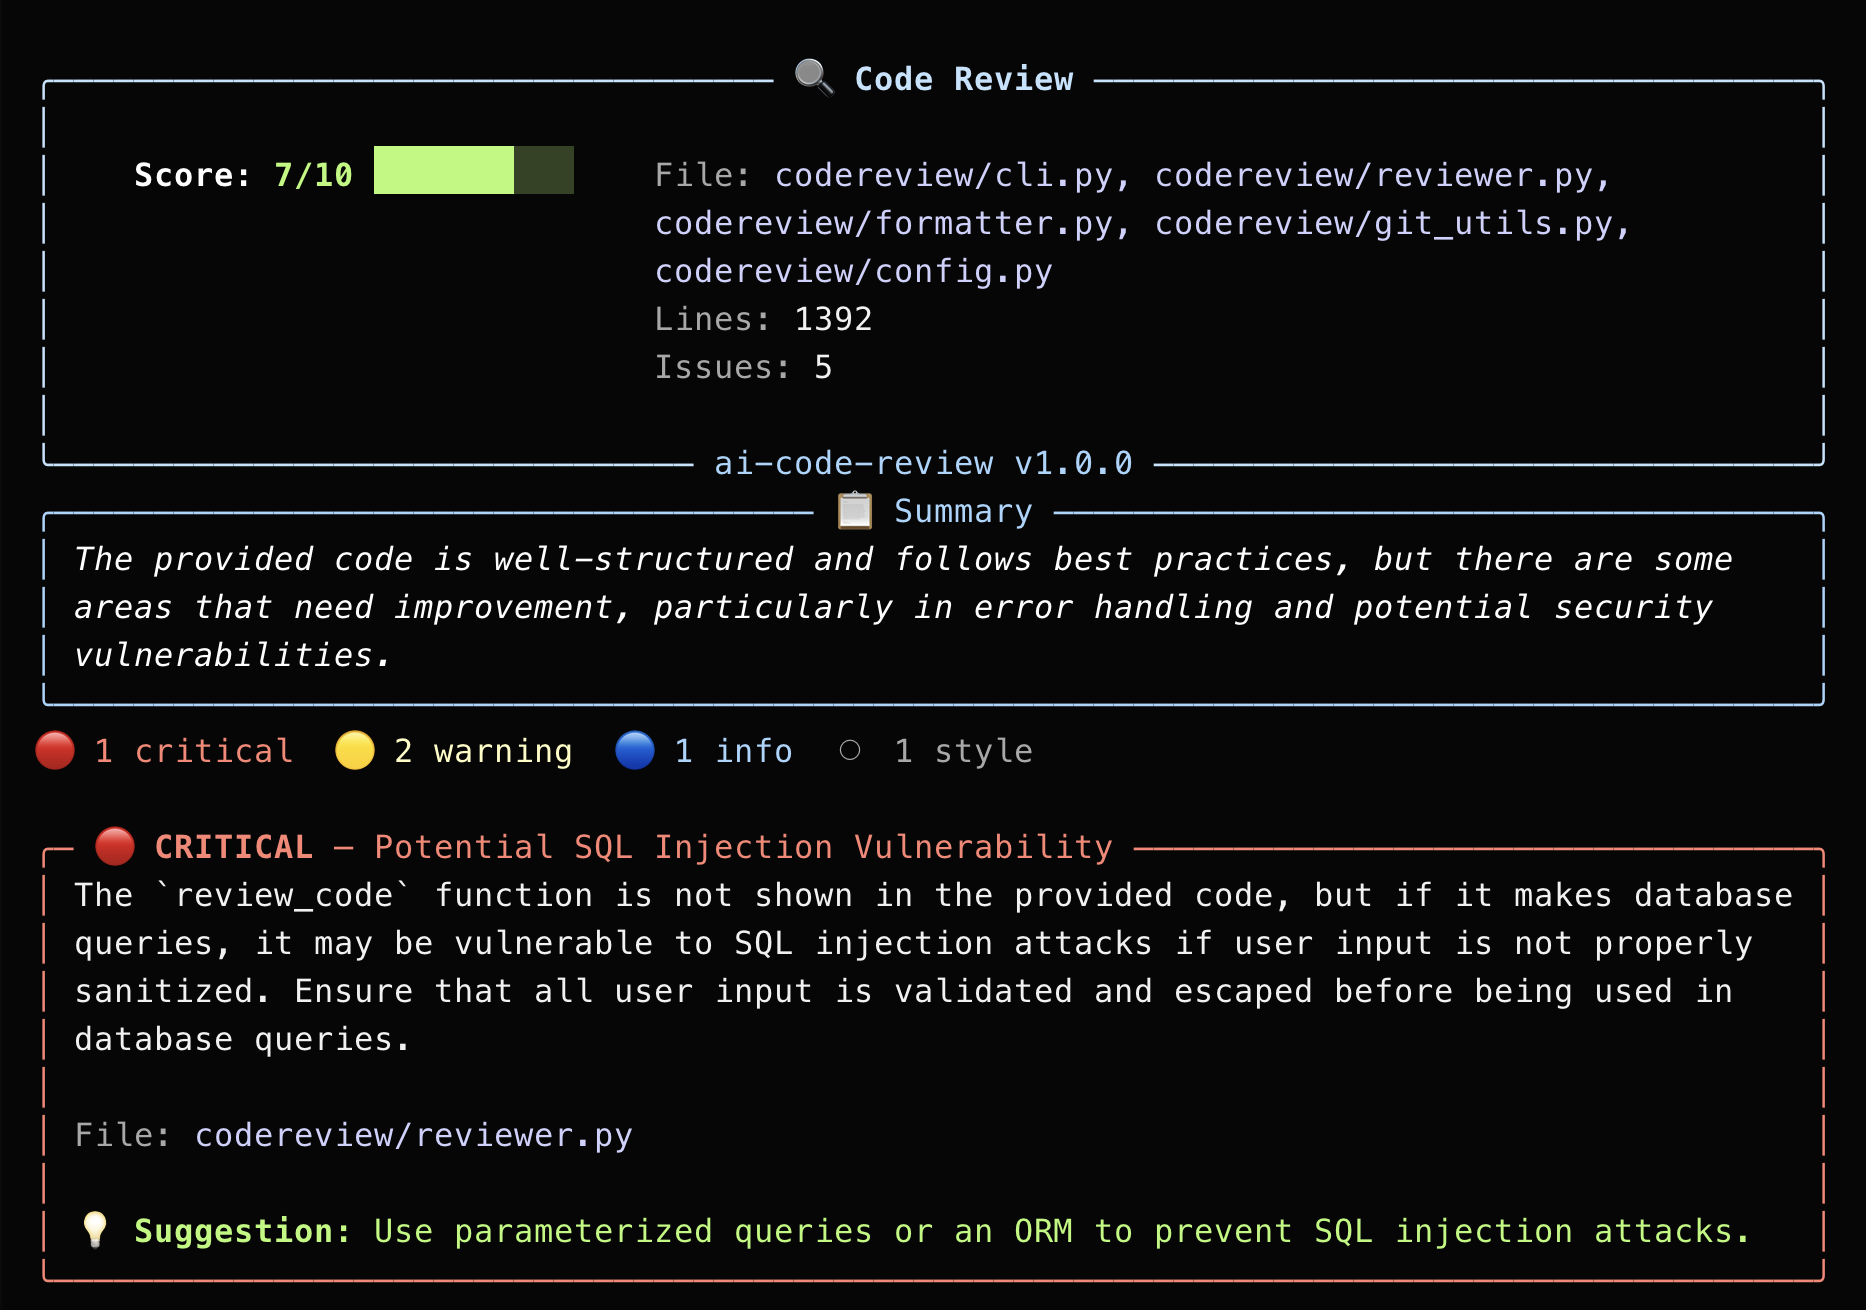
ai-code-review
 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
ai-securitycode-analysisdevsecops+5
3
jaydendancer12/ai-code-reviewAI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 oscerd/cve-2026-49042
PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 avito-tech/deepsecrets
Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 fransvanbuul/cve-2022-22965-susceptibility
Java-based tool to detect and test for CVE-2022-22965 (Spring4Shell) vulnerability in web applications, enabling security validation and exploitation…
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 s4dhul4bs/vimana-framework
Vimana is an experimental security tool that aims to provide resources for auditing Python web applications.
 parikhakshat/autoharness
A tool that automatically creates fuzzing harnesses based on a library
 hazcod/claudleak
Hunt for AI coding artifacts containing secrets.
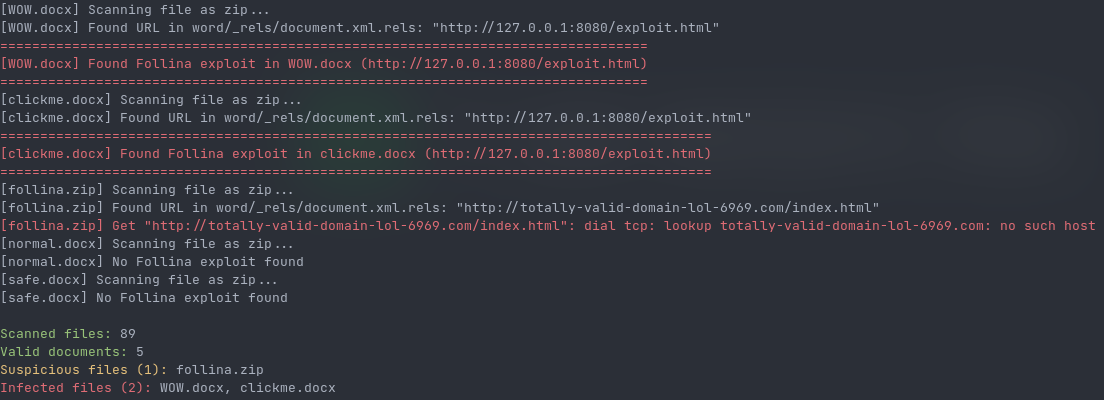 errornointernet/follinascanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 shri142/zipscan
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 shaikusaf/external_expact_aosp10_r33_cve-2022-25313
C library for stream-oriented XML parsing, providing handlers for parsing structures in documents. Includes xmlwf tool and supports UTF-16 encoding.
 akanthed/secureai-scan
SecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
 intrinsec/comission
White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…