
ply_exploit_rejection
 tom025/ply_exploit_rejection
Arguments to reject CVE-2025-56005
code-analysiseducationpapers-research+2
tom025/ply_exploit_rejectionArguments to reject CVE-2025-56005
 okanulkr/curveball-cve-2020-0601-poc
Proof-of-concept exploit for CVE-2020-0601 (CurveBall) demonstrating ECC certificate validation bypass to spoof trusted CA and sign arbitrary…

 haile01/perl_spreadsheet_excel_rce_poc
POC for RCE vulnerability in ParseExcel library, and ParseXLSX too, as a depending library
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 dani33339/tough-cookie-v2.5.0-patched
Patched tough-cookie v2.5.0 fixing CVE-2023-26136 prototype pollution vulnerability with Object.create(null) in MemoryCookieStore, including exploit…
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
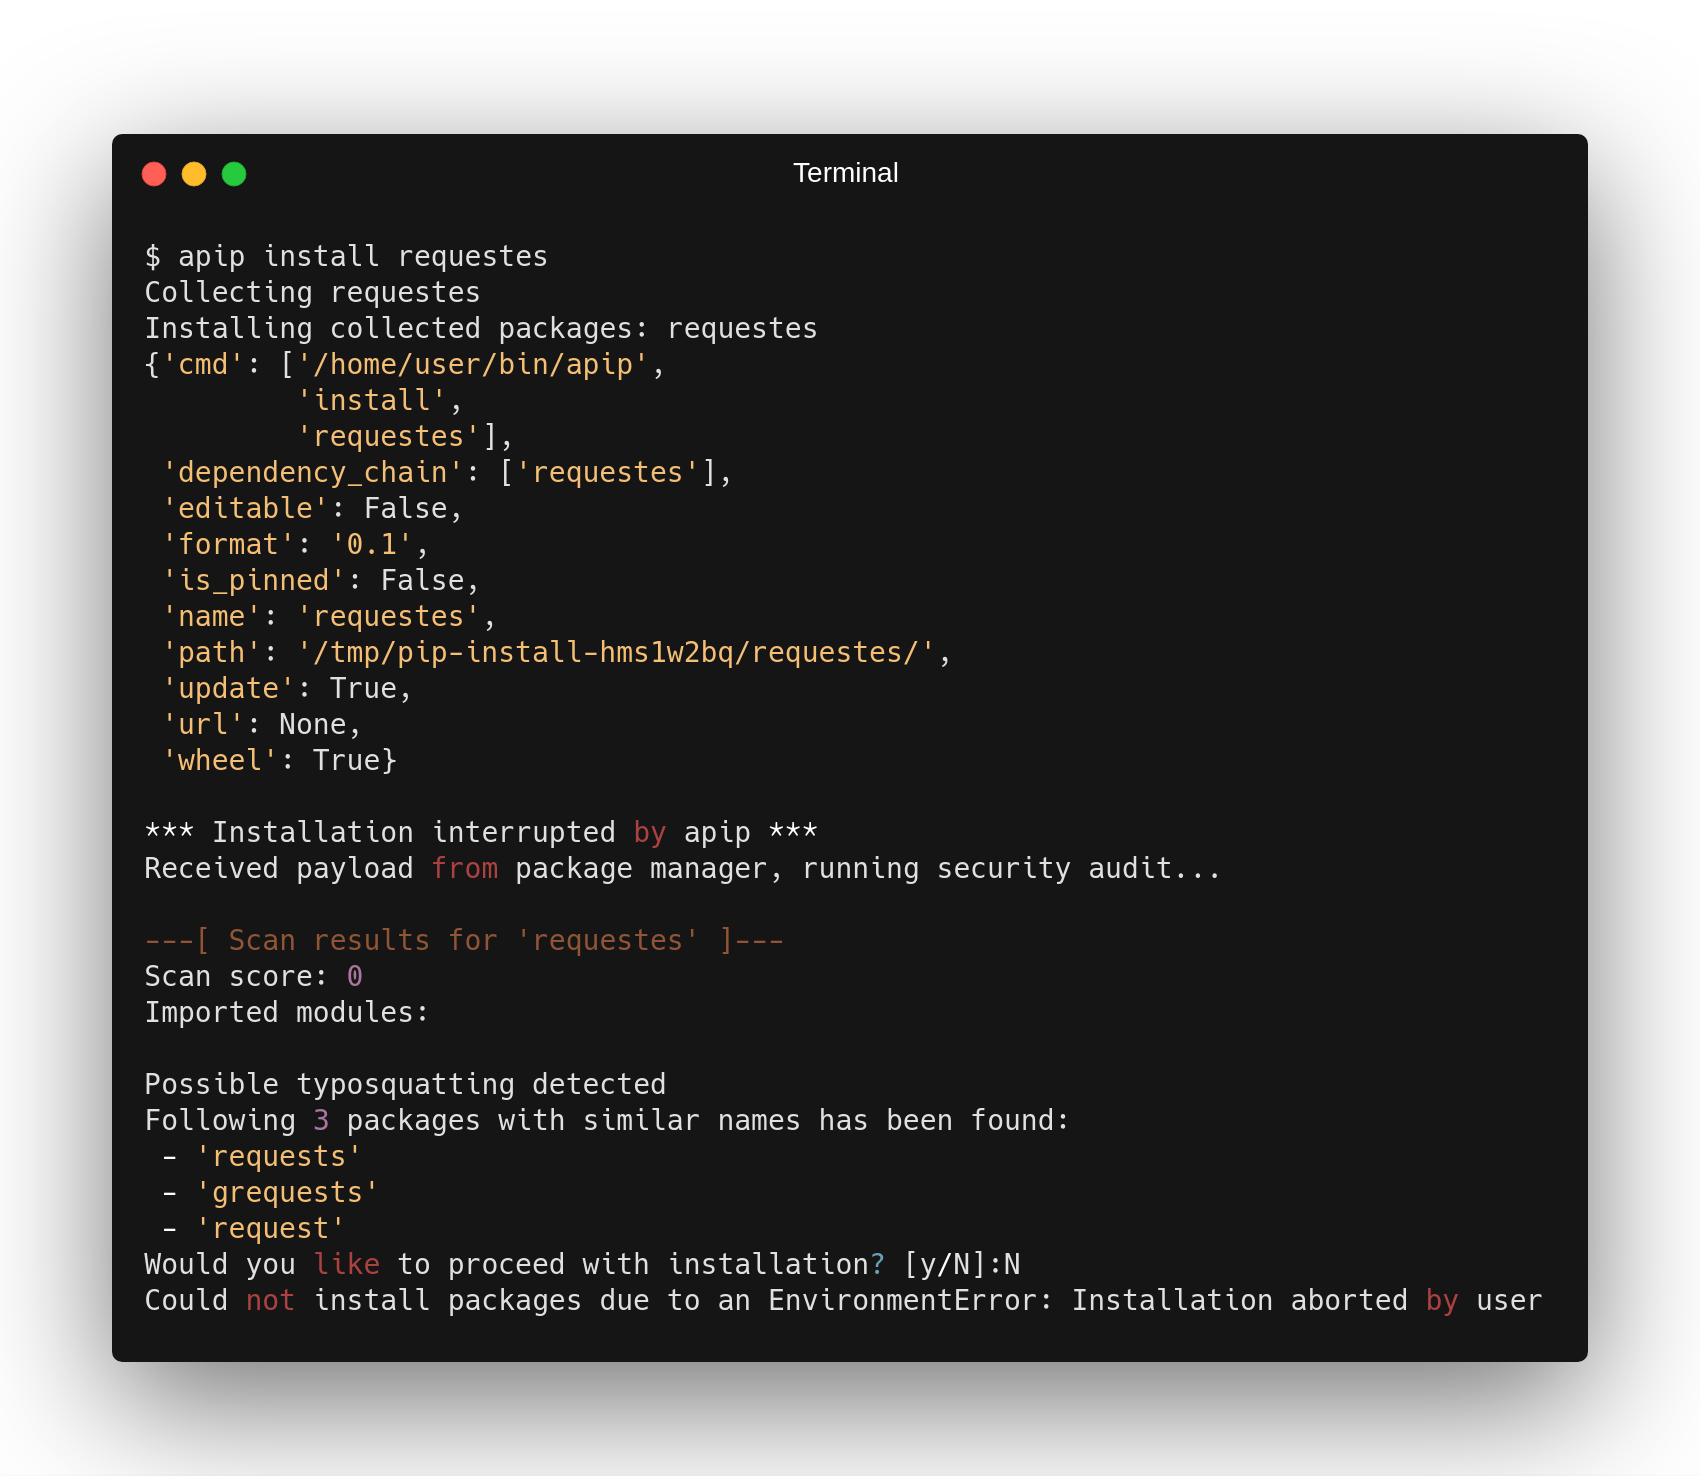 rootlug/aura
Project Aura: Security auditing and code introspection
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…
 releaseown/exploit-js2py
The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
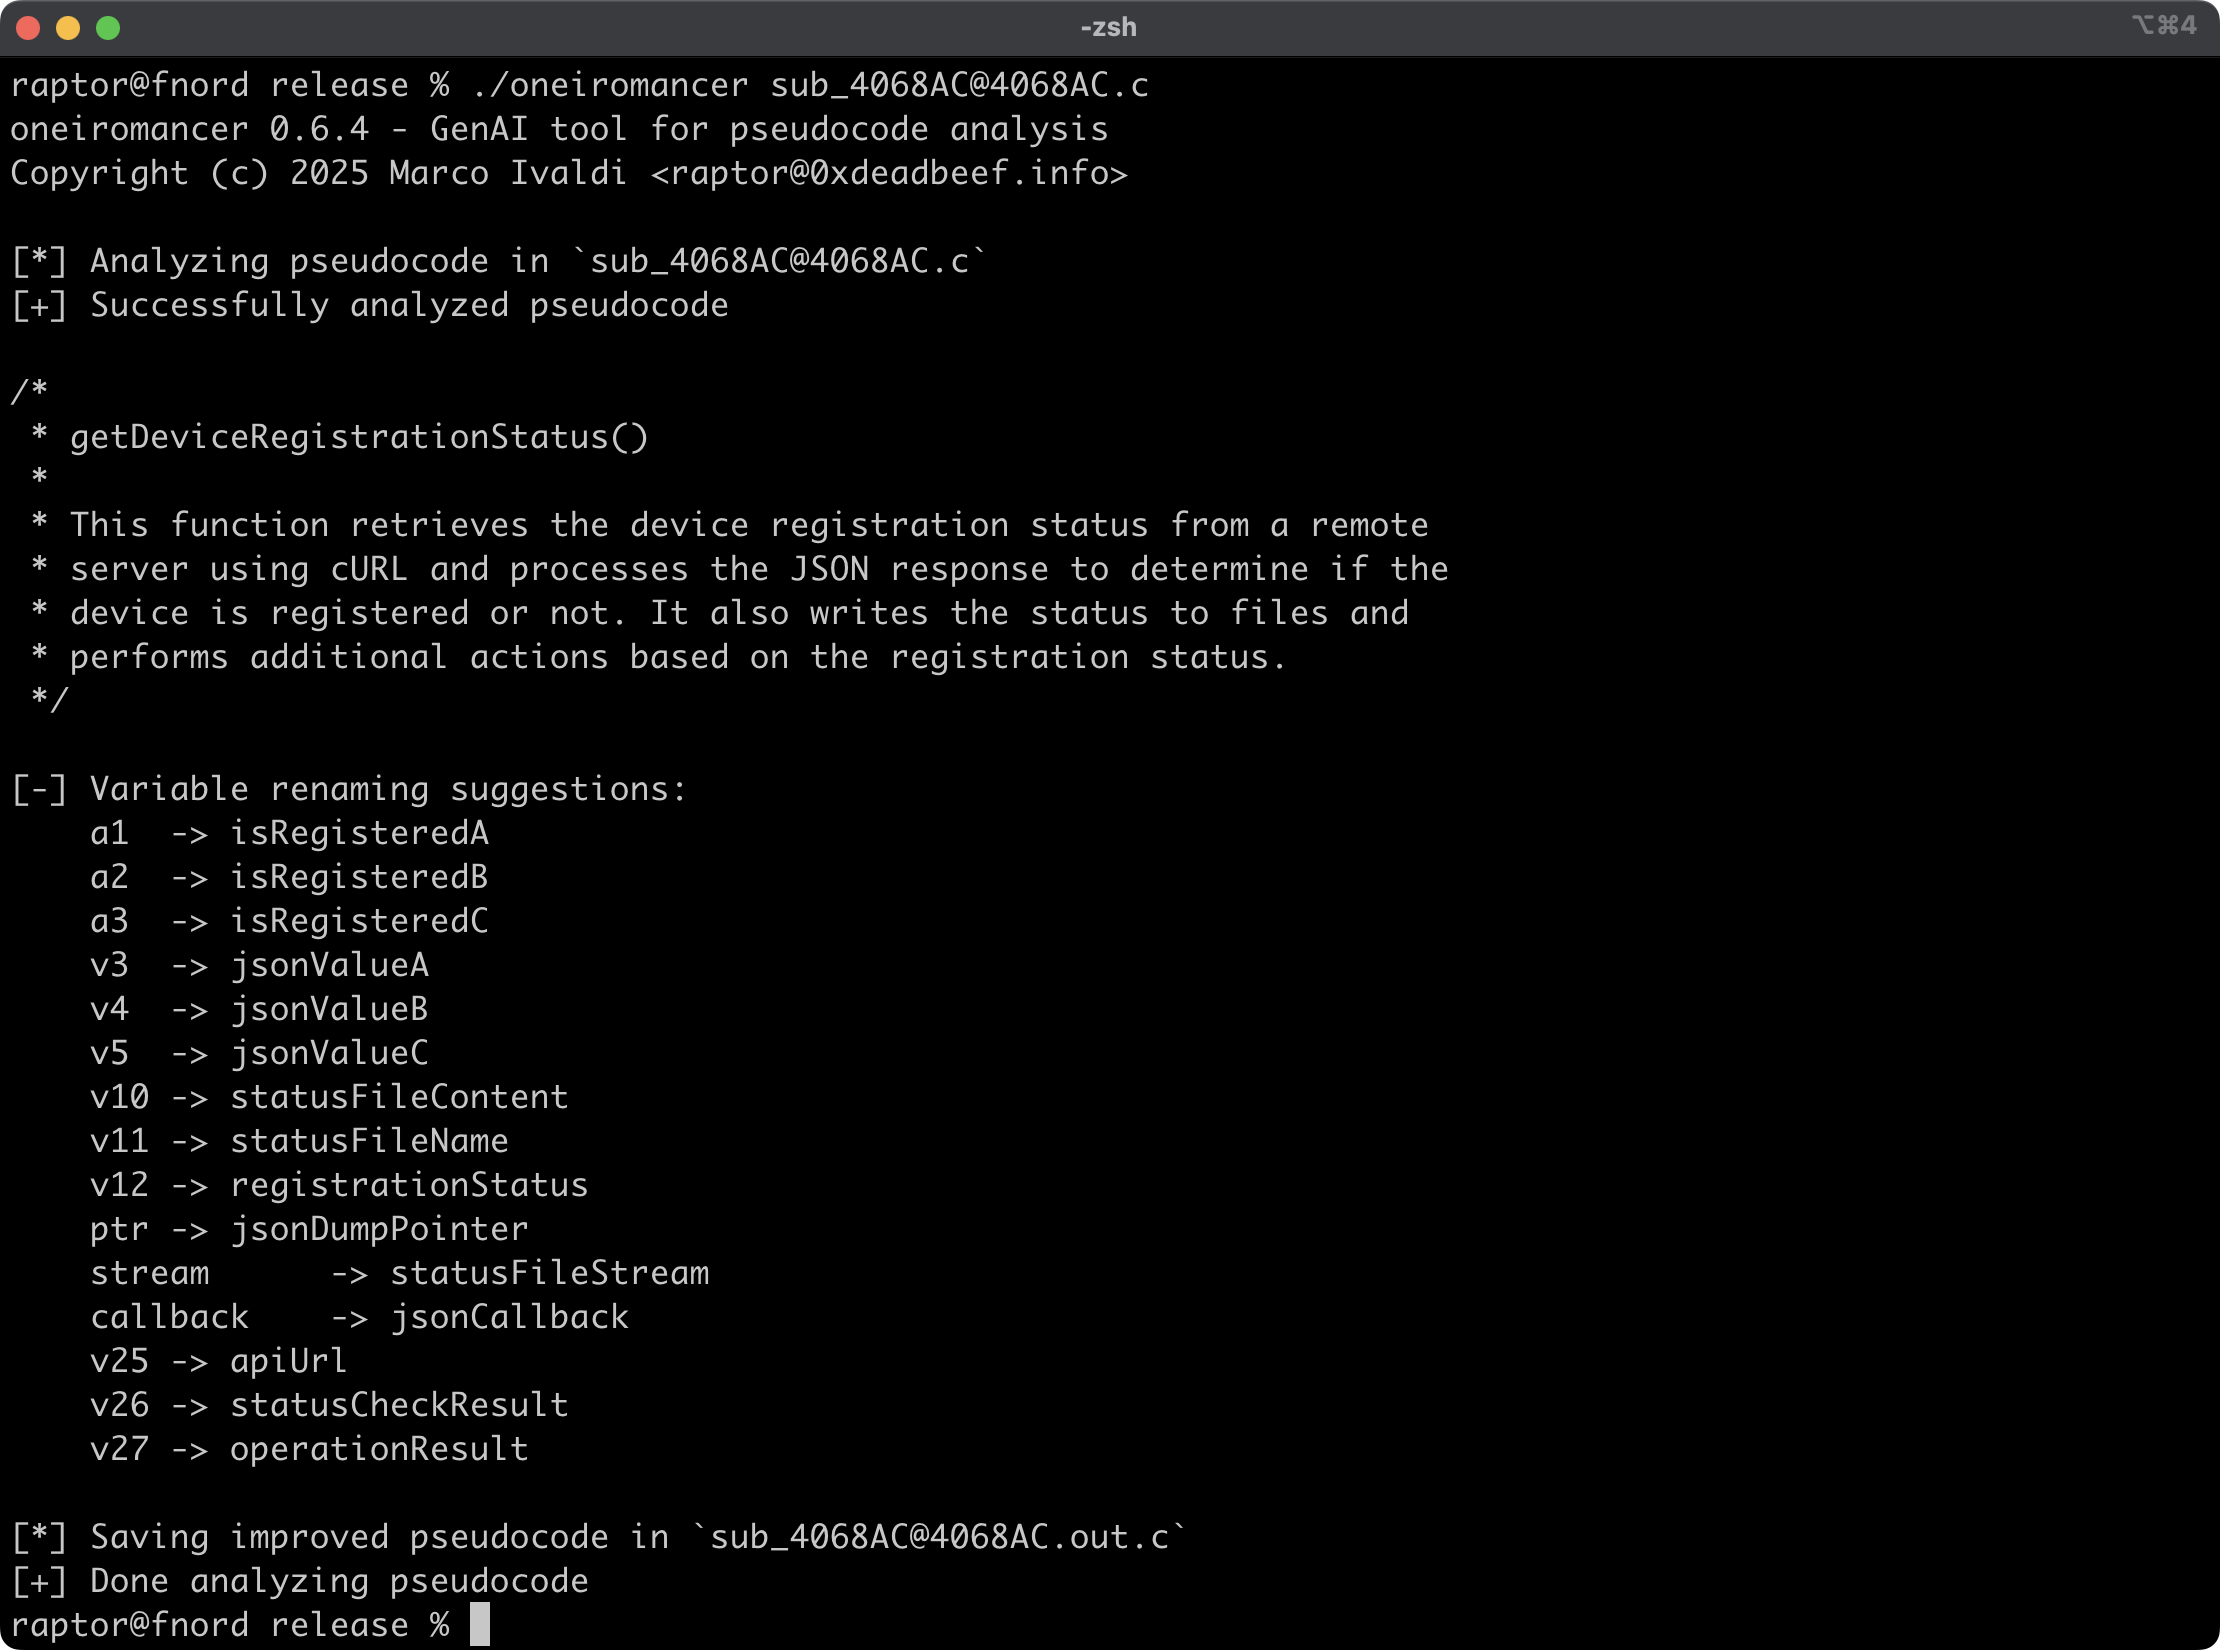 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 joakimbulow/cve-2026-48962
CVE-2026-48962 - IO::Compress - Code Execution
 nickops87/spring4shell-python-firewall-poc
Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…
 buiduchoang24/cve-2023-34040
In Spring for Apache Kafka 3.0.9 and earlier and versions 2.9.10 and earlier, a possible deserialization attack vector existed, but only if unusual…