

jenkins-cve-2016-0792
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
code-analysisdynamic-code-analysisexploitation+3
47
jpiechowka/jenkins-cve-2016-0792Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
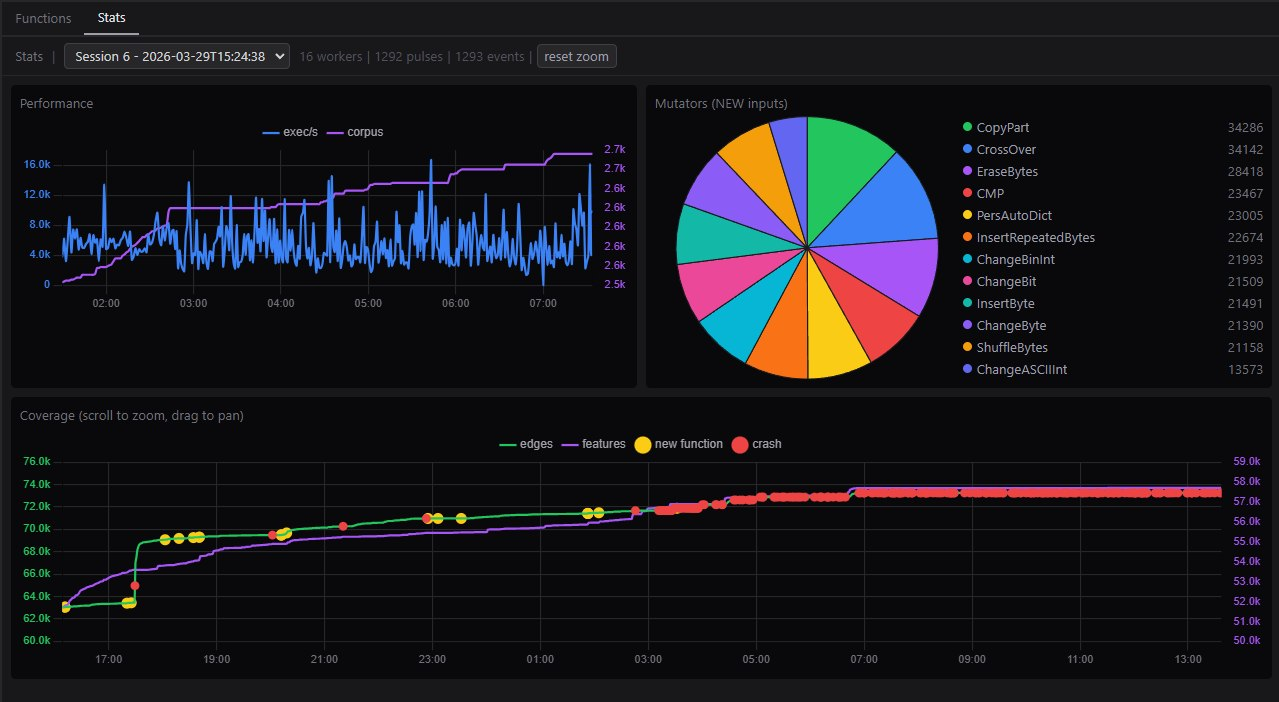 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…
 zack0x01/vuln-app-cve-2025-55182
Intentionally vulnerable Next.js application demonstrating CVE-2025-55182 RCE via unsafe deserialization in React Server Components. Includes exploit…
 andrenasx/cve-2015-10034
Demonstrates CVE-2015-10034 in a vulnerable Java application, including SARIF analysis results from J-TAS Action for educational security testing.
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
 tamaloa/avo-cve-2024-22411
Proof-of-concept exploit for CVE-2024-22411 targeting the Avo admin panel. Demonstrates vulnerability exploitation in Ruby-based web applications.
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
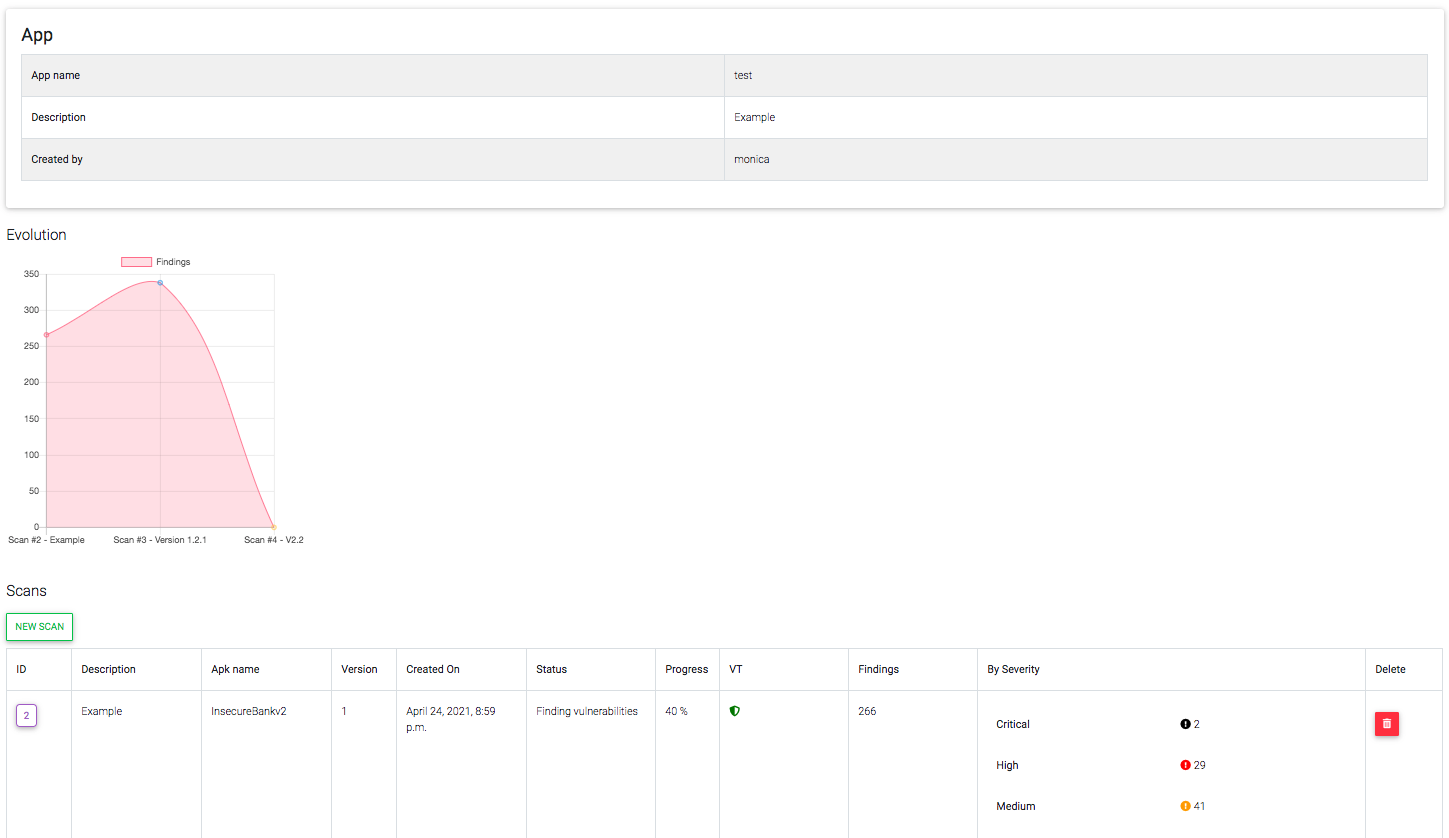 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
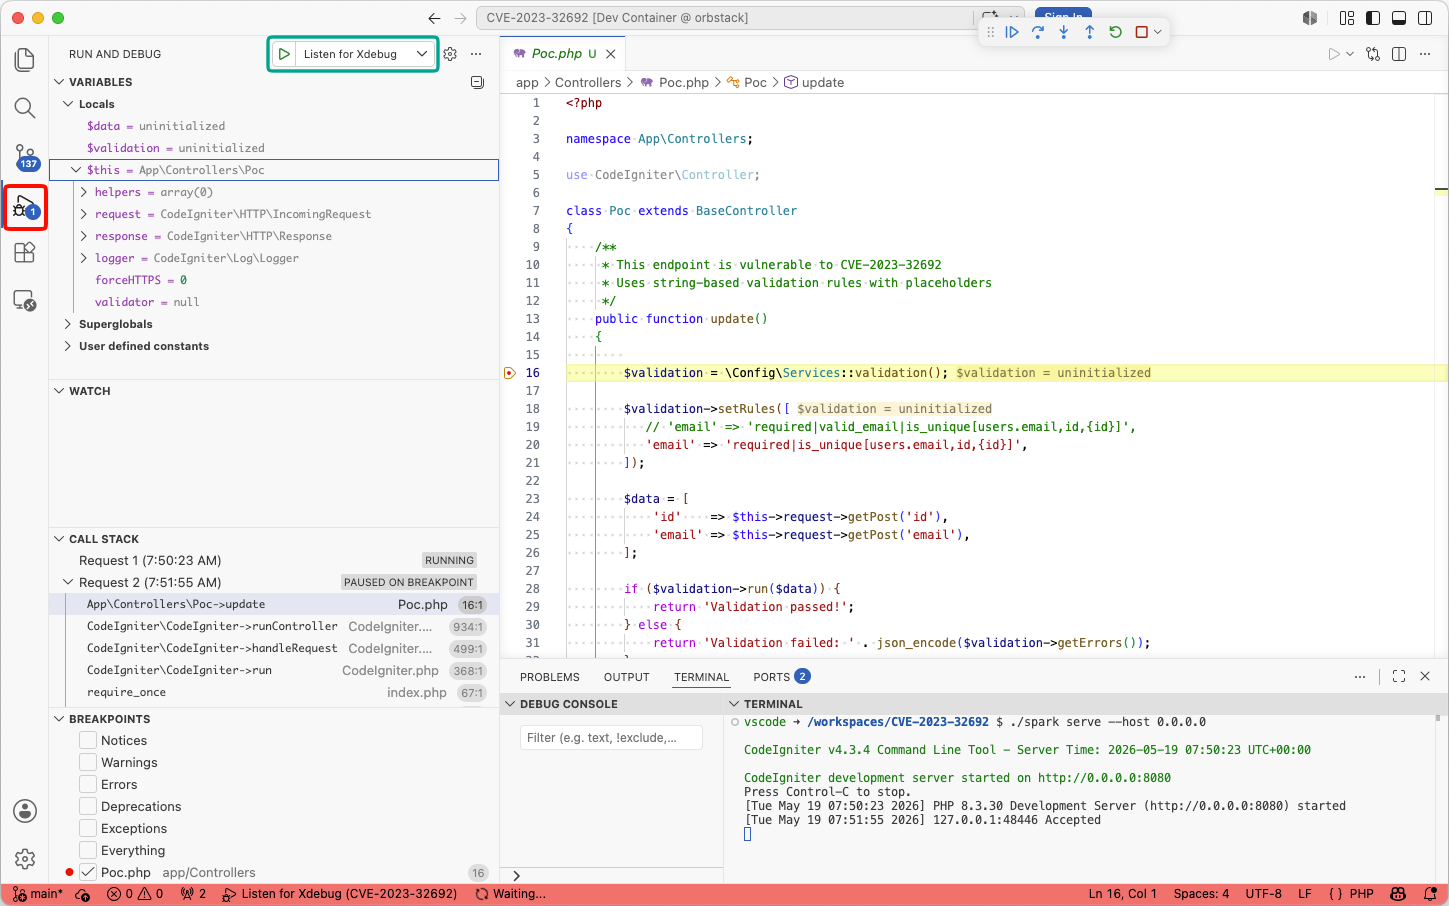 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 kov404/cve-2025-56515
Cross-Site Scripting (XSS) Vulnerability in Fiora Chat Application
 yosasasutsut/cve-2025-56803
OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application
 theratpack/grails-javamelody-sample-app
Grails sample application using the Javamelody 1.44 plugin to illustrate the CVE-2013-4378 vulnerability.
