
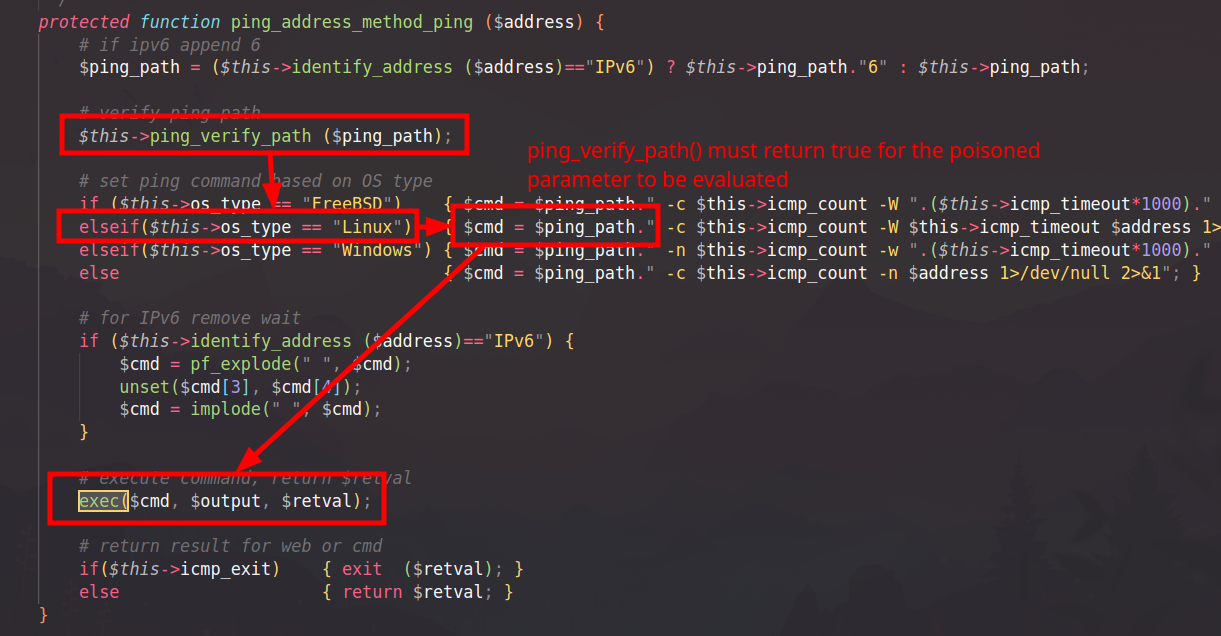
CVE-2024-55187
 mallo-m/cve-2024-55187
Detailed CVE-2024-55187 advisory with proof-of-concept for a remote code execution vulnerability in phpIpam, exploiting path poisoning and PHAR file…
code-analysiseducationexploitation+3
mallo-m/cve-2024-55187Detailed CVE-2024-55187 advisory with proof-of-concept for a remote code execution vulnerability in phpIpam, exploiting path poisoning and PHAR file…
 klassiker/cve-2025-55182
CodeQL-based analysis of CVE-2025-55182 prototype pollution vulnerability in React Server Components, with exploit POC and static detection queries…
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 degenwithheart/react2shell-vulnerability-verification-script
Standalone Python script to verify if a project is affected by CVE-2025-55182 (React2Shell). Checks package.json dependencies and performs optional…
 shoucheng3/jenkinsci__workflow-cps-global-lib-plugin_cve-2022-25174_544-vff04fa68714d
Exploit for CVE-2022-25174 in Jenkins Pipeline Shared Libraries plugin, demonstrating code injection via crafted library definitions for security…
 anchor0221/cve-2025-50460
Technical Details and Exploit for CVE-2025-50460
 uriyahav/tough-cookie-2.5.0-cve-2023-26136-fix
ecurity patch for CVE-2023-26136 in tough-cookie 2.5.0 - Prototype pollution vulnerability fix with backward compatibility
 naved124/cve-2024-28397-js2py-sandbox-escape
Detailed analysis of CVE-2024-28397, a sandbox escape vulnerability in js2py enabling RCE via Python object traversal. Includes code analysis, PoC,…
 zhangyongbo100/-ruby-dl-handle.c-cve-2009-5147-
Community-maintained database of Ruby gem security advisories with structured CVE data, CVSS scores, and patched version requirements. Integrates…
 phzietsman/batchoverflow
A fix for the batchOverflow bug https://medium.com/@peckshield/alert-new-batchoverflow-bug-in-multiple-erc20-smart-contracts-cve-2018-10299-511067db65…
 shoucheng3/srikanth-lingala__zip4j_cve-2018-1002202_1-3-2
Decompiled source code of zip4j library versions 1.3.2 (vulnerable) and 1.3.3 (fixed) for CVE-2018-1002202 path traversal analysis, part of the…
 rootd4ddy/cve-2023-31584
Public disclosure for CVE-2023-31584.
 trinadh465/platform_art_cve-2021-0394
Analyzes and demonstrates the Android Runtime vulnerability CVE-2021-0394, providing code-level insights for security researchers and developers.
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 shoucheng3/hibernate__hibernate-validator_cve-2019-10219_6_0_18_final_fixed
Reference implementation of Bean Validation 2.0 (JSR-380) with annotation-based metadata model and method validation for JavaBeans, including a…
 pandante-central/cve-2023-24329-codeql-test
CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.
 satheesh575555/external_expat_aosp10_r33_cve-2022-23852
C library for parsing XML, patched for CVE-2022-23852, providing stream-oriented XML parsing with handlers for efficient document processing.
 morrisel/cve-2023-26136
This repository contains a solution for the CVE-2023-26136 vulnerability.