
tplmap
 epinna/tplmap
Server-Side Template Injection and Code Injection Detection and Exploitation Tool
code-analysisexploitationpenetration-testing+2
epinna/tplmapServer-Side Template Injection and Code Injection Detection and Exploitation Tool
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 pyupio/safety
Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
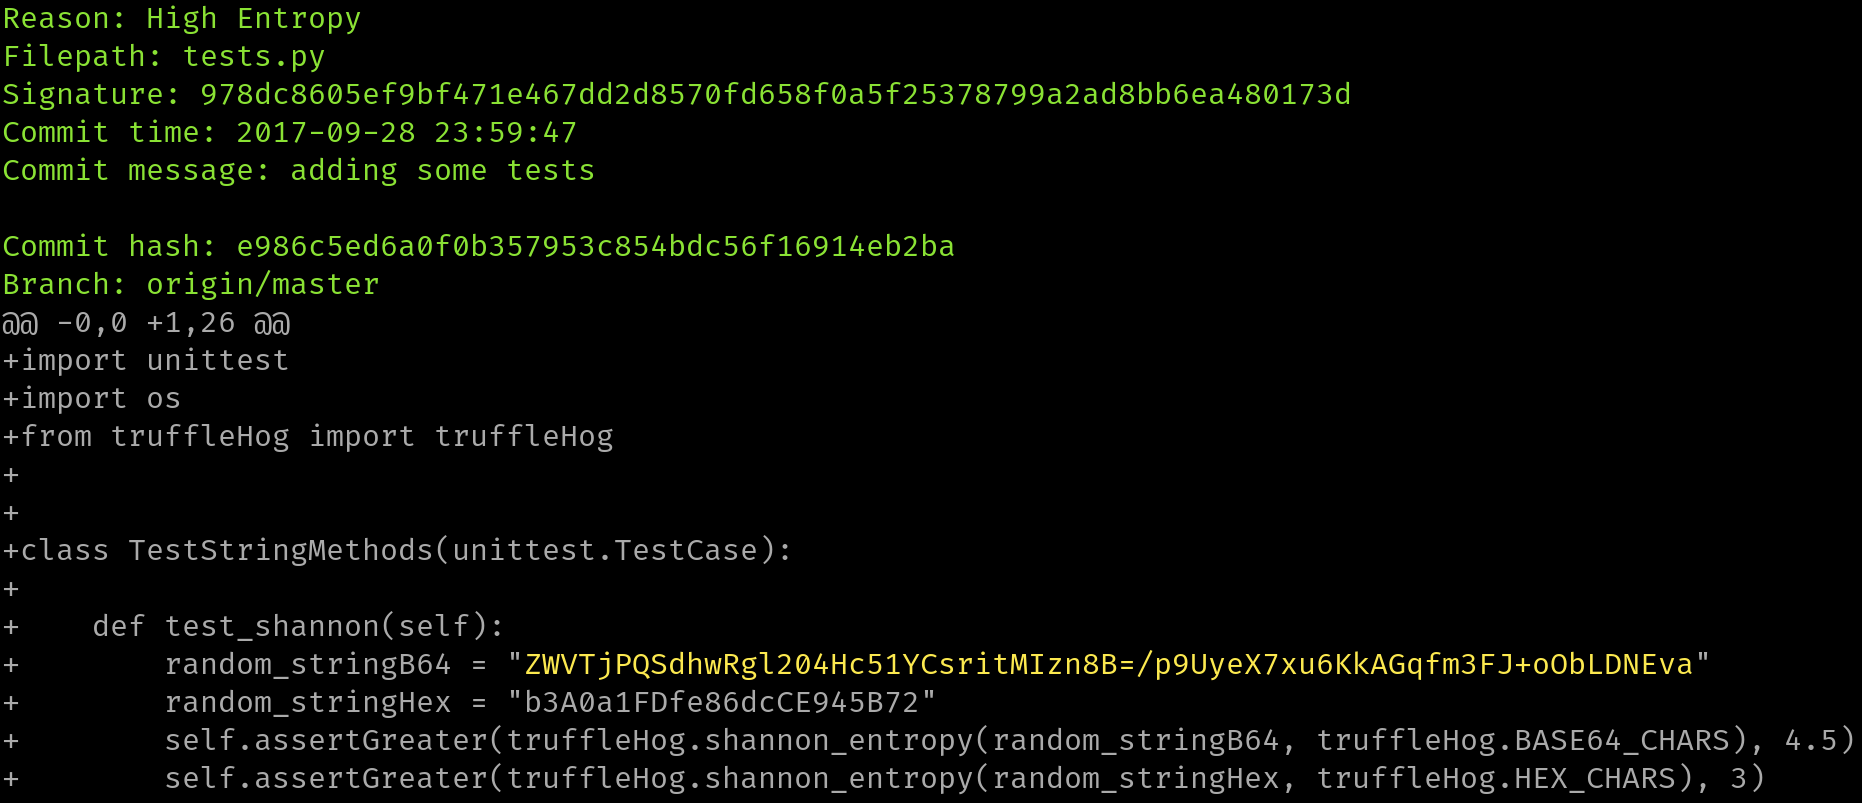 godaddy/tartufo
Searches through git repositories for high entropy strings and secrets, digging deep into commit history
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 nccgroup/freddy
Automatically identify deserialisation issues in Java and .NET applications by using active and passive scans
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 faloker/purify
All-in-one tool for managing vulnerability reports from AppSec pipelines
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.