

hermes-decomp
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
ai-assisted-reversingandroid-securitybinary-analysis+8
178
symbioticsec/hermes-decompA powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 eqstlab/cve-2024-8353
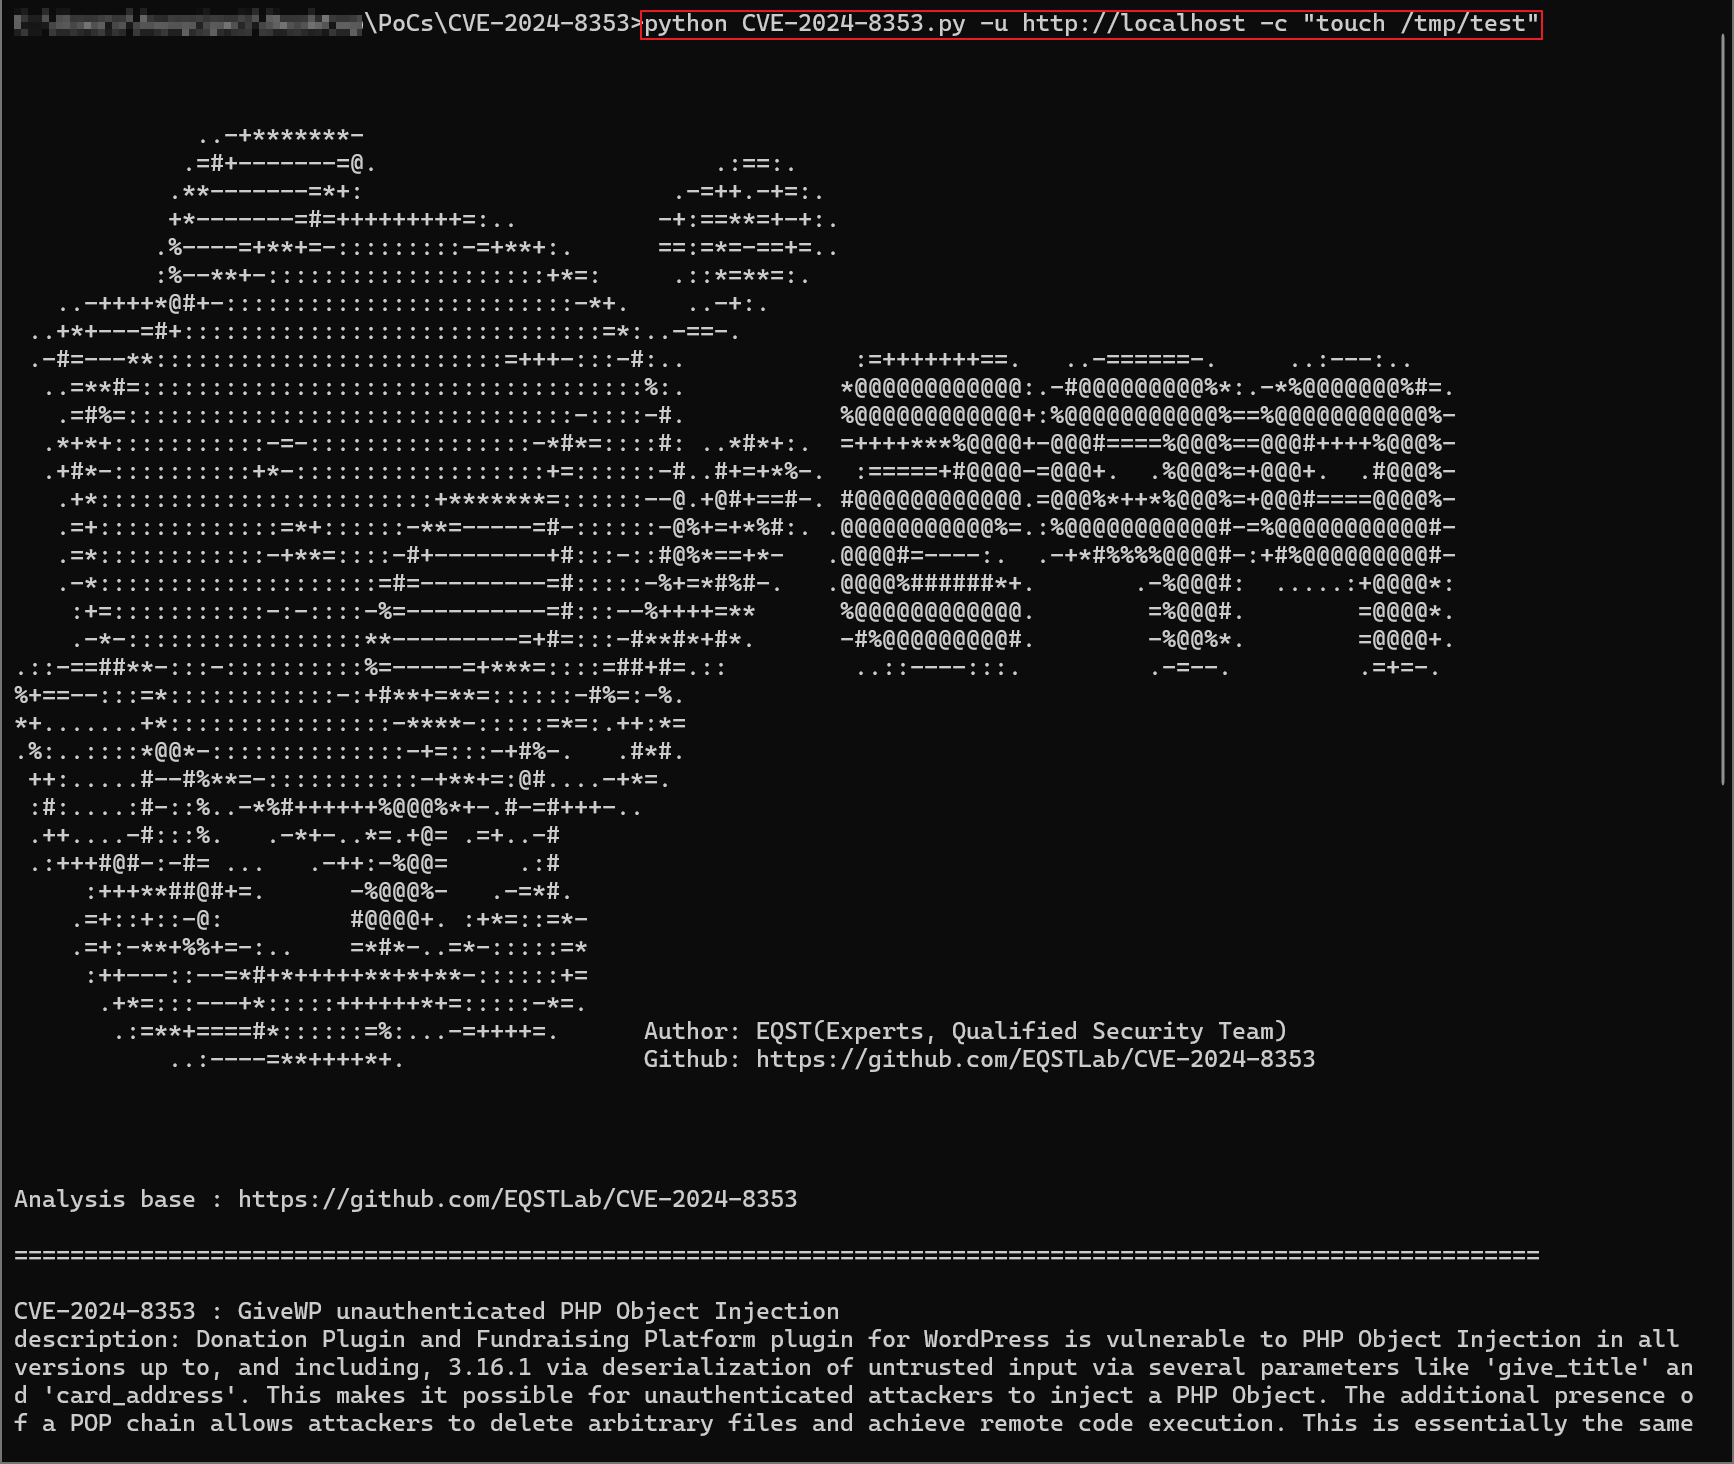
GiveWP PHP Object Injection exploit
 error-inside/cve-2026-47670
Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
 w2xim3/cve-2023-6933
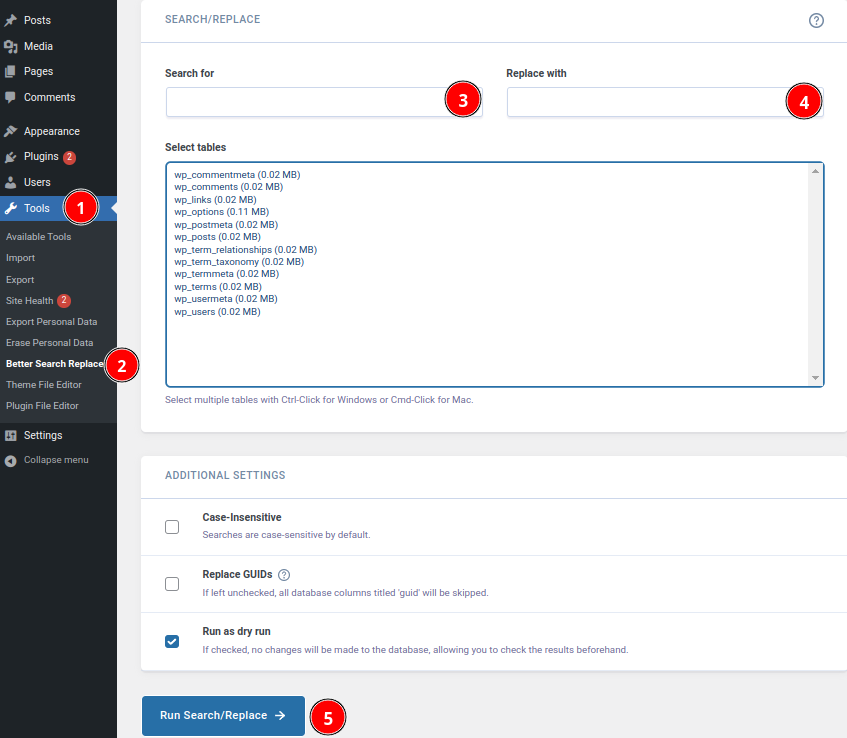
Introduction to CVE-2023-6933 Vulnerability
 praetorian-inc/noseyparker
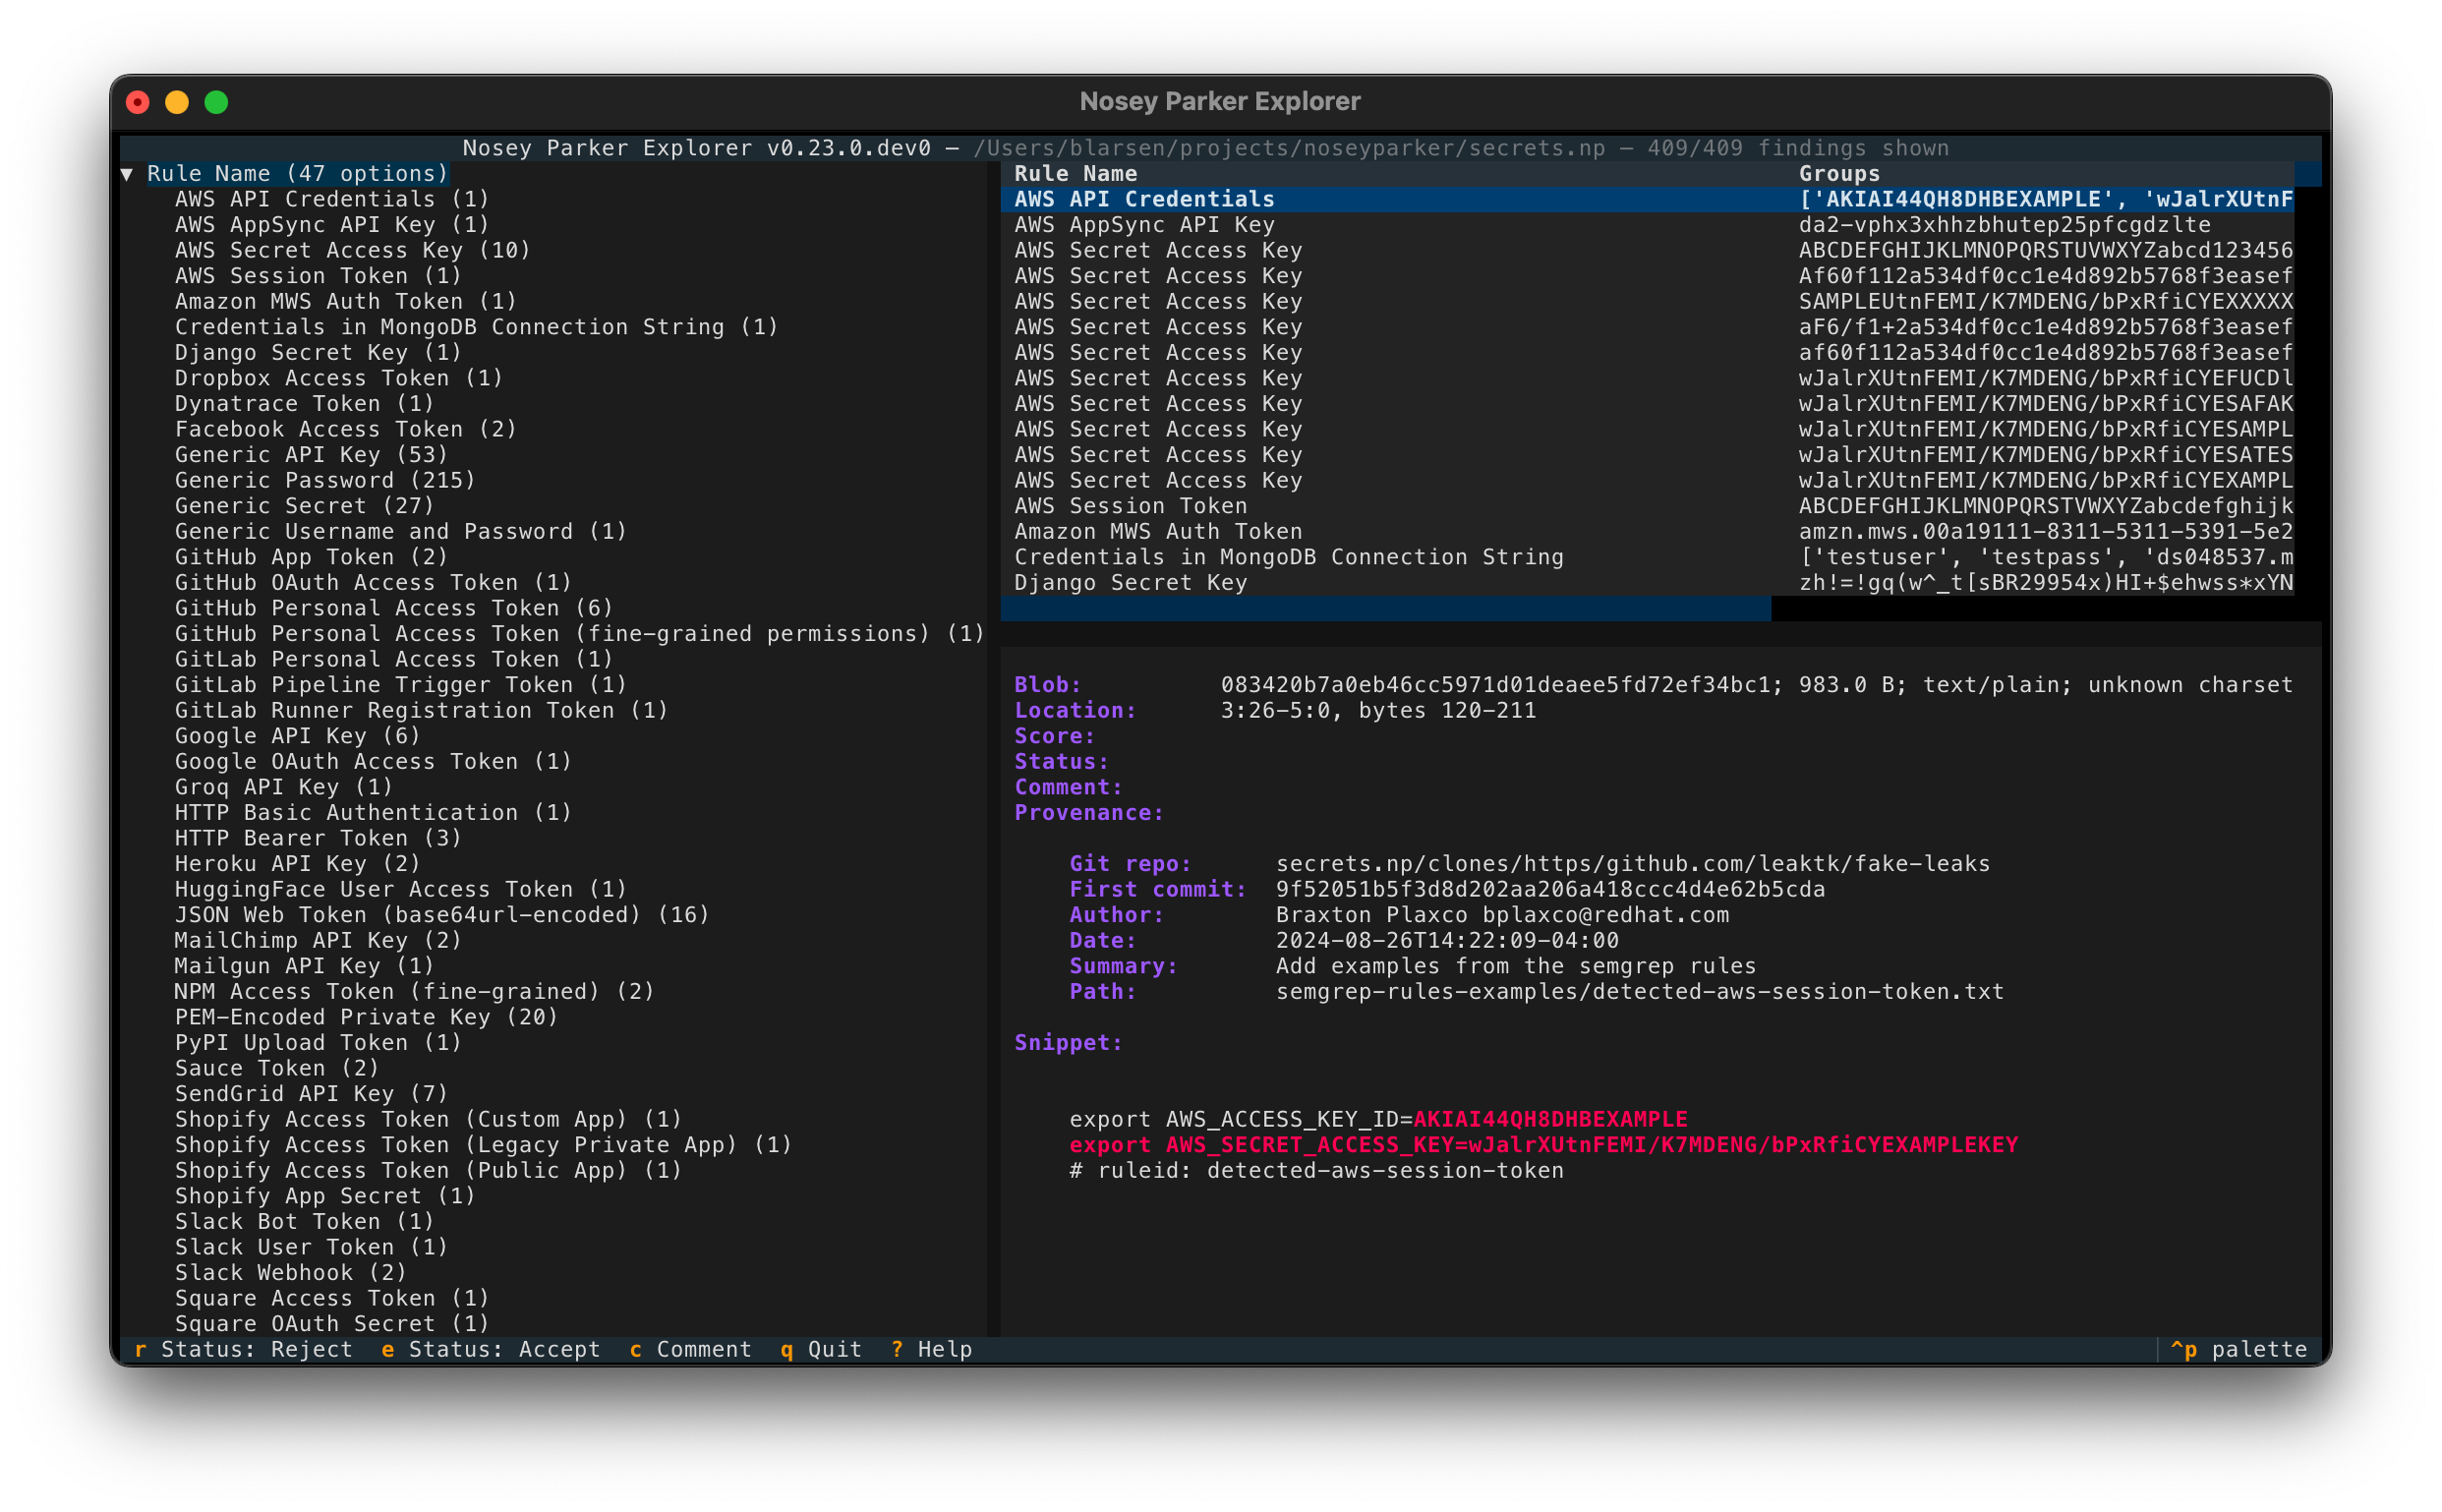
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
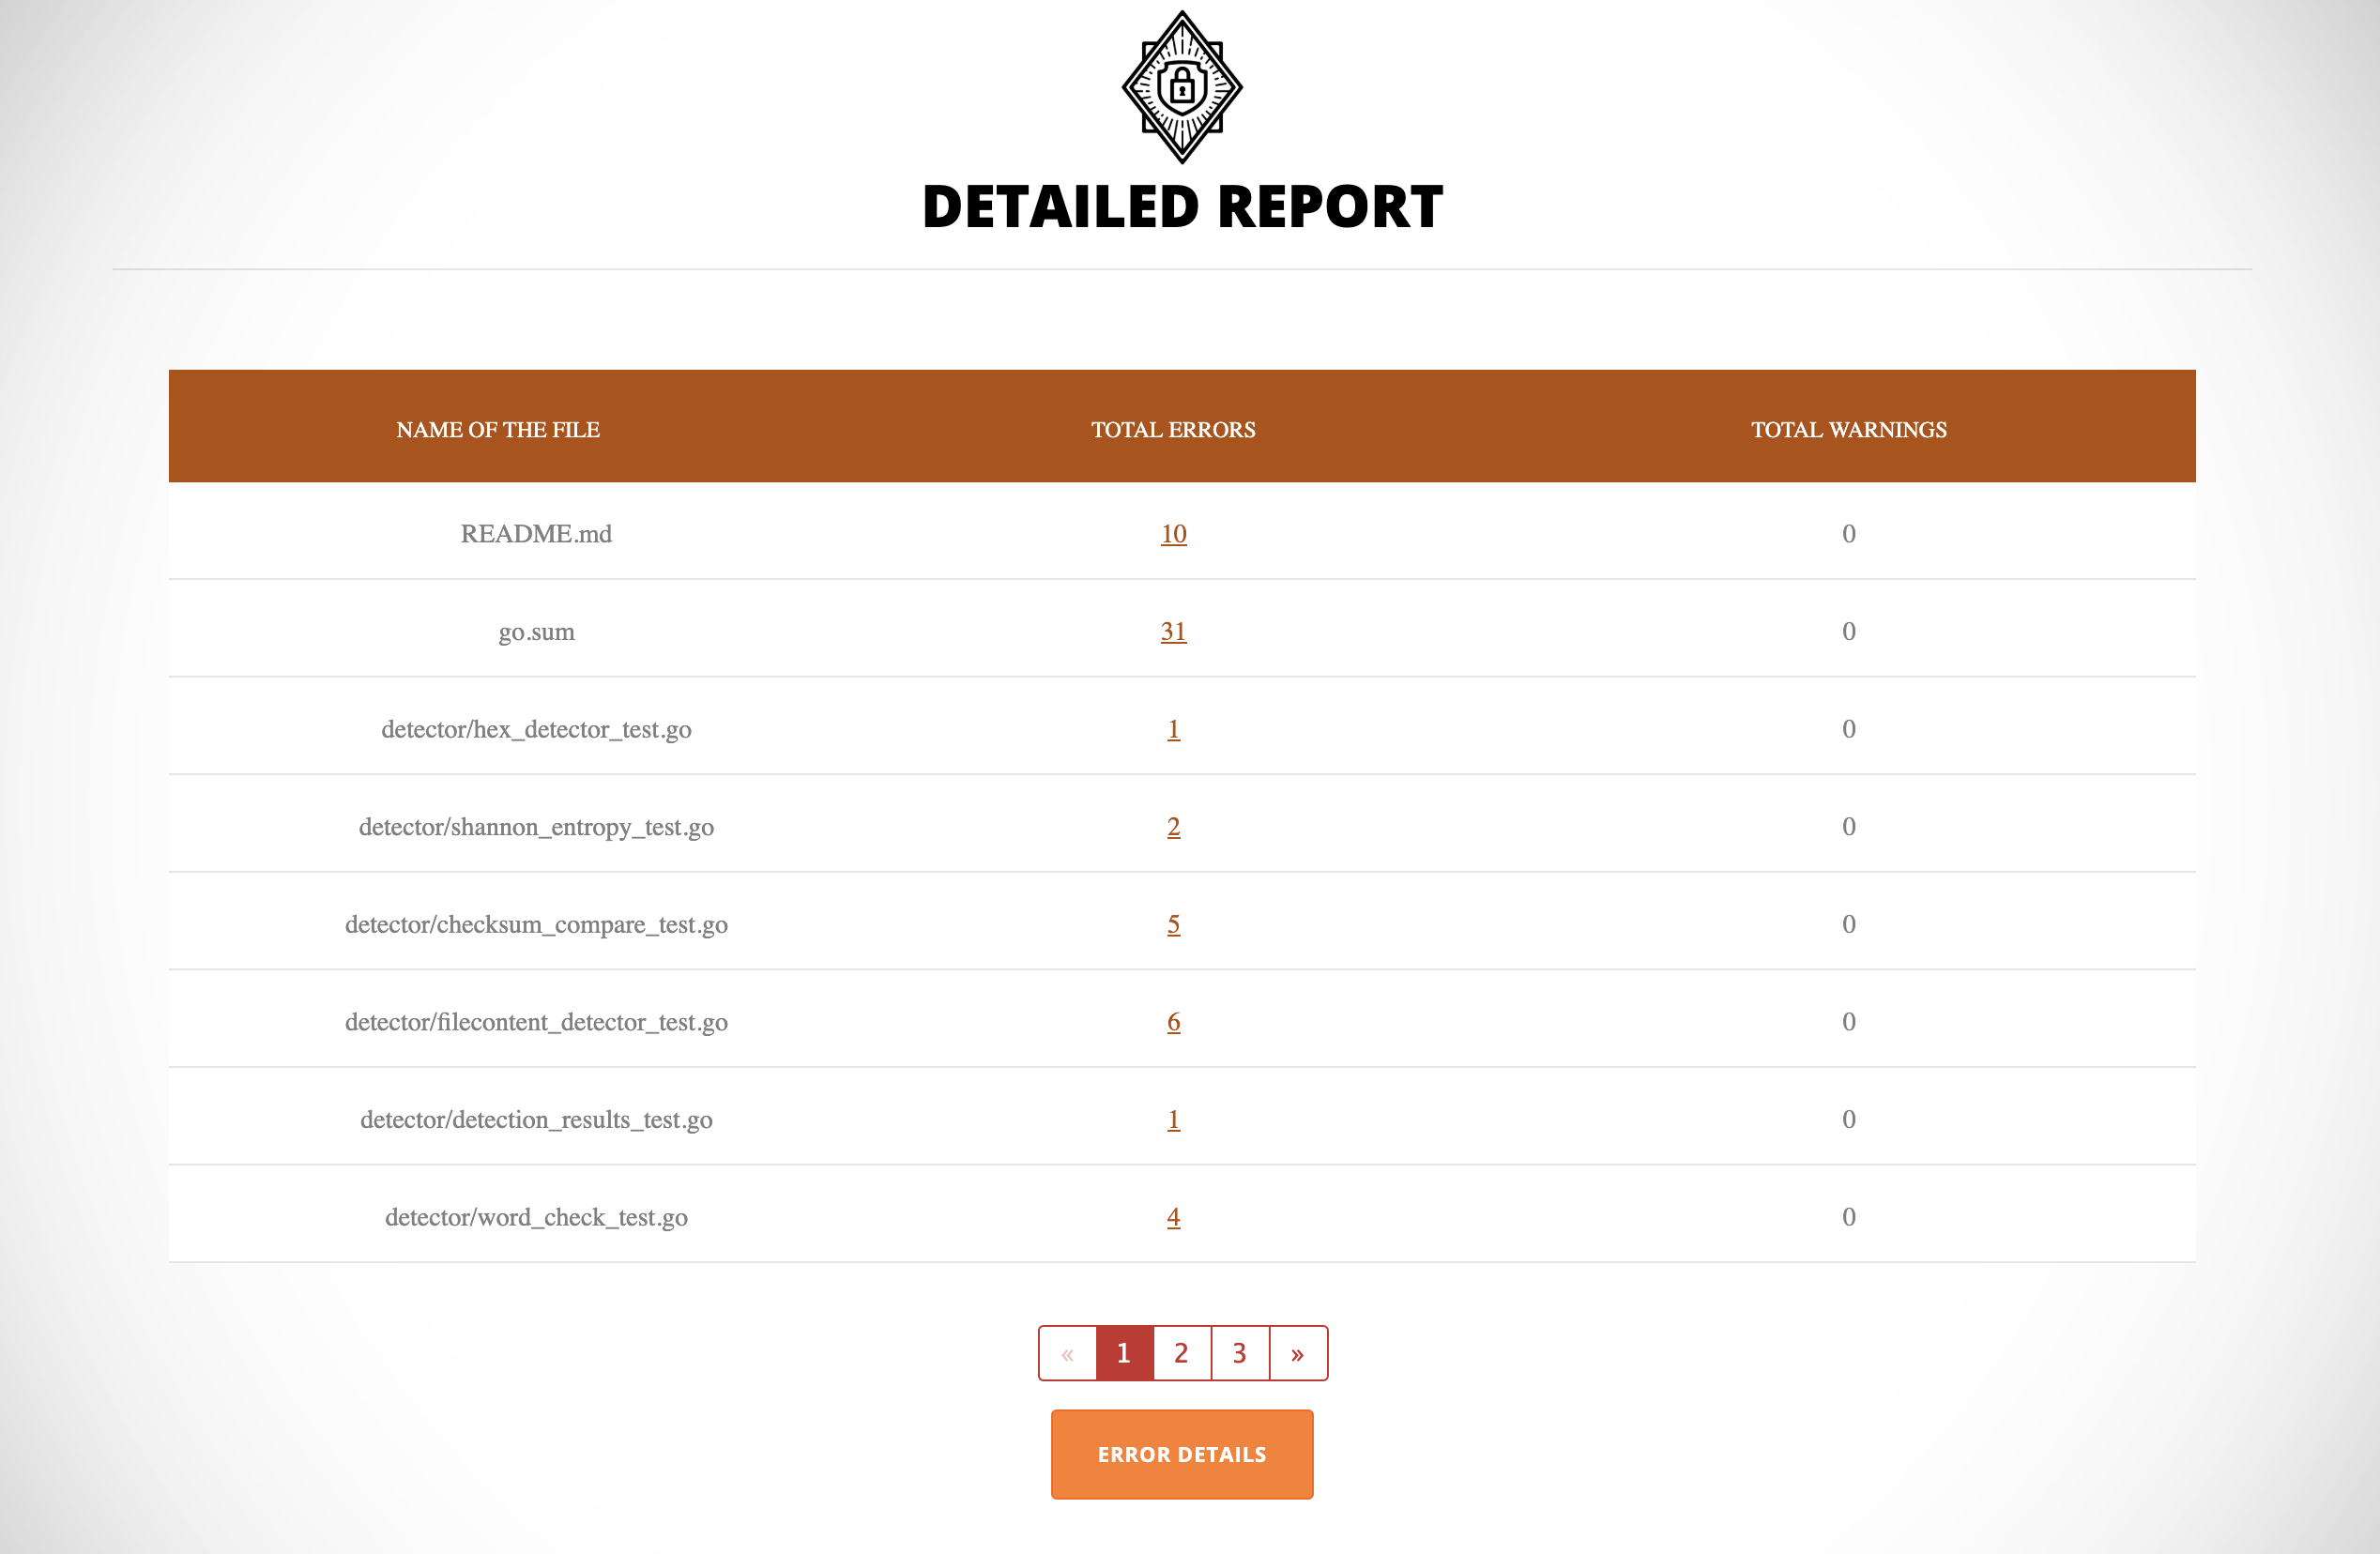 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
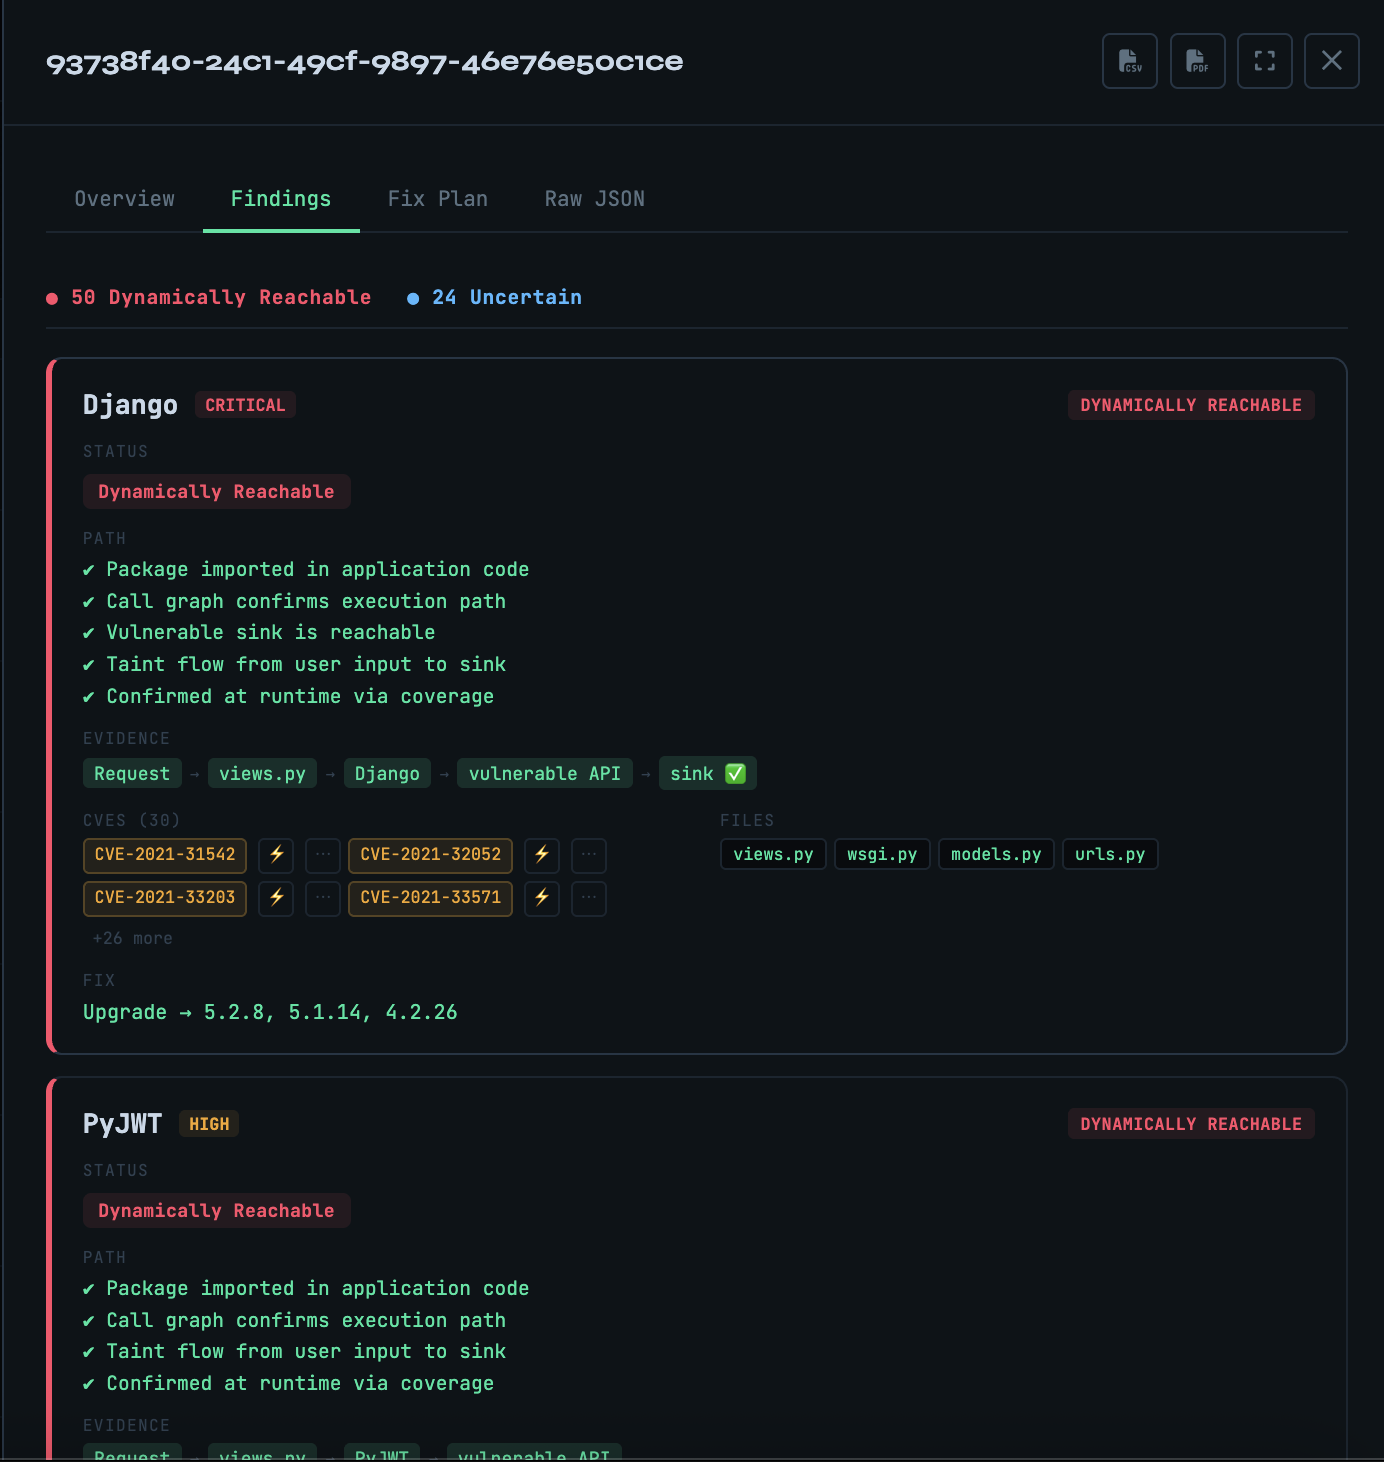 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 dedellix/mut-bc-ss-01
Mutation testing on X.509 Certificate Validation IN OpenSSL v.1.1.1h, based on CVE-2021-3450.
 tranquac/openplc_v3
To reproduce CVE-2021-31630
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 sektioneins/pcc
Automated PHP configuration auditor that scans php.ini for security misconfigurations, supports CLI and web modes, and outputs results in text, HTML,…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 akanthed/secureai-scan
SecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 trailofbits/claude-code-devcontainer
Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.
 gamesarchive/cve-2025-48543
Proof-of-concept exploit for CVE-2025-48543, written in C++. Demonstrates exploitation of a specific vulnerability for security testing and research…