ESAPI__esapi-java-legacy_CVE-2022-23457_2-2-3-1

Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…

Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…

The dependency-check repository has moved:

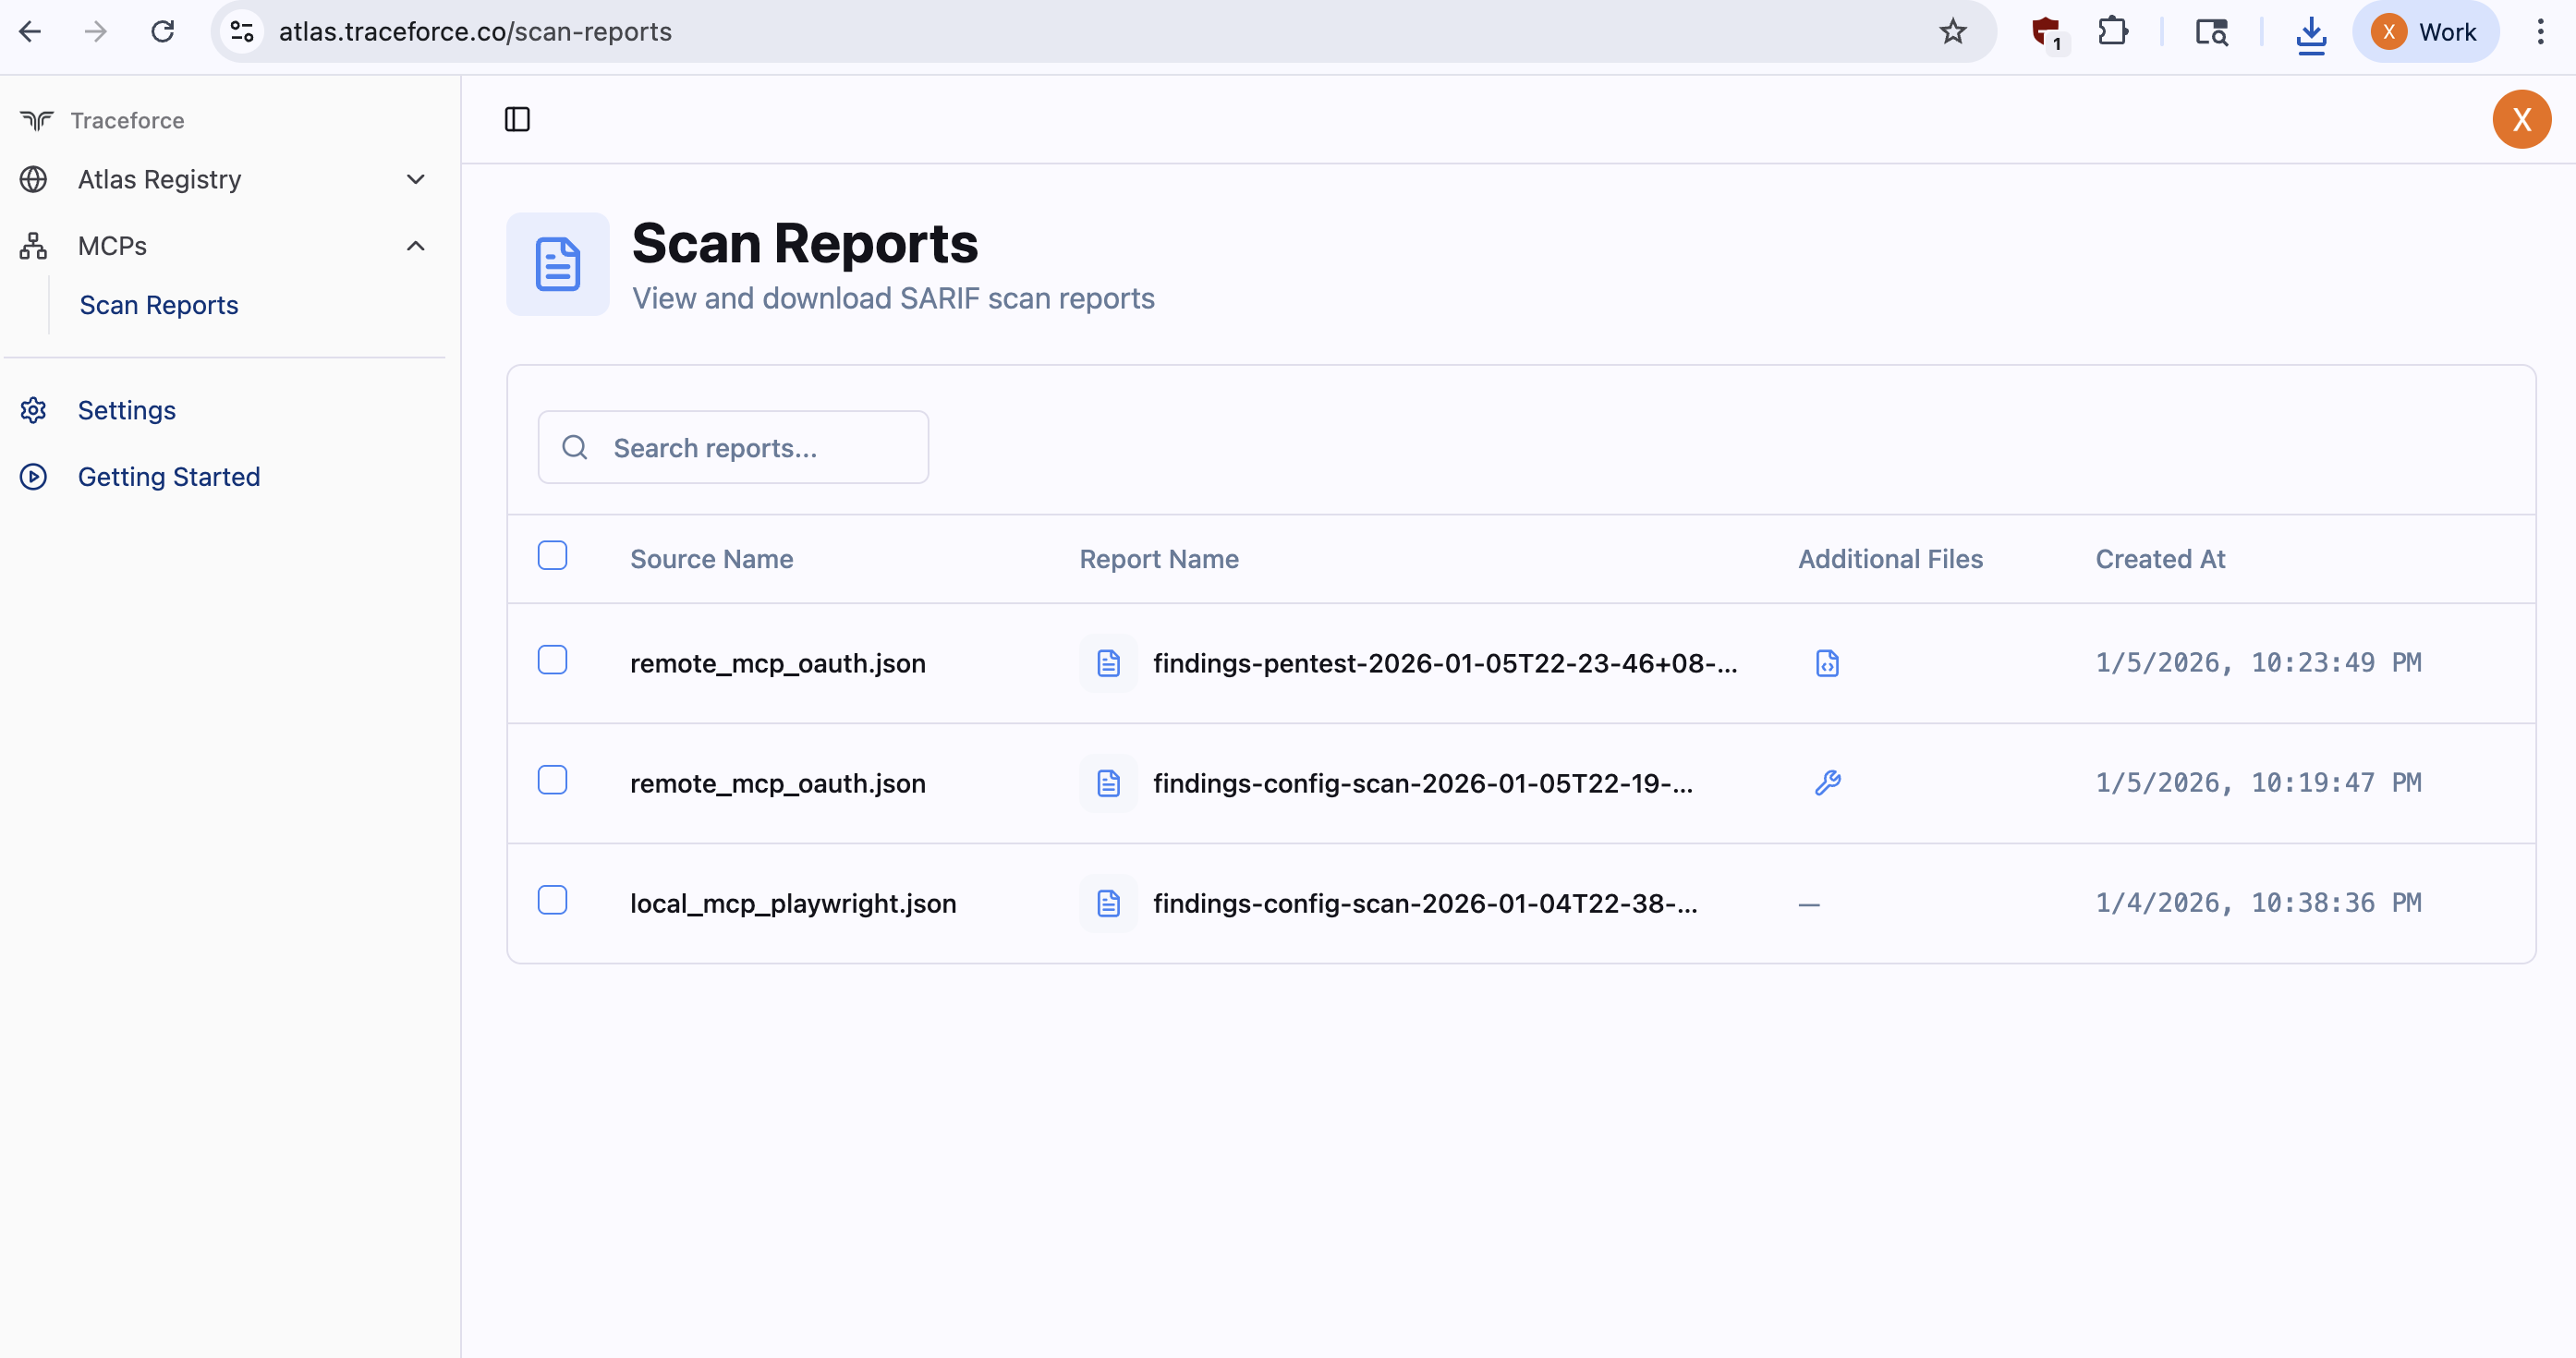
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

Automated testing suite with live traffic record and replay

Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…

Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain

Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.

一个由AI生成的漏洞验证应用