
CVE-2022-1329
 dexit/cve-2022-1329
CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…
code-analysisexploitationpayload-development+3
dexit/cve-2022-1329CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…
 d0n601/cve-2025-5961
Migration, Backup, Staging – WPvivid Backup & Migration <= 0.9.116 - Authenticated (Administrator+) Arbitrary File Upload
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…
 tommiionfire/cve-2016-3714
Proof-of-concept exploit for CVE-2016-3714, a remote code execution vulnerability in ImageMagick's MVG file processing. Demonstrates shell command…
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 themcsam/cve-2024-42471-poc
unzip-stream file write/overwrite vulnerability
 randomrobbiebf/cve-2024-50482
Woocommerce Product Design <= 1.0.0 - Unauthenticated Arbitrary File Upload
 mi-hood/cve-2018-9206
jquery file upload poc
 tigr78/cve-2025-53964
Proof-of-concept exploit for CVE-2025-53964: remote file read/write via malicious XDXF dictionary in GoldenDict 1.5.0/1.5.1, leveraging unsanitized…
 h4ckr4v3n/cve-2024-46209
Security research repository detailing CVE-2024-46209 (authenticated RCE) and CVE-2024-46210 (stored XSS via file upload) in Redaxo CMS v5.17.1, with…
 sromanhu/cve-2023-43360-cmsmadesimple-stored-xss---file-picker-extension
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Top…
 randomrobbiebf/cve-2024-9290
Super Backup & Clone - Migrate for WordPress <= 2.3.3 - Unauthenticated Arbitrary File Upload
 istern/cve-2023-26262
Proof-of-concept for authenticated arbitrary file upload in Sitecore 10.3, enabling webshell deployment and remote code execution via the import…
 k1nakoo/cve-2024-10410
Proof-of-concept exploit for CVE-2024-10410: unrestricted file upload in Online Hotel Reservation System. Demonstrates bypass of image validation via…
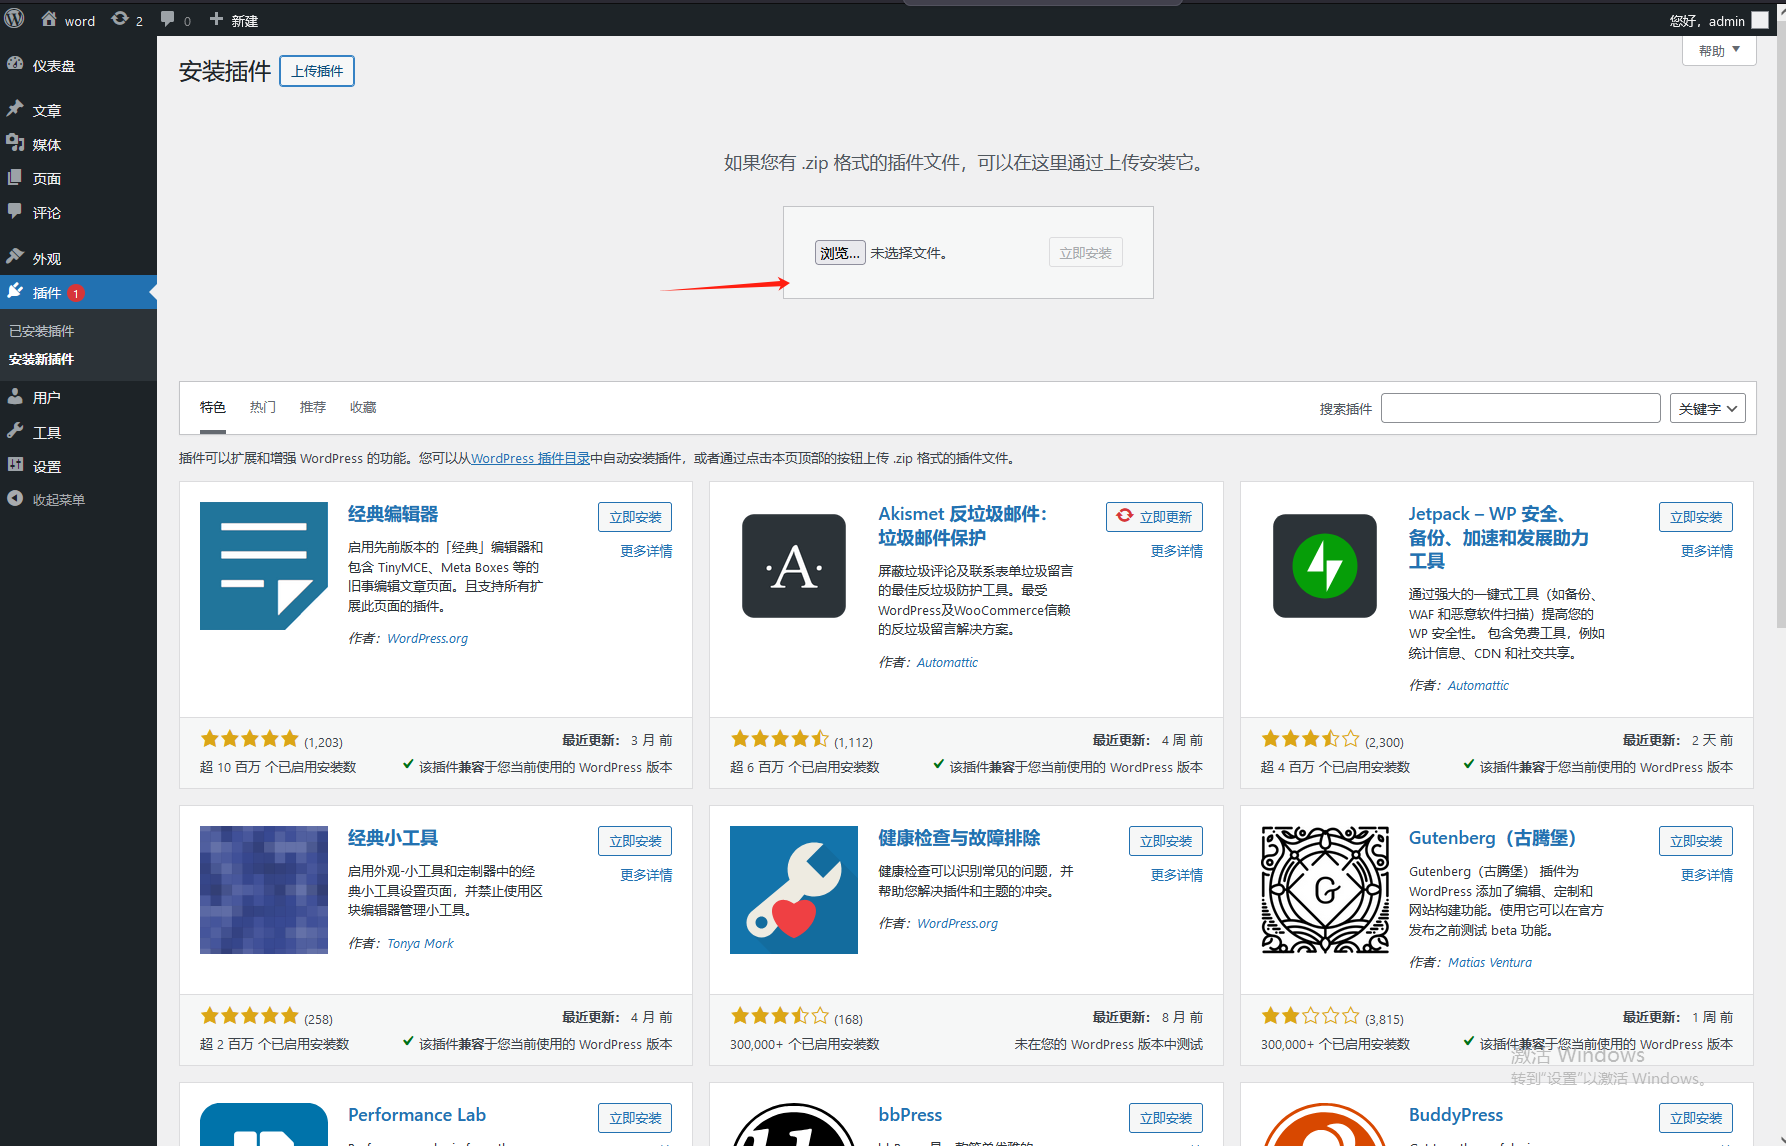 pei4an/cve-2025-28915
Exploit for CVE-2025-28915: WordPress ThemeEgg ToolKit arbitrary file upload vulnerability allowing remote Web Shell deployment. Includes…
 lvl23ht/poc-cve-2025-3914-aeropage-wordpress-file-upload
CVE-2025-3914-PoC | The Aeropage Sync for Airtable WordPress plugin (≤ v3.2.0) is vulnerable to authenticated arbitrary file uploads due to…
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…
 d0n601/cve-2024-13869
Migration,Backup, Staging – WPvivid <= 0.9.112 - Authenticated (Admin+) Arbitrary File Upload via wpvivid_upload_file