
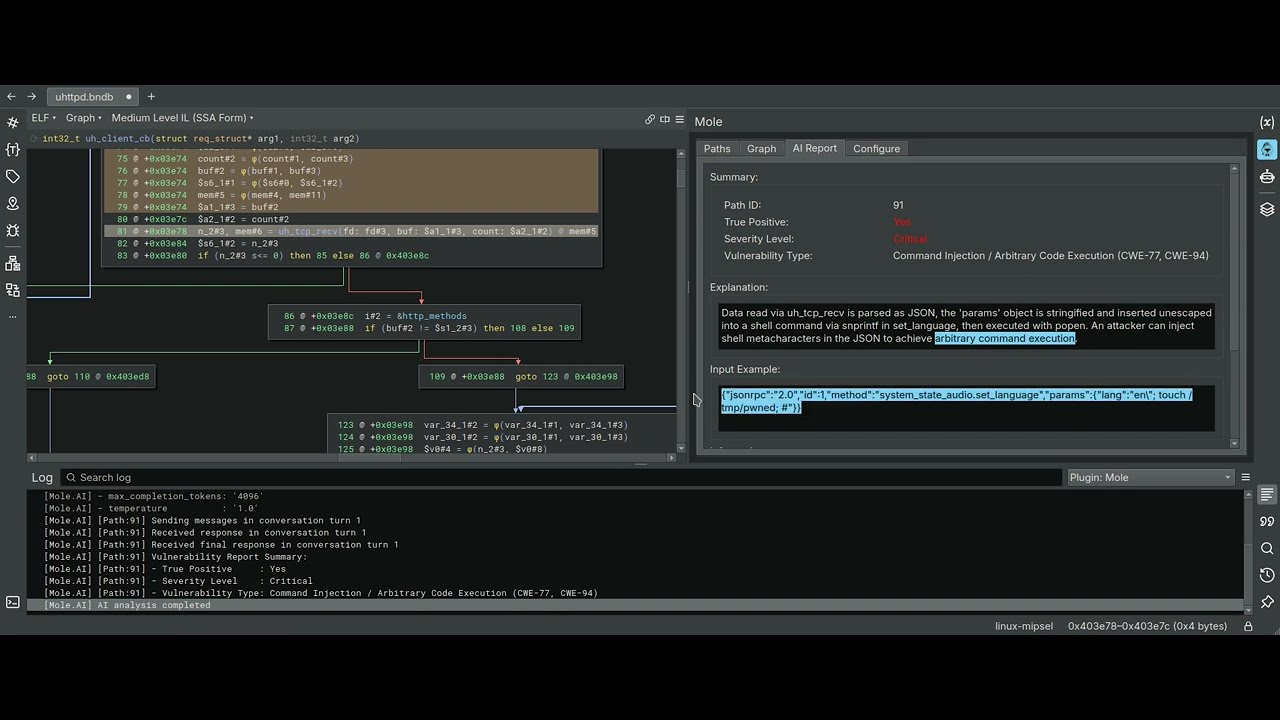
mole
 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
ai-assisted-reversingbinary-analysiscode-analysis+4
85
cyber-defence-campus/moleA Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
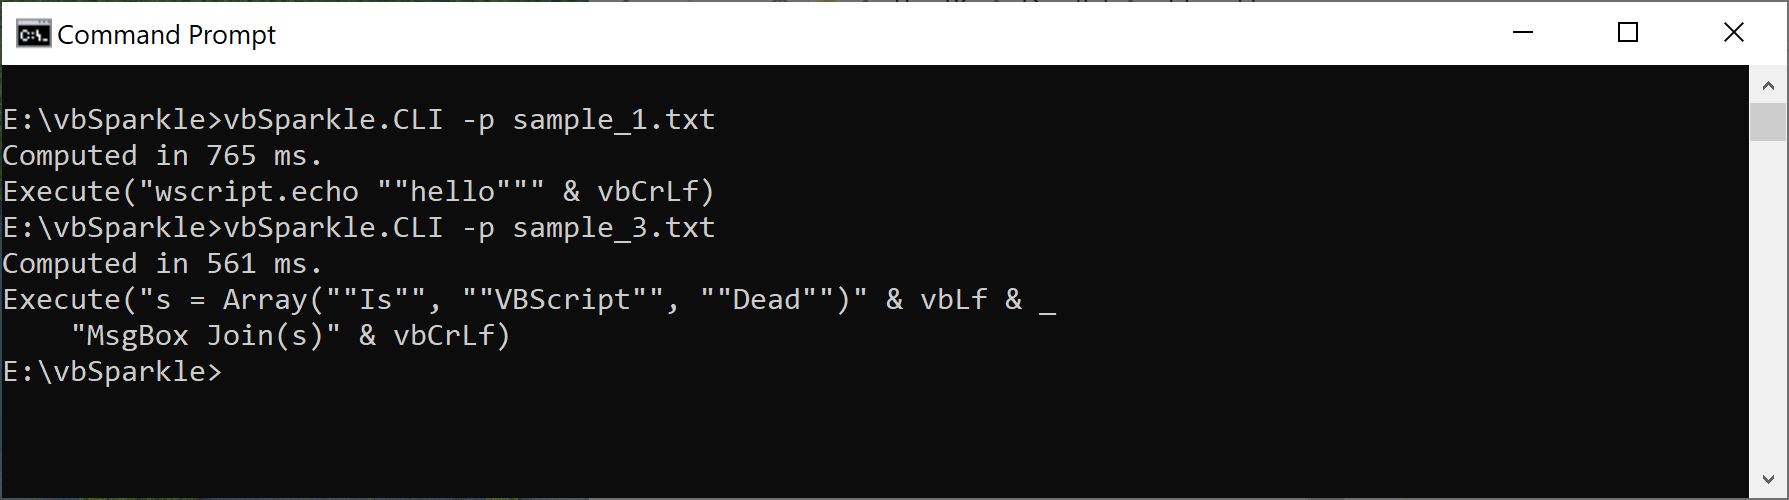 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 josue87/wp_hunter
Static analysis of wordpress plugins
 lunixbochs/revsync
realtime cross-tool collaborative reverse engineering
 pelock/jobfuscator
Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
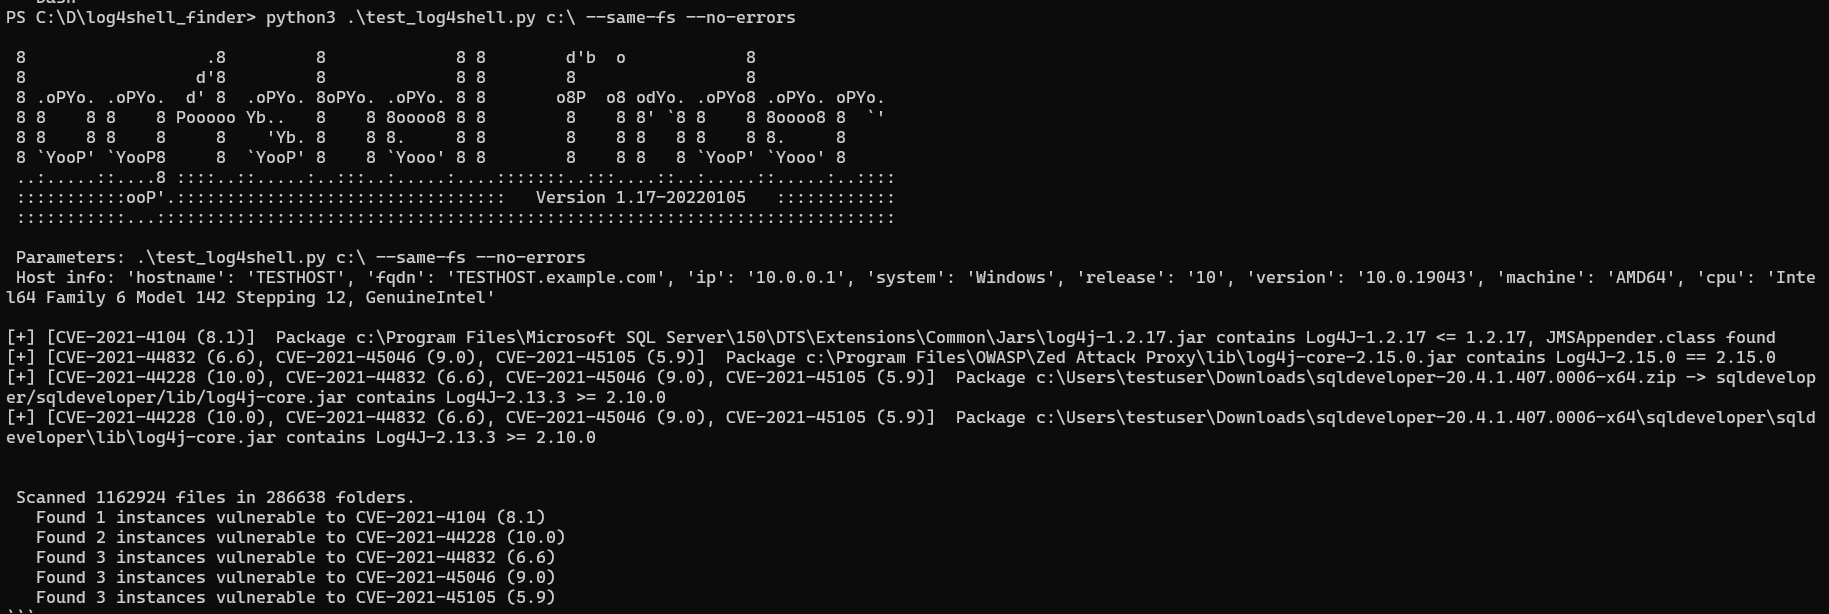 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
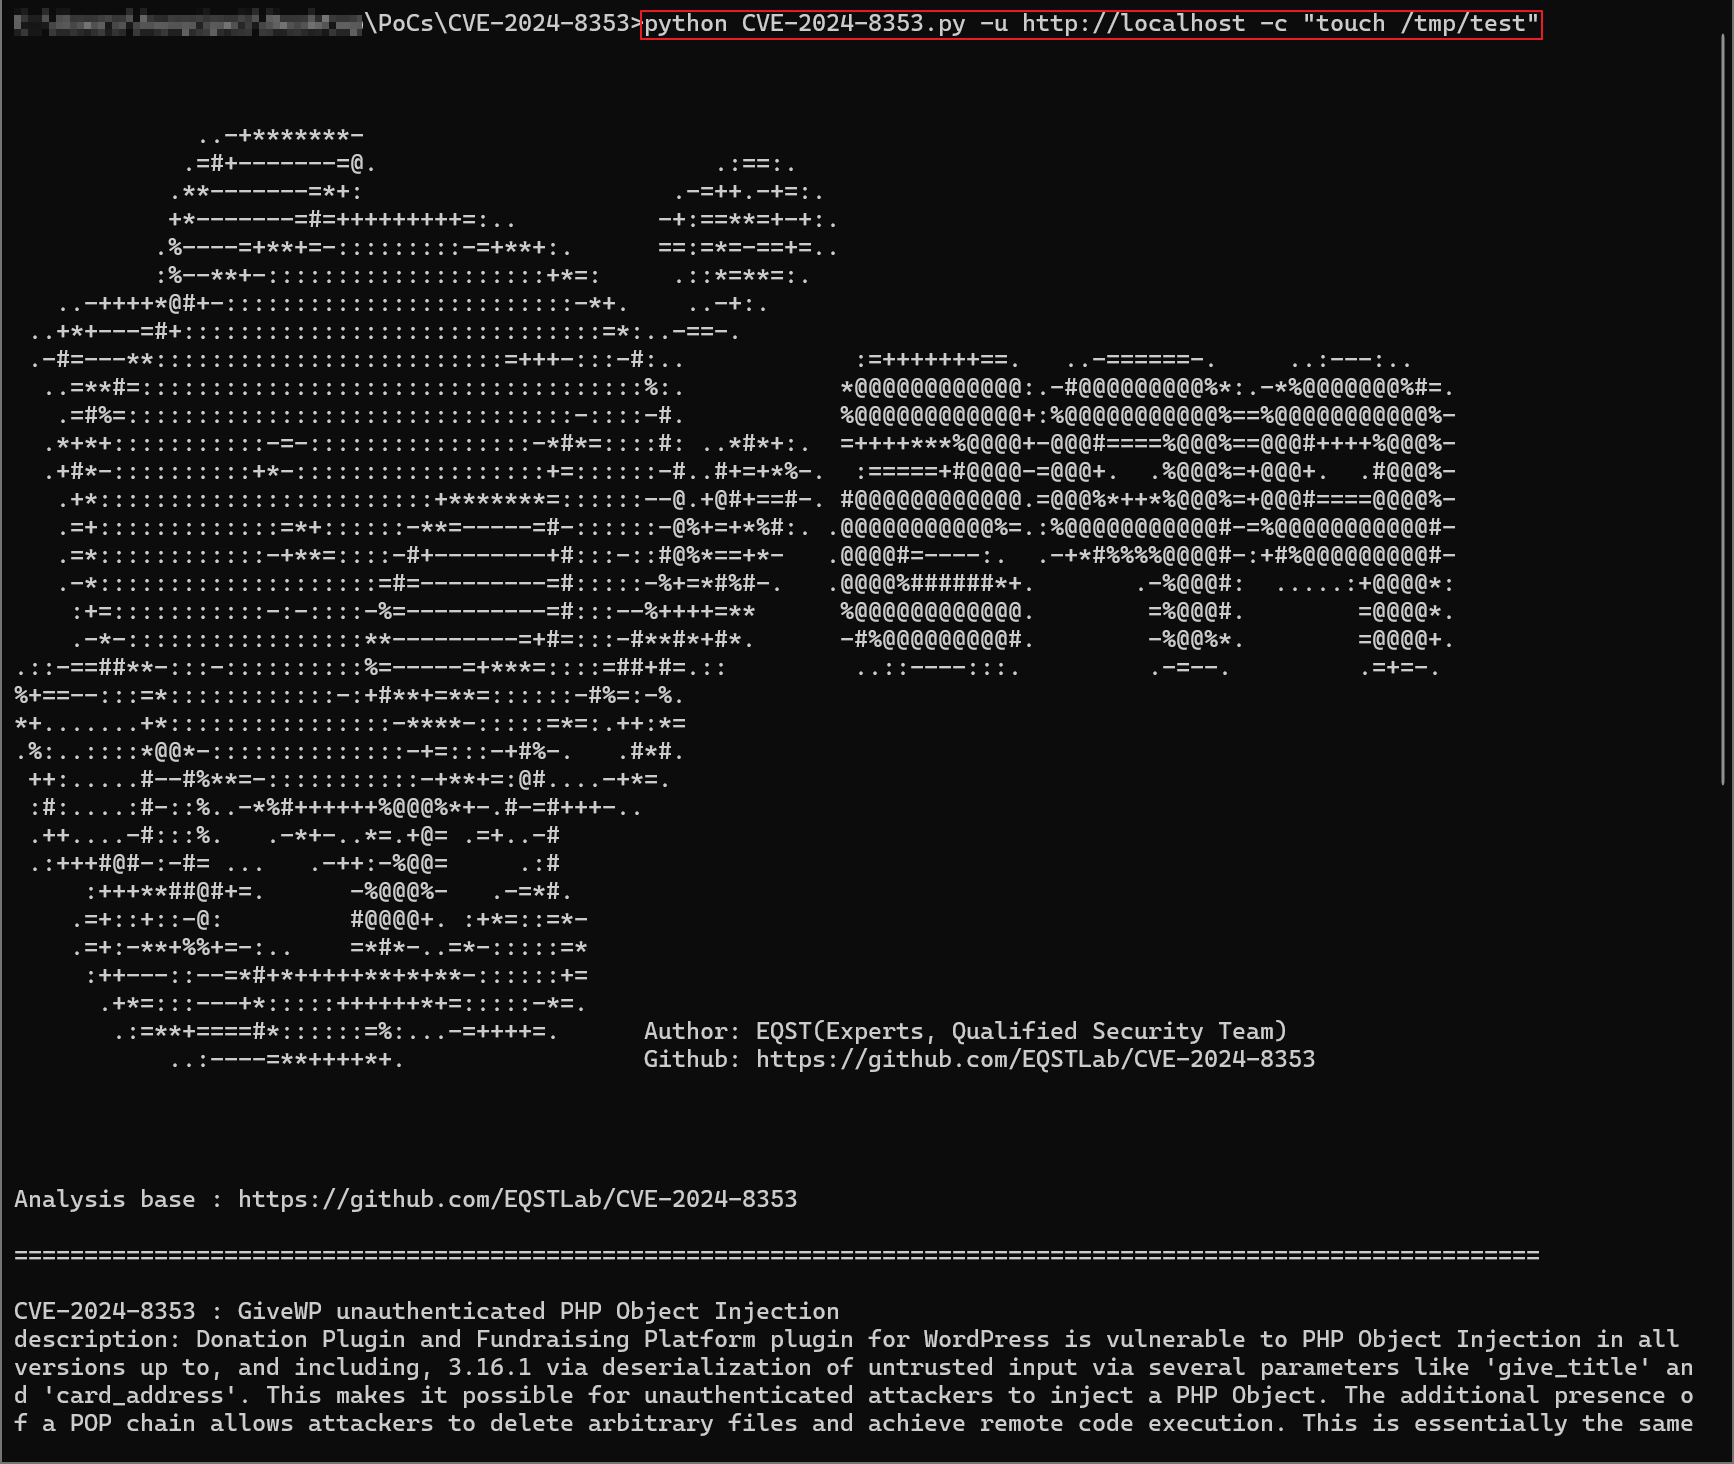 eqstlab/cve-2024-8353
GiveWP PHP Object Injection exploit
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…