CVE-2022-22965_Spring4Shell

A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…

A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…

Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…

CVE-Candidate: DoS in [email protected] via comma-separated brace expansion (CVE-2024-4068 incomplete fix)

Evidence-driven C/C++ vulnerability remediation pipeline + http-parser case study (CVE-2024-22019-class). Python core, React 19 console, 17-test…

Oracle Identity Manager 远程代码执行漏洞CVE-2025-61757

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…


A Bitbucket Pipe to trigger SonarCloud analysis

Heap-buffer-overflow in Oniguruma (function fetch_interval_quantifier)

Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…

Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.

CVE-2025-49113 - Roundcube <= 1.6.10 Post-Auth RCE via PHP Object Deserialization

CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…

A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…

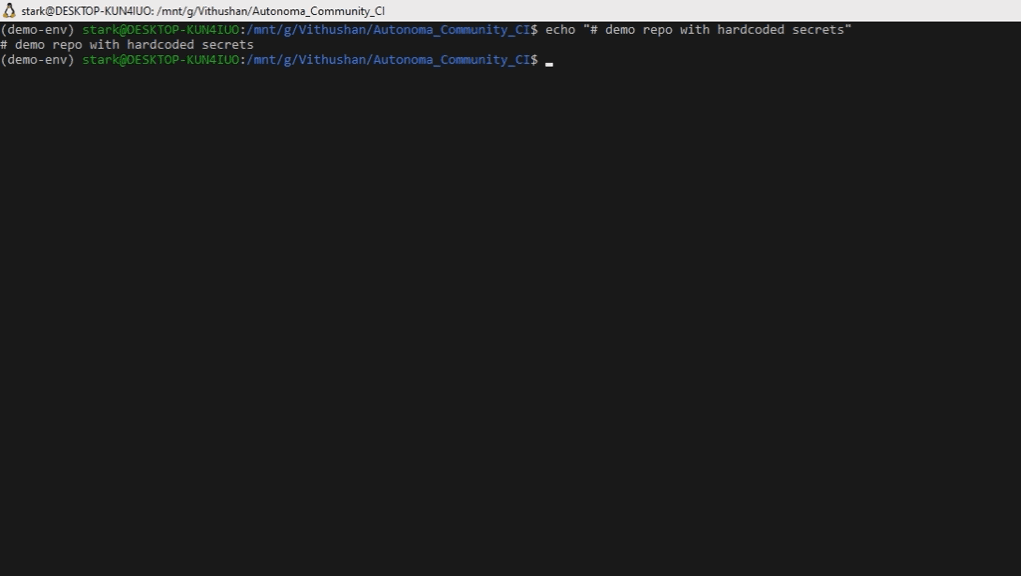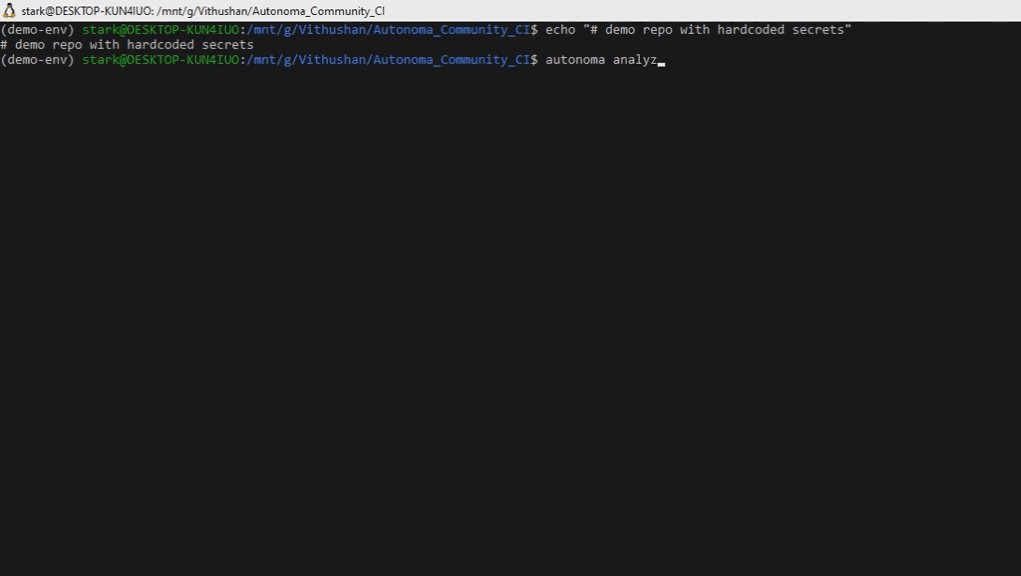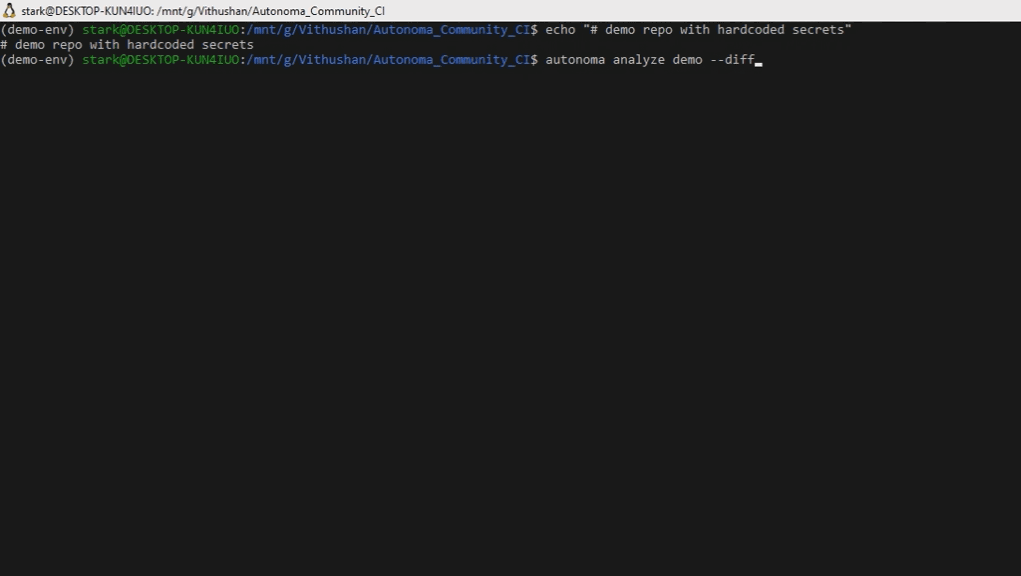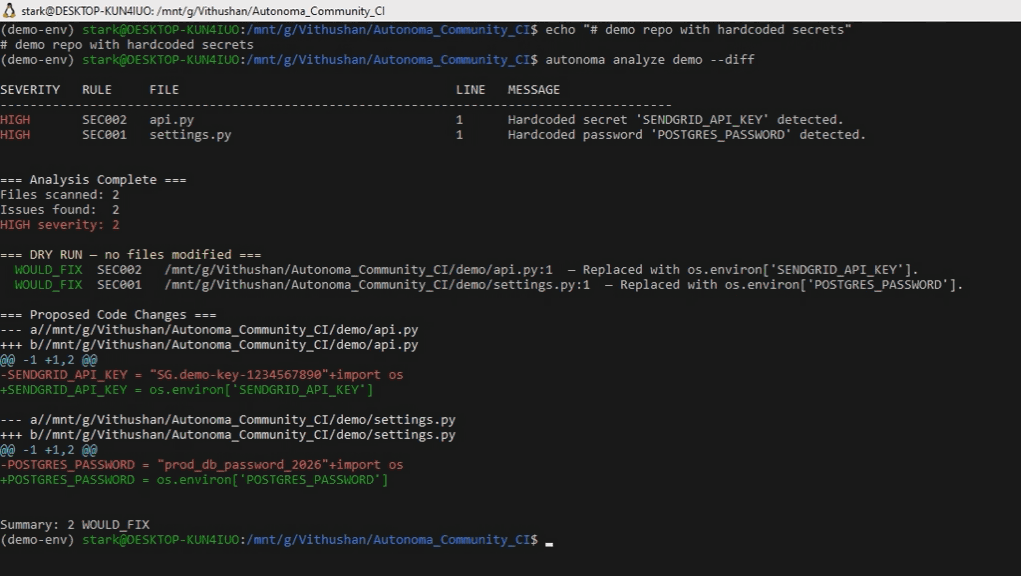
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code

C-based vulnerability analysis and exploitation toolkit targeting AOSP libavc heap overflow (CVE-2021-0325) with static code analysis capabilities.

I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.