
wheelaudit
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
code-analysisconfiguration-auditingdevsecops+5
3
kriskimmerle/wheelauditPython Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
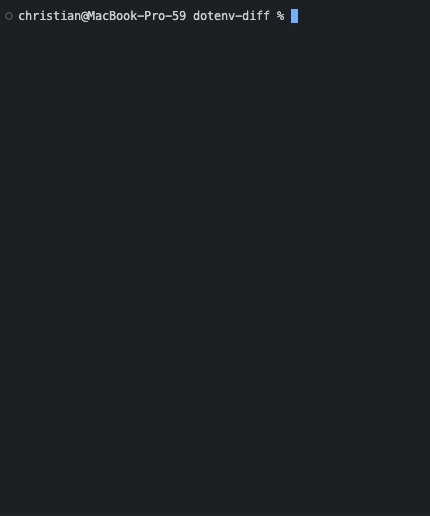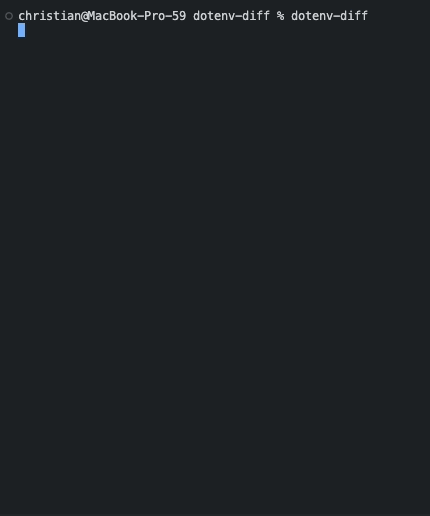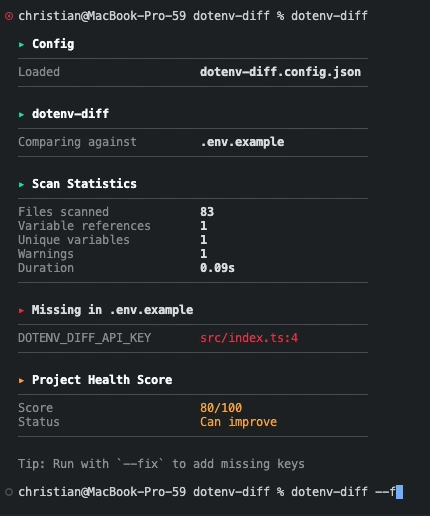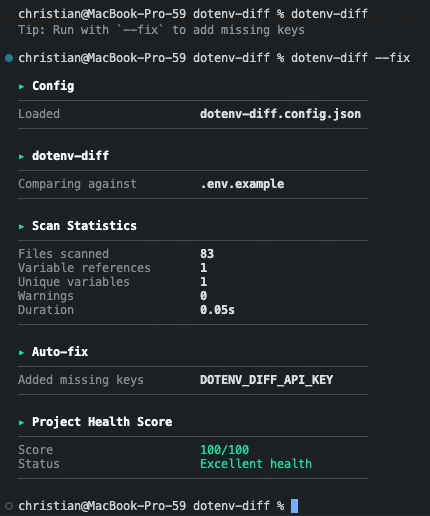 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 skyscanner/whispers
Identify hardcoded secrets in static structured text
 reposaur/reposaur
Open source compliance tool for development platforms.
 awslabs/git-secrets
Prevents you from committing secrets and credentials into git repositories
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 santhreal/keyhog
Open-source secret scanner in Rust
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 smxlabs/lamma-beta
Vulnerability Assessment and Auditing Framework for all the Crypto Implementations.
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…