

CVE-2026-51947-Advisory
 timtimxs/cve-2026-51947-advisory
Pivotal CRM's patch for an initial deserialization vulnerability was incomplete. The fix switched from BinaryFormatter to JSON.NET but left…
code-analysisexploitationpenetration-testing+2
timtimxs/cve-2026-51947-advisoryPivotal CRM's patch for an initial deserialization vulnerability was incomplete. The fix switched from BinaryFormatter to JSON.NET but left…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 shoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3
Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 password123456/py_certificate_extractor
Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…
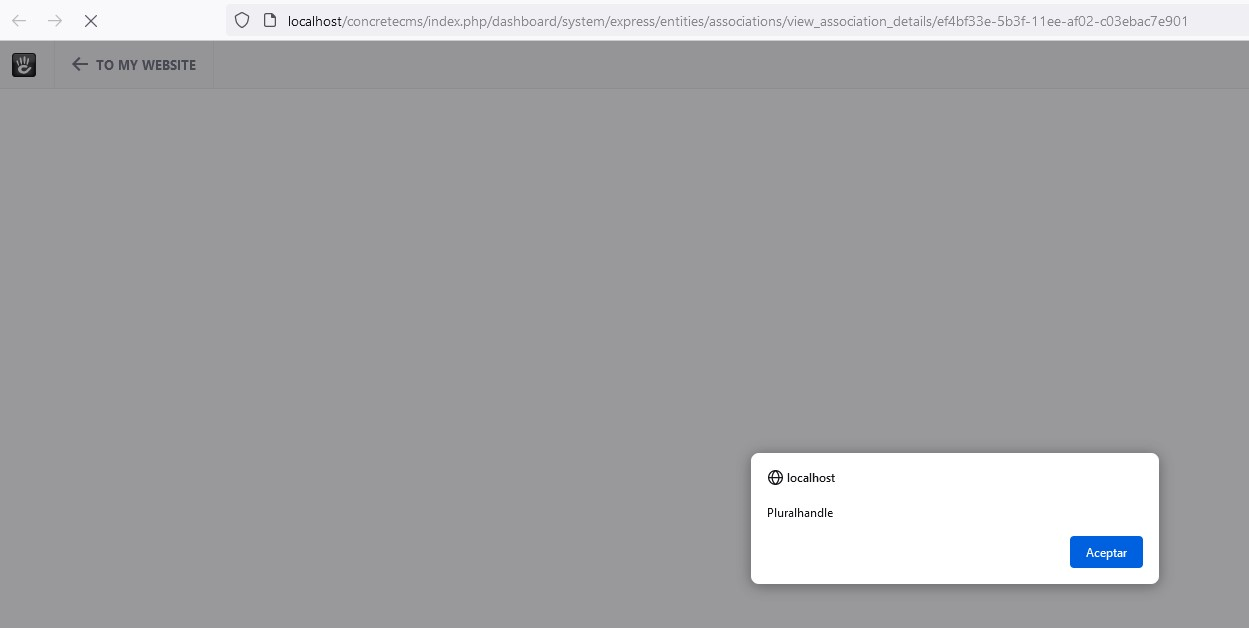 sromanhu/cve-2023-44765_concretecms-stored-xss---associations
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Plural Handle…
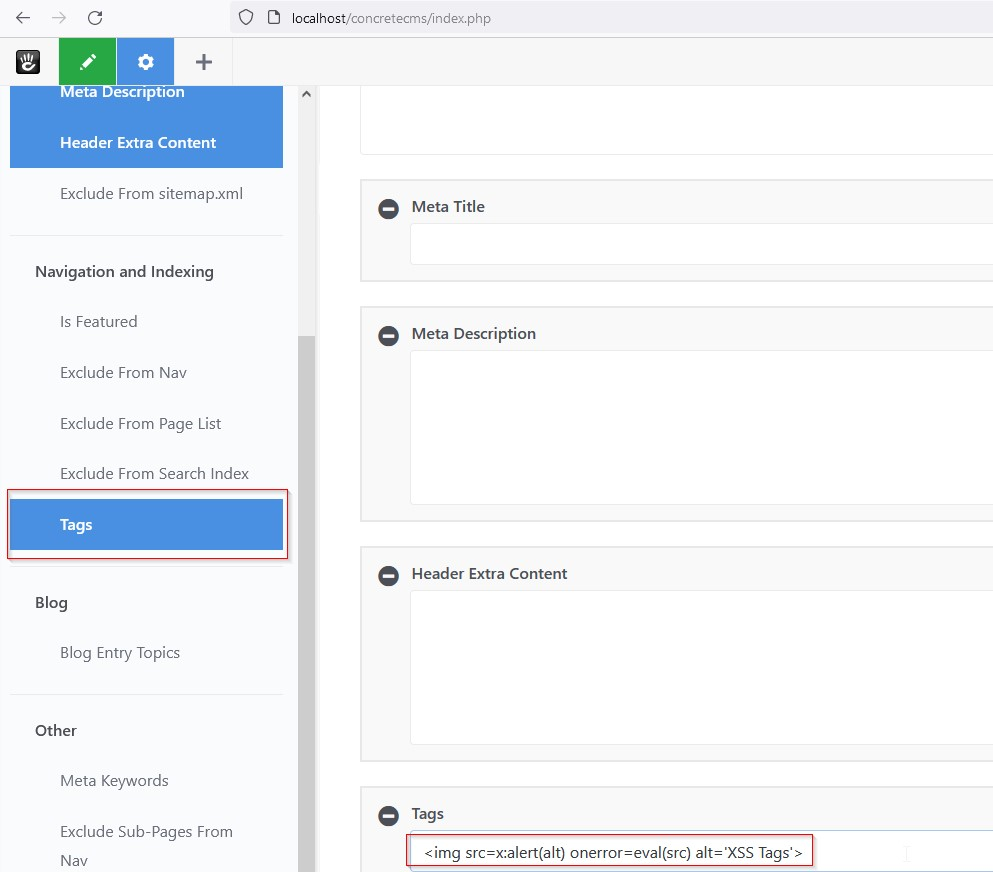 sromanhu/cve-2023-44762_concretecms-reflected-xss---tags
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Tags from…
 andrenasx/cve-2015-10034
Demonstrates CVE-2015-10034 in a vulnerable Java application, including SARIF analysis results from J-TAS Action for educational security testing.
 anthropics/defending-code-reference-harness
Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications


 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
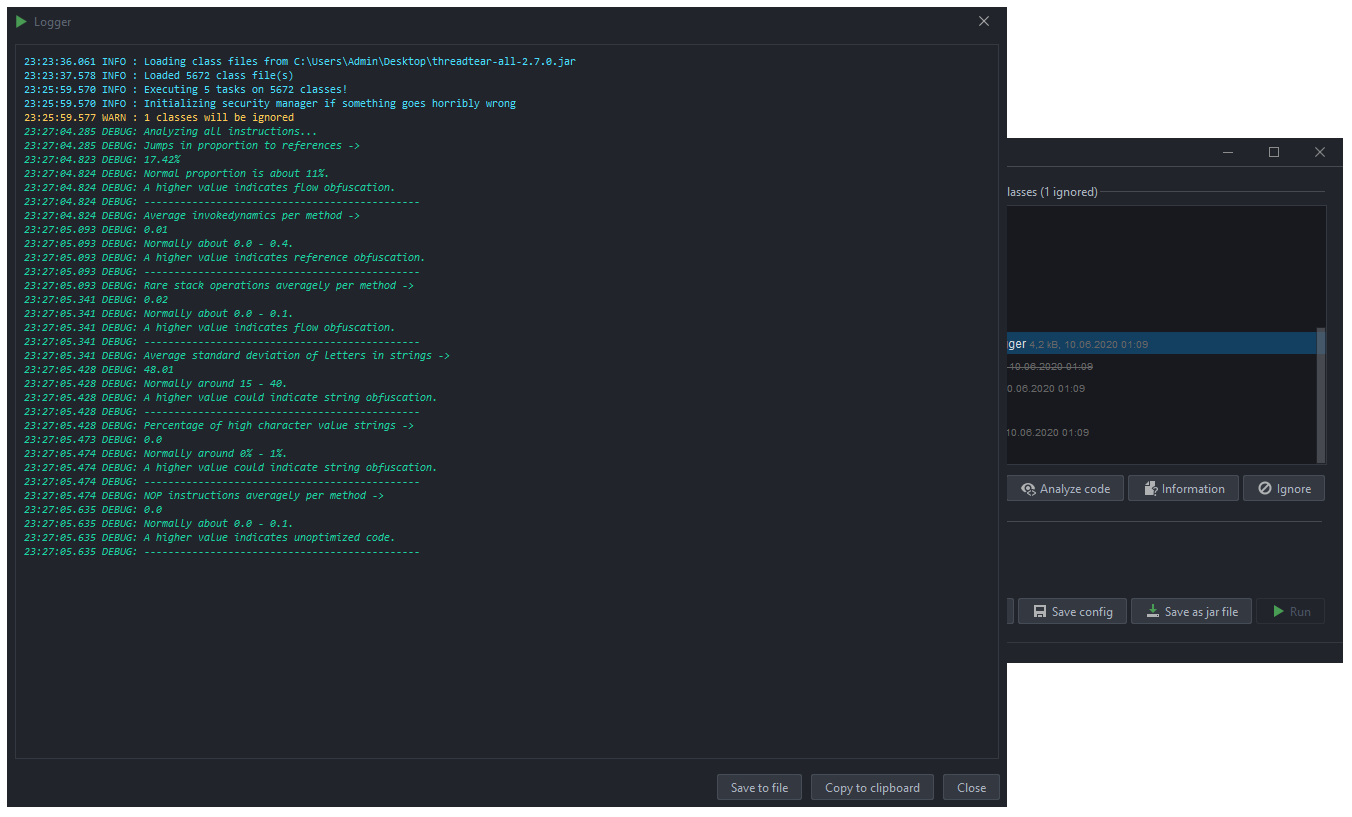 loerting/threadtear
Multifunctional java deobfuscation tool suite