
SILENTCHAIN
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
ai-securityapi-security-testingcode-analysis+8
463
silentchainai/silentchainAI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 nccgroup/freddy
Automatically identify deserialisation issues in Java and .NET applications by using active and passive scans
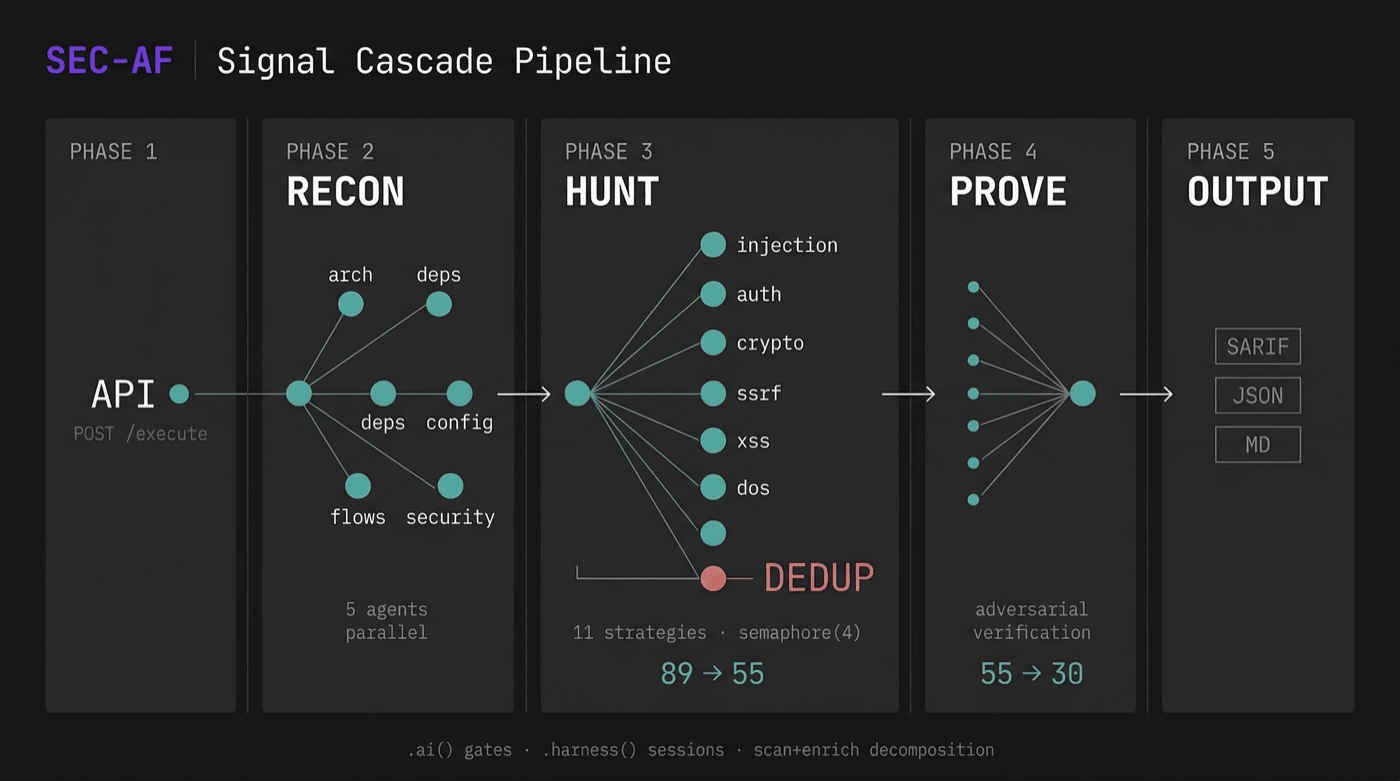 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
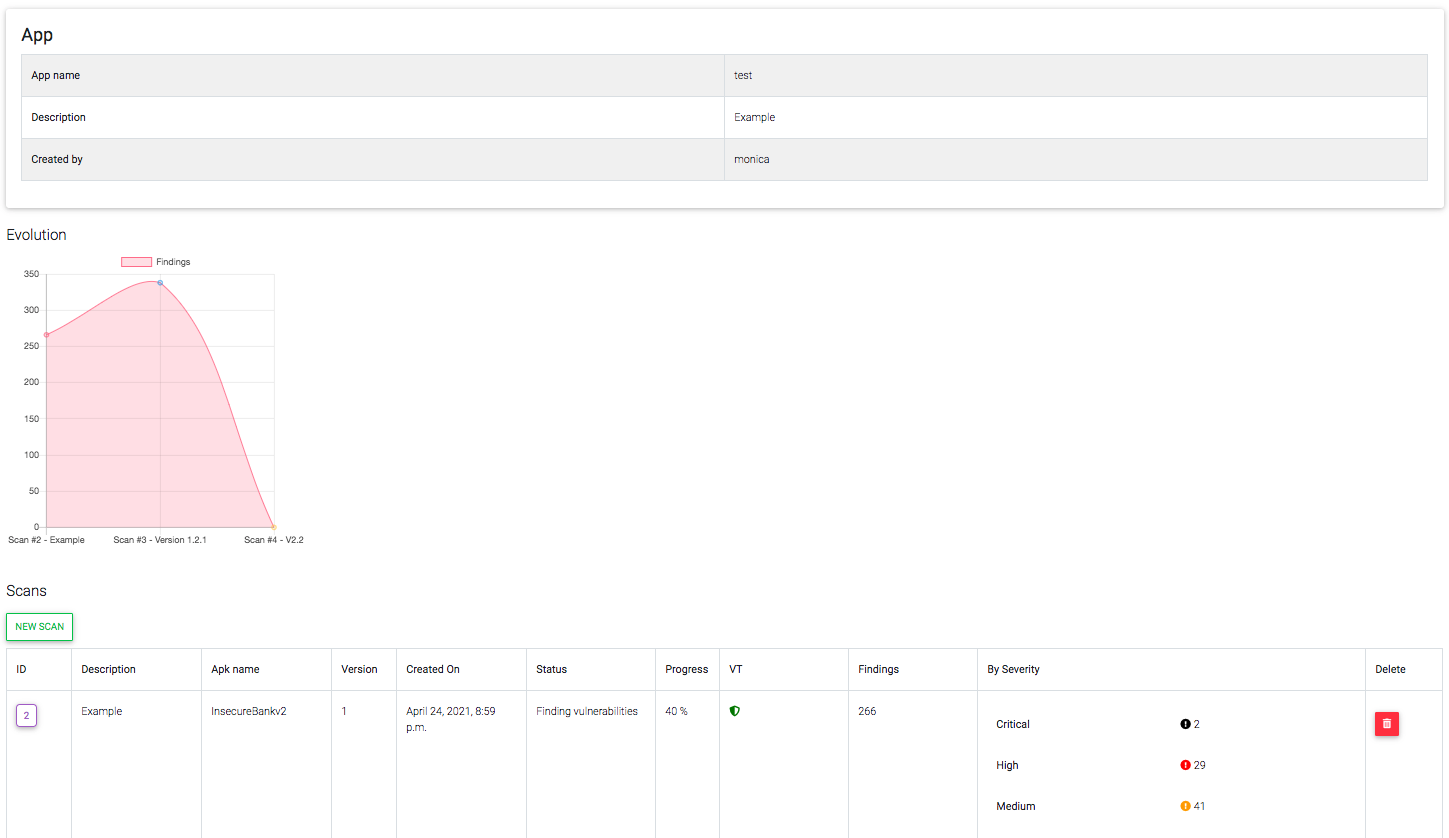 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 kudelskisecurity/chainoffools
Proof-of-concept exploit for CVE-2020-0601 Windows CryptoAPI spoofing vulnerability, demonstrating rogue CA certificate generation using elliptic…
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 lucksec/spring-cloud-gateway-cve-2022-22947
Exploit for CVE-2022-22947: remote code execution in Spring Cloud Gateway via crafted requests to the Actuator endpoint. Includes Python script and…
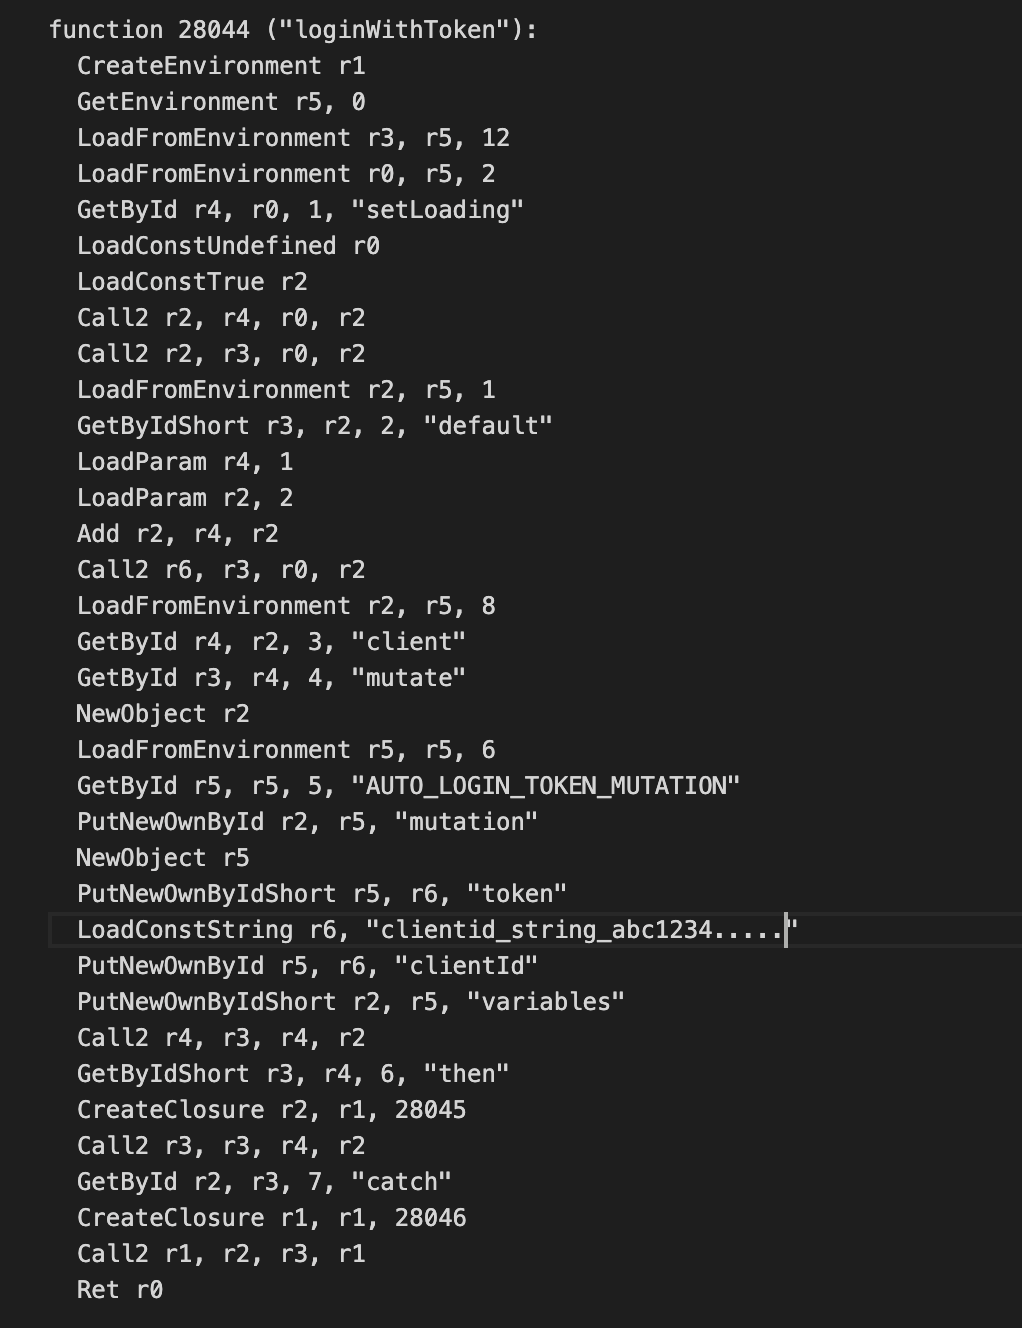 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)
 codewhitesec/httpremotingobjrefleak
Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 jas502n/jackson-cve-2020-8840
FasterXML/jackson-databind 远程代码执行漏洞
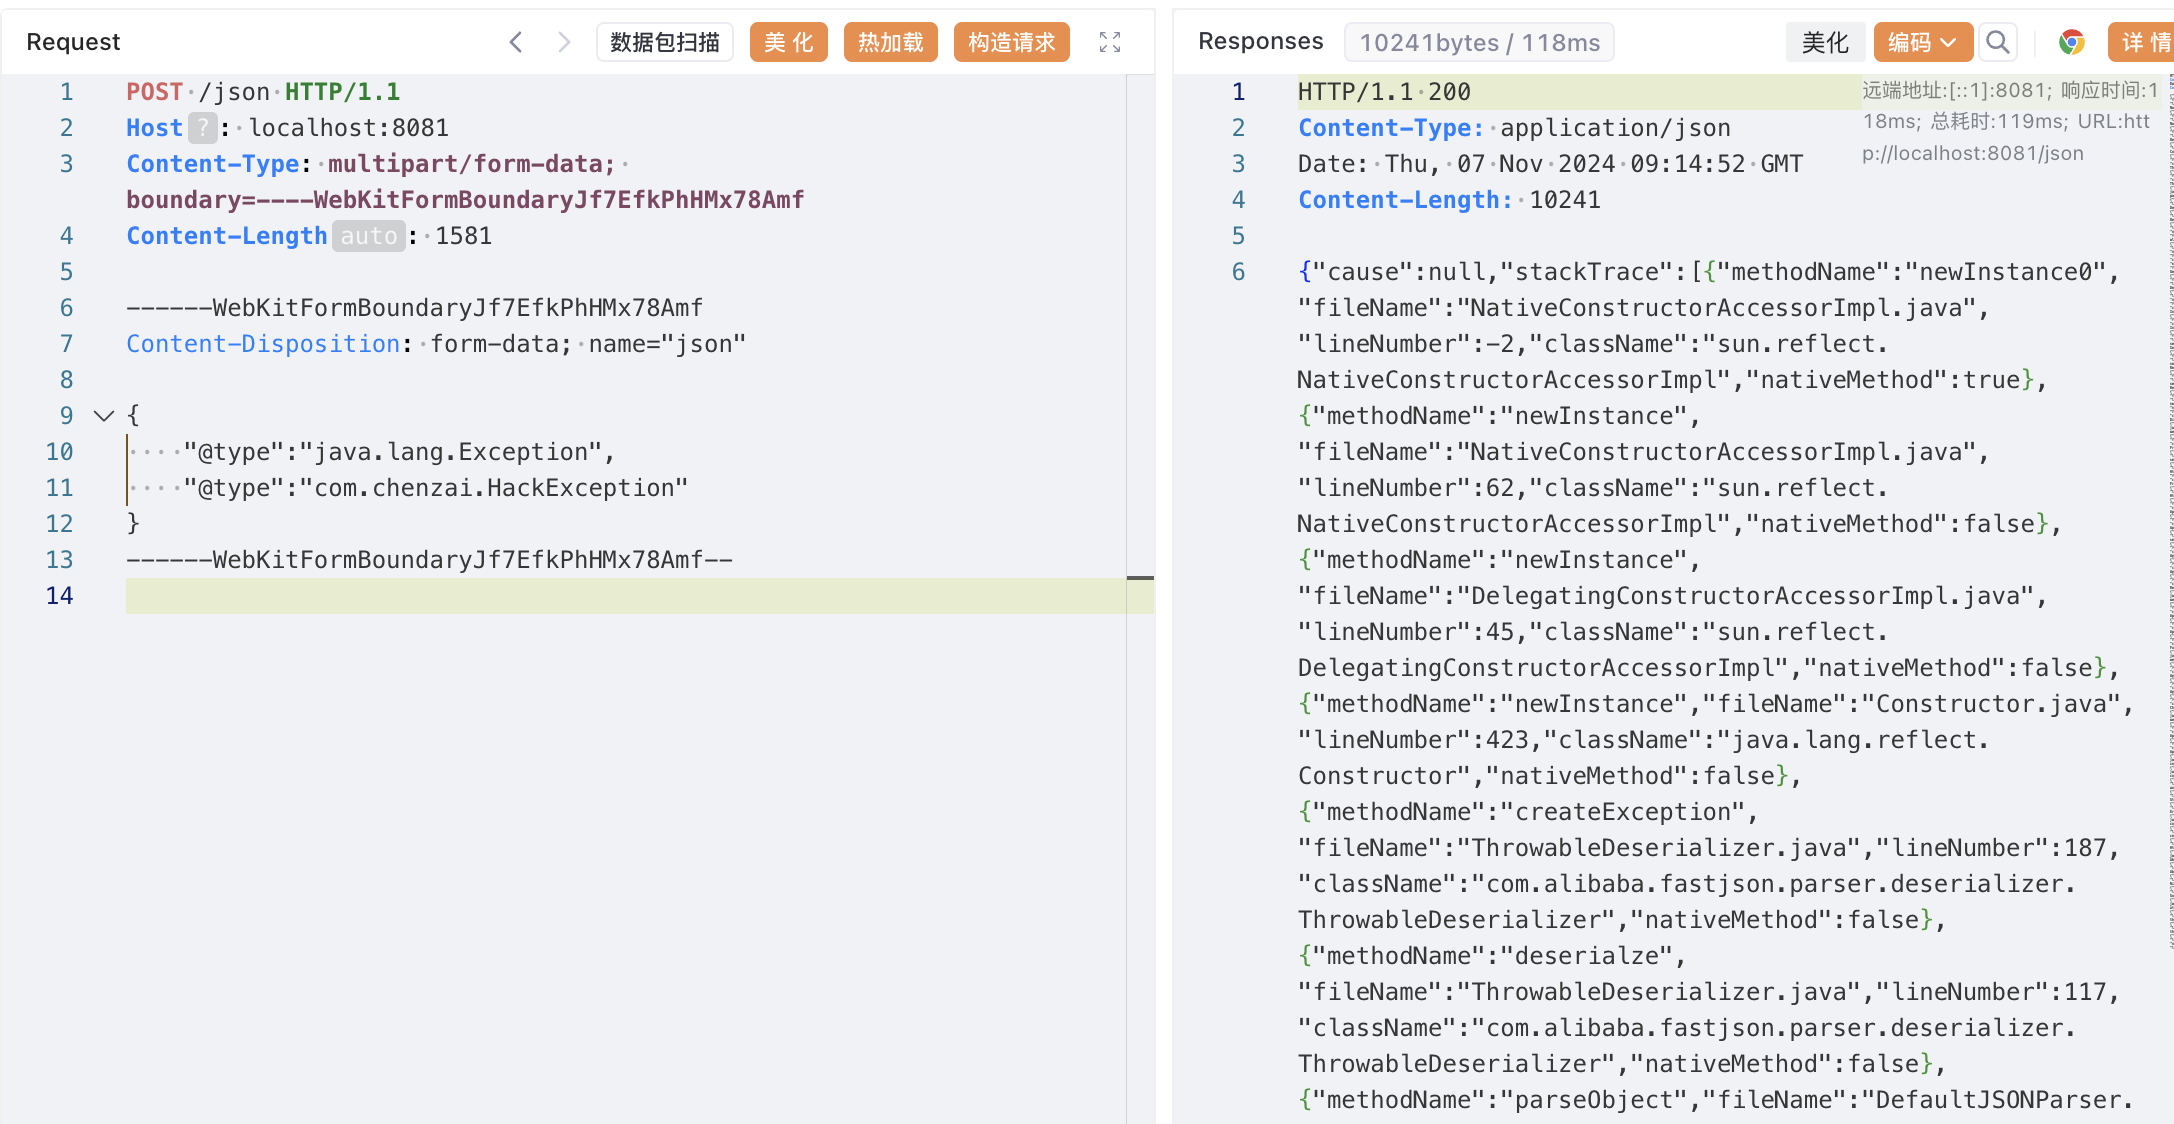 luelueking/cve-2022-25845-in-spring
CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…
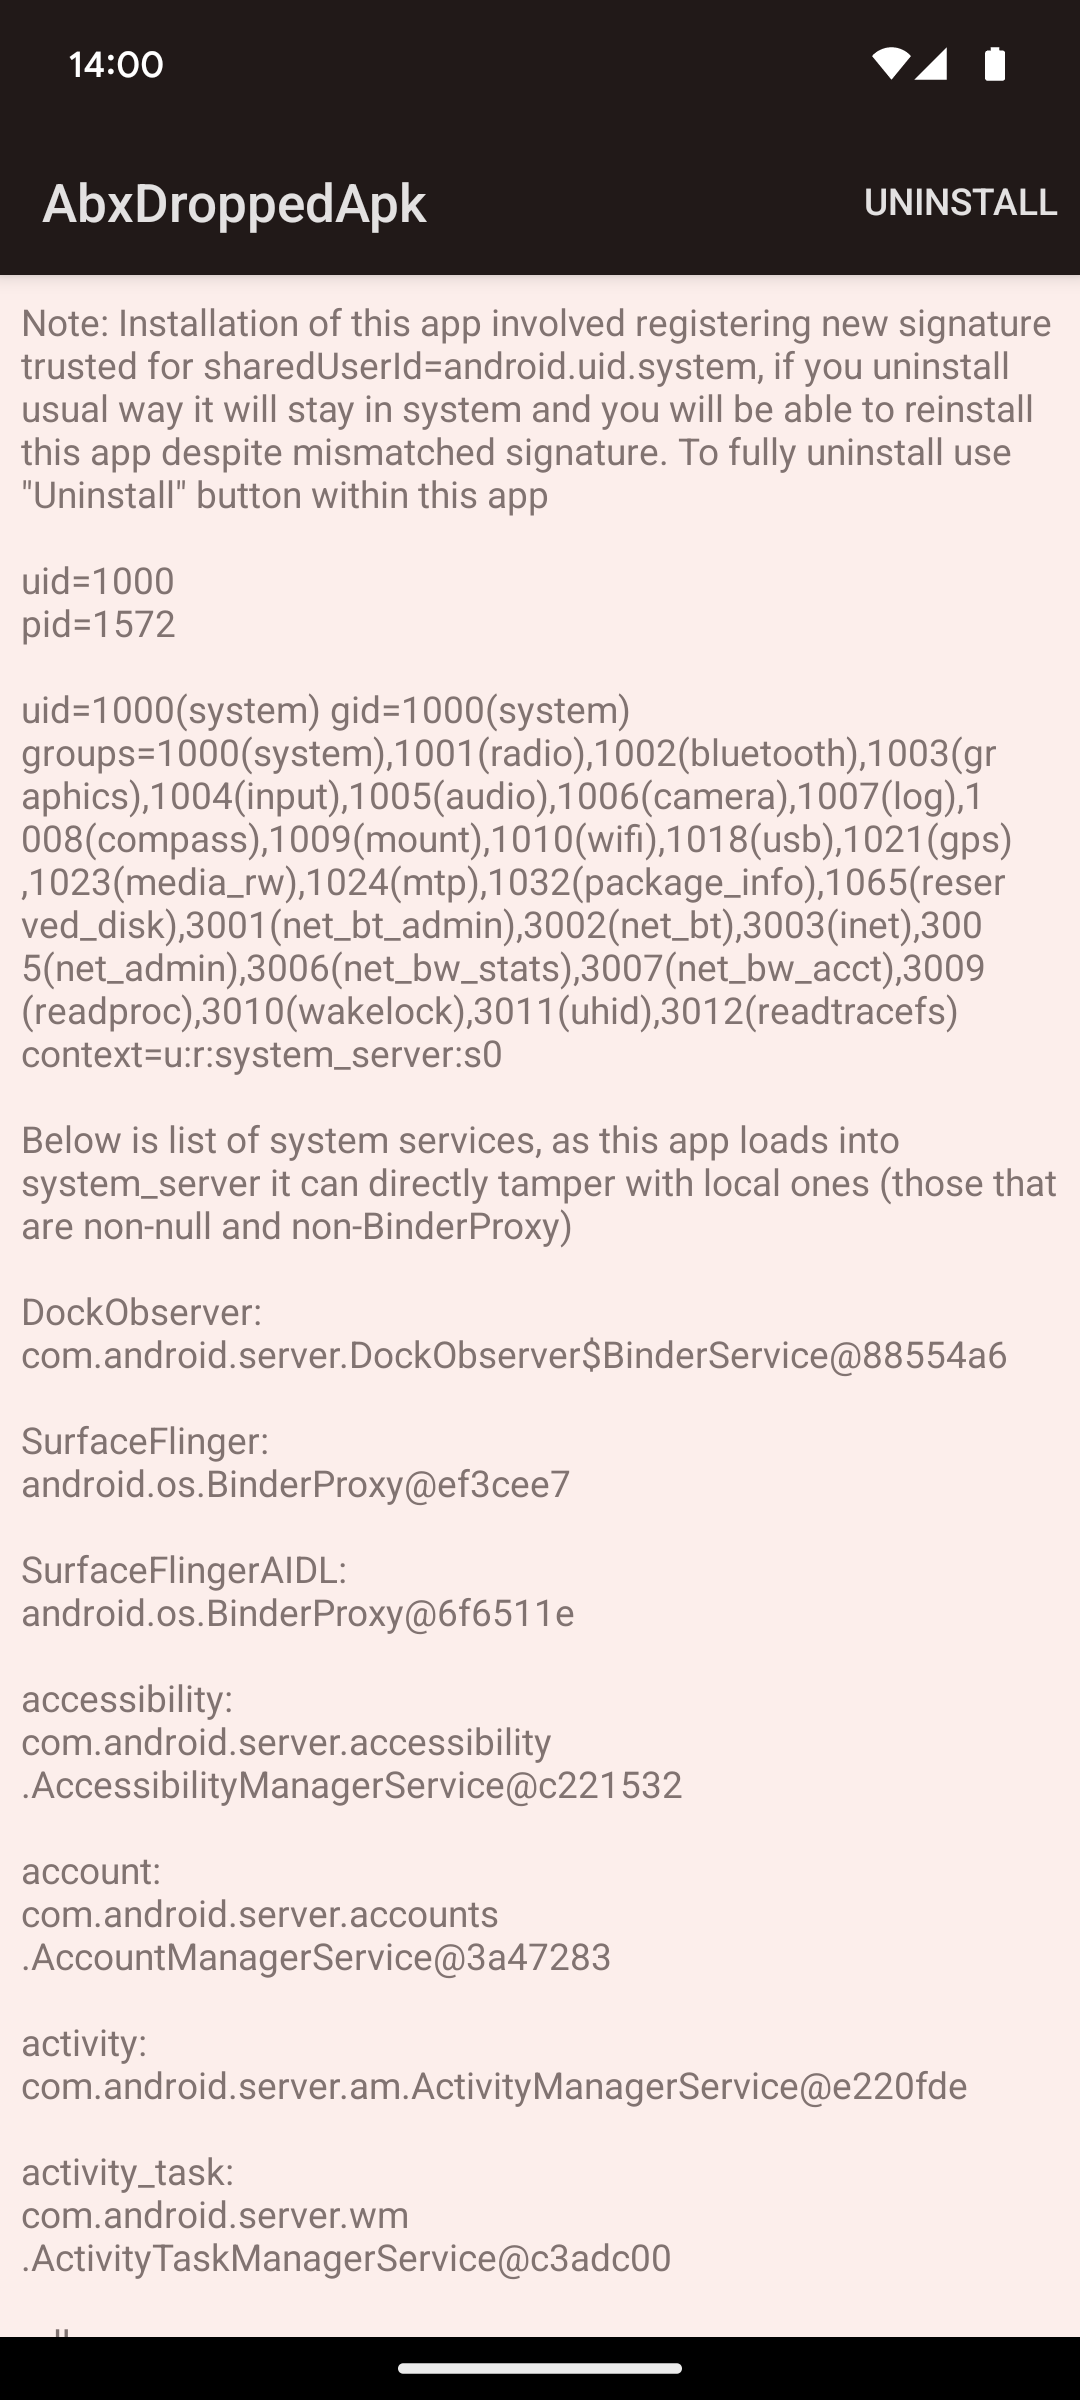 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
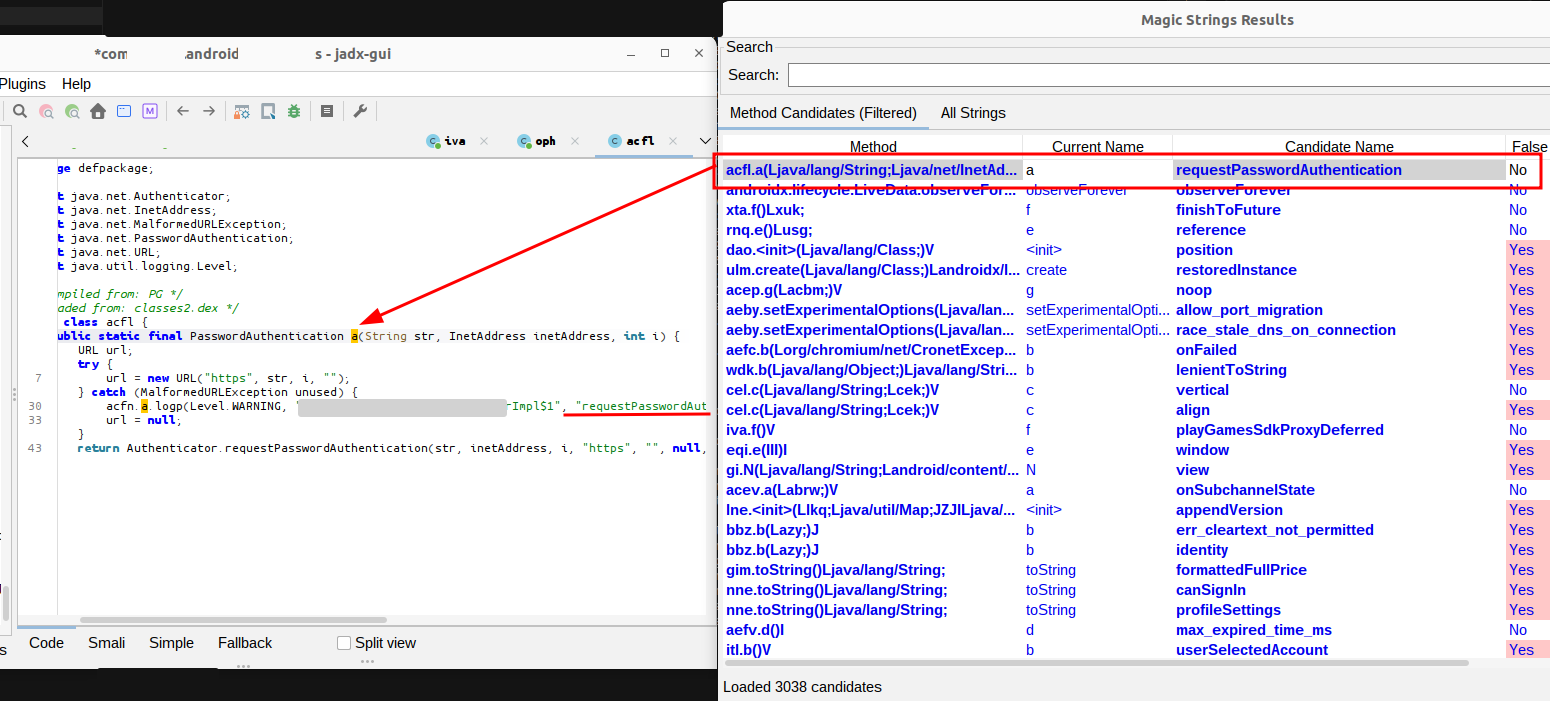 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.