

CVE-2024-51793
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
code-analysisexploitationpayload-generation+6
1
ktn1990/cve-2024-51793(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
 m2sousa/cve-2025-69212
CVE-2025-69212 Proof-of-concept.
 dannners/jackson-deserialization-2017-7525
Jackson Deserialization CVE-2017-7525 PoC
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
 kang8/cve-2021-43503
Proof-of-concept exploit for CVE-2021-43503, a Laravel deserialization RCE vulnerability. Includes PHP POP chain generation and HTTP-based payload…
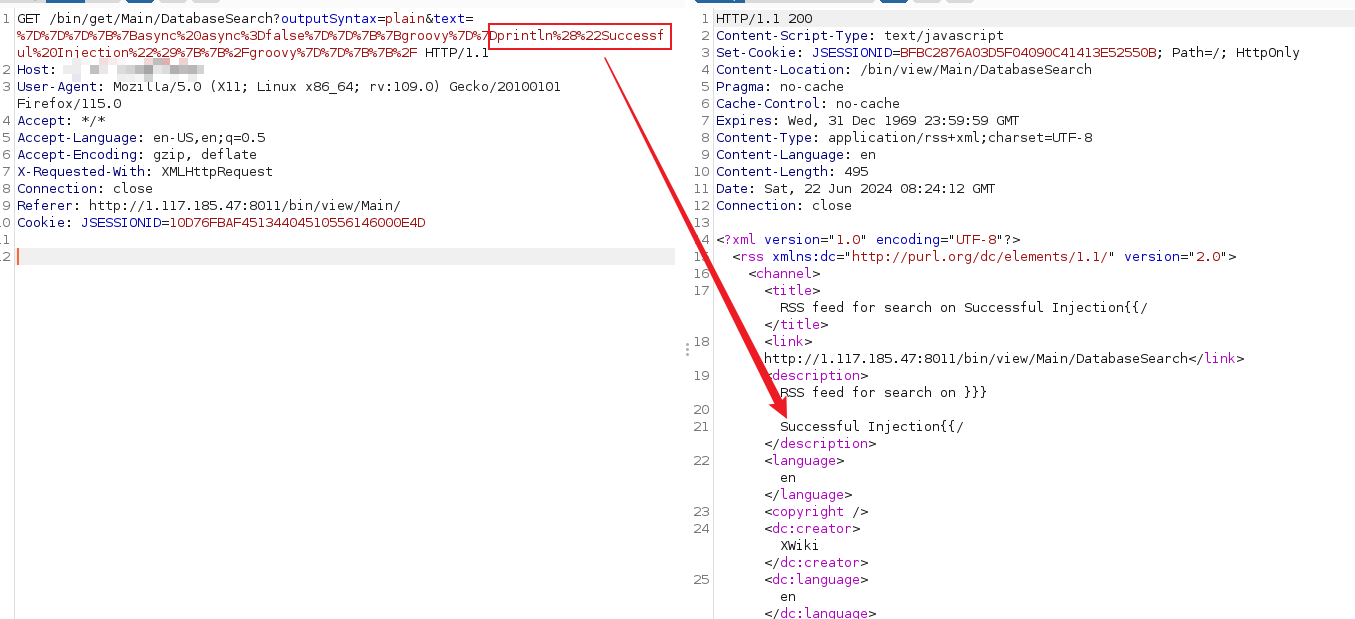 nanowraith/cve-2024-31982
Proof-of-concept exploit for CVE-2024-31982: Java Server-Side Template Injection (SSTI) leading to remote code execution via Groovy payload injection.
 y0s9/cve-2021-3129
CVE-2021-3129-Laravel Debug mode 远程代码执行漏洞
 fatkz/cve-2025-24813
Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
 randomrobbiebf/cve-2024-49699
ARPrice <= 4.0.3 - Authenticated (Subscriber+) PHP Object Injection
 randomrobbiebf/cve-2024-12877
GiveWP – Donation Plugin and Fundraising Platform <= 3.19.2 - Unauthenticated PHP Object Injection
 d0n601/cve-2025-13595
CIBELES AI <= 1.10.8 - Unauthenticated Arbitrary File Upload
 zs1n/cve-2023-46818
CVE-2023-46818 | PoC | ISPConfig 3.2.11p1
 anothersec/cve-2025-6440
WooCommerce Designer Pro 1.9.26 - Arbitrary File Upload
 loaxert/cve-2018-15133-poc
Python exploit for CVE-2018-15133, achieving remote code execution on vulnerable Laravel applications via insecure deserialization of encrypted…
 d0n601/cve-2025-13374
Kalrav AI Agent <= 2.3.3 - Unauthenticated Arbitrary File Upload via kalrav_upload_file AJAX Action
 kerburenthusiasm/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132 enabling unauthenticated remote code execution in Pterodactyl Panel <= 1.11.10 via locale parameter…
 kai-one001/-cve-2015-10137-wordpress-n-media-website-contact-form-with-file-upload-1.3.4
Python exploit for CVE-2015-10137 targeting an arbitrary file upload vulnerability in the WordPress N-Media Website Contact Form plugin, enabling…