
joern
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
binary-analysiscode-analysisreverse-engineering+2
3.5k
joernio/joernOpen-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 globocom/huskyci
Performing security tests inside your CI
 koadt/poc-cve-2025-55182
This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…
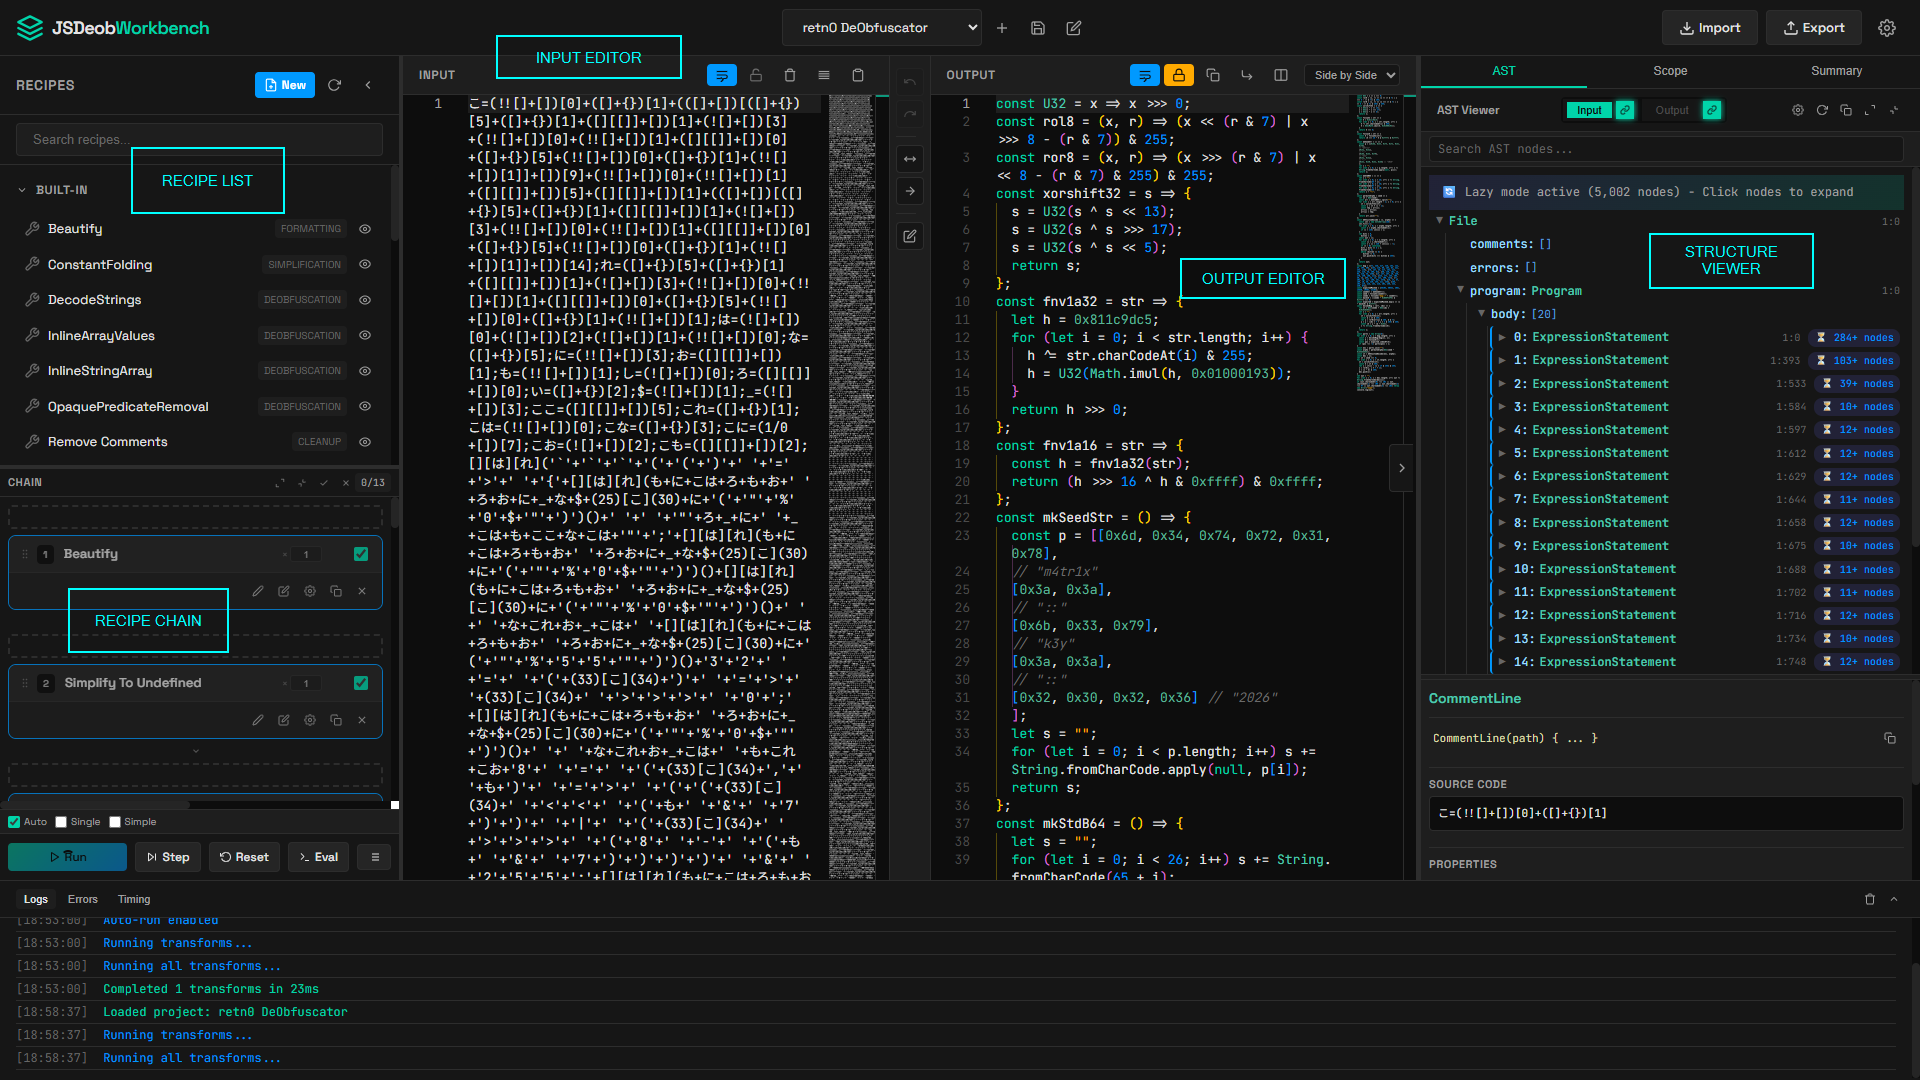 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 ghostoverflow/cve-2024-28397-command-execution-poc
This vulnerability arises from incomplete sandboxing in js2py, where crafted JavaScript can traverse Python’s internal object model and access…
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
 marven11/cve-2024-28397-js2py-sandbox-escape
CVE-2024-28397: js2py sandbox escape, bypass pyimport restriction.
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
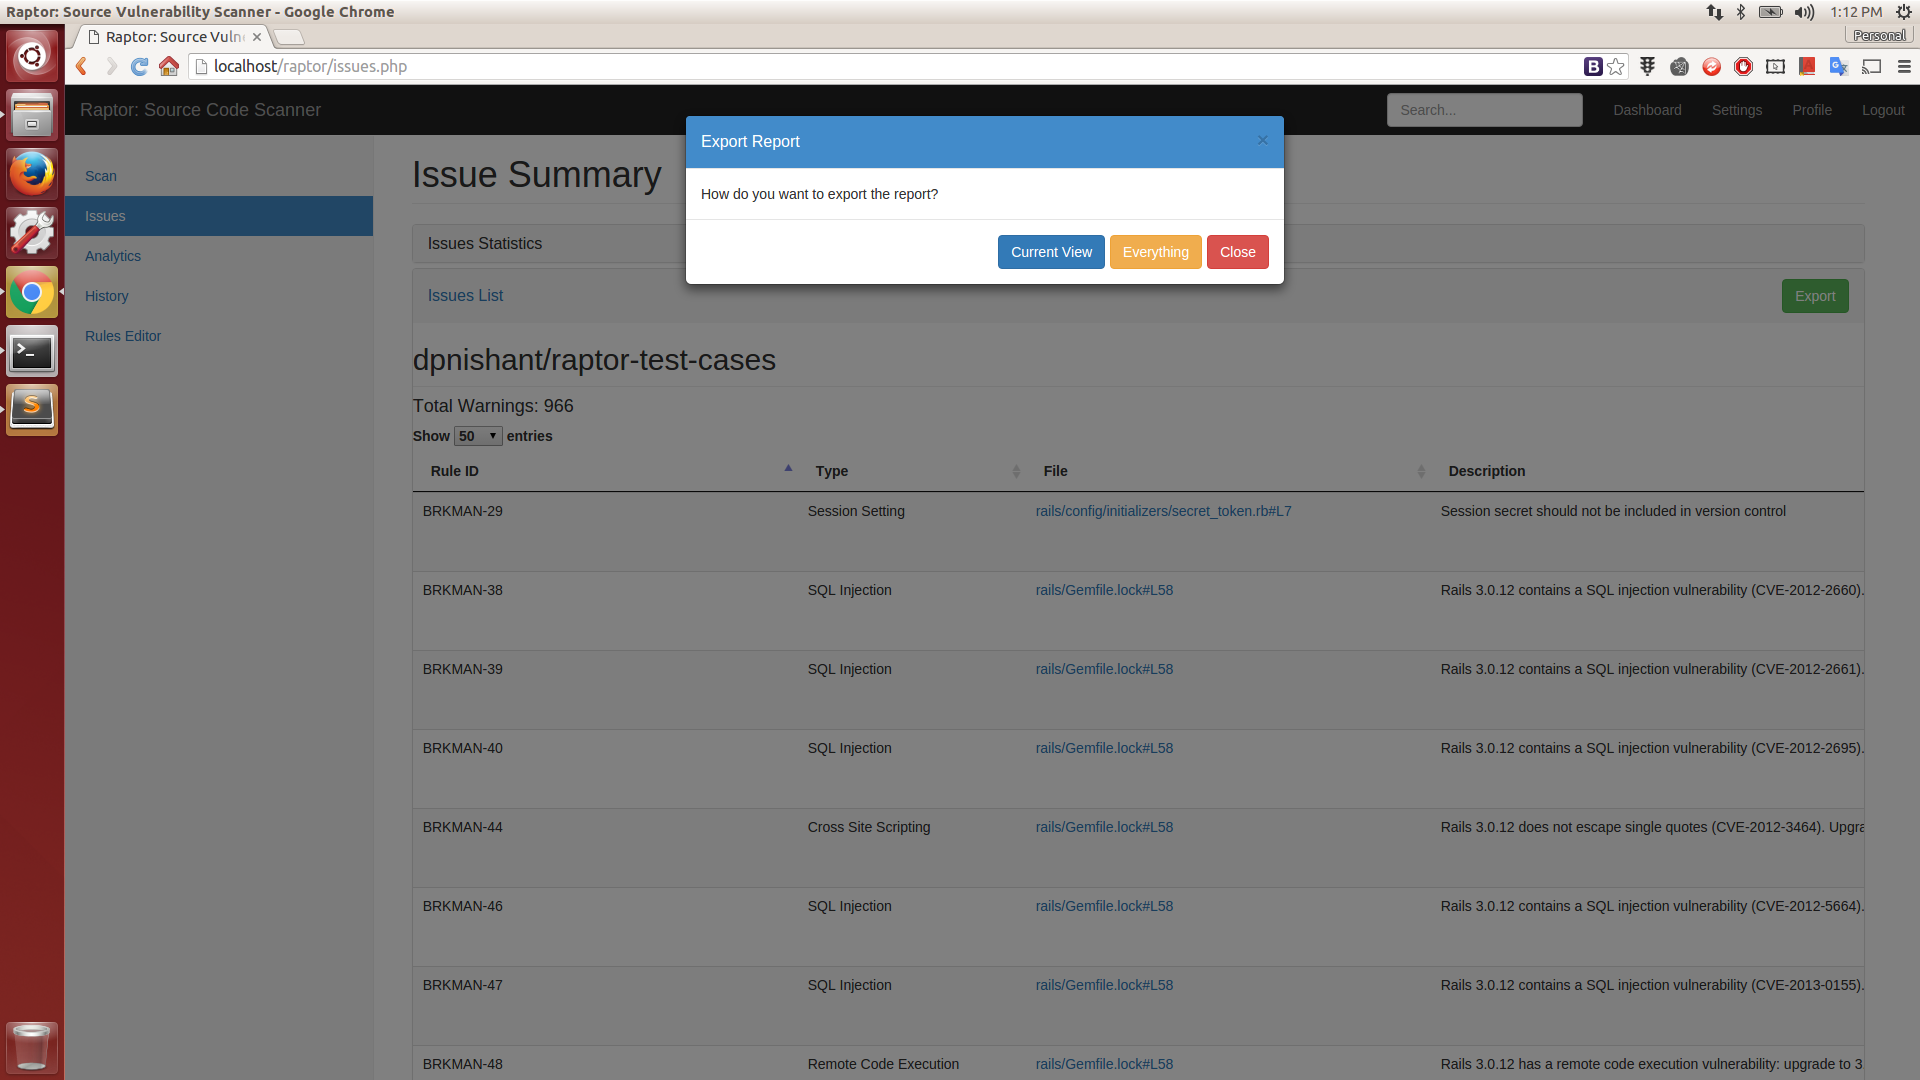 dpnishant/raptor
Web-based Source Code Vulnerability Scanner
 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques
 maximilianmarx/bassmaster-rce
Exploiting CVE-2014-7205 by injecting arbitrary JavaScript resulting in Remote Code Execution.
 releaseown/exploit-js2py
The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…
 ch4120n/cve-2026-58138
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 releaseown/analysis-and-poc-n8n-cve-2025-68613
Technical study of the CVE-2025-68613 vulnerability in n8n, covering affected versions, laboratory exploration scenario, offensive and defensive…
 bhavyakcwestern/hacking-pdf.js-vulnerability
CVE-2024-4367