
appshark
 bytedance/appshark
Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…
android-securitycode-analysisstatic-analysis+1
1.8k
bytedance/appsharkStatic taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
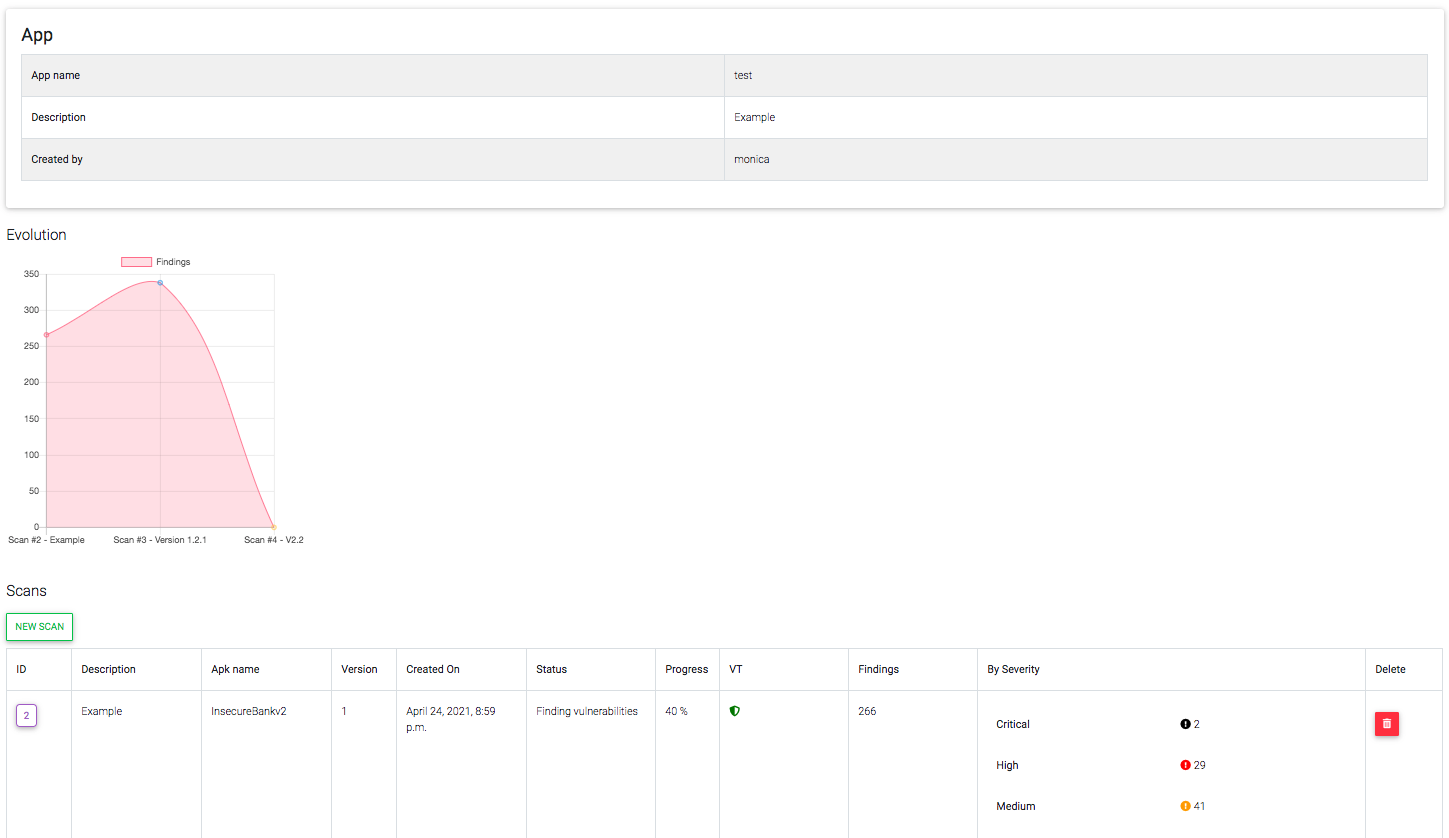 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
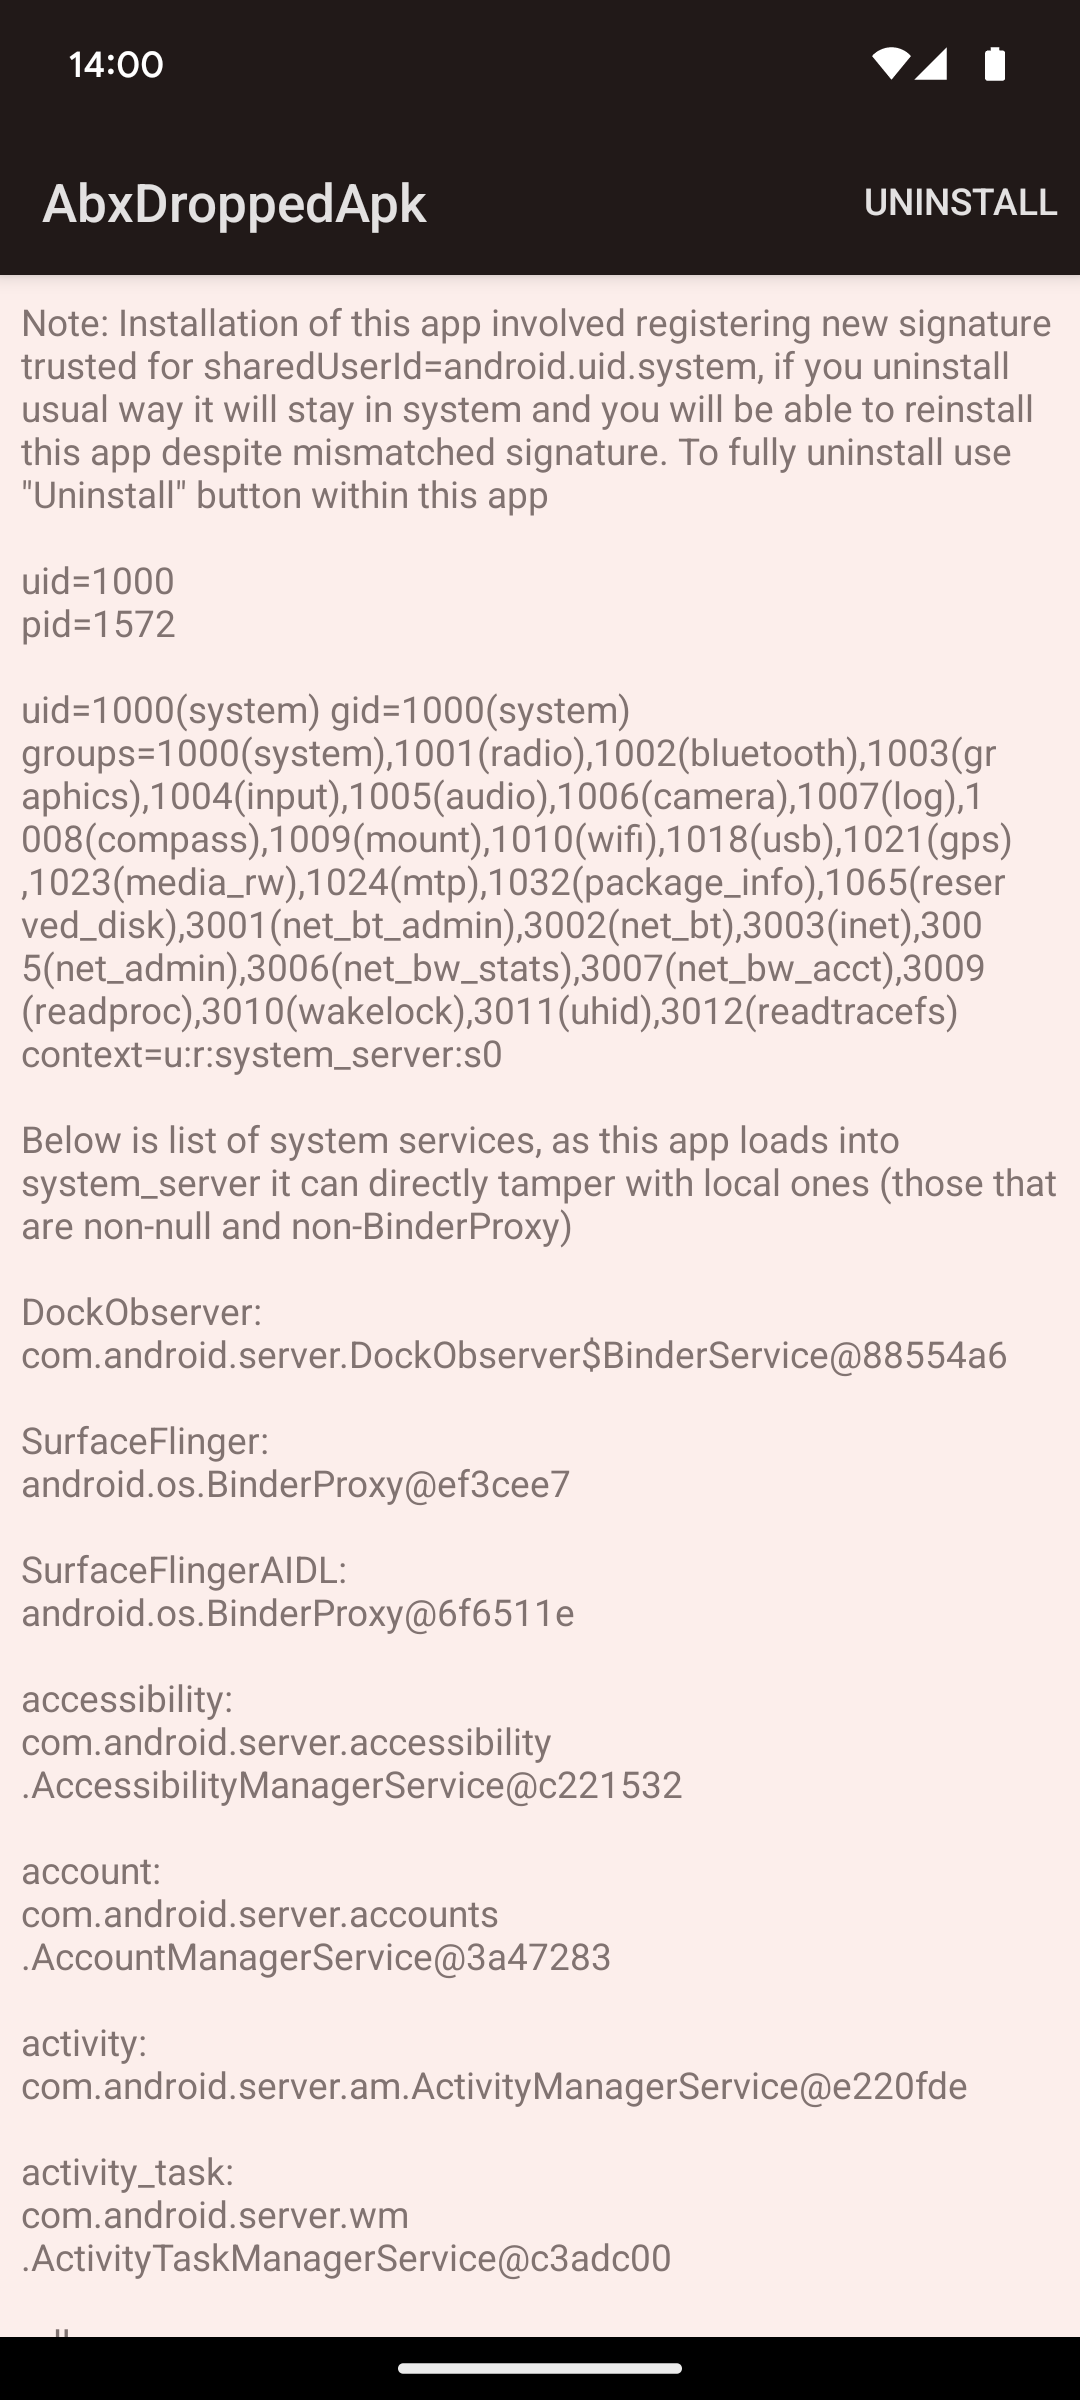 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
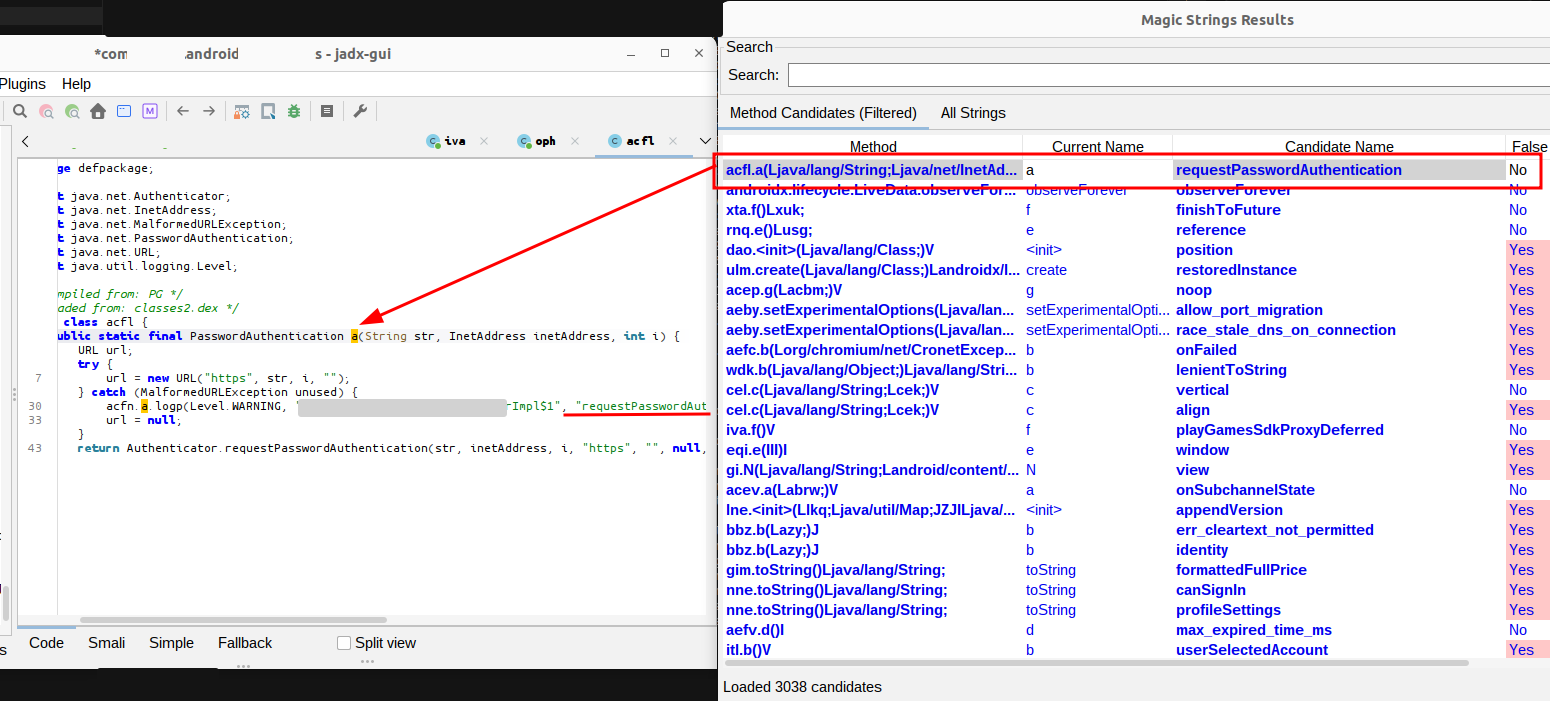 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
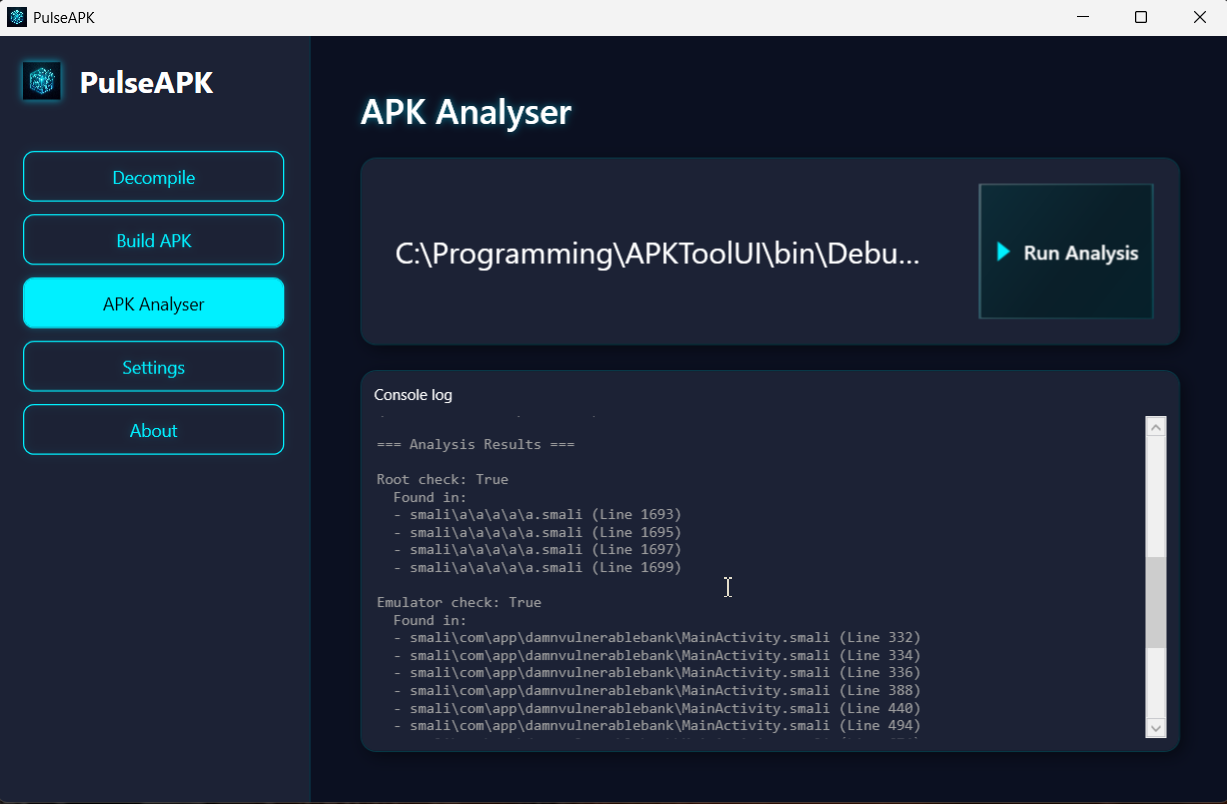 deemoun/pulseapk
PulseAPK is a WPF frontend for apktool and uber-signer with drag-and-drop support, live decompilation output, smali analysis, and integrated APK…
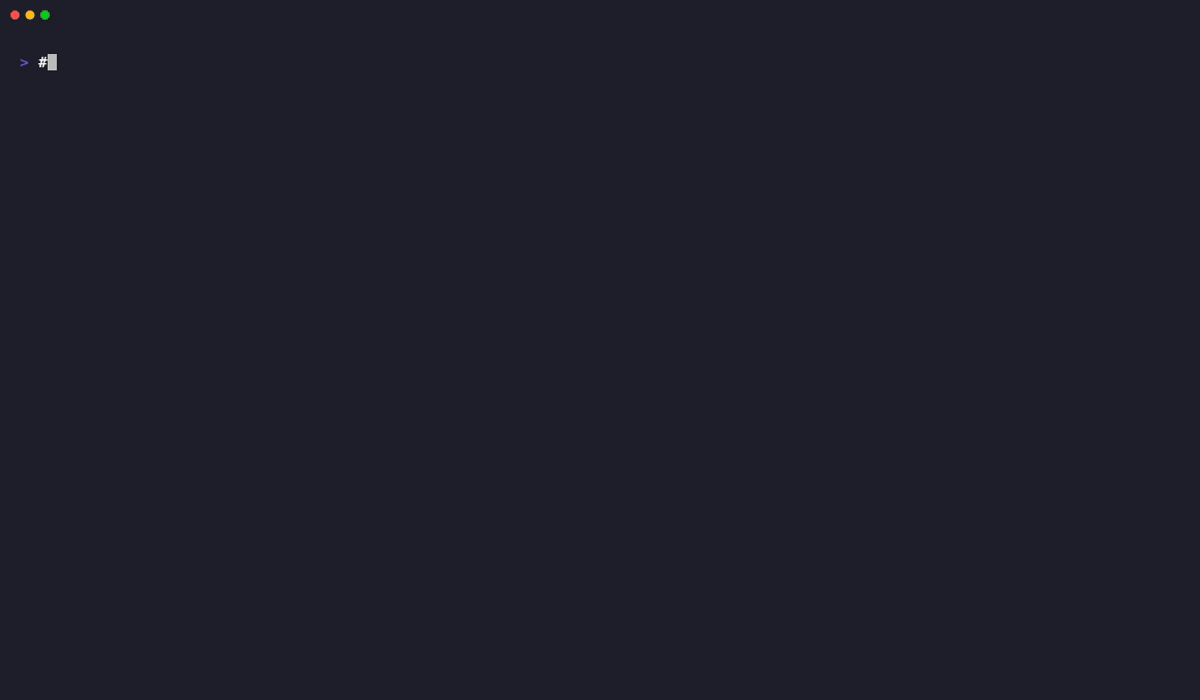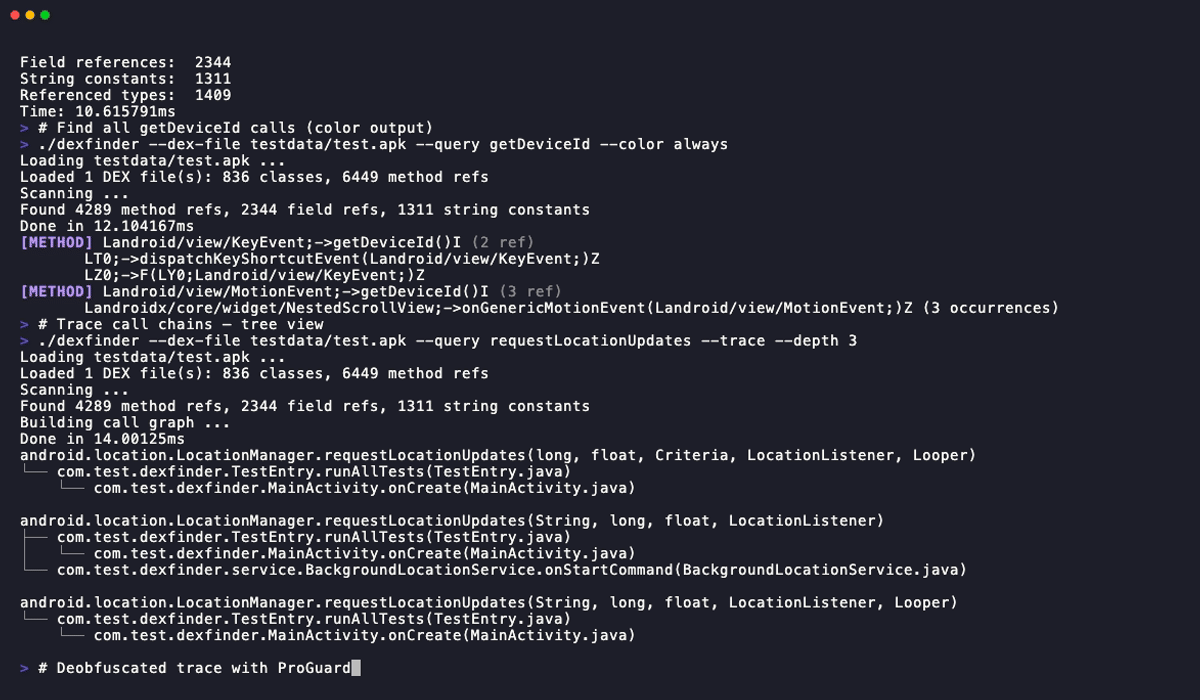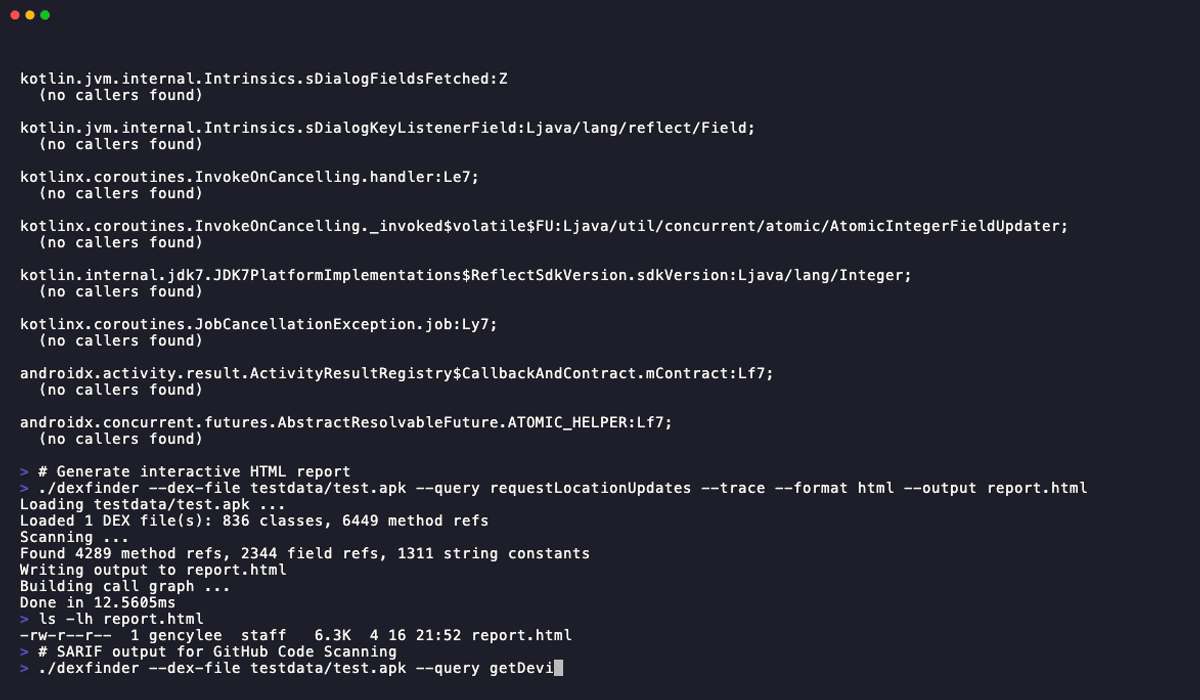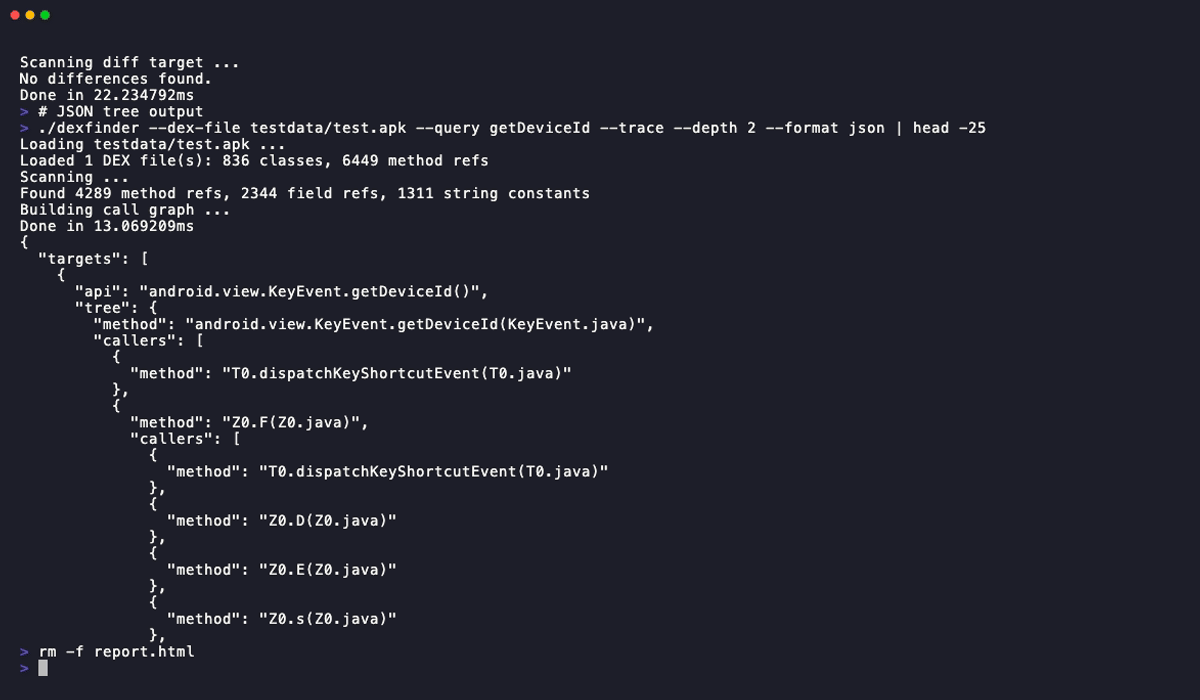 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 trailofbits/slither-mcp
MCP server for Slither static analysis of Solidity smart contracts
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
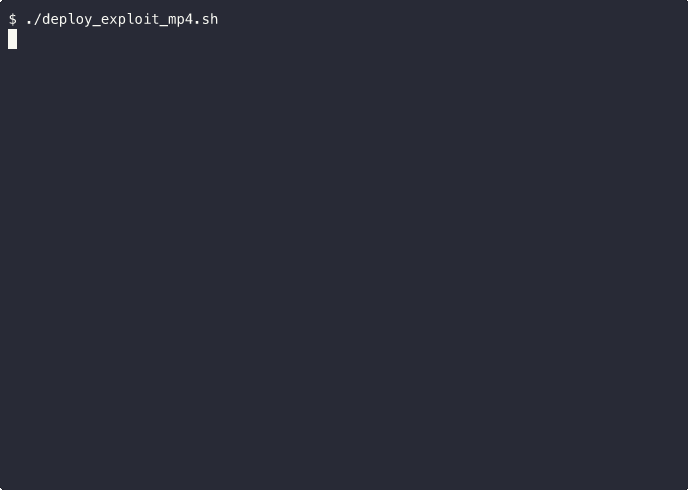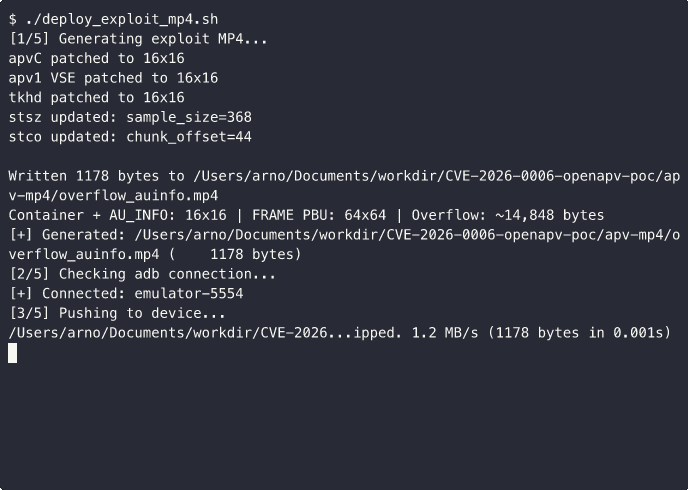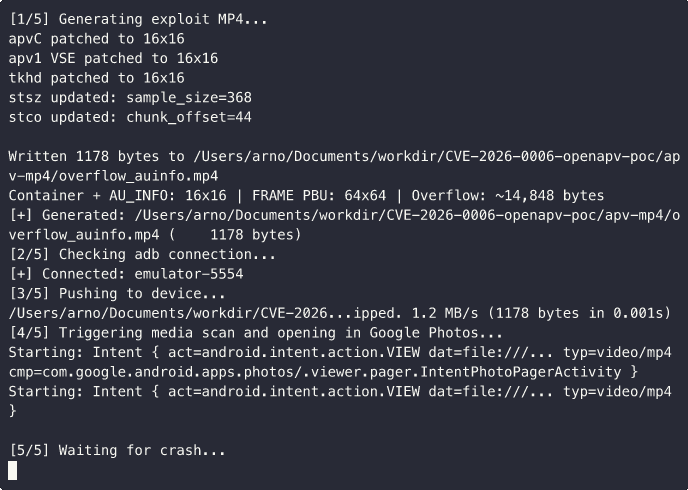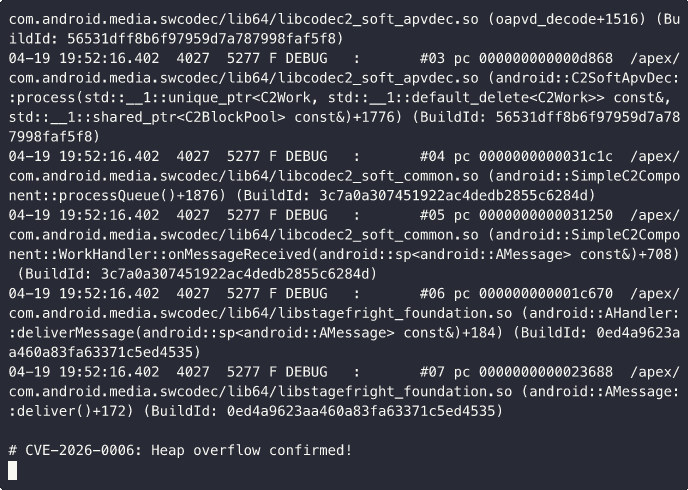 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing