

trivy-action
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
cloud-securitycode-analysiscontainer-security+5
1.4k
aquasecurity/trivy-actionRuns Trivy as GitHub action to scan your Docker container image for vulnerabilities
 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
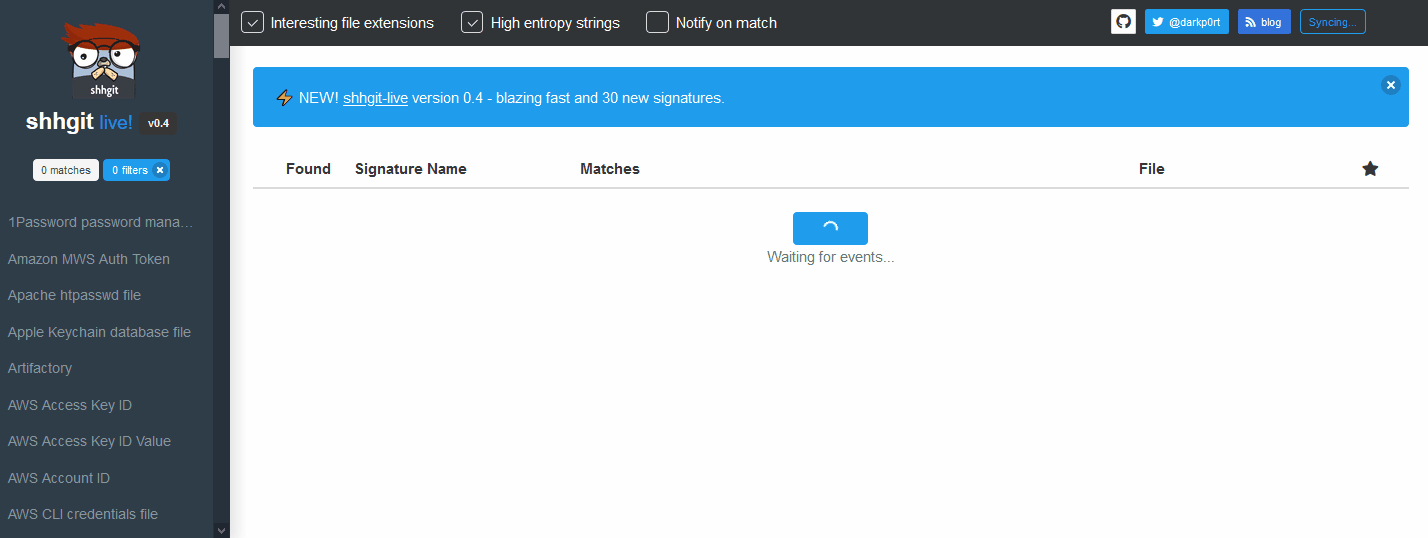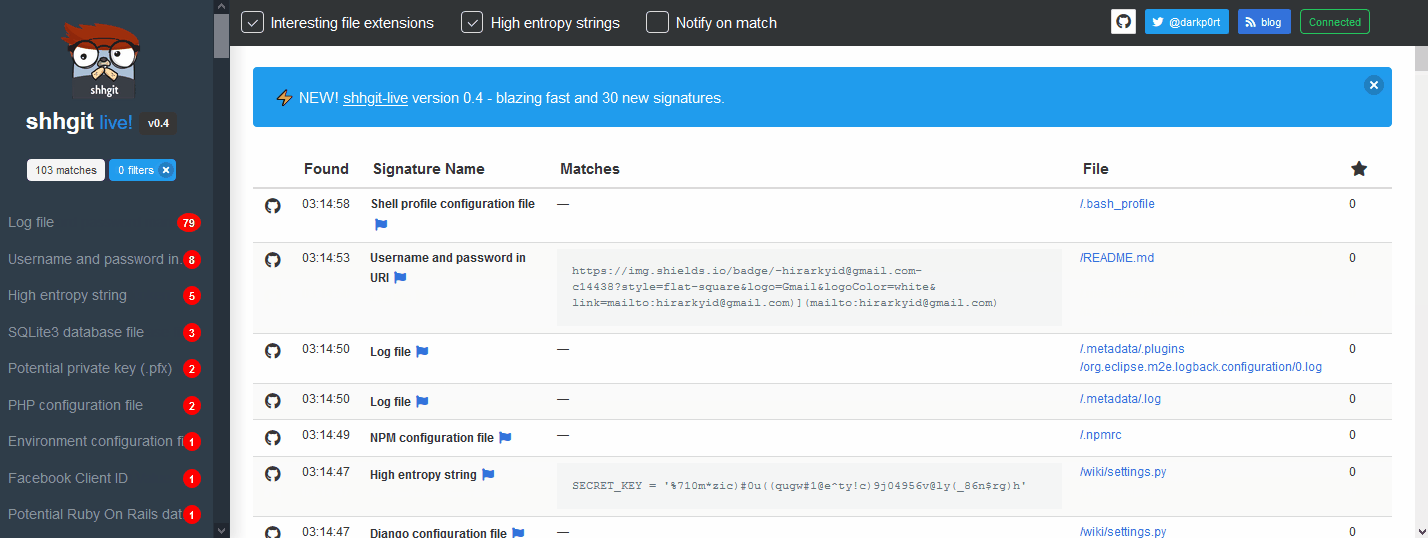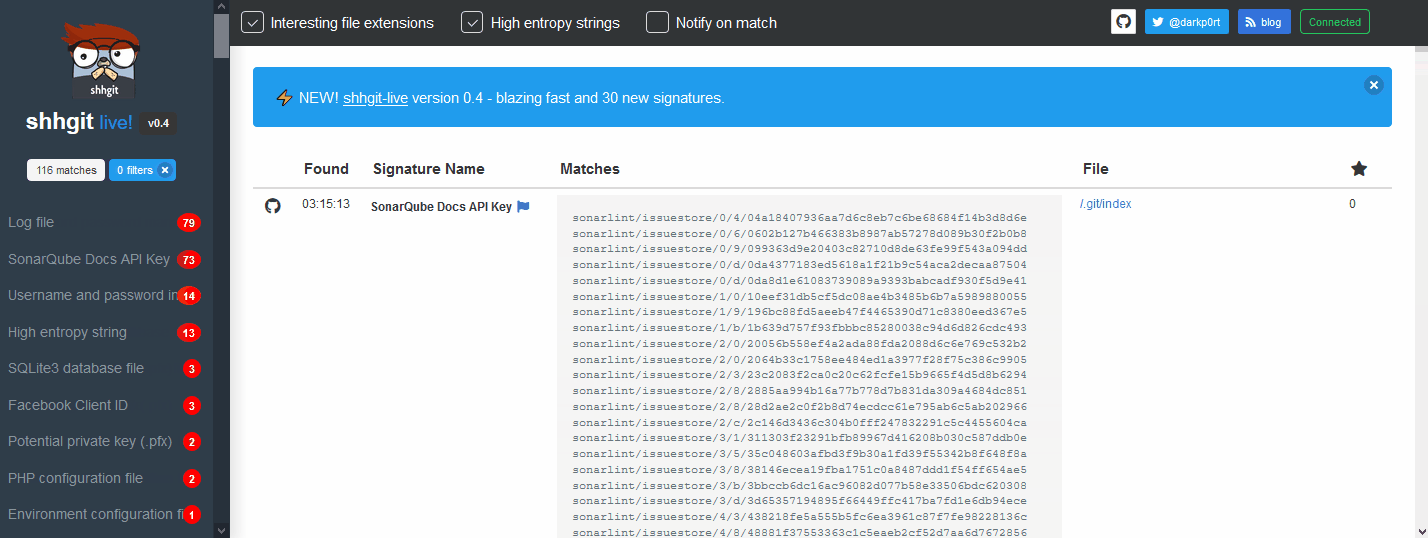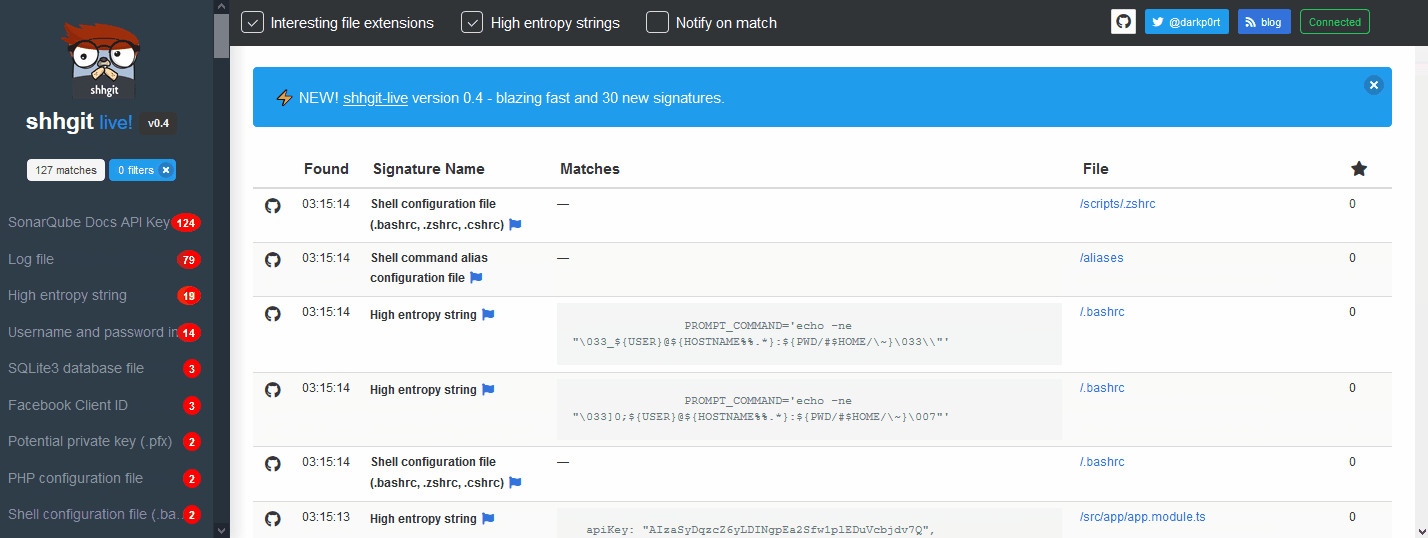 eth0izzle/shhgit
Ah shhgit! Find secrets in your code. Secrets detection for your GitHub, GitLab and Bitbucket repositories.
 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C

 google-github-actions/run-gemini-cli
A GitHub Action invoking the Gemini CLI.
 trailofbits/claude-code-devcontainer
Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.

 google/paranoid_crypto
Paranoid's library contains implementations of checks for well known weaknesses on cryptographic artifacts.
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 zhangzhuosjtu/web3bugs
Demystifying Exploitable Bugs in Smart Contracts
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 viruscamp/luadec
Lua Decompiler for lua 5.1 , 5.2 and 5.3
 tellerops/teller
Cloud native secrets management for developers - never leave your command line for secrets.
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages