

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.0k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 safedep/vet
Protect against malicious open source packages 🤖
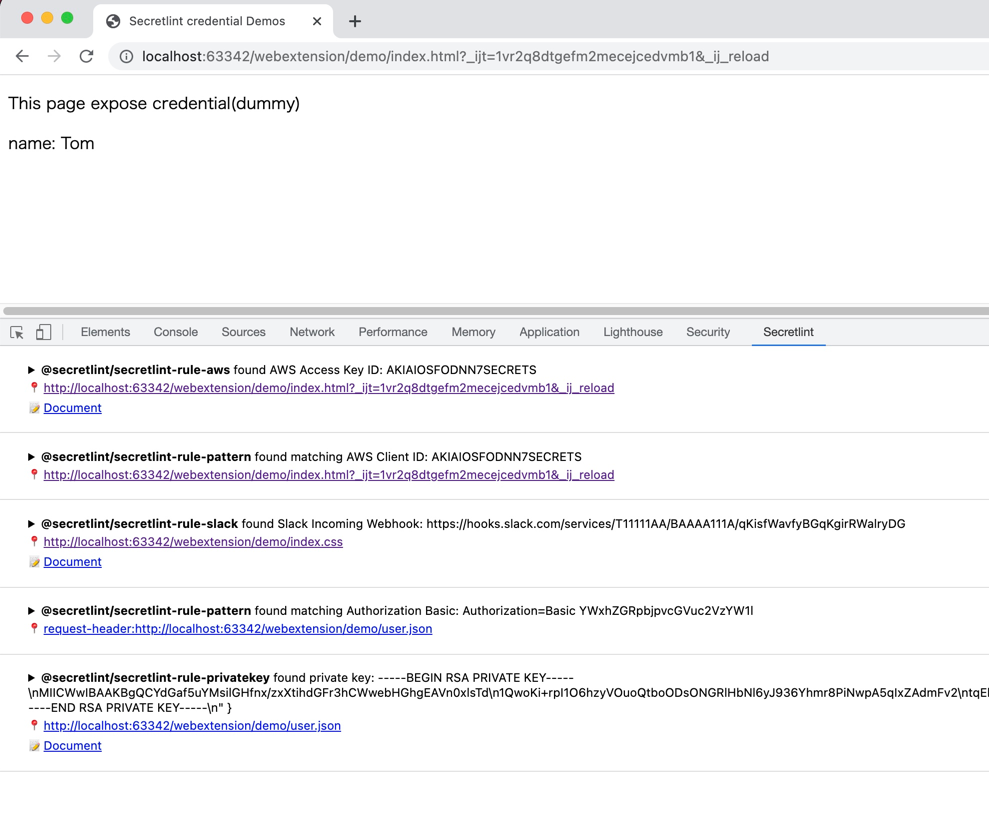 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 client9/libinjection
SQL / SQLI tokenizer parser analyzer
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 nccgroup/freddy
Automatically identify deserialisation issues in Java and .NET applications by using active and passive scans
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)