

CVE-2025-13486
 whattheslime/cve-2025-13486
CVE-2025-13486 - Remote Code Execution & Privilege Escalation exploit
code-analysiseducationexploitation+5
whattheslime/cve-2025-13486CVE-2025-13486 - Remote Code Execution & Privilege Escalation exploit
 intrinsec/comission
White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…
 josue87/wp_hunter
Static analysis of wordpress plugins
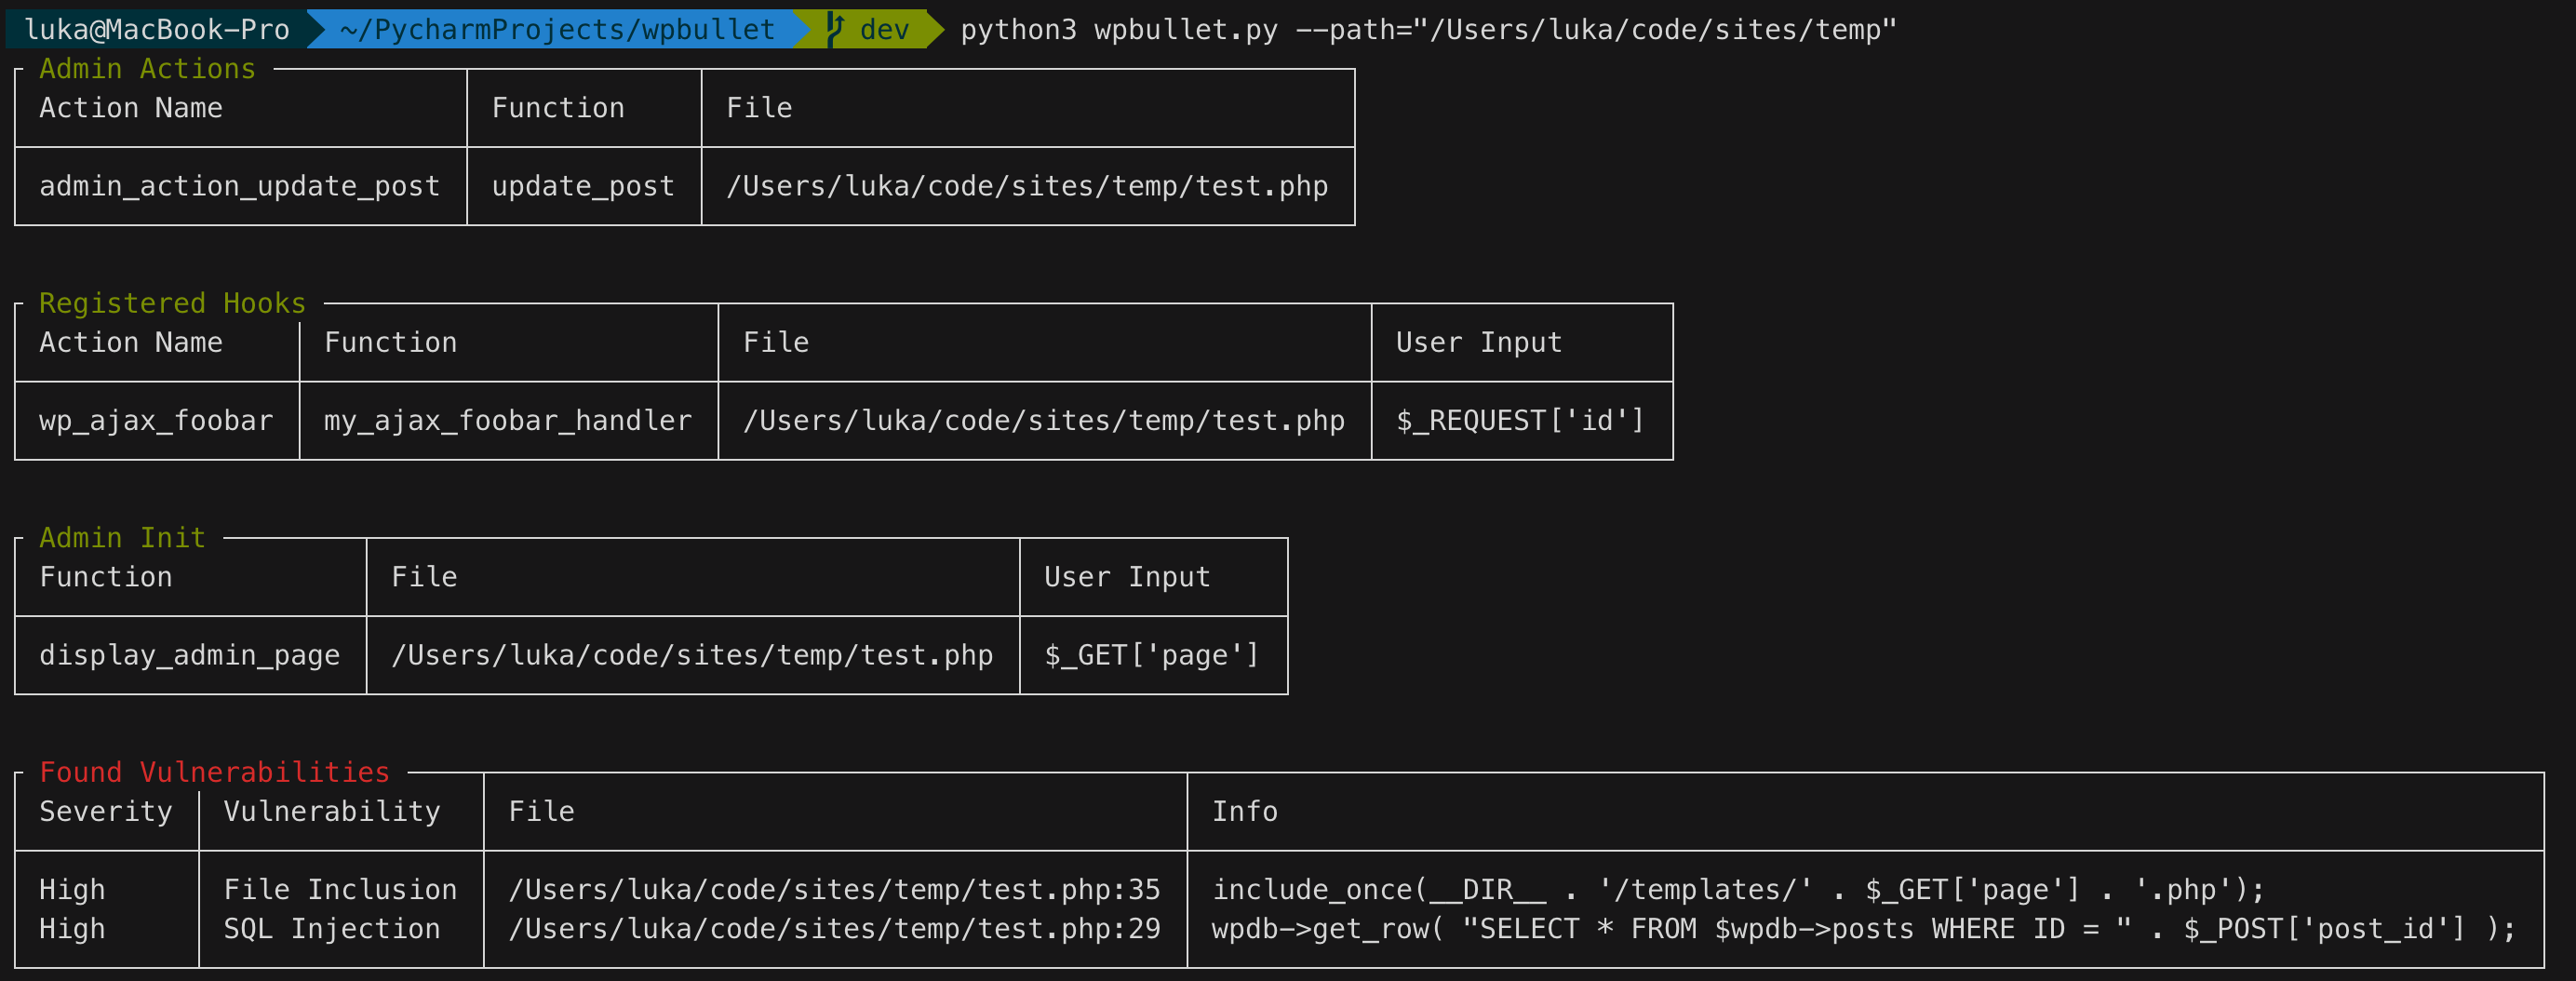 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
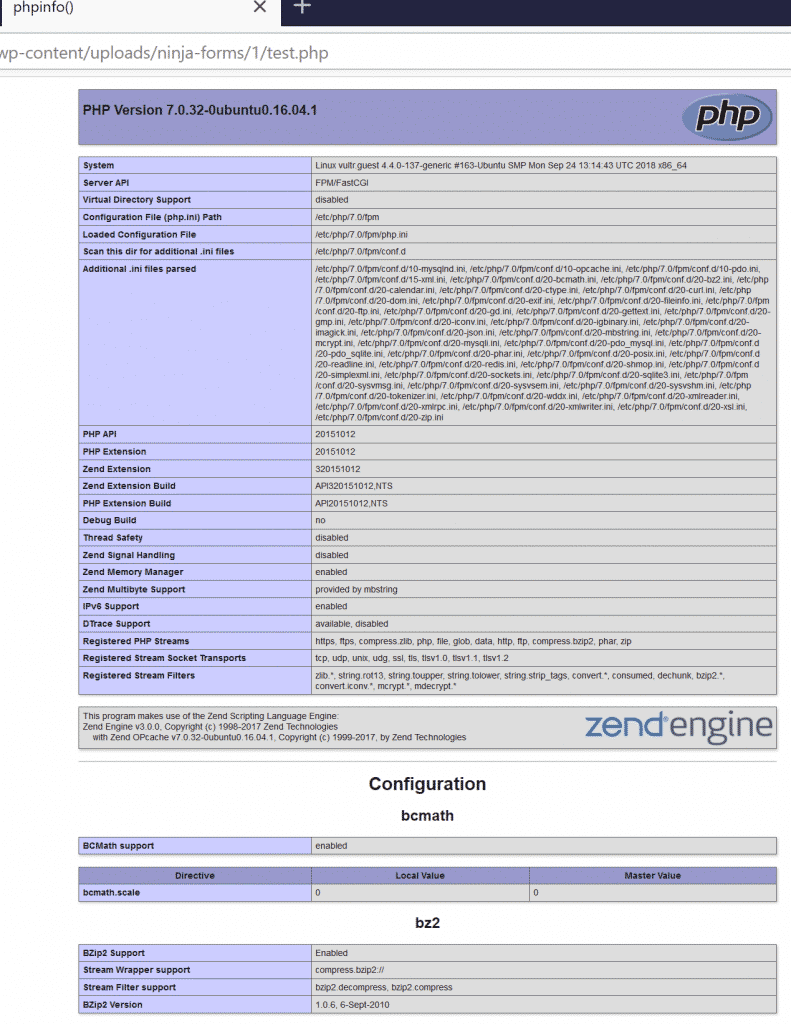 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 nxploited/cve-2025-3776
WordPress Verification SMS with TargetSMS Plugin <= 1.5 is vulnerable to Remote Code Execution (RCE)
 siunam321/cve-2024-7627-poc
Proof-of-Concept script for WordPress plugin Bit File Manager version 6.0 - 6.5.5 Unauthenticated Remote Code Execution via Race Condition…
 ghostinexile/cve-2026-63030-wp2shell
WordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)
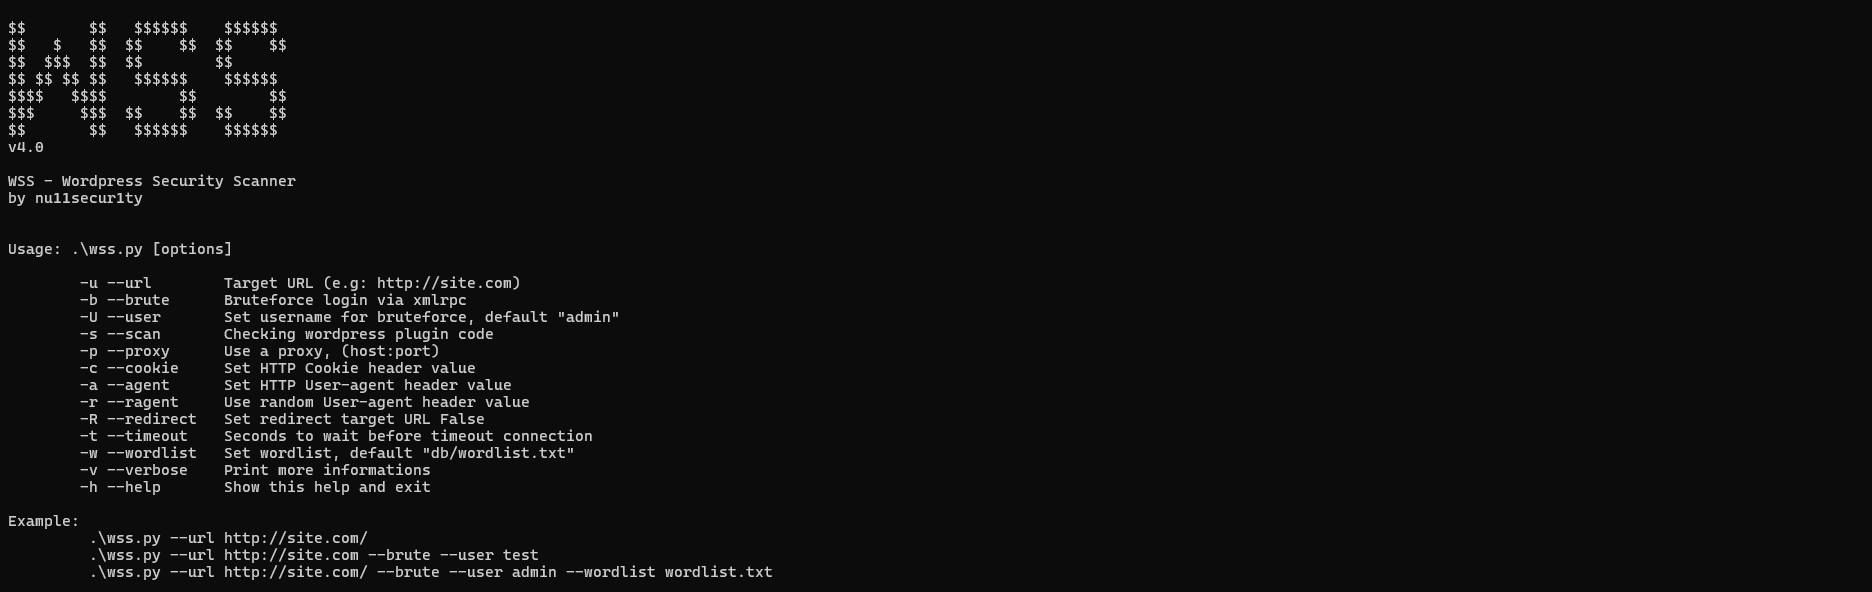 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 adamshaikhma/cve-2026-3300
Exploit for CVE-2026-3300, an unauthenticated stored XSS leading to RCE in Everest Forms Pro WordPress plugin, with a Python script to generate a…
 motikan2010/cve-2023-6553-poc
Python proof-of-concept exploit for CVE-2023-6553, demonstrating unauthenticated remote code execution via PHP filter chain in the Backup Migration…
 hunthubspace/cve-2024-3105-poc
A PoC Exploit for CVE-2024-3105 - The Woody code snippets – Insert Header Footer Code, AdSense Ads plugin for WordPress Remote Code Execution (RCE)
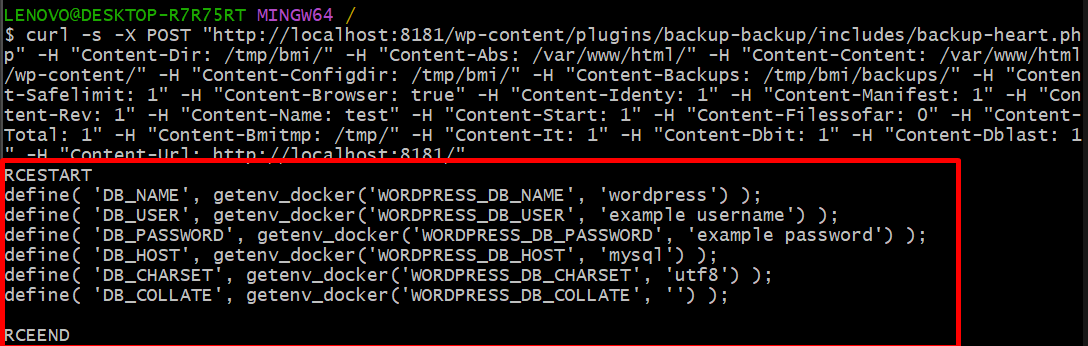 dungsocool/cve-2023-6553
Proof-of-concept exploit and technical write-up for CVE-2023-6553, an unauthenticated PHP file inclusion vulnerability enabling remote code execution…
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 izxci/cve-2026-49085
PHP Object Injection exploit for WP Insightly (CVE-2026-49085). Provides proof-of-concept code to demonstrate and test the vulnerability in affected…