

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.3k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 imran-parray/mind-maps
Mind-Maps of Several Things
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
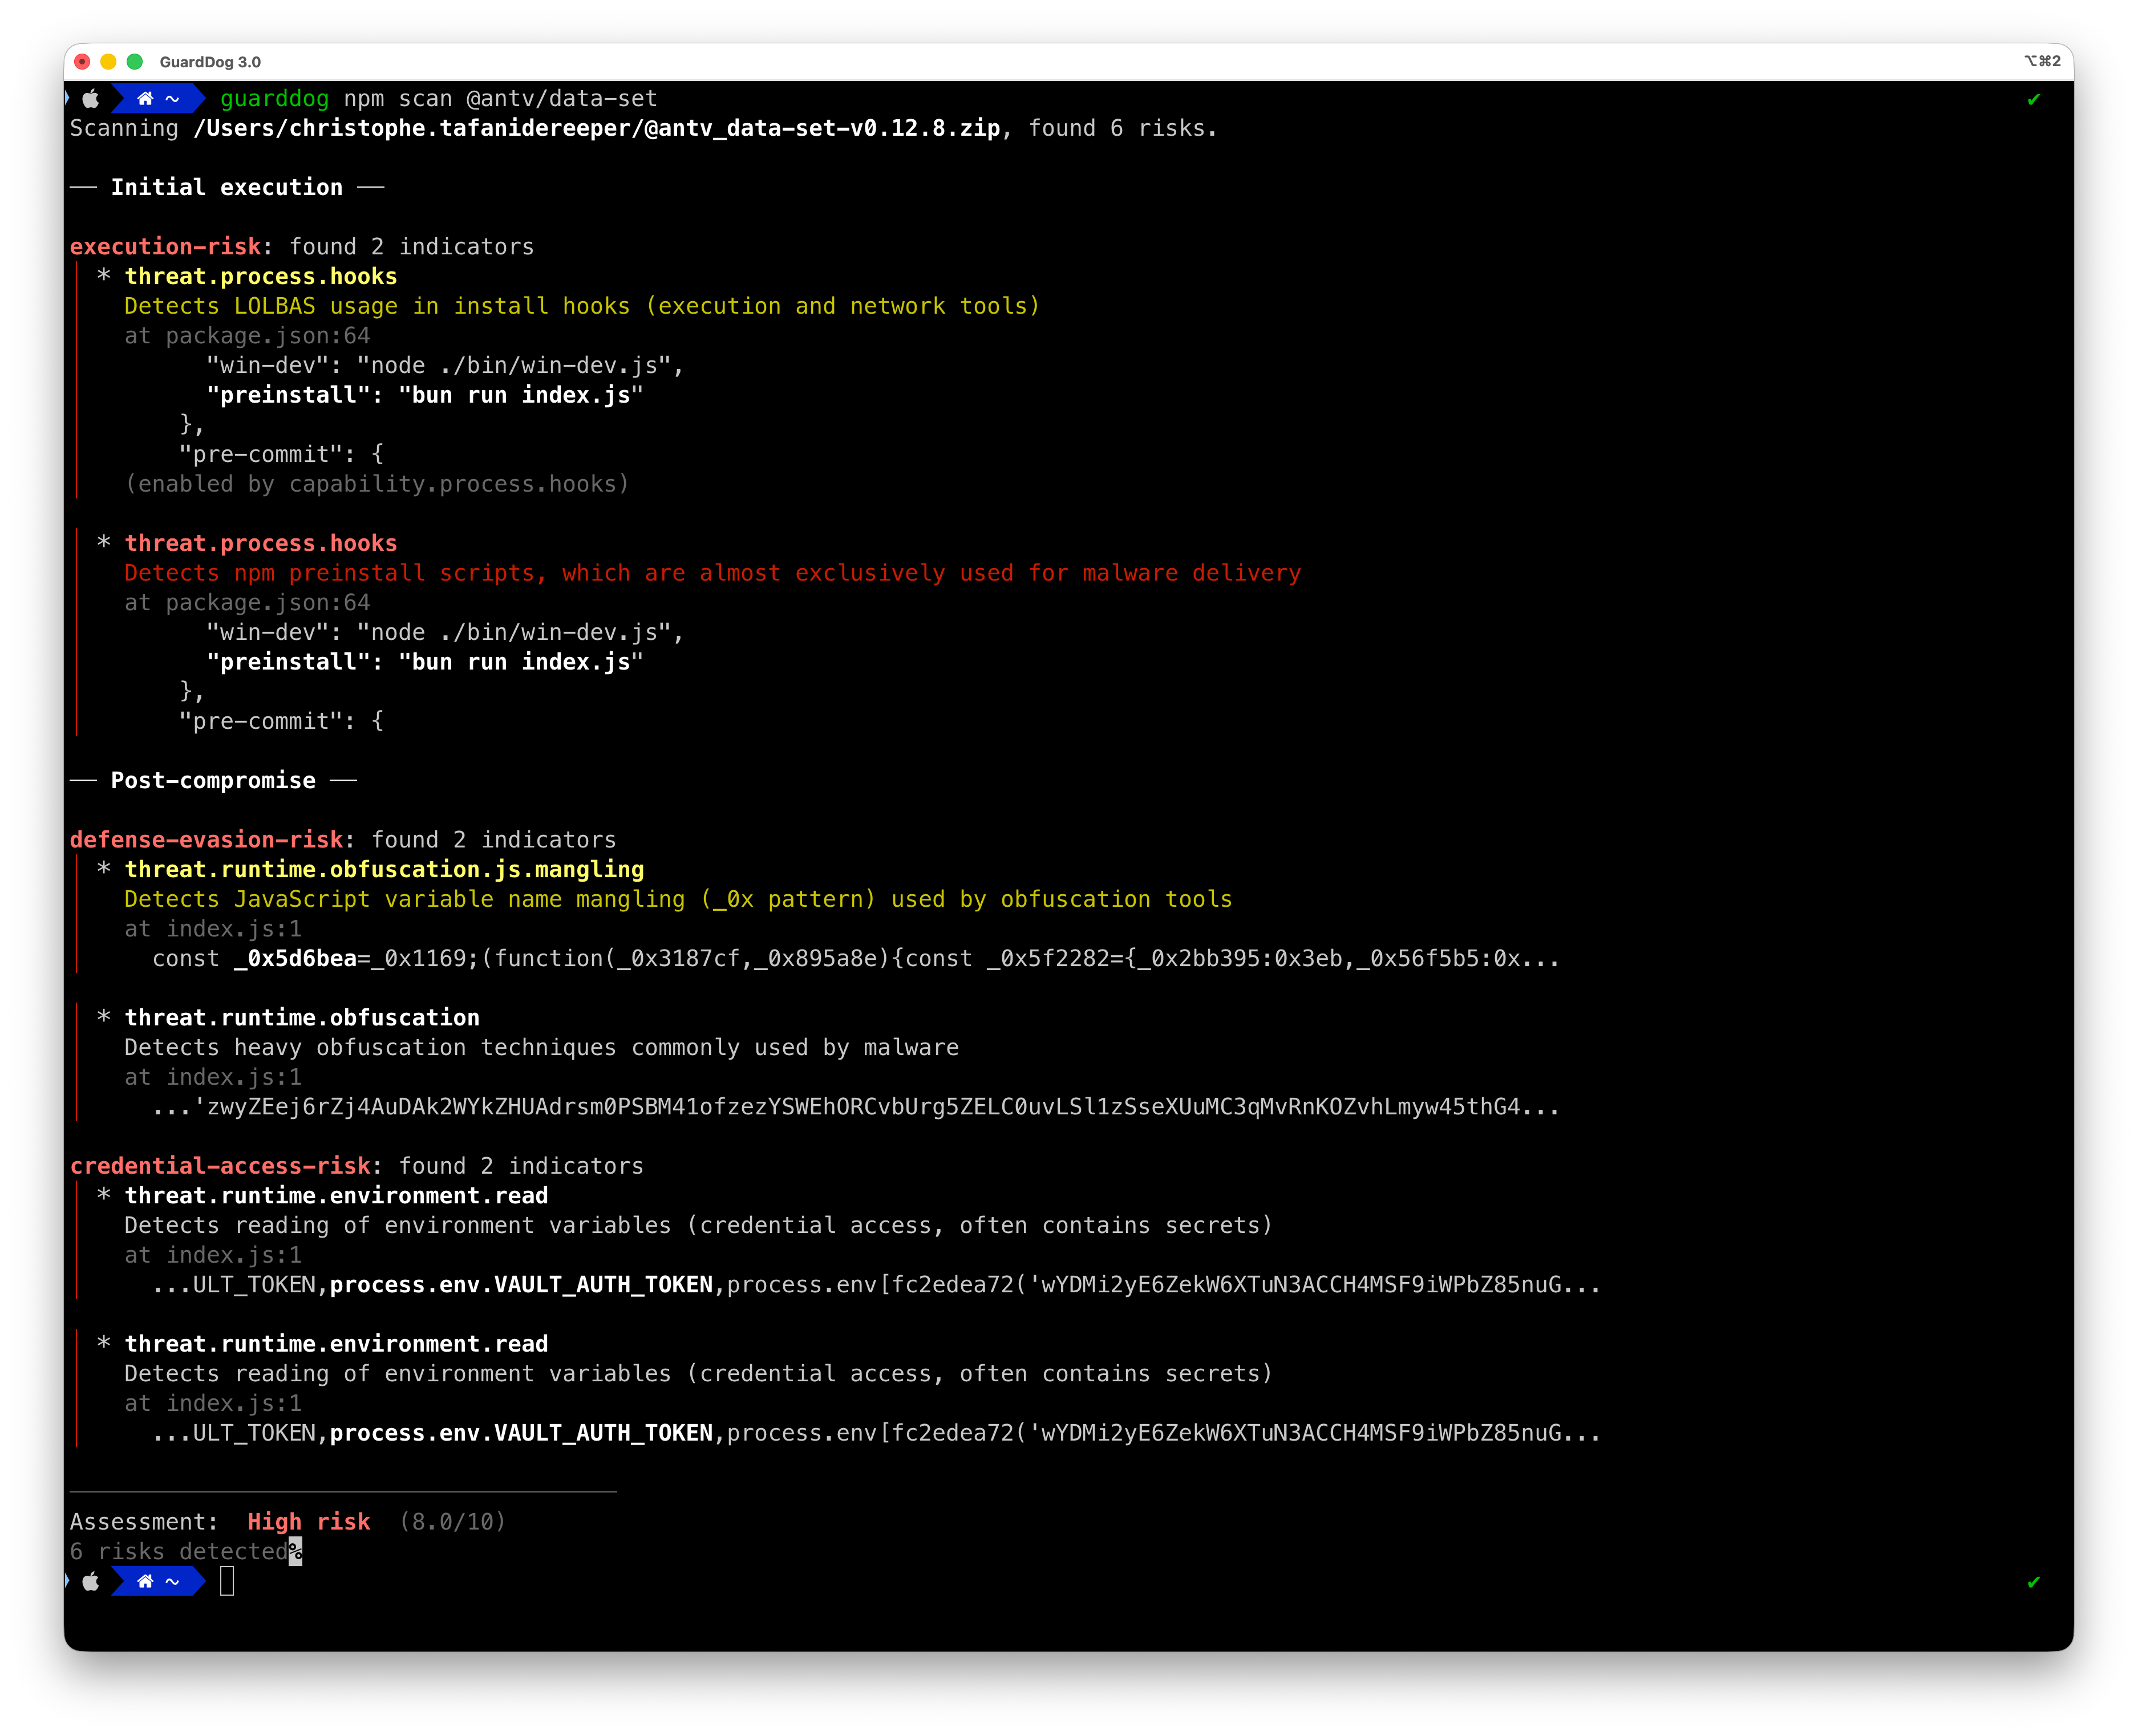 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 p3nt4/powershdll
Run PowerShell with rundll32. Bypass software restrictions.