cve-2022-22947-spring-cloud-gateway

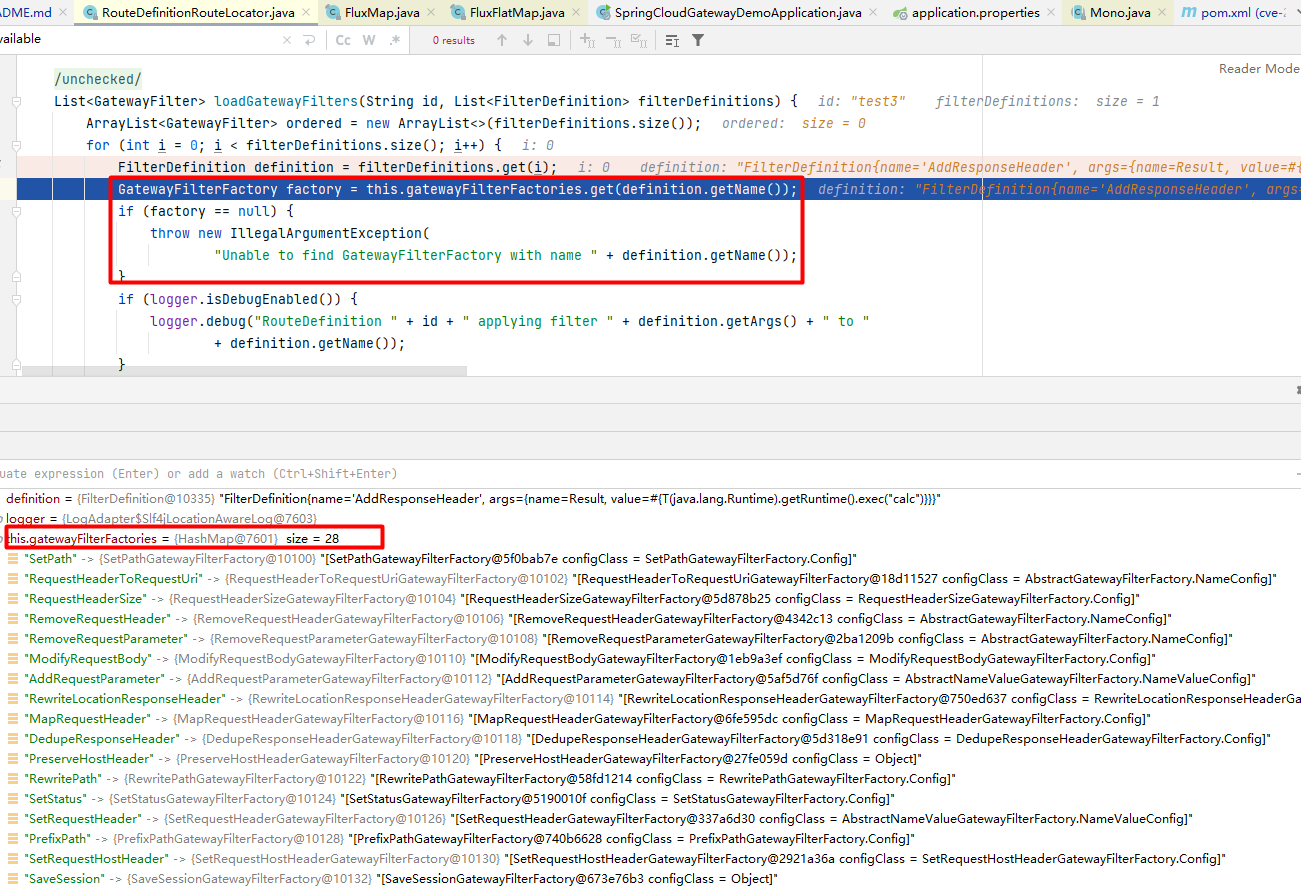
Detailed analysis and exploit for CVE-2022-22947, a remote code execution vulnerability in Spring Cloud Gateway via SpEL injection in the Actuator…

Detailed analysis and exploit for CVE-2022-22947, a remote code execution vulnerability in Spring Cloud Gateway via SpEL injection in the Actuator…

Proof-of-concept exploit for CVE-2023-49314 demonstrating code injection in Asana Desktop on macOS via Electron Fuses, with automated vulnerability…

Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…

Authenticated low-privileged RCE in Coolify via unsanitized shell commands in the Git Repository field.

Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…

Exploit tool for CVE-2026-22785, a critical code injection in orval < 7.18.0. Provides shell command execution and file scanning to demonstrate the…

Proof-of-concept exploit for CVE-2026-0766, a remote code execution vulnerability in OpenWebUI via tool code injection. Includes command execution,…

Exploit for CVE-2023-27372 with interactiev shell

Proof-of-concept exploit for CVE-2016-3714, a remote code execution vulnerability in ImageMagick's MVG file processing. Demonstrates shell command…

Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…

Trace untrusted OAuth endpoint URLs from source to shell sink — the CVE-2026-119025 attack class, checked in your code, lockfile and MCP configs.

Local classroom demo of NoSQL operator injection in LangGraph's MongoDBSaver (GHSA-98xf-r82g-9mhx / CVE-2026-48121). Fictional data only.

Multiple Command Injection vulnerabilities in openhands <0.62.0 allow an attacker to run arbitrary system commands.