

trivy-action
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
cloud-securitycode-analysiscontainer-security+5
1.4k
aquasecurity/trivy-actionRuns Trivy as GitHub action to scan your Docker container image for vulnerabilities
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 sakib570/cve-2018-1263-demo
Educational exploit demo for CVE-2018-1263 (phpMyAdmin RCE/LFI). Includes vulnerable environment setup via Docker and step-by-step attack walkthrough…
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
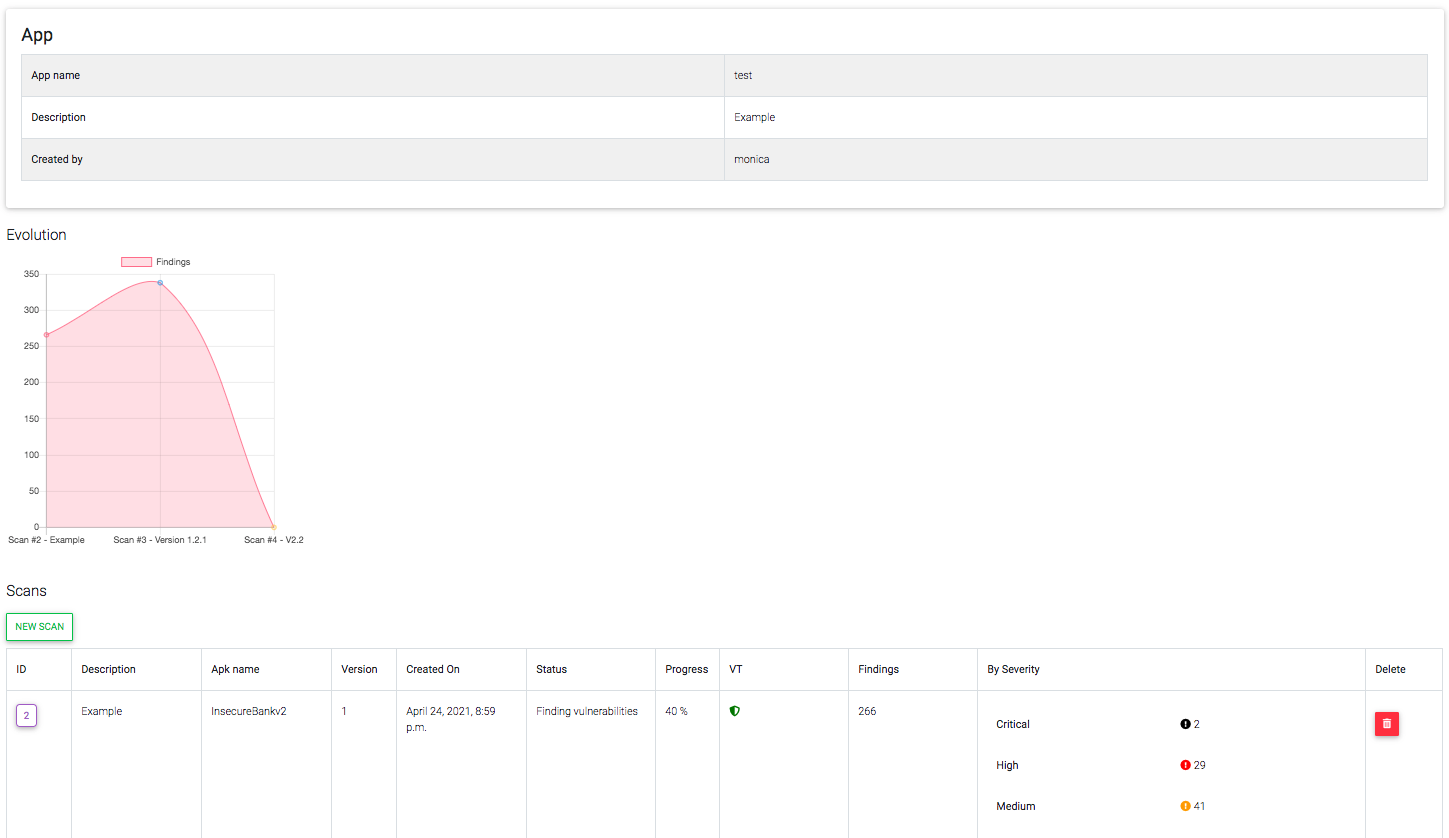 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 lucadibello/tmux-fuzzing
Enhanced fuzzing for tmux using OSS-Fuzz. Includes custom `cmd-fuzzer` and `argument-fuzzer` harnesses for improved code coverage and a PoC for…
 dosx-dev/obfus.h
Macro-header for compile-time C obfuscation (tcc, win x86/x64)
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
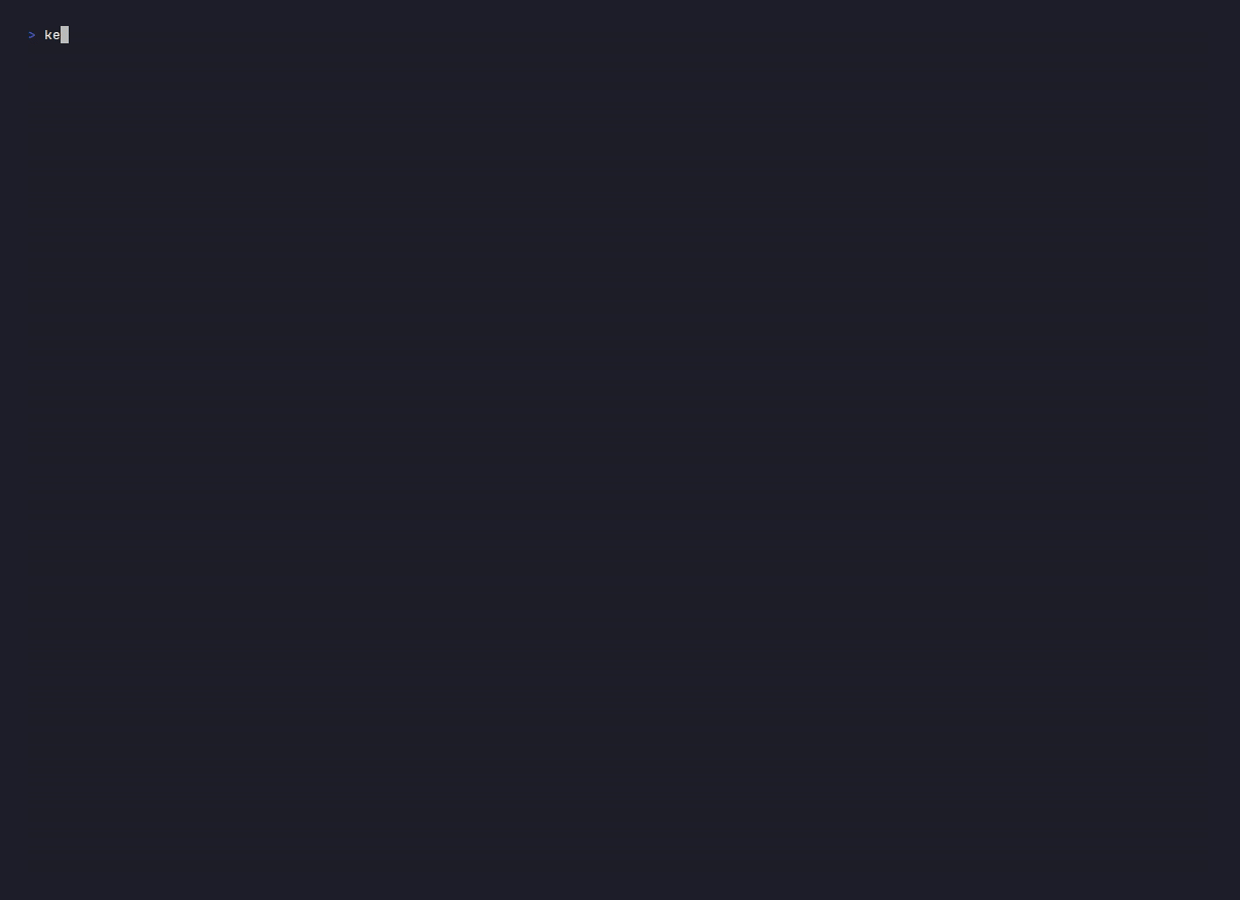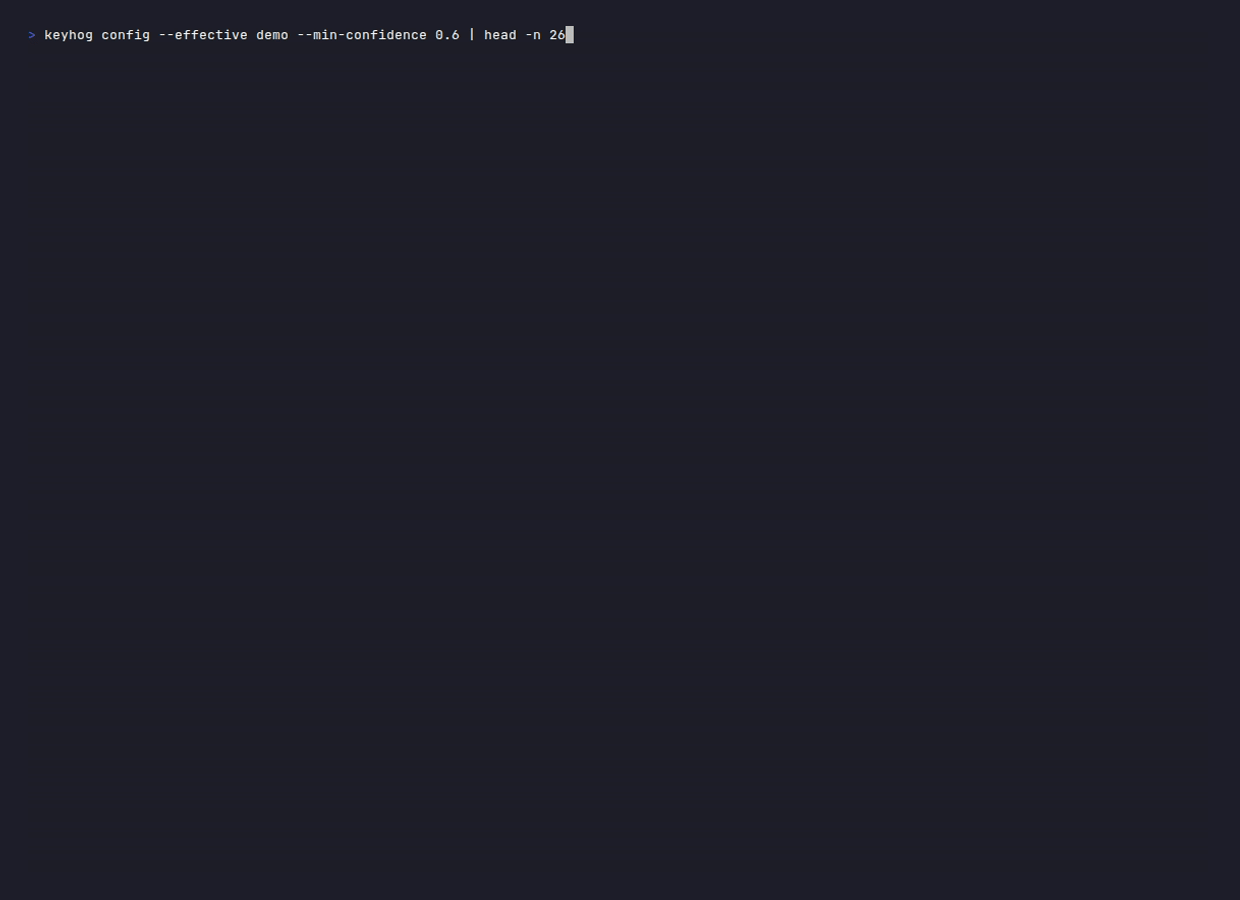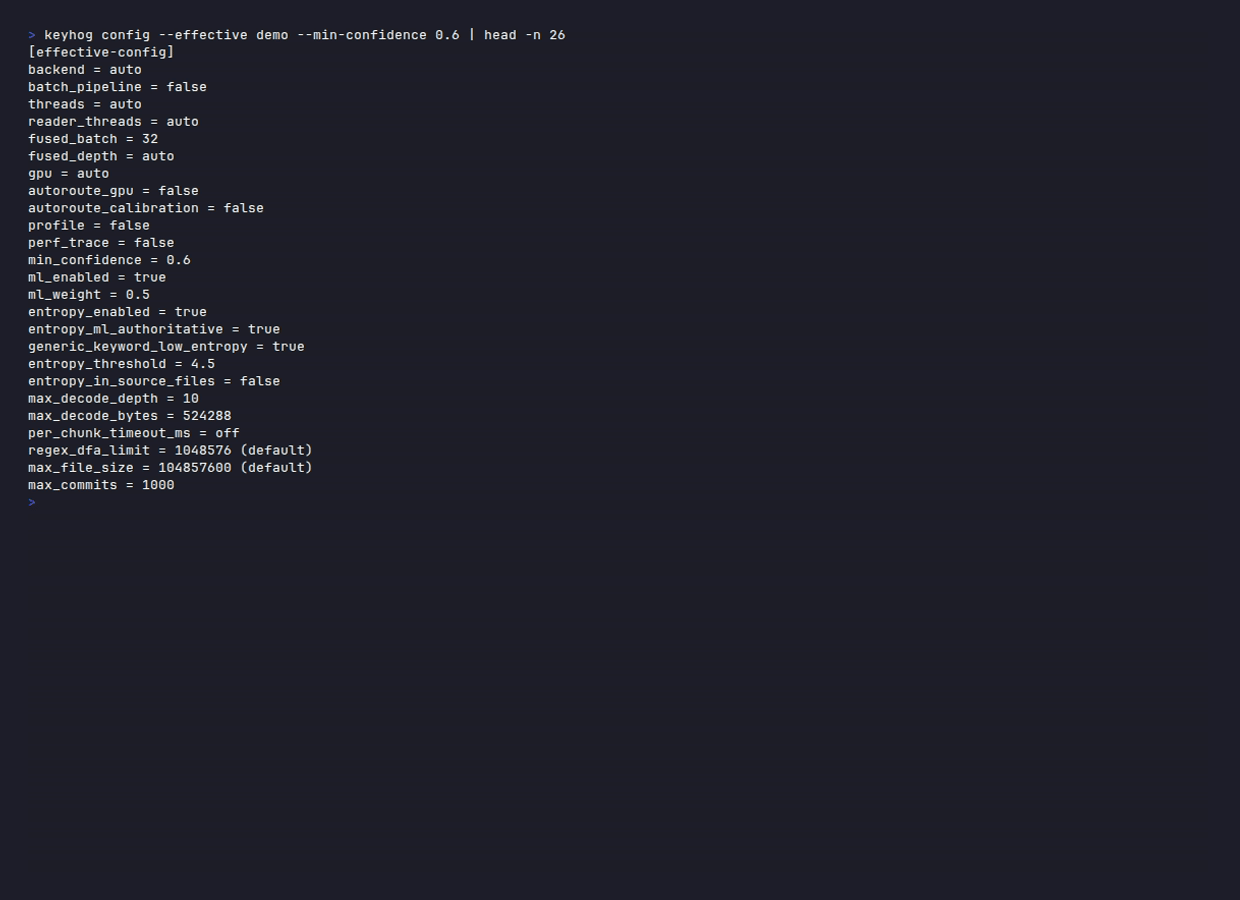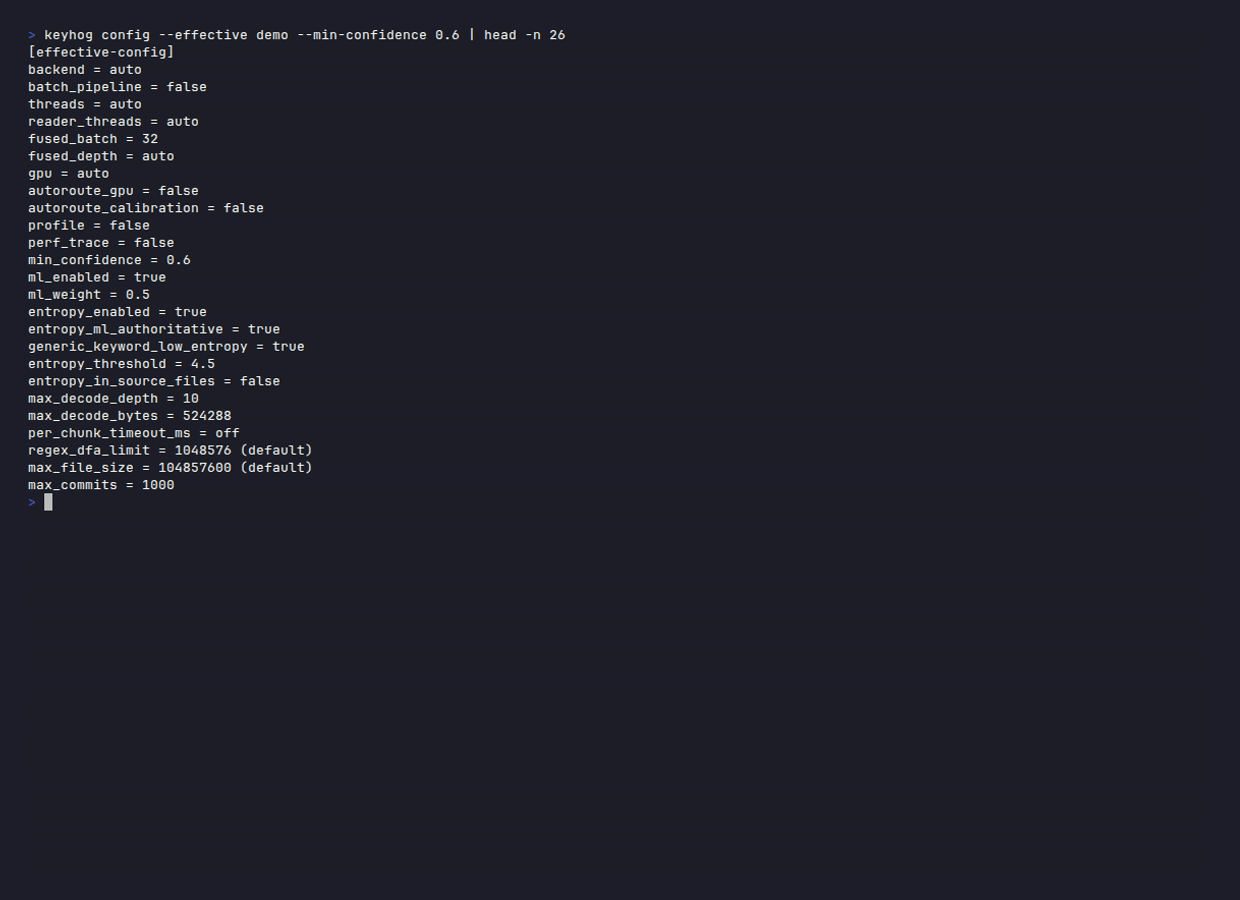 santhreal/keyhog
Open-source secret scanner in Rust
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…