
appsec-agent
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
ai-securitycode-analysisdevsecops+5
15
owasp/appsec-agentA TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 owasp/asvs
Application Security Verification Standard
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
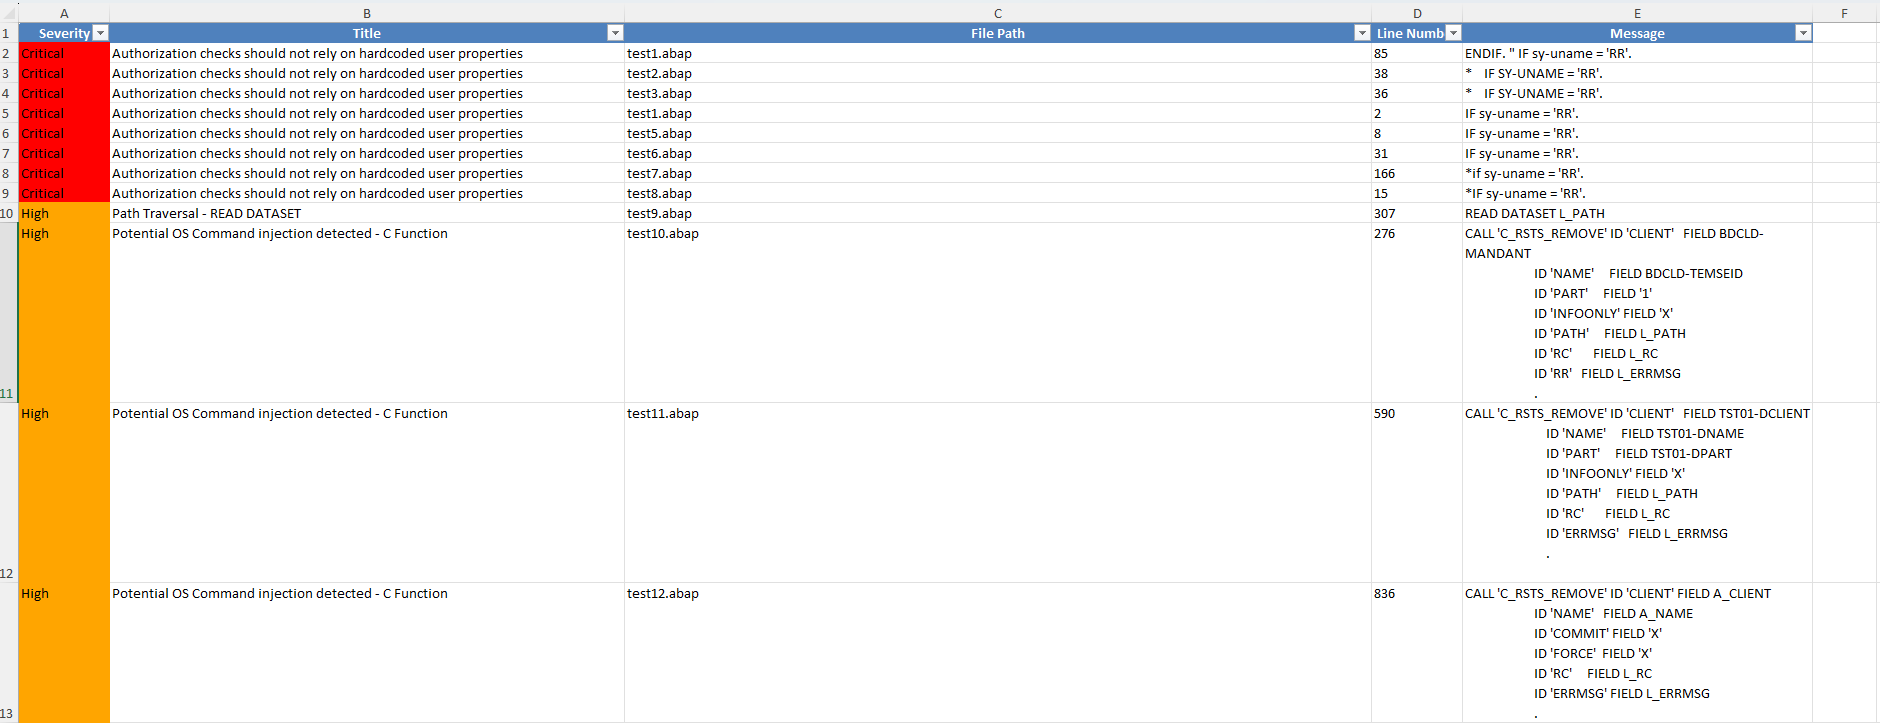
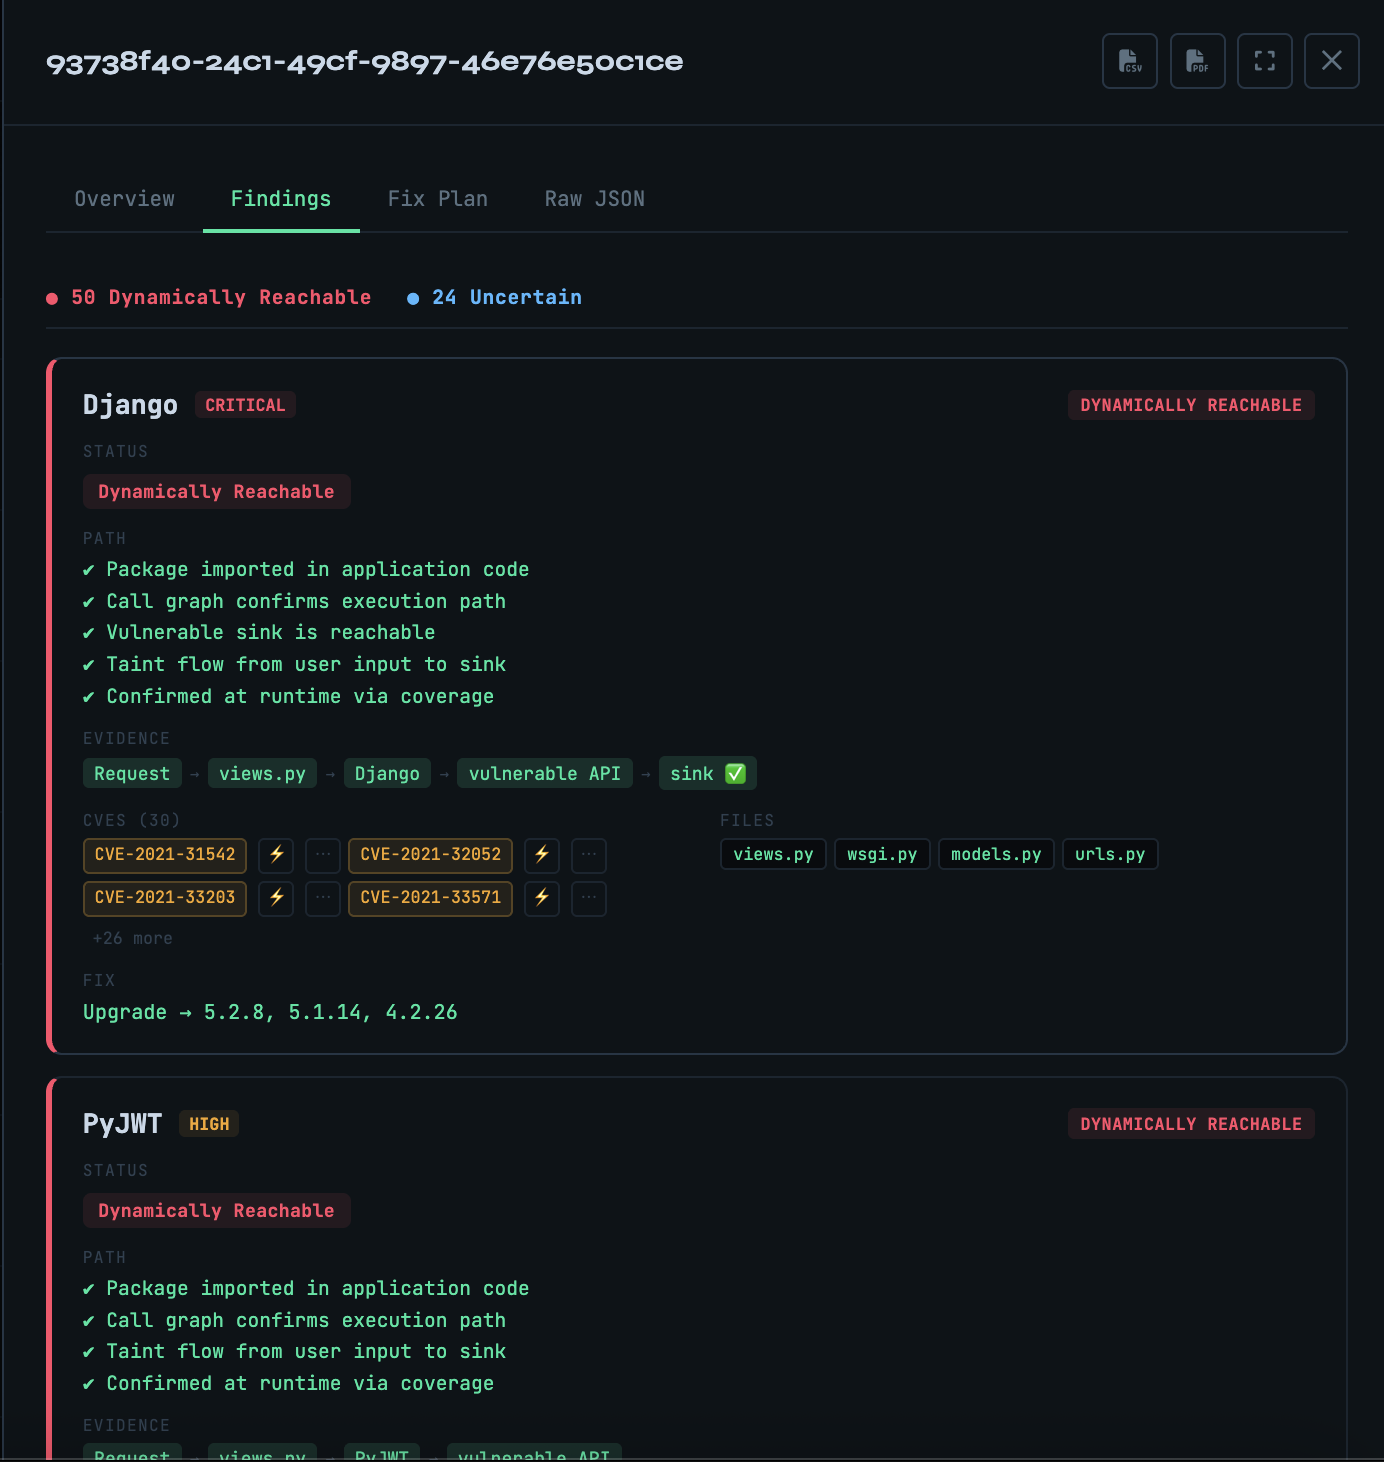 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 jeremylong/dependencycheck
The dependency-check repository has moved:
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP