
CVE-2023-6246
 elpe-pinillo/cve-2023-6246
C-based proof-of-concept exploit for CVE-2023-6246, targeting a privilege escalation vulnerability in the Linux kernel's syscalls. Tested on Fedora…
binary-exploitationcode-analysisexploitation+2
8
elpe-pinillo/cve-2023-6246C-based proof-of-concept exploit for CVE-2023-6246, targeting a privilege escalation vulnerability in the Linux kernel's syscalls. Tested on Fedora…
 0xeval/cve-2015-3224
Ruby on Rails Web Console (v2) Whitelist Bypass Code Execution implementation in Python
 ok0mo/cve-2022-24086-rce-poc
Verifed Proof of Concept on CVE-2022-24086
 louiselalanne/cve-2023-49314
Proof-of-concept exploit for CVE-2023-49314 demonstrating code injection in Asana Desktop on macOS via Electron Fuses, with automated vulnerability…
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 cyberh3als/cve-2023-36845-poc
Automated PoC script for CVE-2023-36845, exploiting a PHP flaw in Juniper Junos OS J-Web to remotely modify PHPRC and achieve code injection on…
 ph-hitachi/cve-2025-58440
Remote Code Execution (RCE) via Polyglot File Attack and Null Byte Injection on Laravel FileManager
 jenkinsci-cert/security-3430
Java agent that transforms a vulnerable class to block exploitation of CVE-2024-43044 in Jenkins controllers, with optional forced shutdown on…
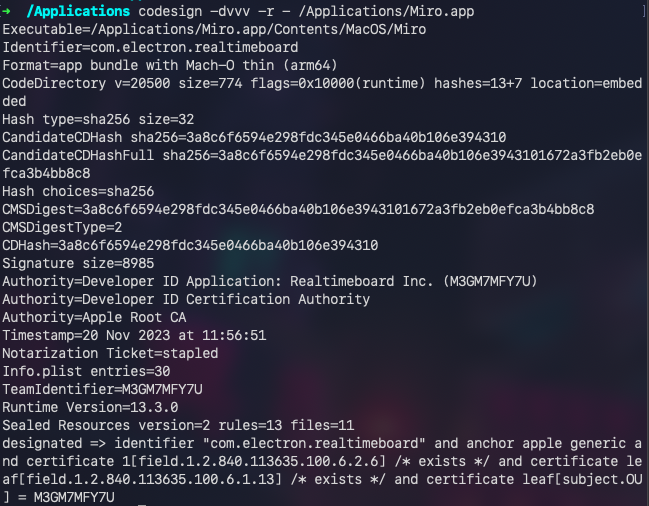 louiselalanne/cve-2024-23746
Miro Desktop 0.8.18 on macOS allows Electron code injection.
 x-defender/cve-2023-29007_win-version
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation on Windows systems for…
 kailing0220/cve-2019-5418
Ruby on Rails是一个 Web 应用程序框架,是一个相对较新的 Web 应用程序框架,构建在 Ruby 语言之上。这个漏洞主要是由于Ruby on Rails使用了指定参数的render…
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle
 danielhemmati/cve-2016-2098-my-first-exploit
This exploit is remote code execution vulnerability in Ruby-on-Rails when using render on user-supplied data
 grishinpv/cve-2026-31431-old-python
Provides a ctypes wrapper for the splice syscall to enable exploitation of CVE-2026-31431 on Python versions below 3.10, tested on Python 3.7.3.
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 apena-ba/cve-2024-39306
Proof-of-concept exploit for CVE-2024-39306, a SQL injection vulnerability in ChurchCRM <= 5.8.0 that allows authenticated remote code execution.…
 rajchowdhury240/cve-2025-67435
A critical Remote Code Execution (RCE) vulnerability has been identified in PluXML CMS version 5.8.22. This vulnerability allows authenticated…