

CVE-2022-24434_POC
 nayankadamm/cve-2022-24434_poc
Proof-of-concept exploit for CVE-2022-24434 targeting the Dicer npm package v0.3.1. Demonstrates server-side vulnerability exploitation with a…
code-analysiseducationexploitation+2
nayankadamm/cve-2022-24434_pocProof-of-concept exploit for CVE-2022-24434 targeting the Dicer npm package v0.3.1. Demonstrates server-side vulnerability exploitation with a…
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
 hopsypopsy8/cve-2024-53677-exploitation
Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…
 heimd411/cve-2025-24813-nopoc
Research repository documenting failed exploitation attempts for CVE-2025-24813, a deserialization vulnerability in Apache Tomcat, with tested…
 rxerium/cve-2025-42944
Detection for CVE-2025-42944
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.
 mbadanoiu/cve-2021-46362
CVE-2021-46362: FreeMarker Server-Side Template Injection in Magnolia CMS
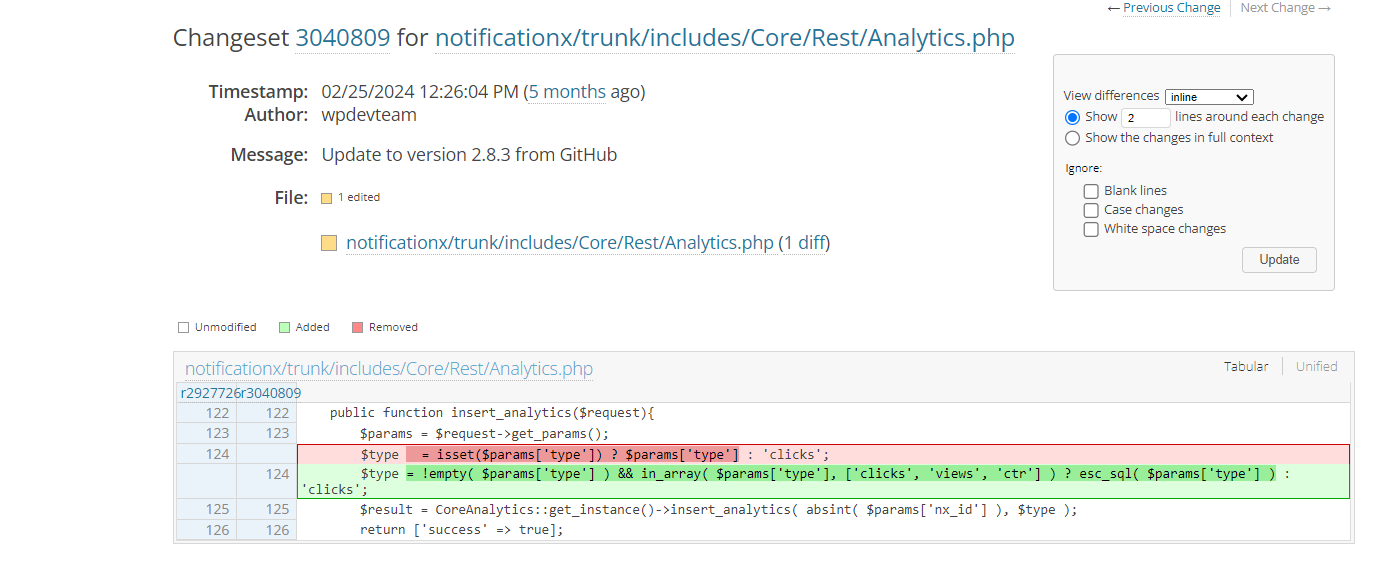 raytran54/cve-2019-1698
Step-by-step technical analysis of CVE-2019-1698, a WordPress plugin SQL injection vulnerability, with code diff review, vulnerable function…