openssl-1.1.1g_CVE-2021-23840

OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…

OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…

Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…

OpenSSL 1.1.0g cryptographic library and TLS toolkit, providing encryption, decryption, certificate management, and SSL/TLS protocol support for…

Anticipator is an open-source threat detection platform for multi-agent AI systems.

CVE-2022-22947 exploit script

glibc getaddrinfo stack-based buffer overflow

Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability in OpenSSH server, demonstrating exploitation techniques for…

Proof-of-concept exploit for CVE-2024-0195, a critical code injection vulnerability in SpiderFlow 0.4.3 enabling remote code execution via the…

JSON sanitizer that converts malformed JSON-like content into valid, safe JSON, preventing code injection and ensuring standards compliance for web…


Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…

Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…

Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.

[Moved to Codeberg] Simple local scanner for vulnerable log4j instances

Tool to search secrets in various filetypes.

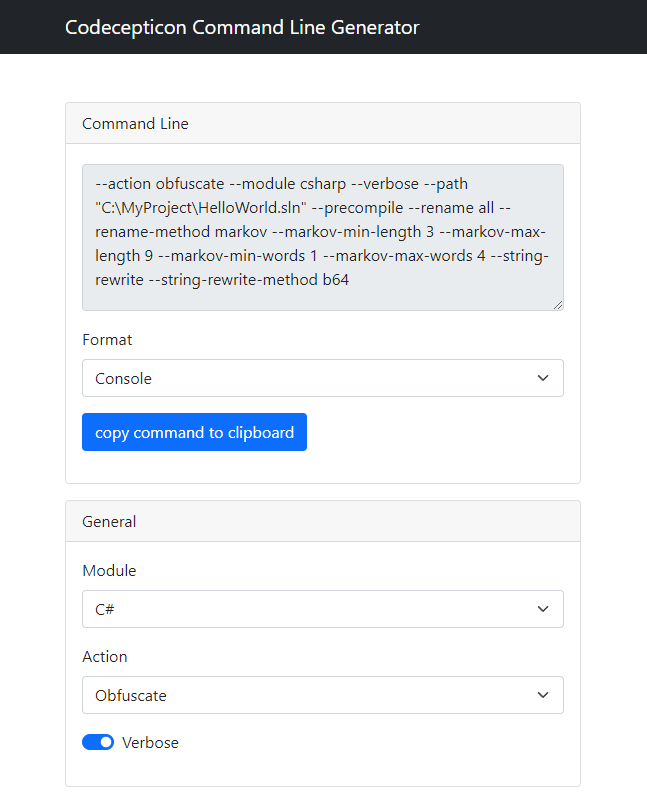
.NET/PowerShell/VBA Offensive Security Obfuscator

Go scripts for finding sensitive data like API key / some keywords in the github repository