
wrongsecrets-binaries
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
binary-analysiscode-analysisctf+6
12
owasp/wrongsecrets-binariesSource code for the Binaries of OWASP WrongSecrets
 nccgroup/firstexecution
Collection of different ways to execute code outside of the expected entry points
 alfarom256/cve-2022-45451
PoC for Acronis Arbitrary File Read - CVE-2022-45451
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
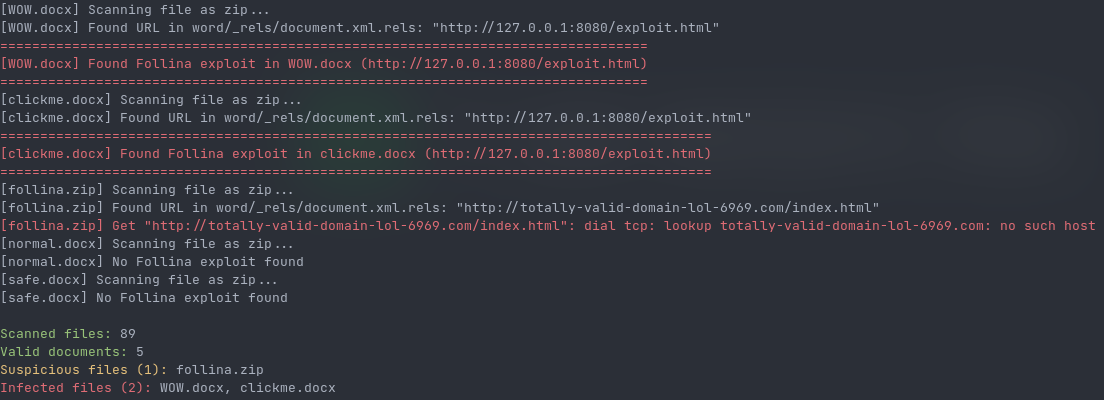 errornointernet/follinascanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
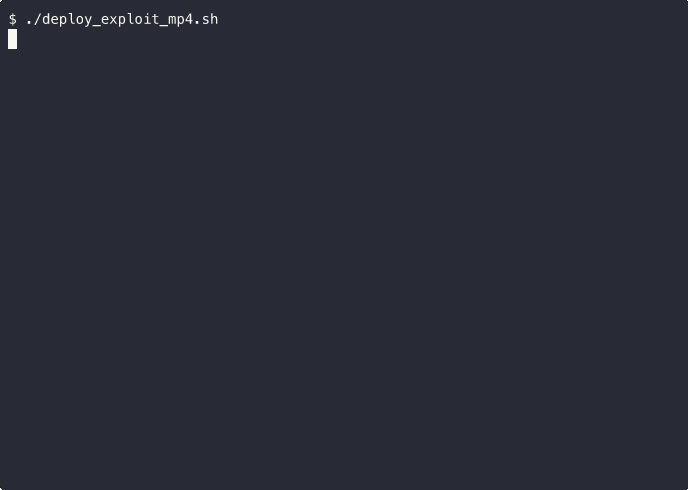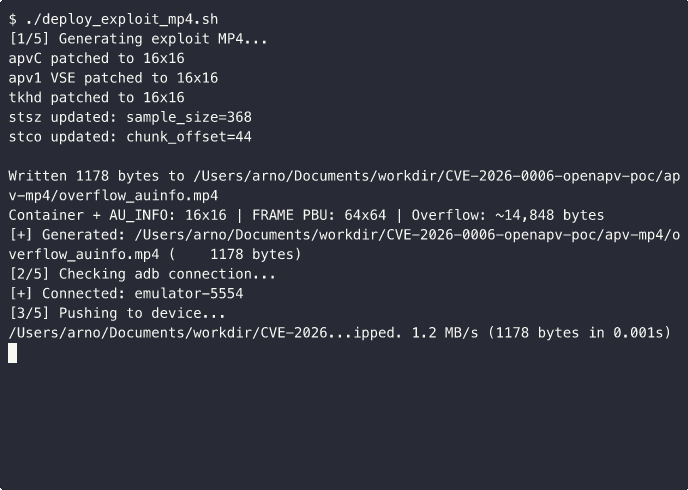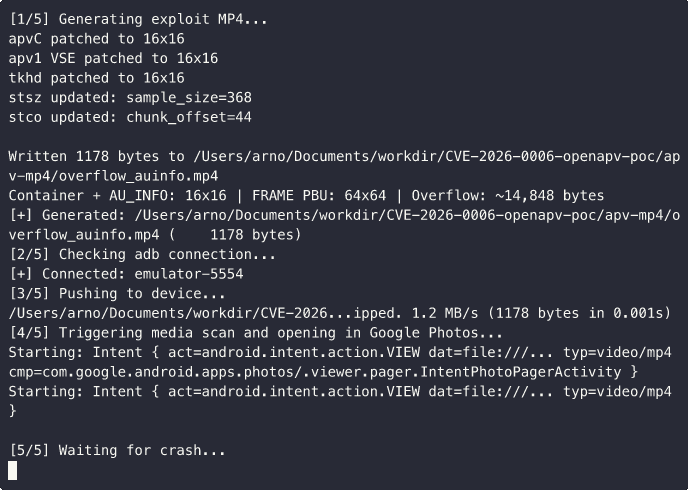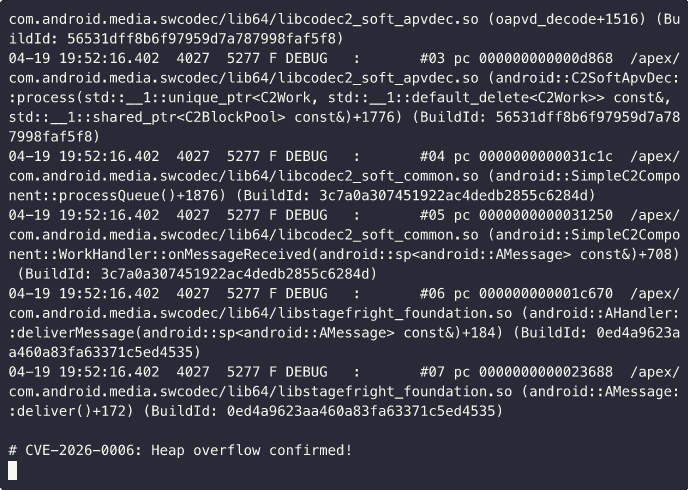 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 hackinglz/cve-2025-27237
CVE 2025 27237 Zabbix LPE proof of concept.
 koblers/np-audit
Static security analysis for npm packages. Detects obfuscated code, malicious patterns, and known vulnerabilities before installation.
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
 vulnmachines/imagemagick-cve-2022-44268
Imagemagick CVE-2022-44268
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 actions-security-demo/compromised-packages
StepSecurity owned org for analyzing compromised packages
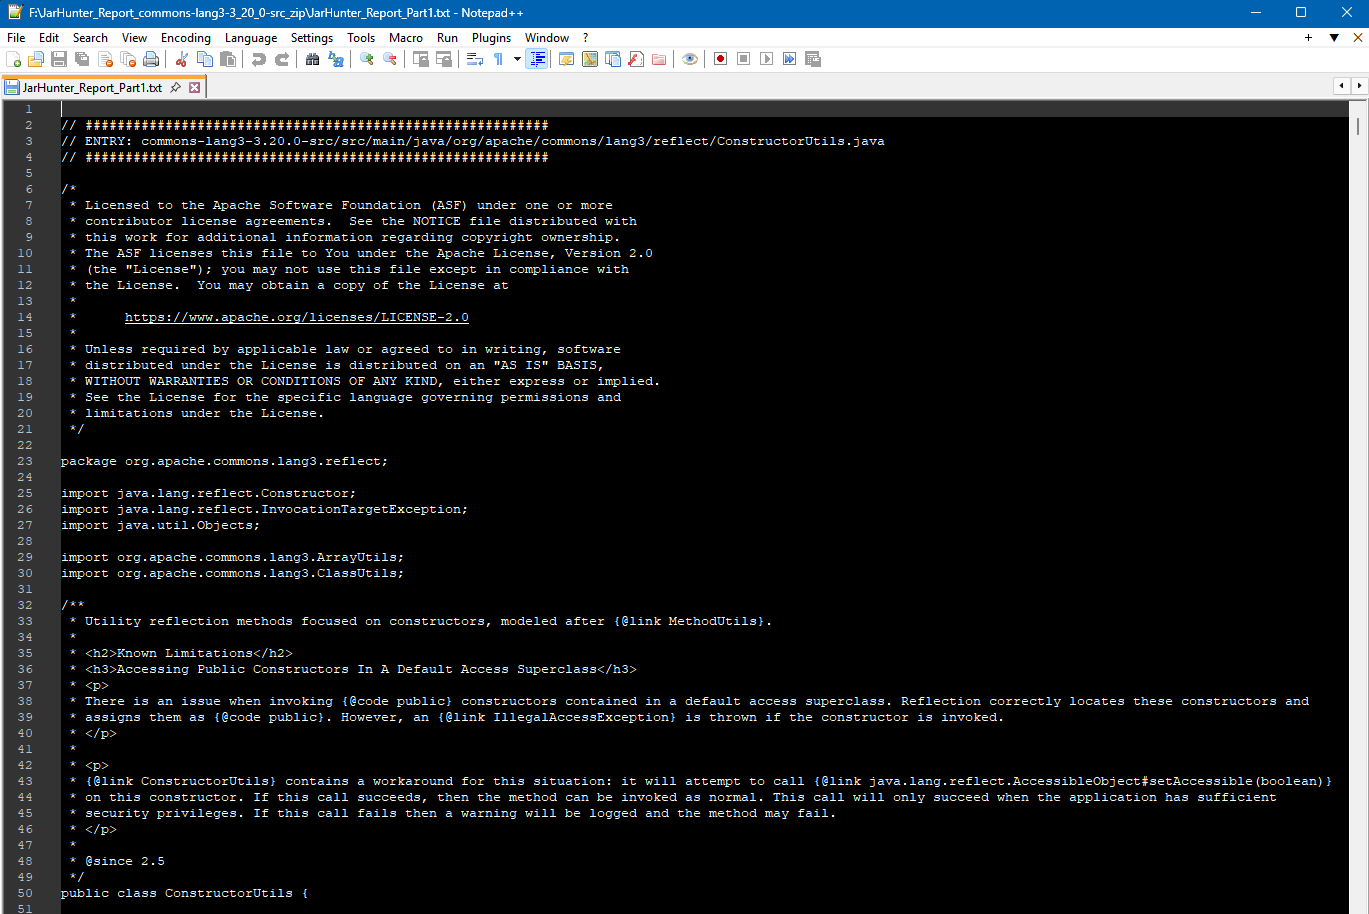 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…