

 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
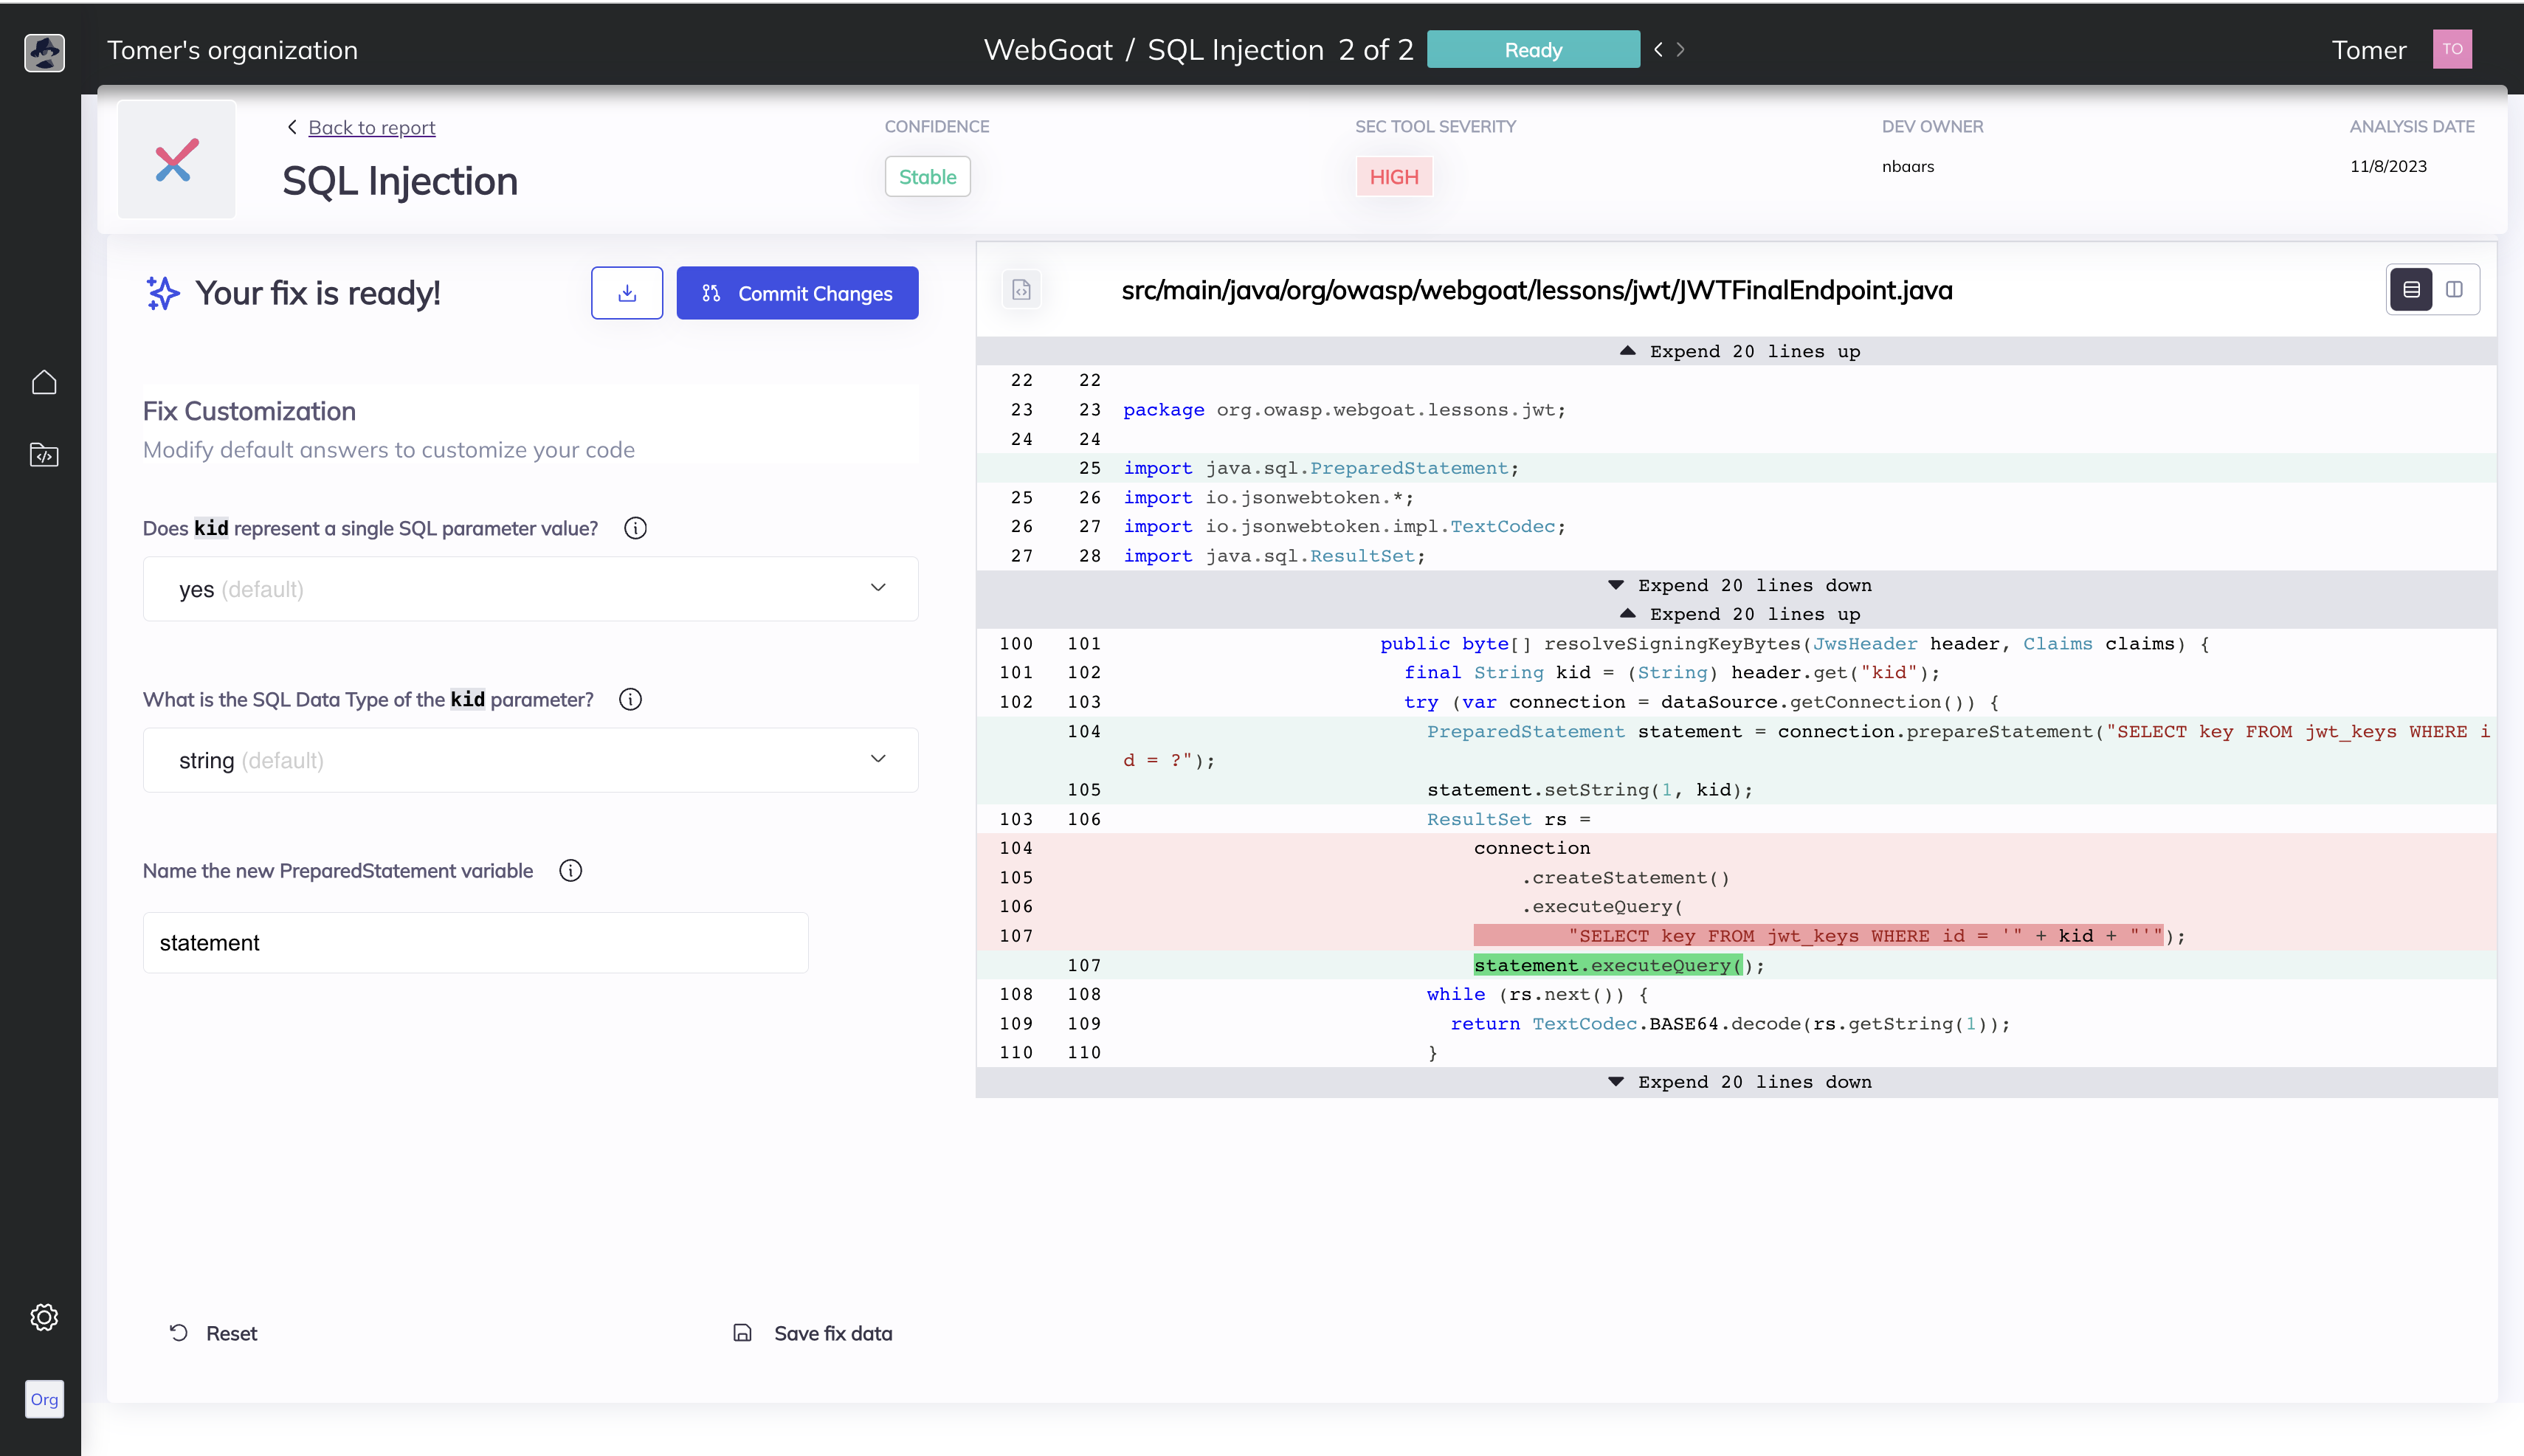 mobb-dev/bugsy
Automatic security vulnerability remediation for your code.
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart
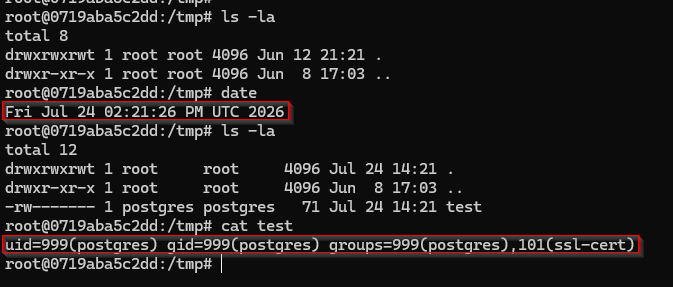 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 ghostinexile/cve-2026-63030-wp2shell
WordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)
 nicpwns/cve-2026-62183
Apache Syncope: User self-service privilege escalation
 ch4120n/cve-2026-58138
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 biitts/cve-2026-56121-feast-unauth-rce
CVE-2026-56121 — Feast <0.63.0 unauthenticated RCE via gRPC registry dill.loads of OnDemandFeatureView UDF (pre-auth). Lab + PoC, verified e2e.
 reactivezero/cve-2026-20251
CVE-2026-20251 — Splunk Secure Gateway jsonpickle deserialization RCE (CVSS 8.8) | ReactiveZero Security Research
 0xmrma/cve-2026-42089
A local package installation helper trusted caller-supplied package names too much. In yeoman-environment, missing generators could be installed…
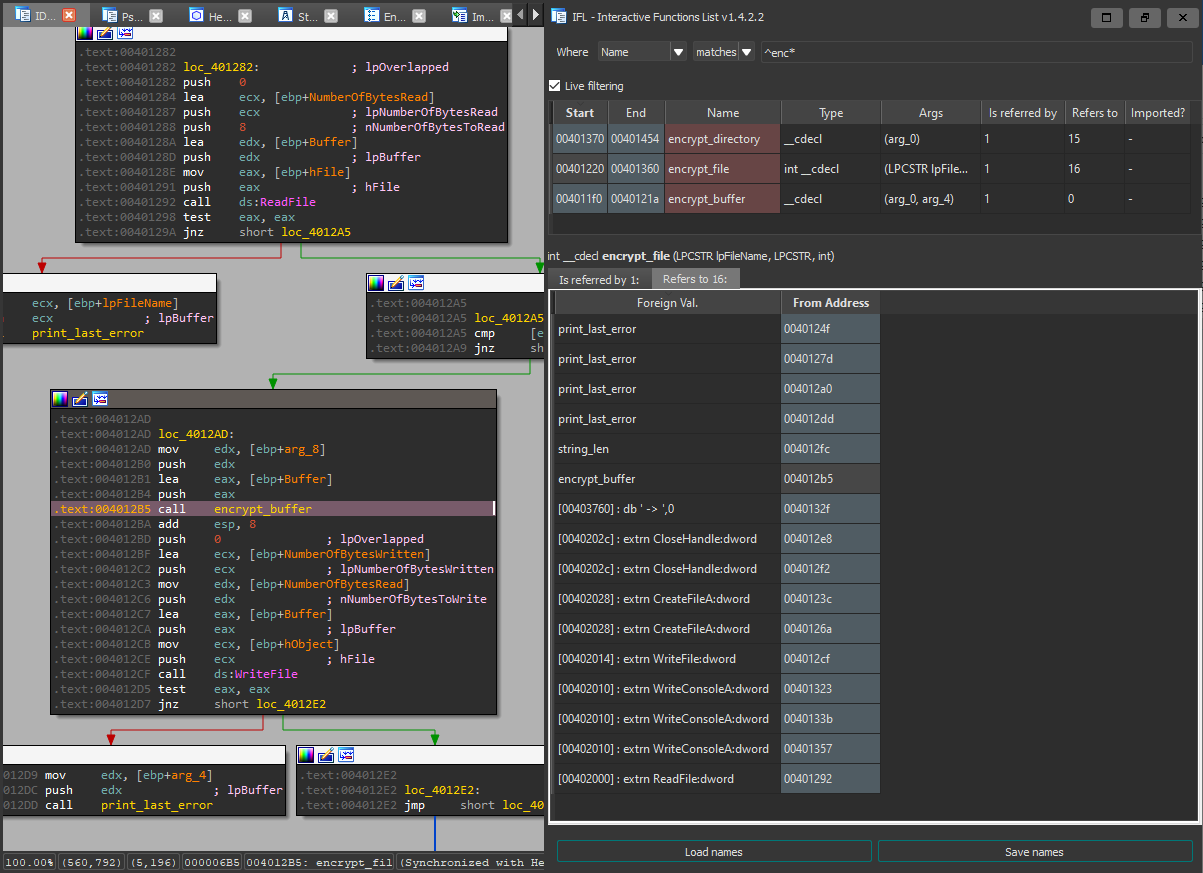 hasherezade/ida_ifl
IFL - Interactive Functions List (plugin for IDA Pro)
 learner202649/cve-2026-47102-poc
The code for personally reproducing the corresponding vulnerability
 dannyendortest/gin-vulnerable
Demo consumer for gin v1.7.0 (CVE-2023-29401) — Context.FileAttachment with user input. endorctl scan target.
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
 y0un9eee/cve-2024-27766
Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…