
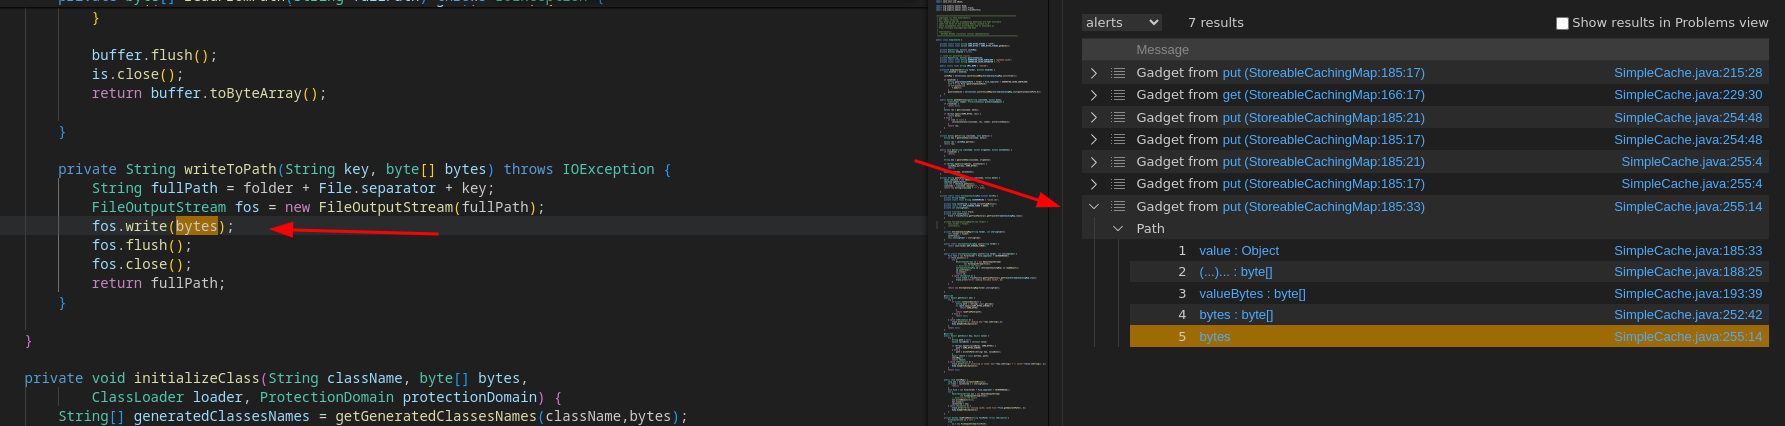
QLinspector
 synacktiv/qlinspector
Finding Java/C# gadget chains with CodeQL
code-analysisexploitationpayload-development+2
synacktiv/qlinspectorFinding Java/C# gadget chains with CodeQL
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
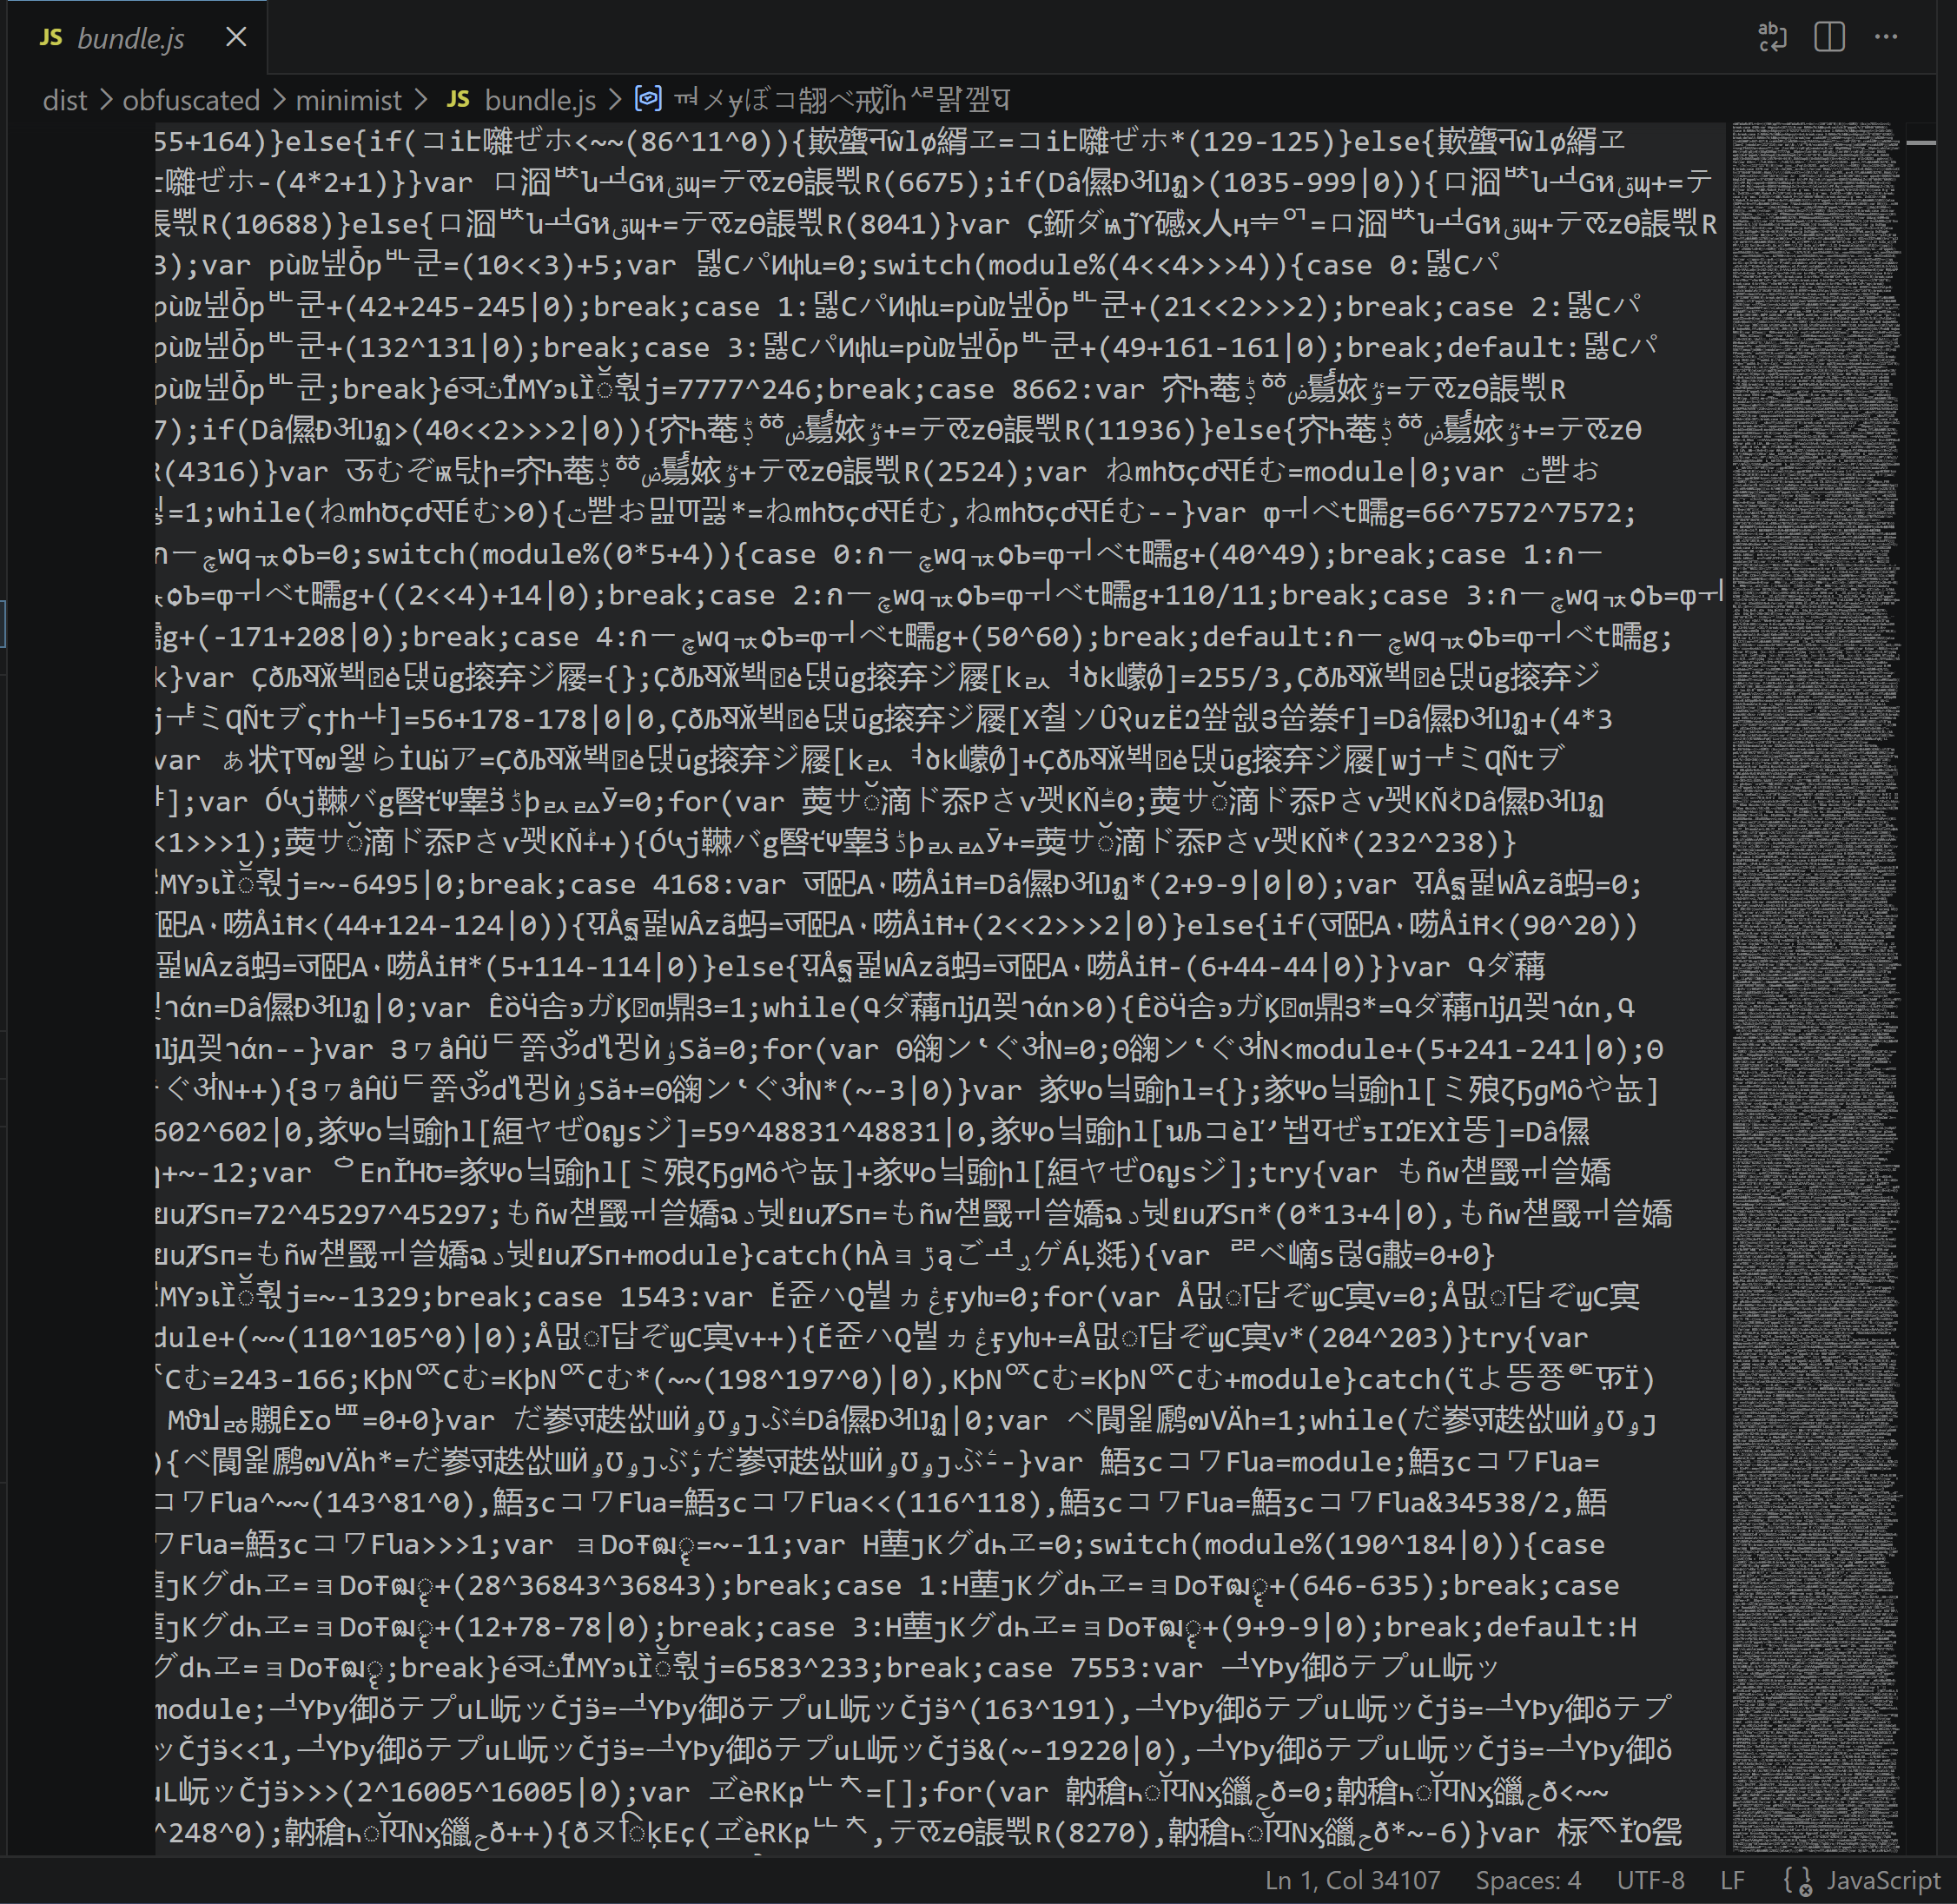 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
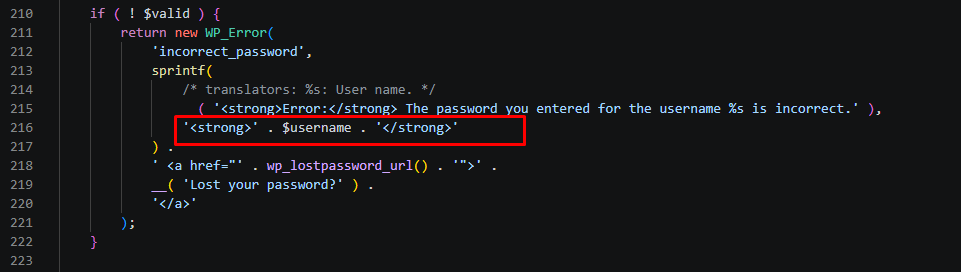 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
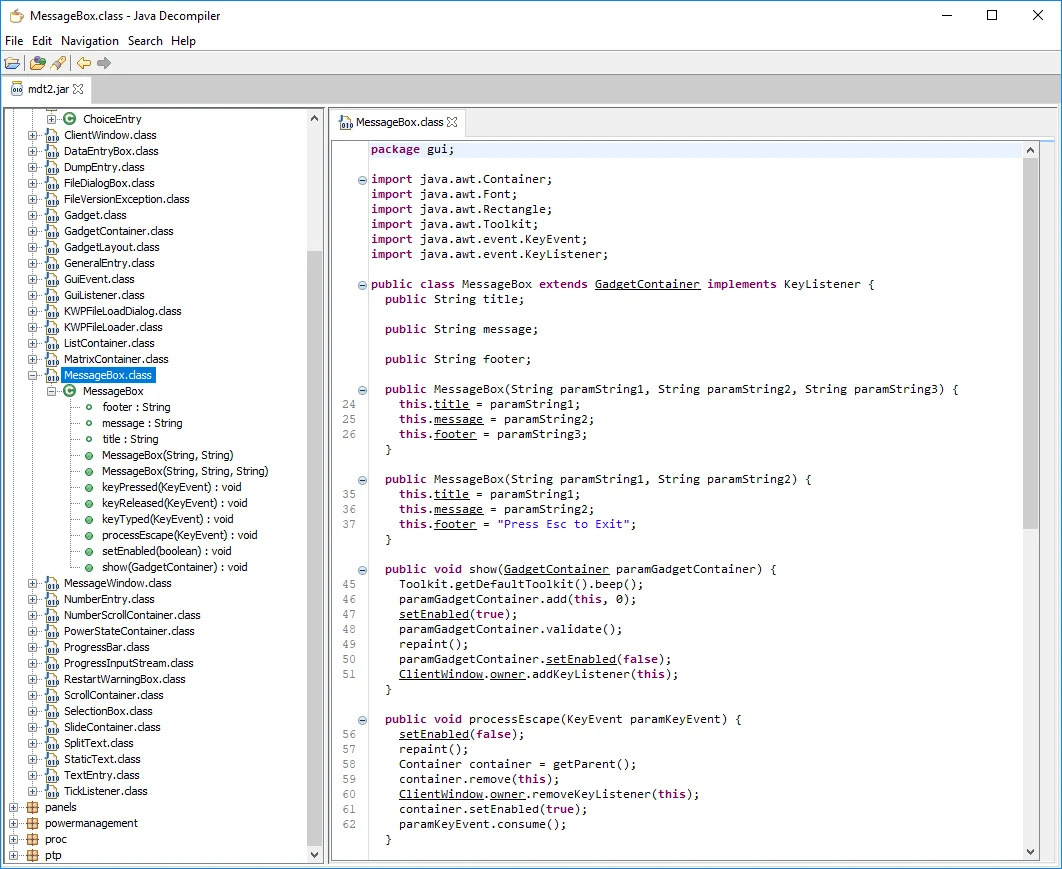 pelock/jobfuscator
Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 oscerd/cve-2026-33454
Reproducer for CVE-2026-33454: Apache Camel camel-mail header injection to RCE via camel-exec
 alexb616/sessionreaper-cve-2025-54236
PoC Magento Session Reaper - CVE-2025-54236
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
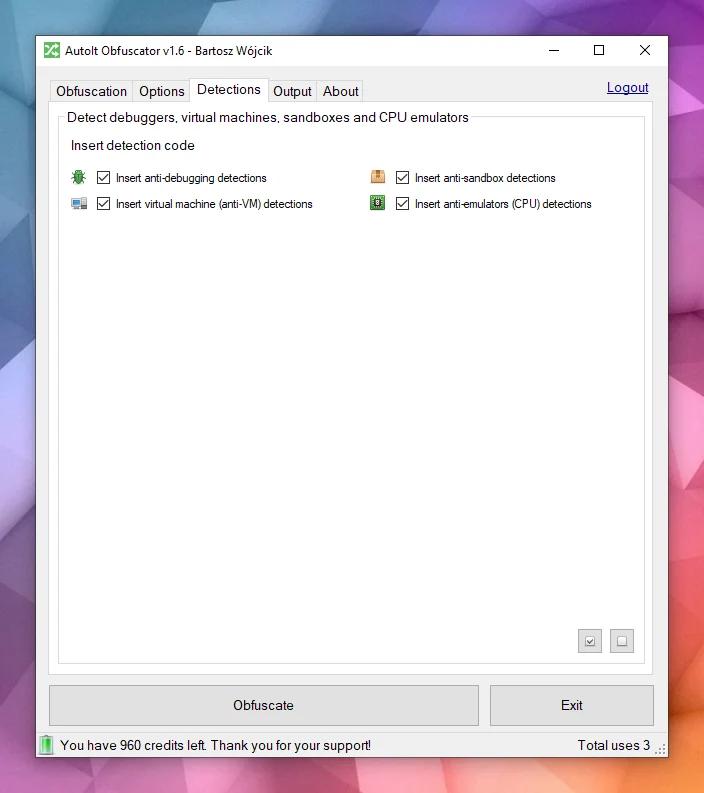 pelock/autoit-obfuscator
Obfuscates AutoIt scripts to protect source code from analysis, reverse engineering, and decompilation using advanced obfuscation and polymorphic…
 lirantal/safer-eval-cve-cve-2019-10760
Publicly disclosed Proof-of-Concept (POC) exploit for the [email protected] version
 adamshaikhma/cve-2026-3300
Exploit for CVE-2026-3300, an unauthenticated stored XSS leading to RCE in Everest Forms Pro WordPress plugin, with a Python script to generate a…
 habuon/cve-2026-48208
This is POC repo for CVE-2026-48208