
heartwood
 radicle-dev/heartwood
Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
authentication-authorizationcode-analysisnetwork-security+2
267
radicle-dev/heartwoodPeer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
 toanln-cov/cve-2026-66917
IDOR + Stored XSS via Broken Object-Level Authorization in JoomGallery
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 theopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized Room Deletion (Let's Chat)
 darrocarocatest-sys/pv2-victim
authz research - CVE-2026-3306 fix coverage
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
 bekwiner/cve-2026-47777
Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 estebanzarate/cve-2023-27372-spip-4.2.1-unauthenticated-rce-poc
Proof-of-concept exploit for unauthenticated remote code execution in SPIP < 4.2.1 via PHP object injection in the password reset form. Provides…
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.
 trinadh465/openssl-1_0_1g_cve-2015-1791
OpenSSL 1.0.1g source code with CVE-2015-1791 patch, providing SSL/TLS and cryptographic library for secure communications.
 pazhanivel07/openssl_1_0_1g_cve-2015-1788
General-purpose cryptography library implementing SSL/TLS protocols, symmetric/ asymmetric ciphers, message digests, and X.509 certificate handling…

 grails/gssc-cve-2022-41923
Workaround guide for CVE-2022-41923 privilege management vulnerability in Grails Spring Security Core plugin, providing patched filter definitions…
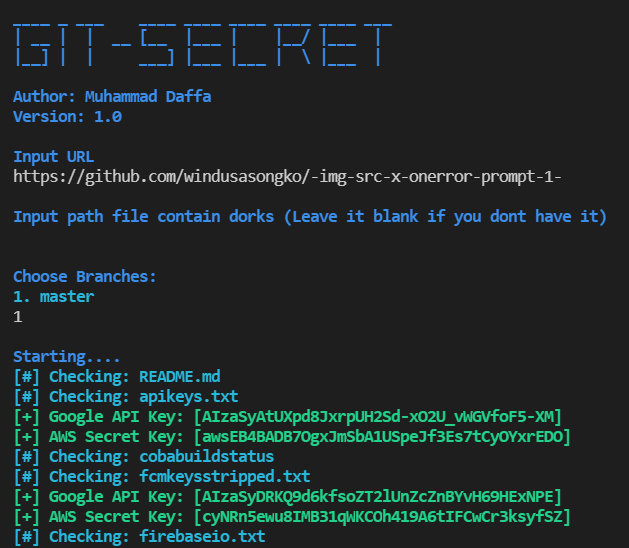 daffainfo/git-secret
Go scripts for finding sensitive data like API key / some keywords in the github repository
 uzju/gin-vue-admin-poc-cve-2022-21660
CVE-2022-21660