

gortex-PoC
 squeeze440/gortex-poc
PoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).
code-analysisexploitationinformation-gathering+4
squeeze440/gortex-pocPoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).
 soxoj/gitcolombo
🧬 Extract and analyze contributors info from git repos
 0xmrma/cve-2026-5061
Consul Template validated where a symlink pointed during template evaluation, but its later dependency fetch read the original path. Retargeting the…
 oscerd/cve-2026-49097
PoC reproducer for CVE-2026-49097 (Apache Camel camel-irc): the non-Camel-prefixed irc.sendTo header escapes the HTTP header filter and overrides the…
 zephrfish/wp2shell-scanner
CVE-2026-63030, CVE-2026-60137, wp2shell scanner
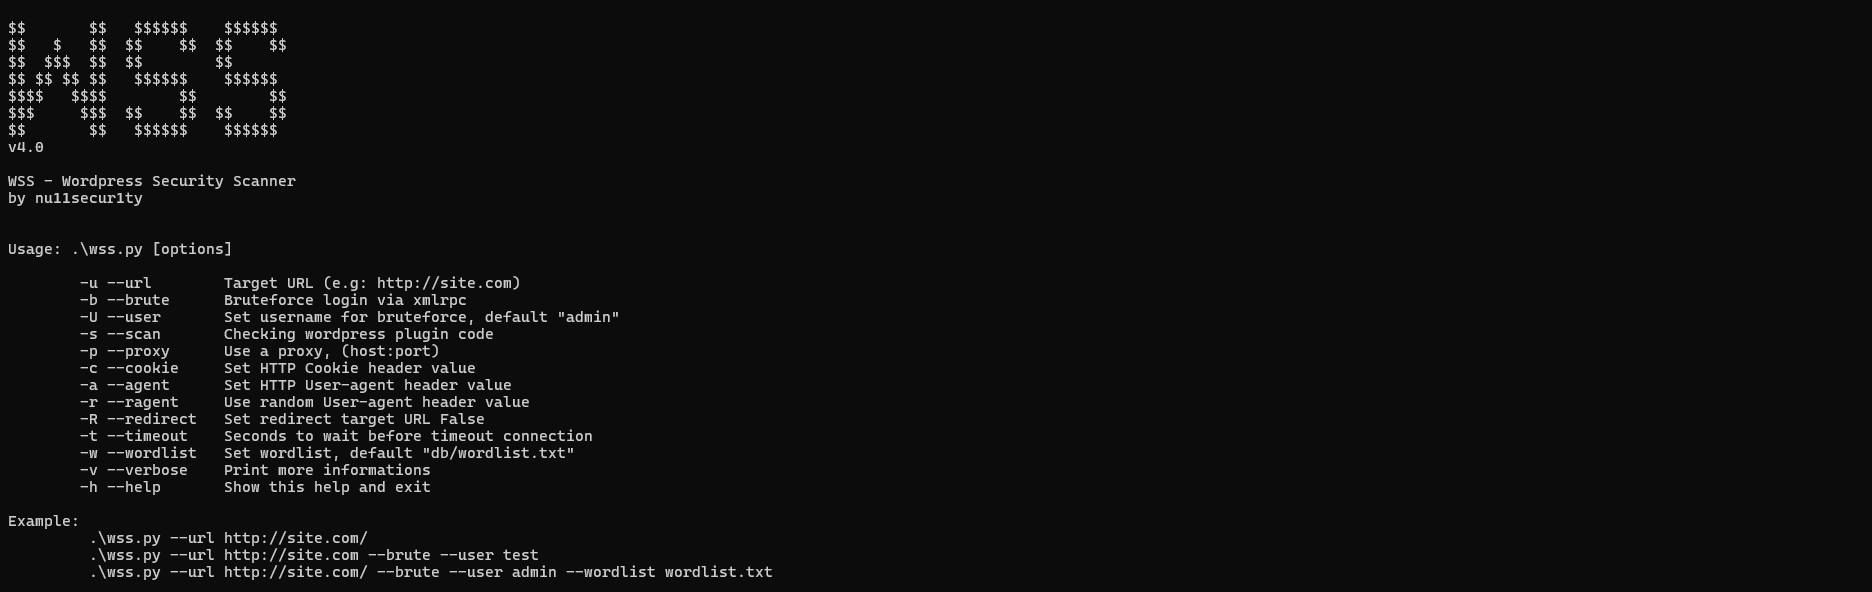 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 kx00007/cve-2026-39938
Detailed CVE-2026-39938 vulnerability report for Cacti ≤1.2.30, demonstrating unauthenticated LFI chained to OS command injection RCE with PoC, root…
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
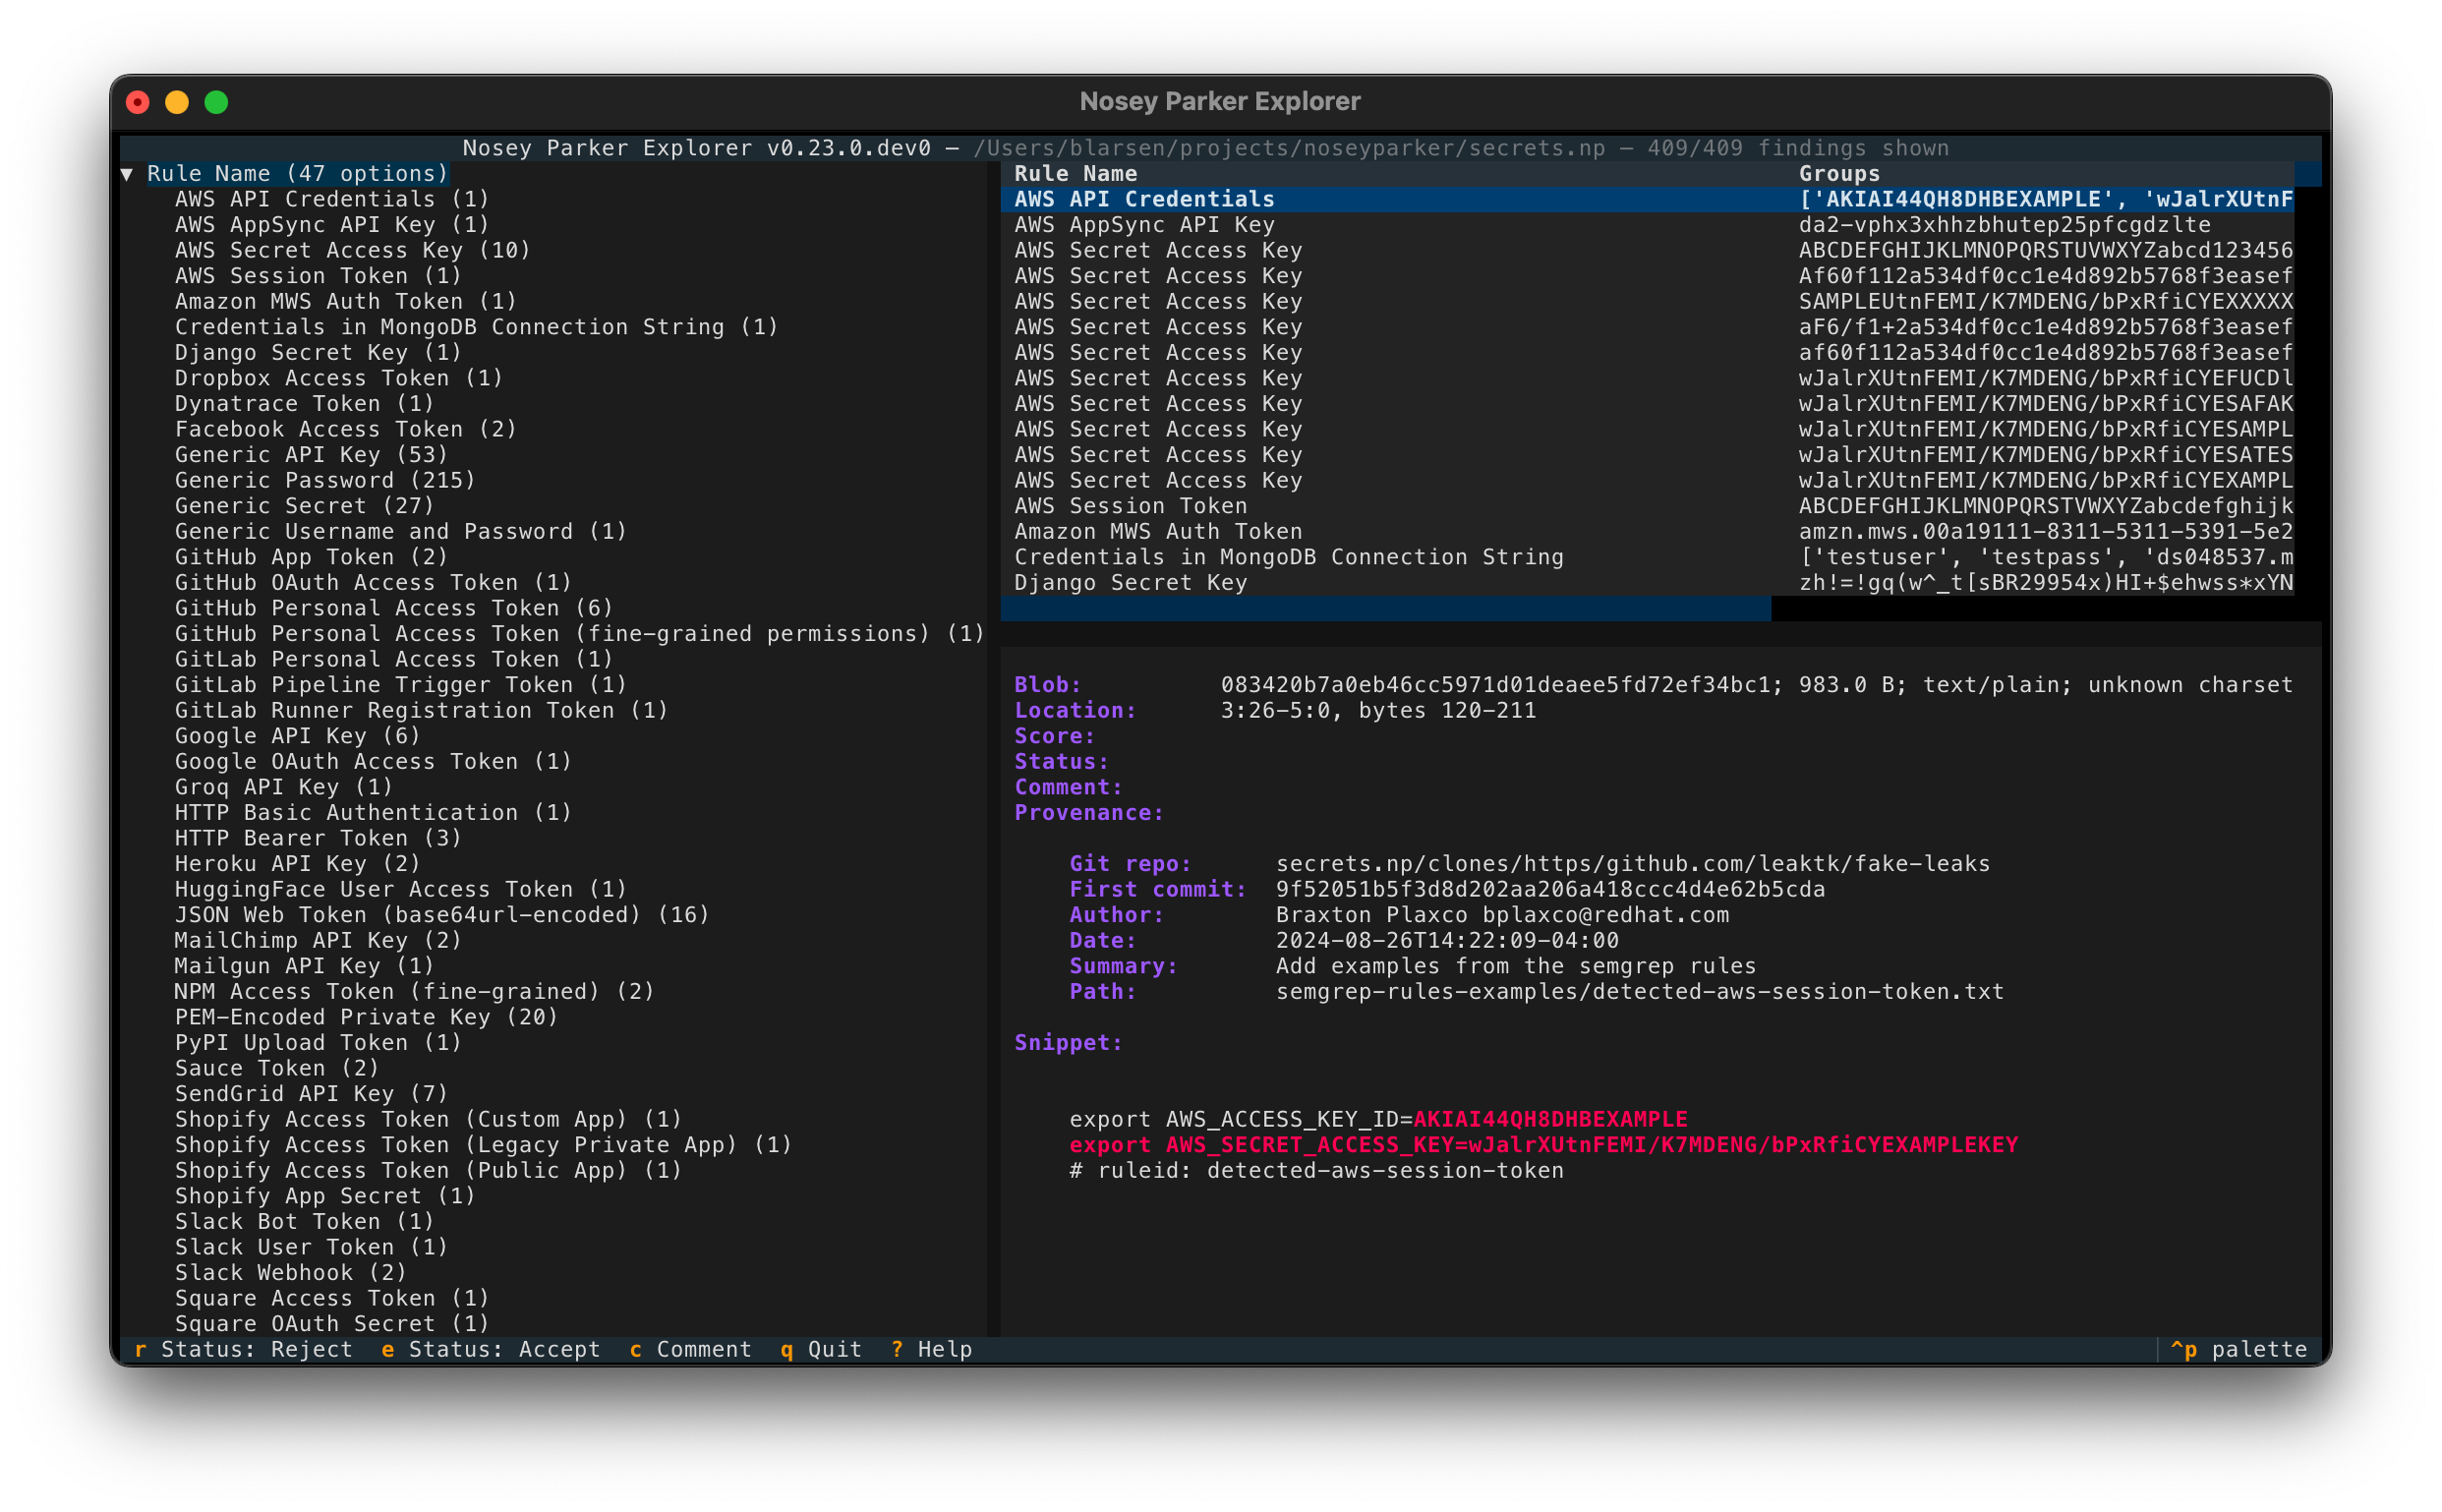 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 nurjaman2004/jspdf-bulk-detector-cve-2025-68428-
Asset-wide detection tool for identifying jsPDF usage related to CVE-2025-68428 Detection only — no exploitation
 mooseloveti/hippoo-mobile-app-for-woocommerce-cve-report
Disclosure for CVE-2025-13339
 bankkroll/quickcheck-cve-2025-55182-react-and-cve-2025-66478-next.js
Script to quick check CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Critical unauthenticated RCE vulnerabilities in the React Server…
 tillson/git-hound
Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.
 unkl4b/gitminer3
Tool for advanced mining for content on Github
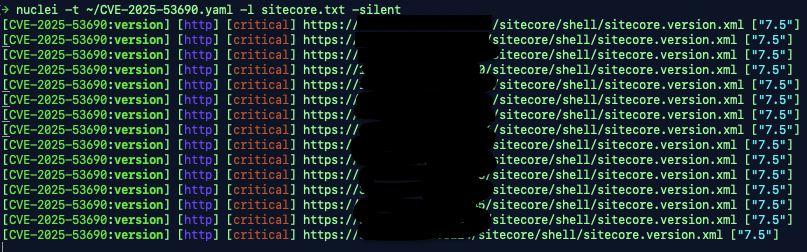 rxerium/cve-2025-53690
Detection for CVE-2025-53690
 joaosilva21/cve-2024-43018
Proof-of-concept for CVE-2024-43018: SQL injection in Piwigo 13.8.0 via unsanitized max_level and min_register parameters, enabling information…