

opengrep
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
code-analysisdefensive-toolsdevsecops+7
opengrep/opengrep🔎 Static code analysis engine to find security issues in code.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
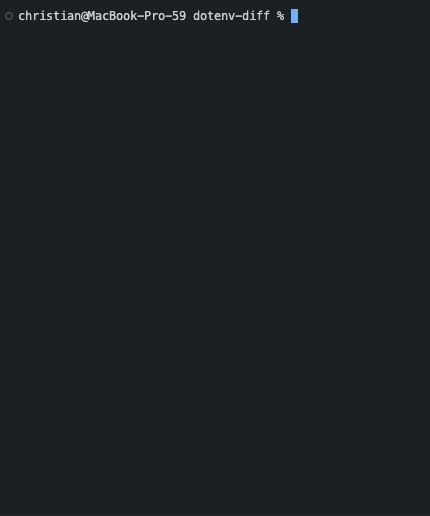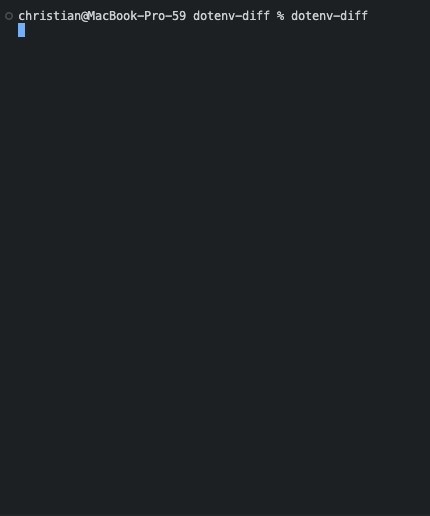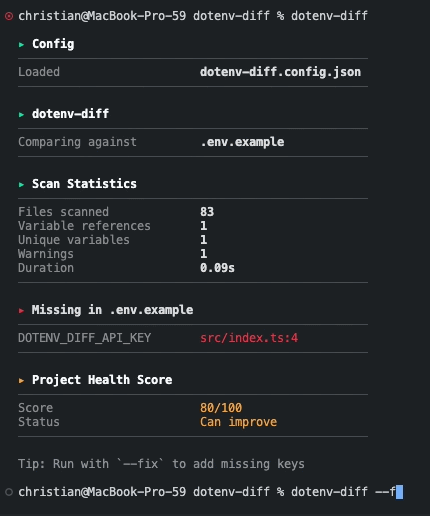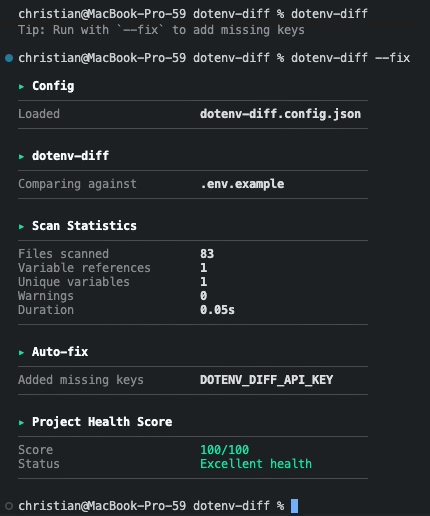 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
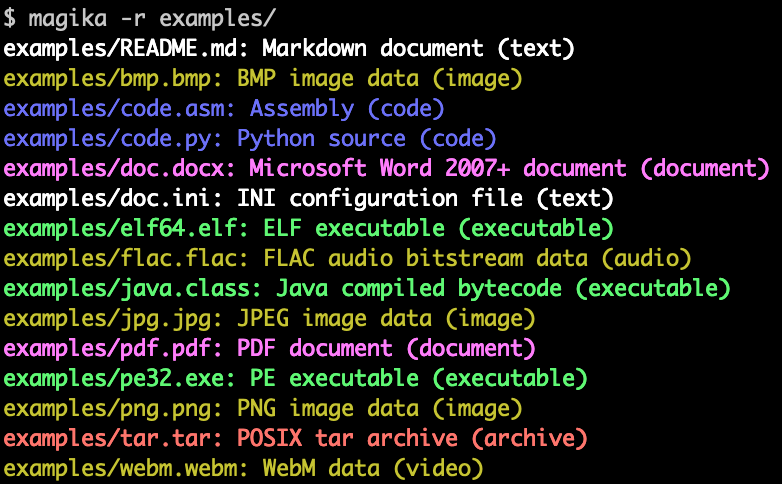 google/magika
Fast and accurate AI powered file content types detection
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 safedep/vet
Protect against malicious open source packages 🤖
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…

 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI