

mariana-trench
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
android-securitycode-analysismobile-security+2
1.3k
facebook/mariana-trenchA security focused static analysis tool for Android and Java applications.
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
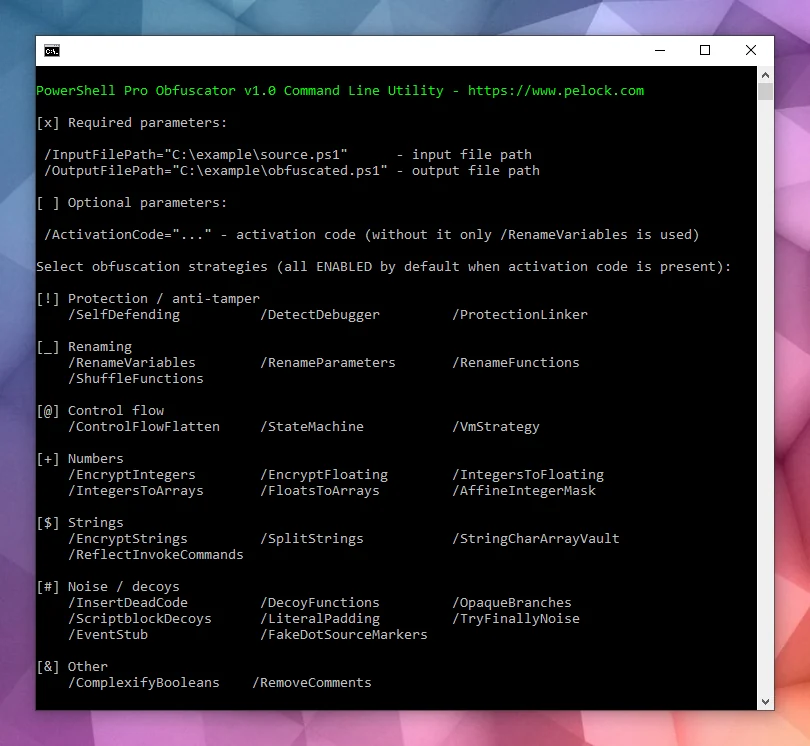 pelock/powershell-pro-obfuscator-python
Automate PowerShell script source code obfuscation & virtualization with a flexible Web API for Python (pip package).
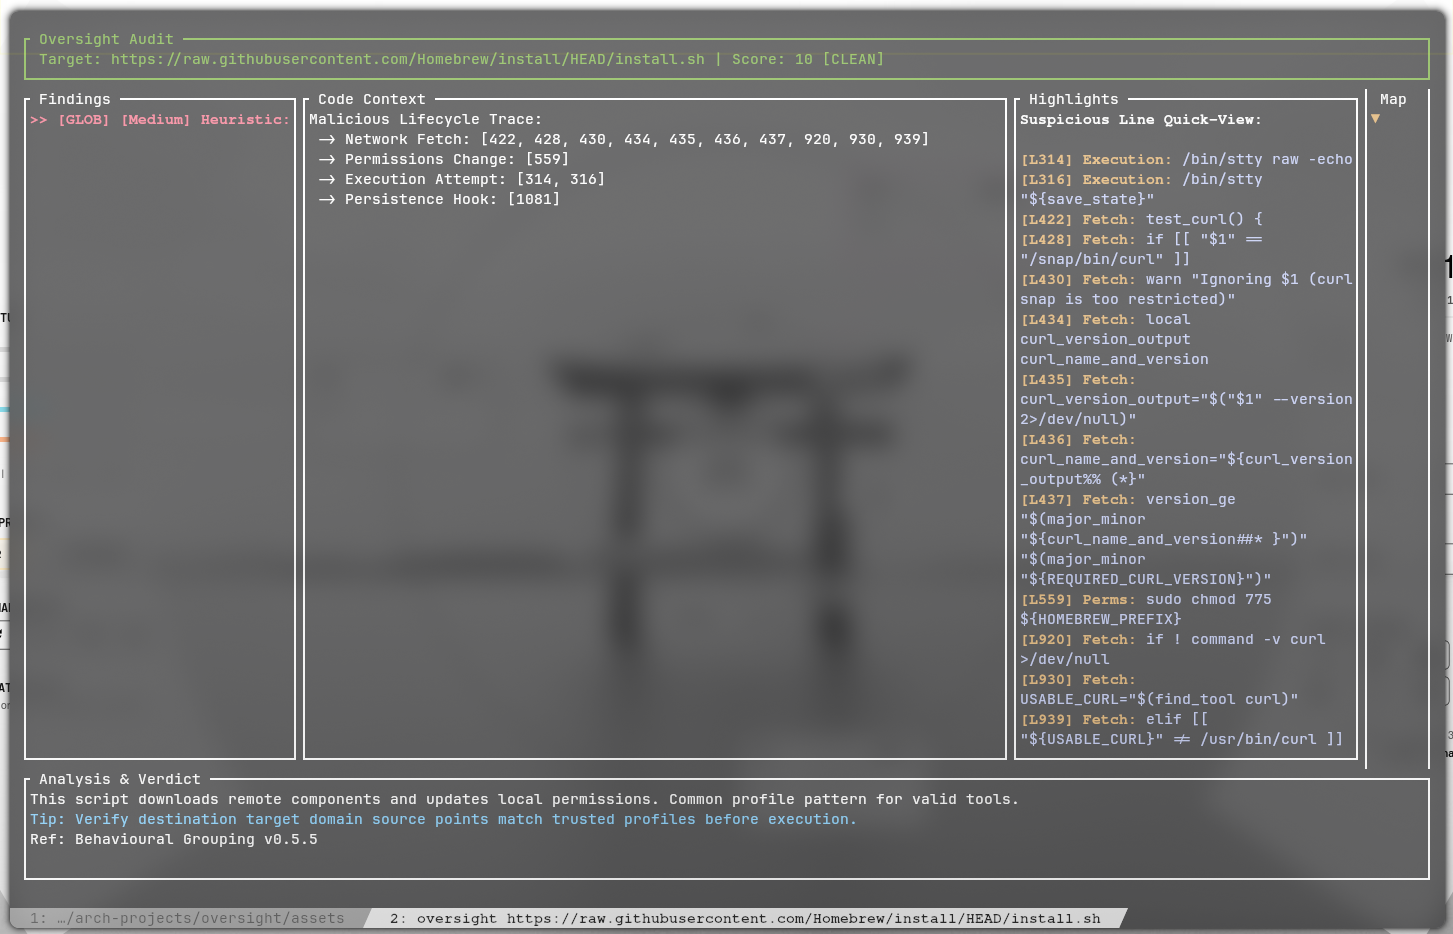 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 error-inside/cve-2026-47670
Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
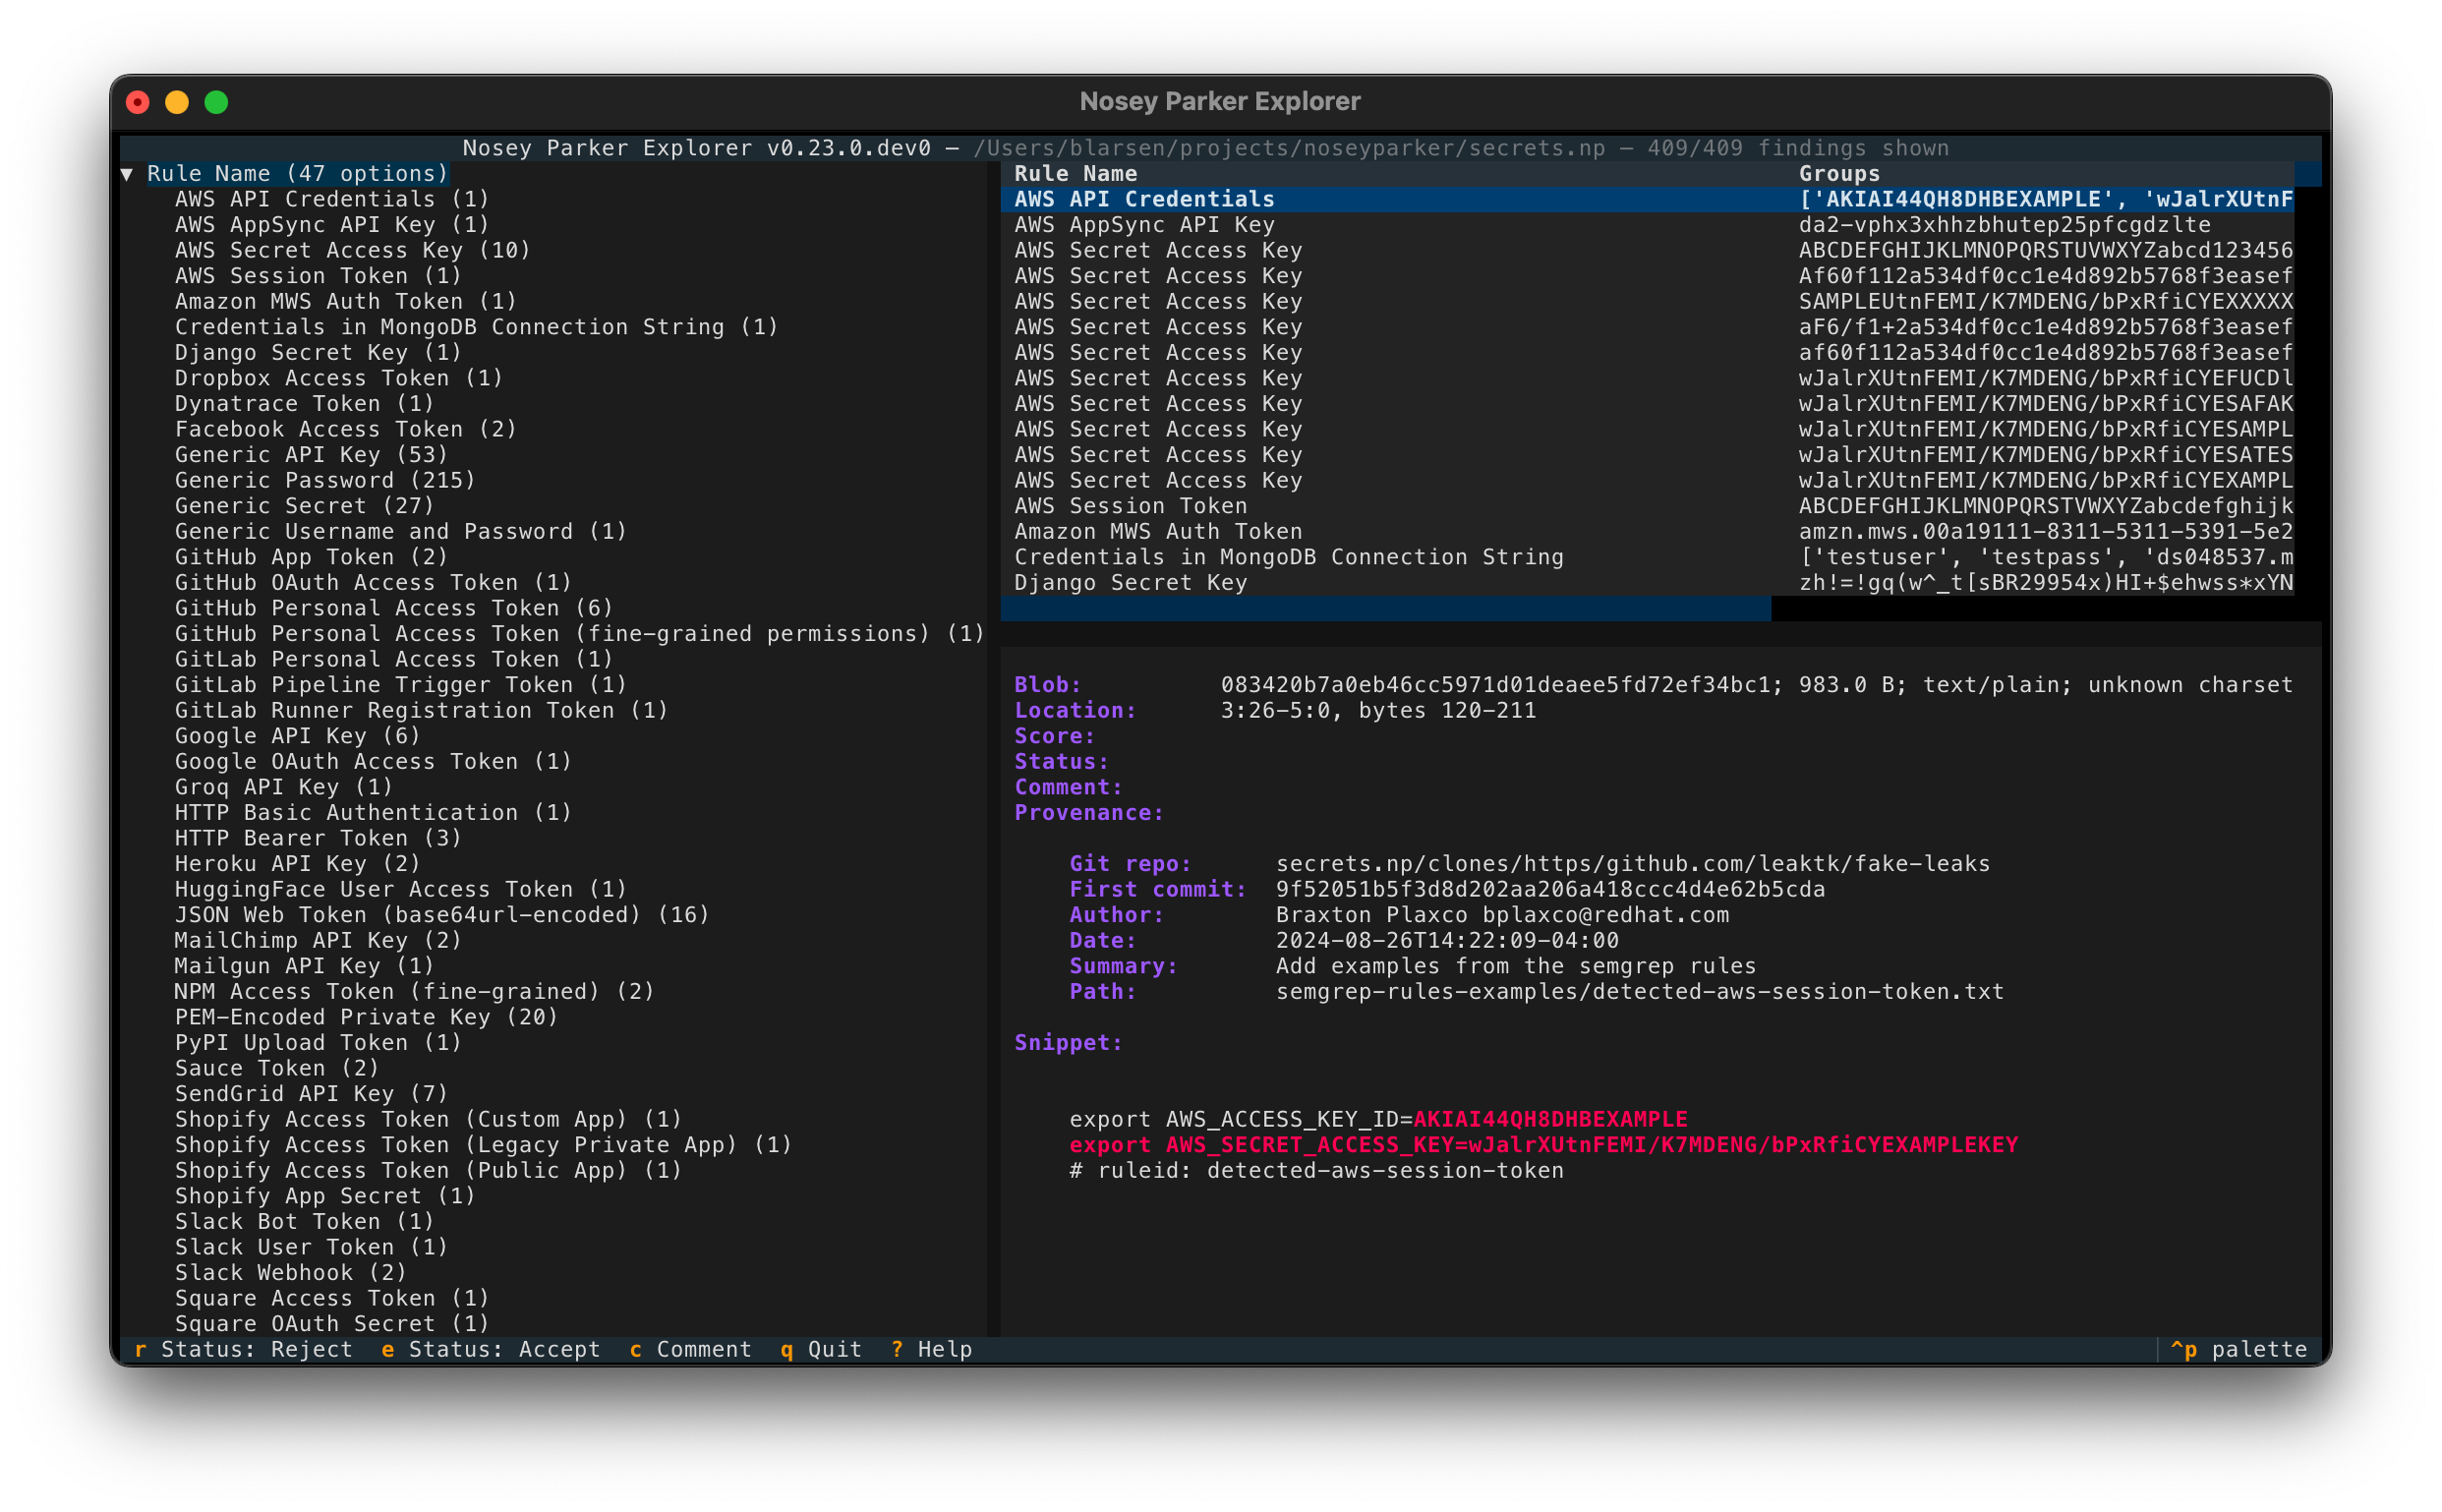 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
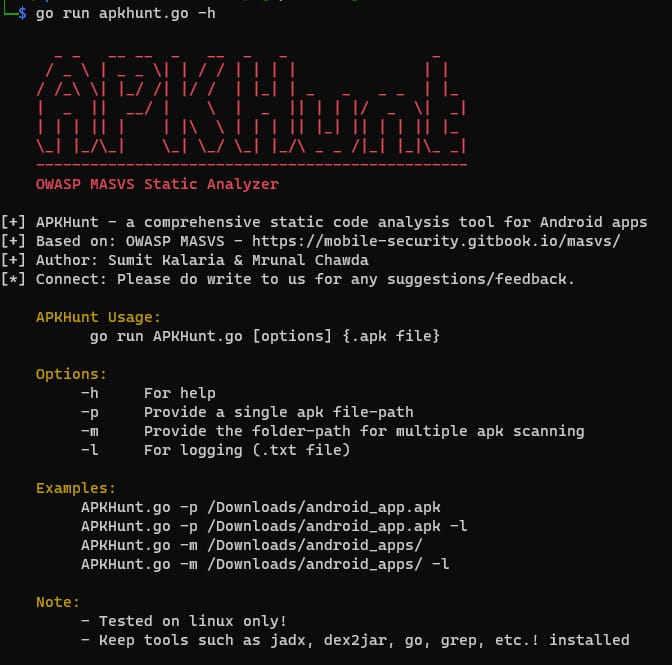 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)