
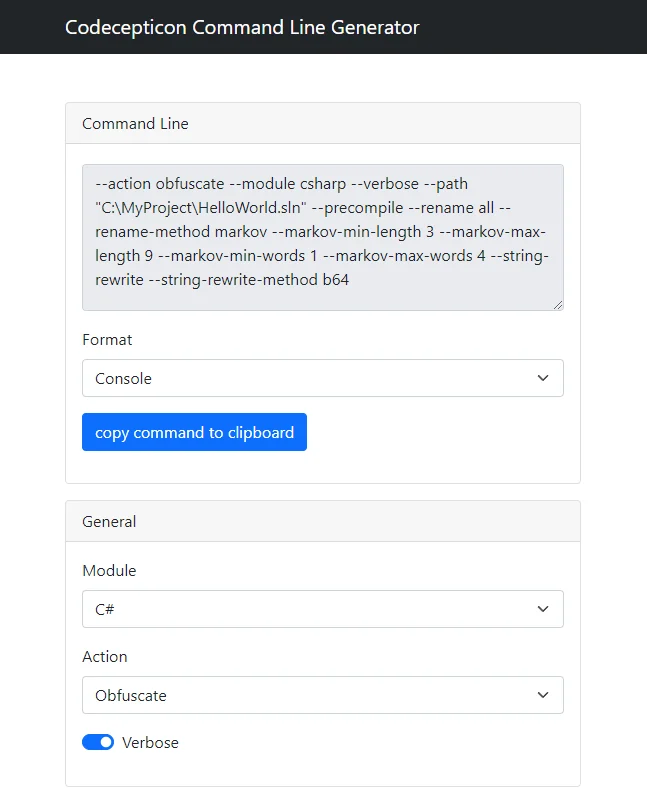
Codecepticon
 sadreck/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
code-analysisdefensive-toolsids-ips-evasion+5
sadreck/codecepticon.NET/PowerShell/VBA Offensive Security Obfuscator
 borewit/svg-sanitizer
Java library that sanitizes SVG files by stripping JavaScript, inline event handlers, and script tags while blocking external resource loading to…
 bgalek/safe-svg
Simple and lightweight library that helps to validate SVG files in security manners.
 piecar21/cve-2026-0303
Proof-of-concept and Docker lab for CVE-2026-0303, demonstrating arbitrary code execution in Checkov via an auto-loaded .checkov.yml pointing to an…
 ntoskernel/deepsecrets
Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.

 divyanshukumar0014/shipproof
Automated SOC 2 change management for GitLab CI.
 ejfkdev/pycdc
Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
 odomojuli/regextokens
list of regex patterns for oauth / api tokens with provided source
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 edoardottt/openhands-disclosure
Multiple Command Injection vulnerabilities in openhands <0.62.0 allow an attacker to run arbitrary system commands.
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 neurosaki987/tvm-recover
Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 happytotoro116/ghidra-llm-pipeline
Deterministic PyGhidra extraction, triage, and local LLM compiler-backend pipeline for C reimplementation.