

Xpsd
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
ai-securitycode-analysisdevsecops+6
13 days ago
owasp/xpsdReachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 edoardottt/openhands-disclosure
Multiple Command Injection vulnerabilities in openhands <0.62.0 allow an attacker to run arbitrary system commands.
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
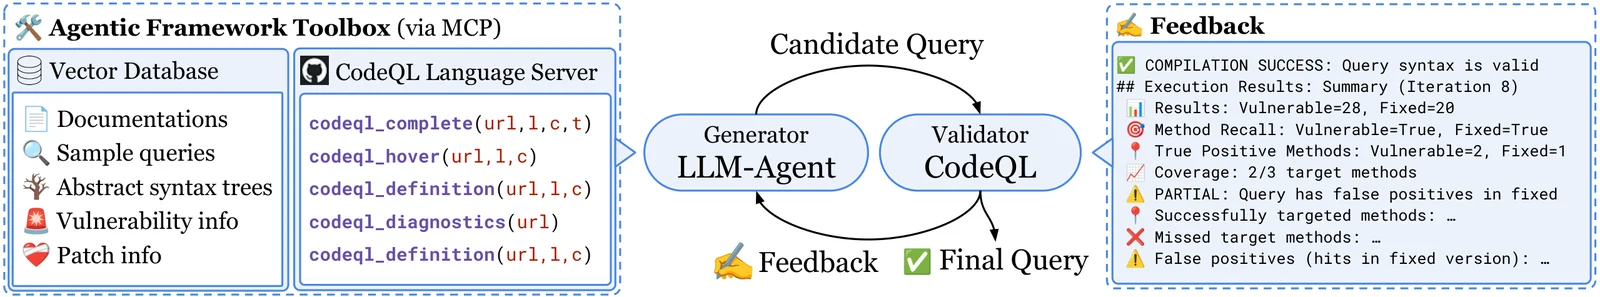 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 sivaadityacoder/cve-2026-22038
Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 ashizzz/cve-2026-22610
Scans Angular projects for XSS vulnerabilities in SVG elements and unsafe bindings, generating a vulnerability report with line numbers and…
 renio-wow/cve-2026-51416
Analyzes a specific CVE in WeChat OAuth handler, identifying unbounded HTTP response reads leading to denial of service, with remediation guidance.